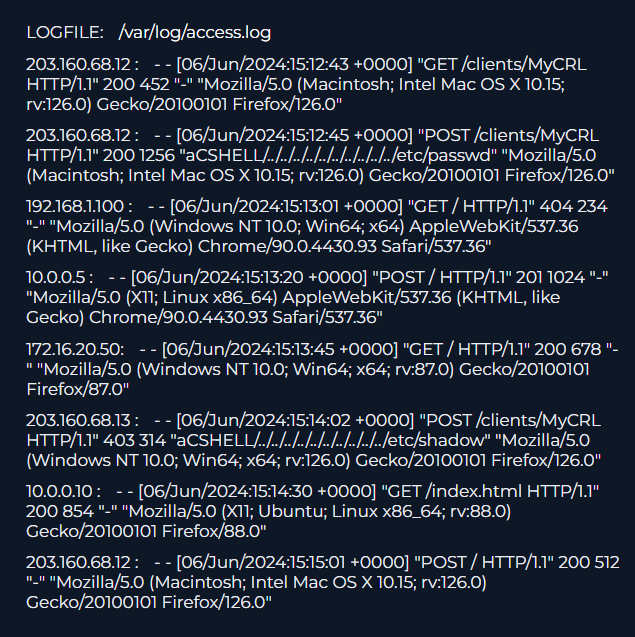
Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management


Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.

It was developed to speed up the processes of SOC Analysts during analysis

Bro analyzer that detects Google's QUIC protocol

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

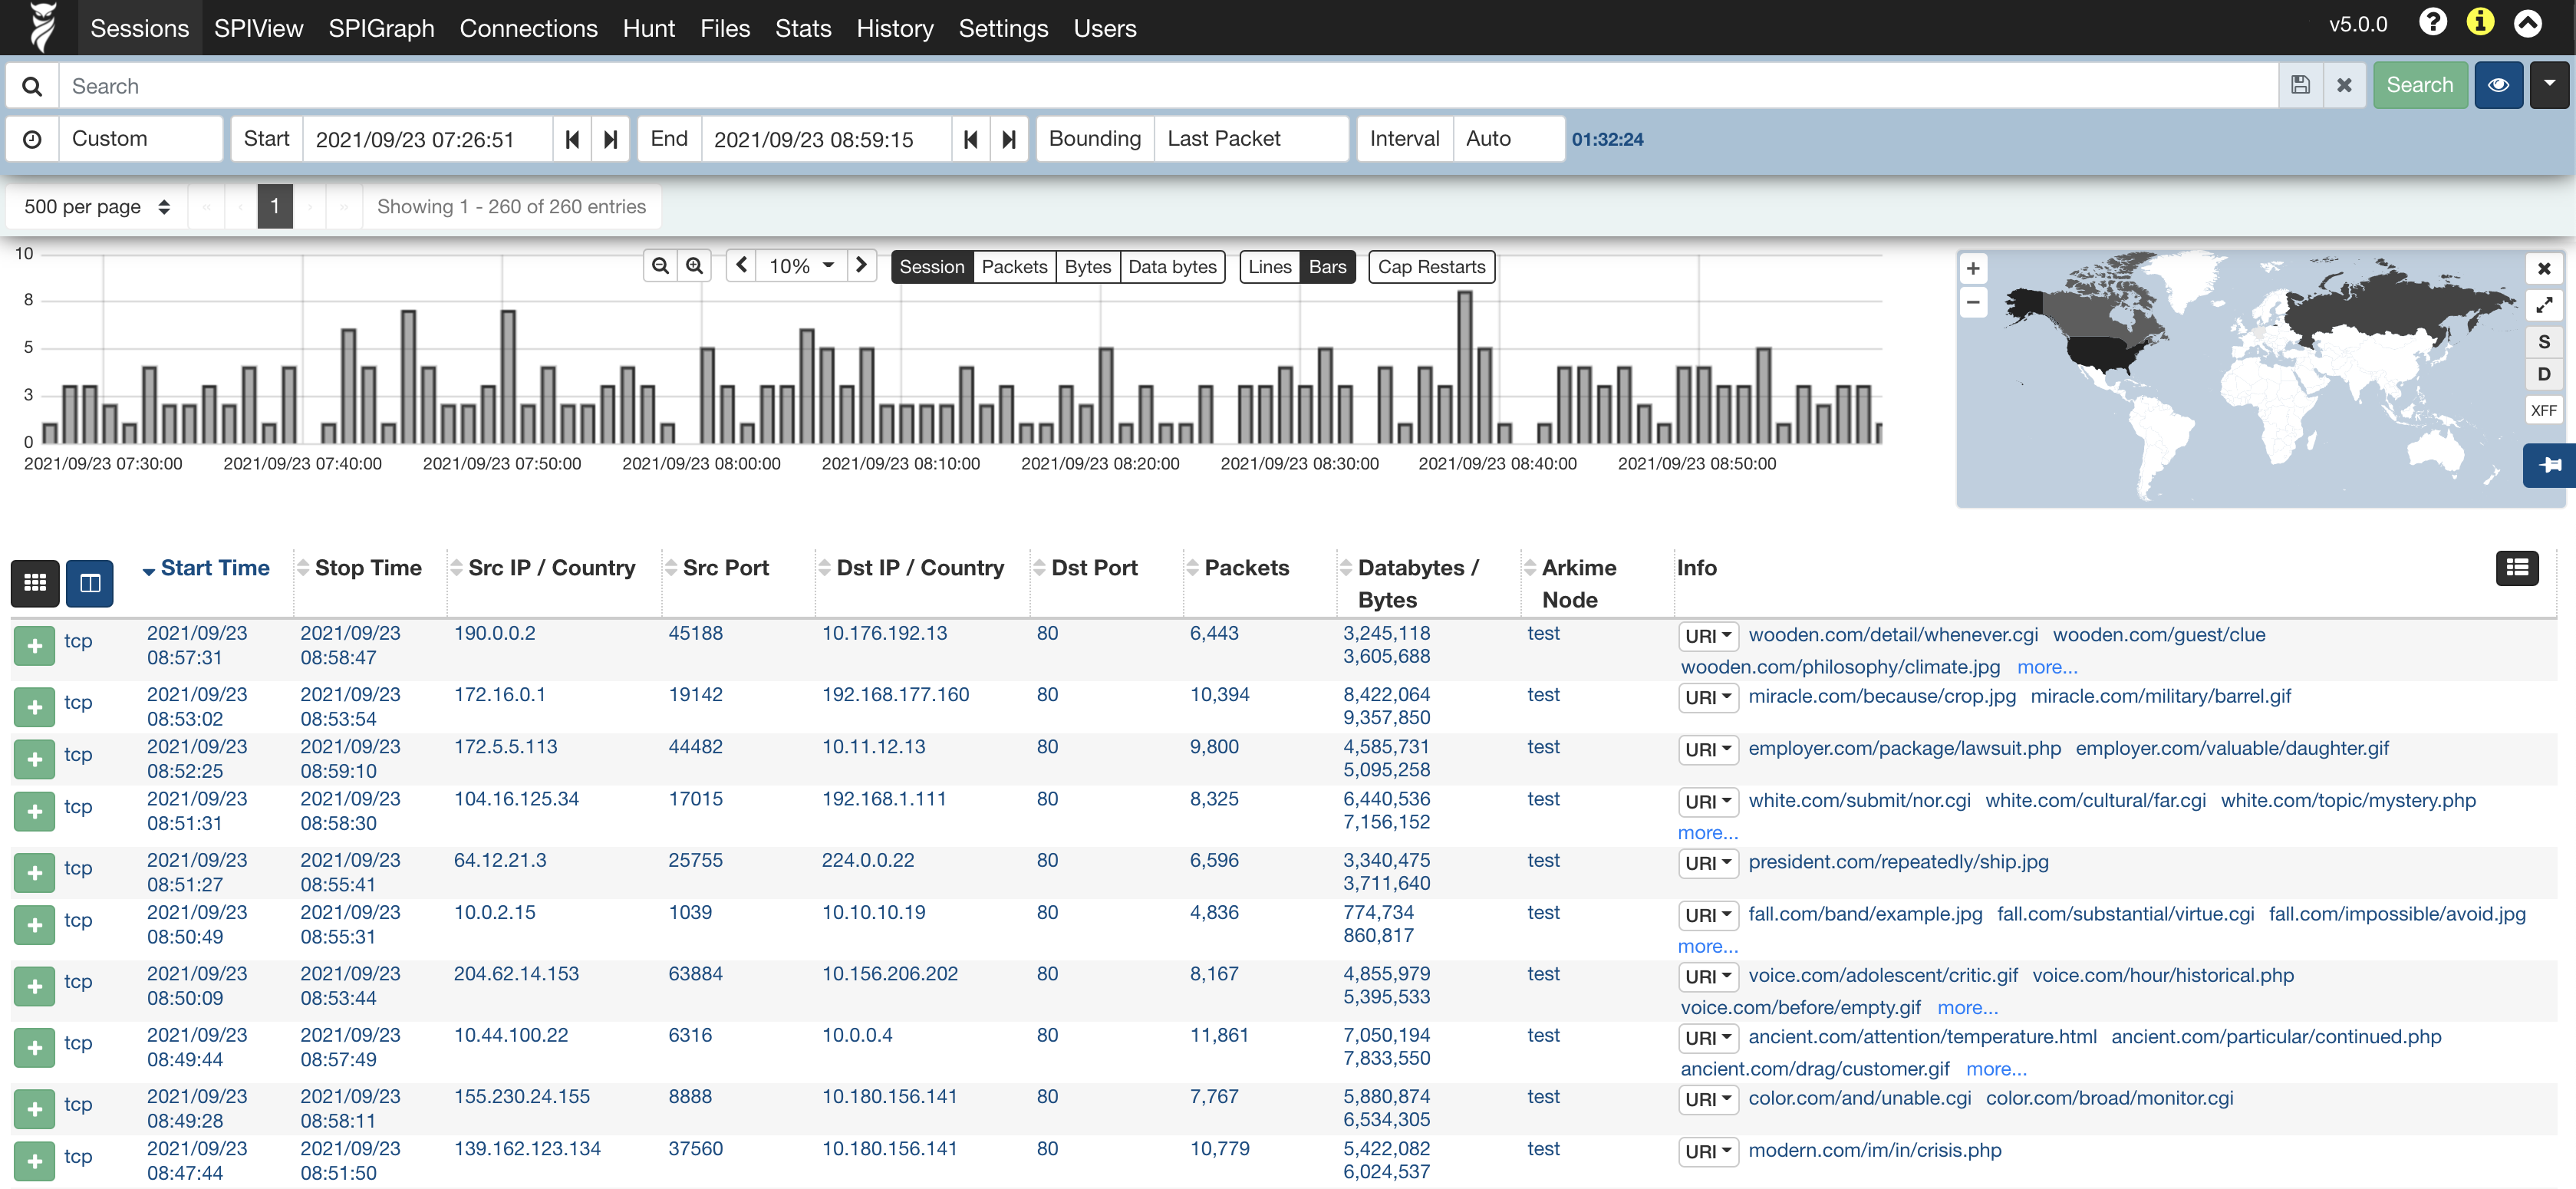
Arkime is an open source, large scale, full packet capturing, indexing, and database system.


A list of cyber-chef recipes and curated links

TCP/IP packet demultiplexer. Download from:

Malicious HTTP traffic explorer

The Multiplatform Linux Sandbox

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.

A tool to analyze the network flow during attack/defence Capture the Flag competitions

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark

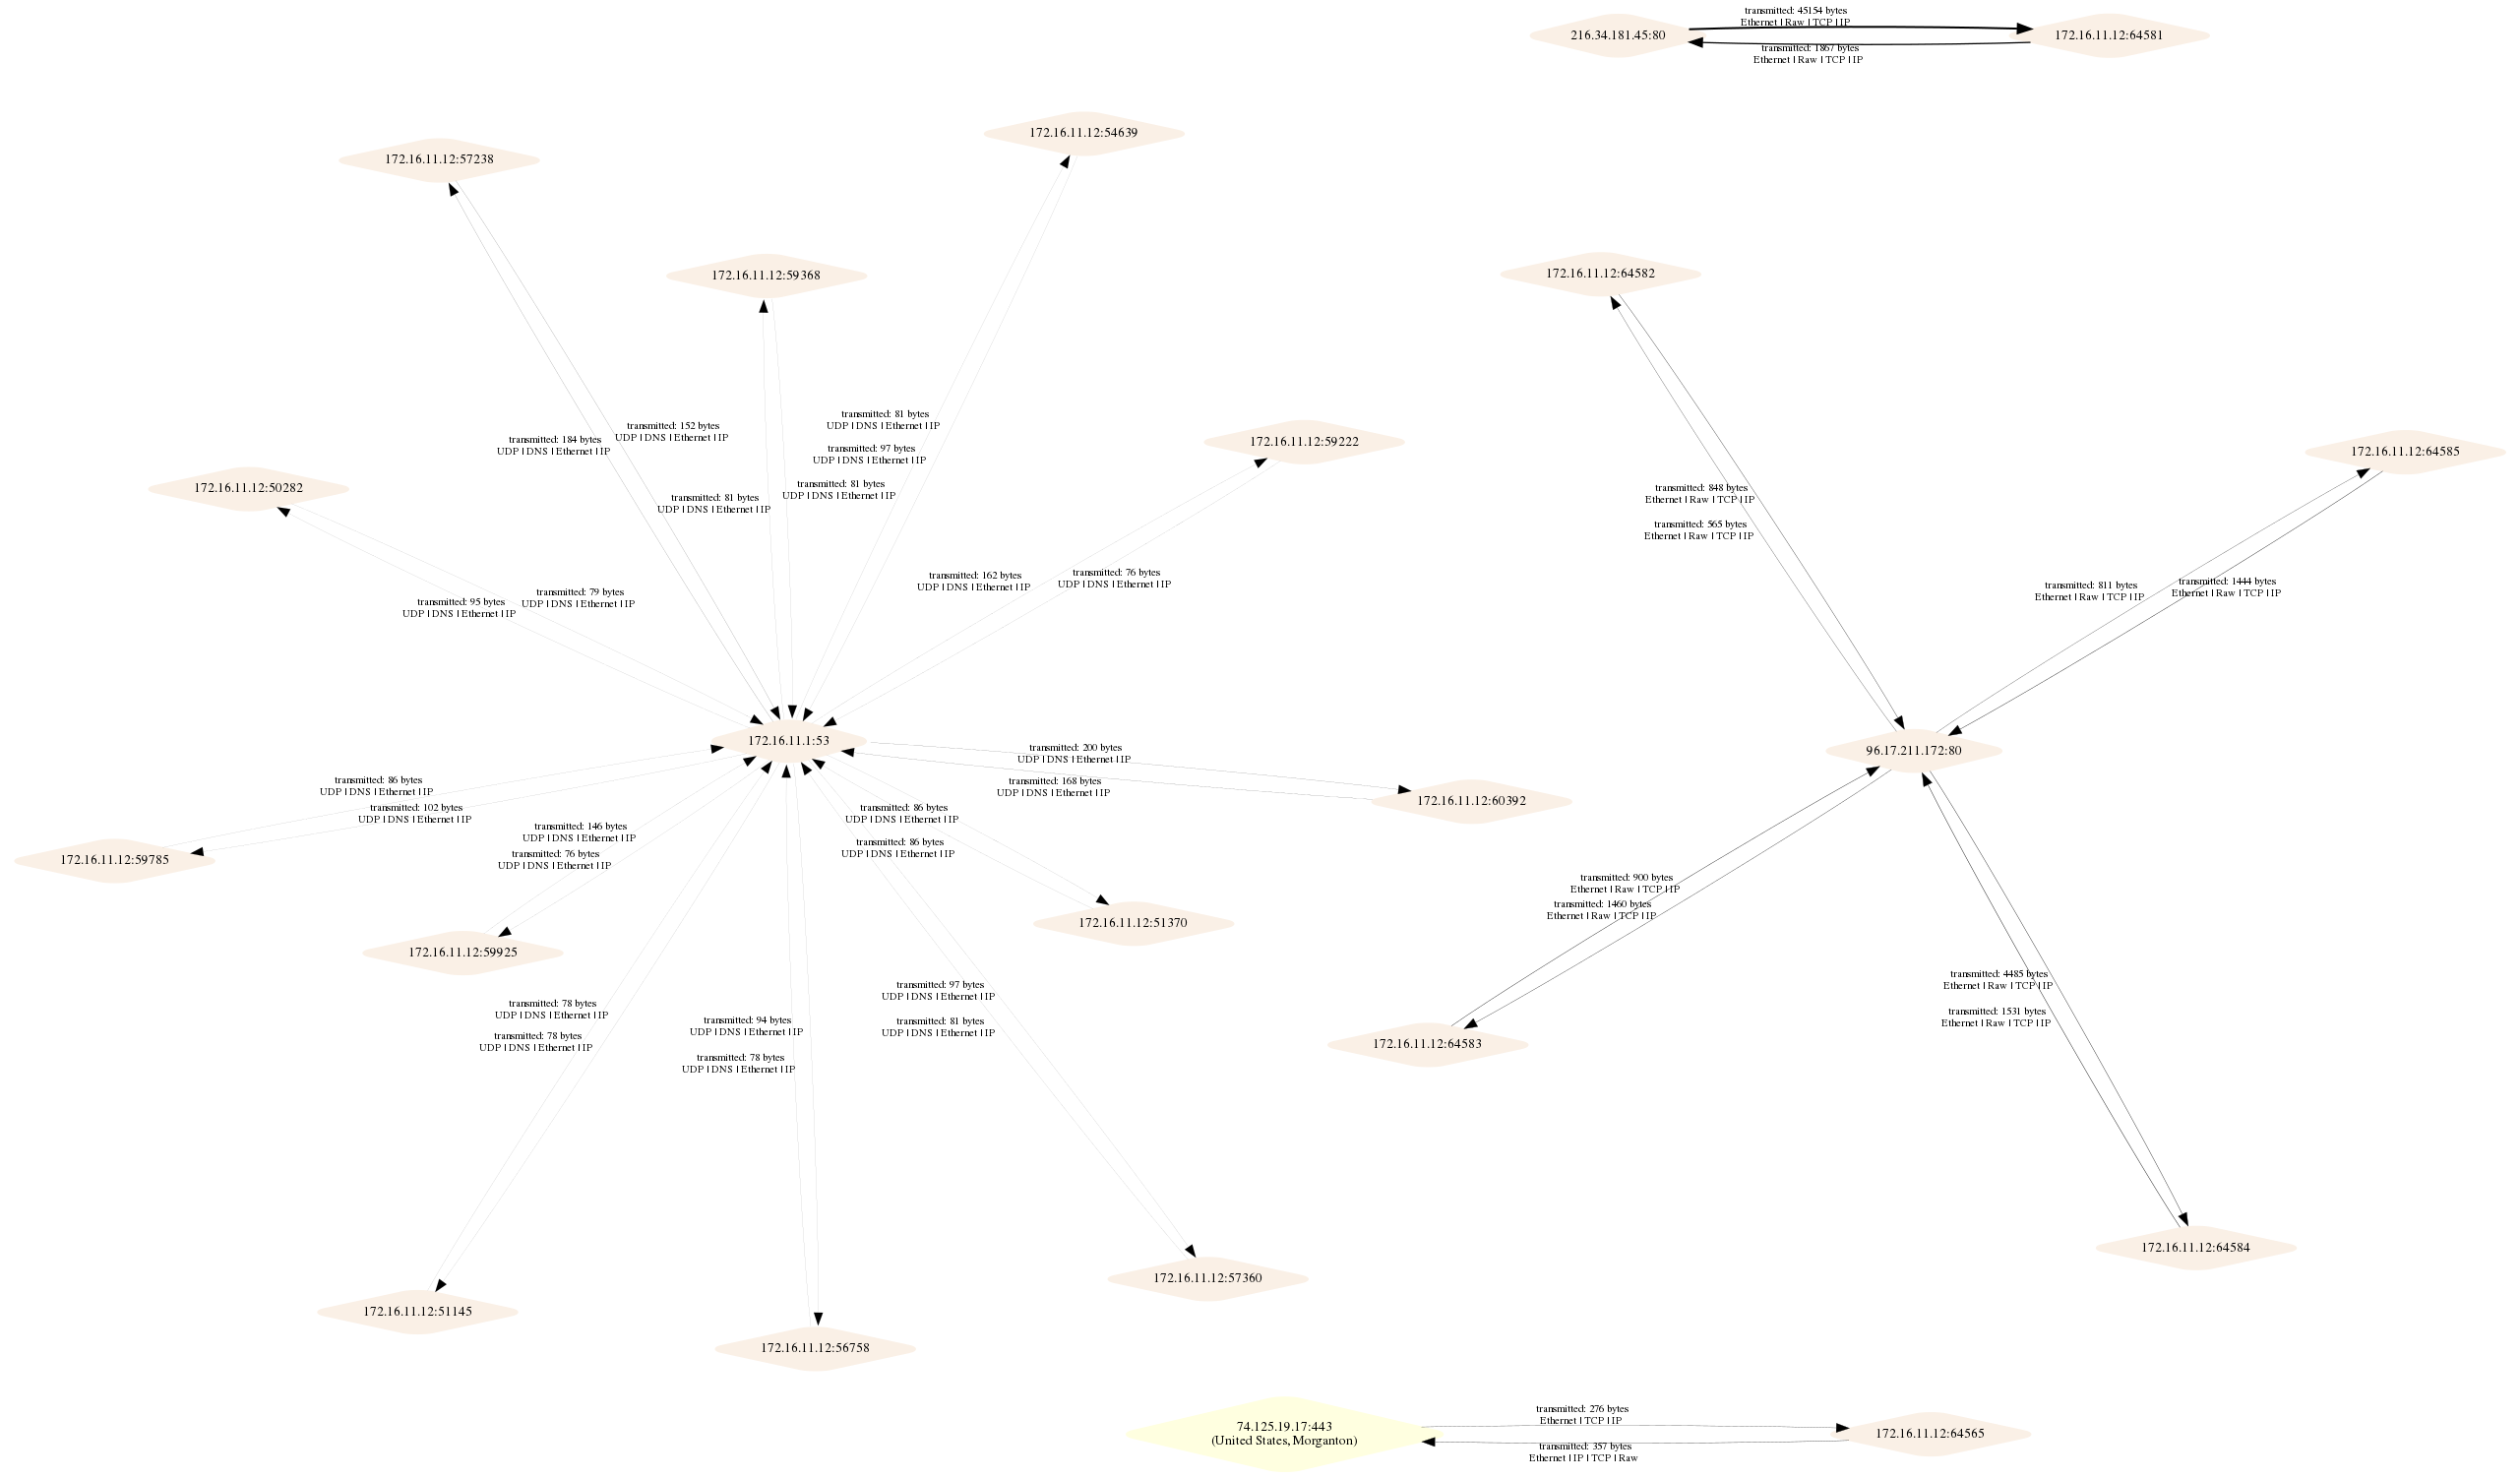
Visualize network topologies and collect graph statistics based on pcap files