
CapTipper
 omriher/captipper
Malicious HTTP traffic explorer
digital-forensicsexploit-frameworksforensics+5
omriher/captipperMalicious HTTP traffic explorer
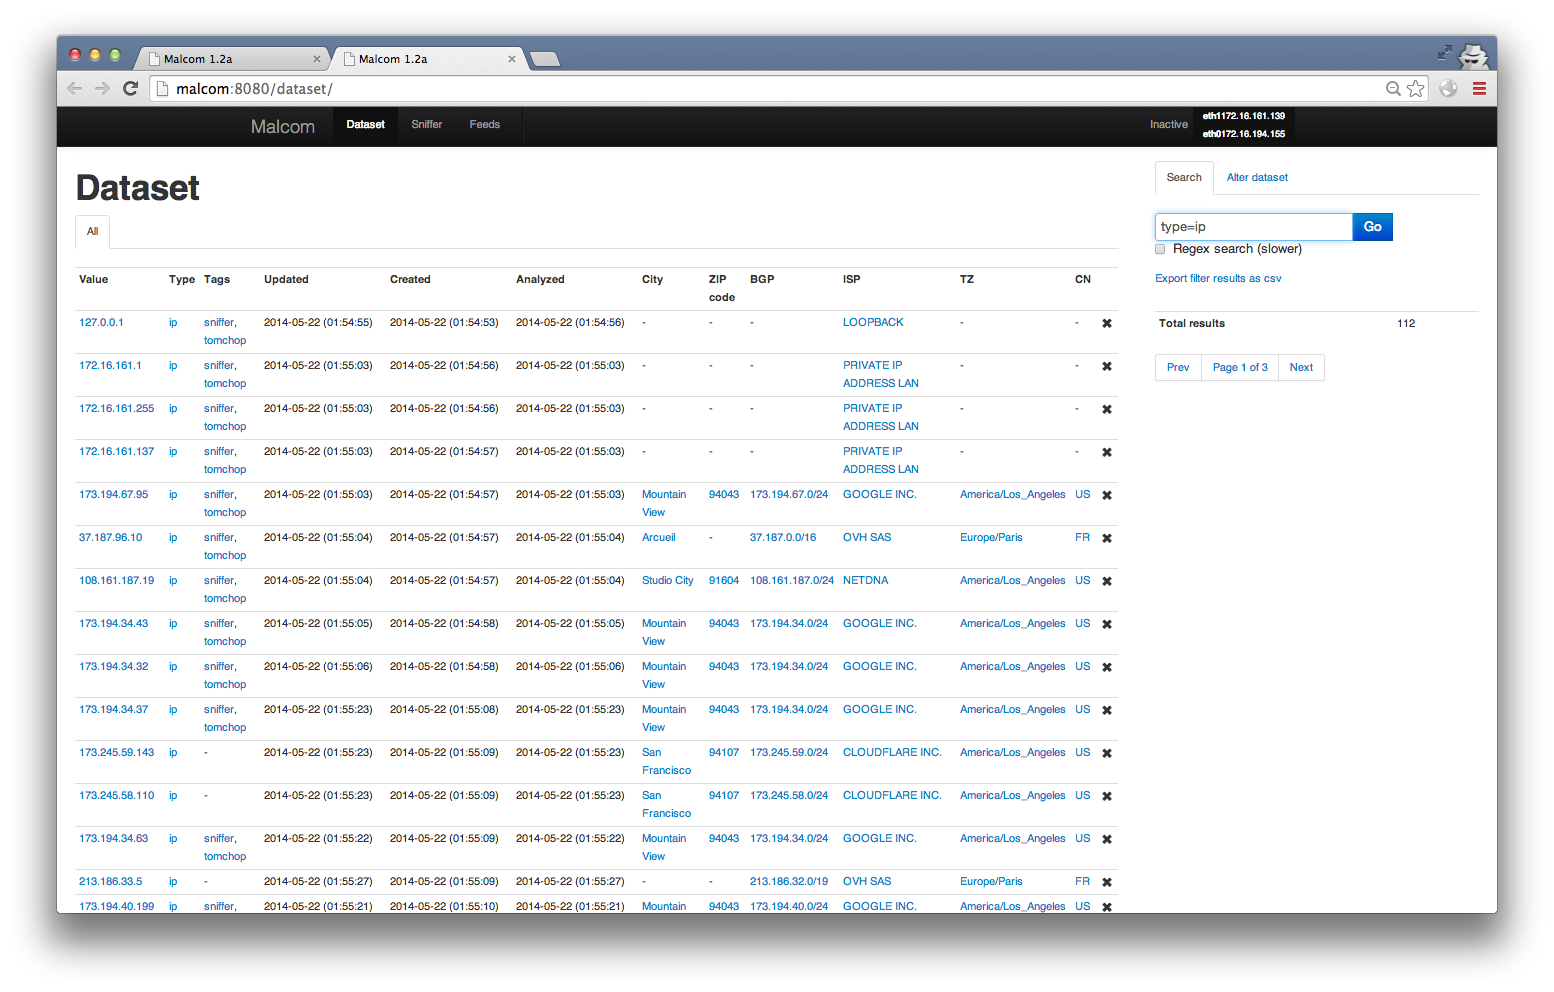 tomchop/malcom
Malcom - Malware Communications Analyzer
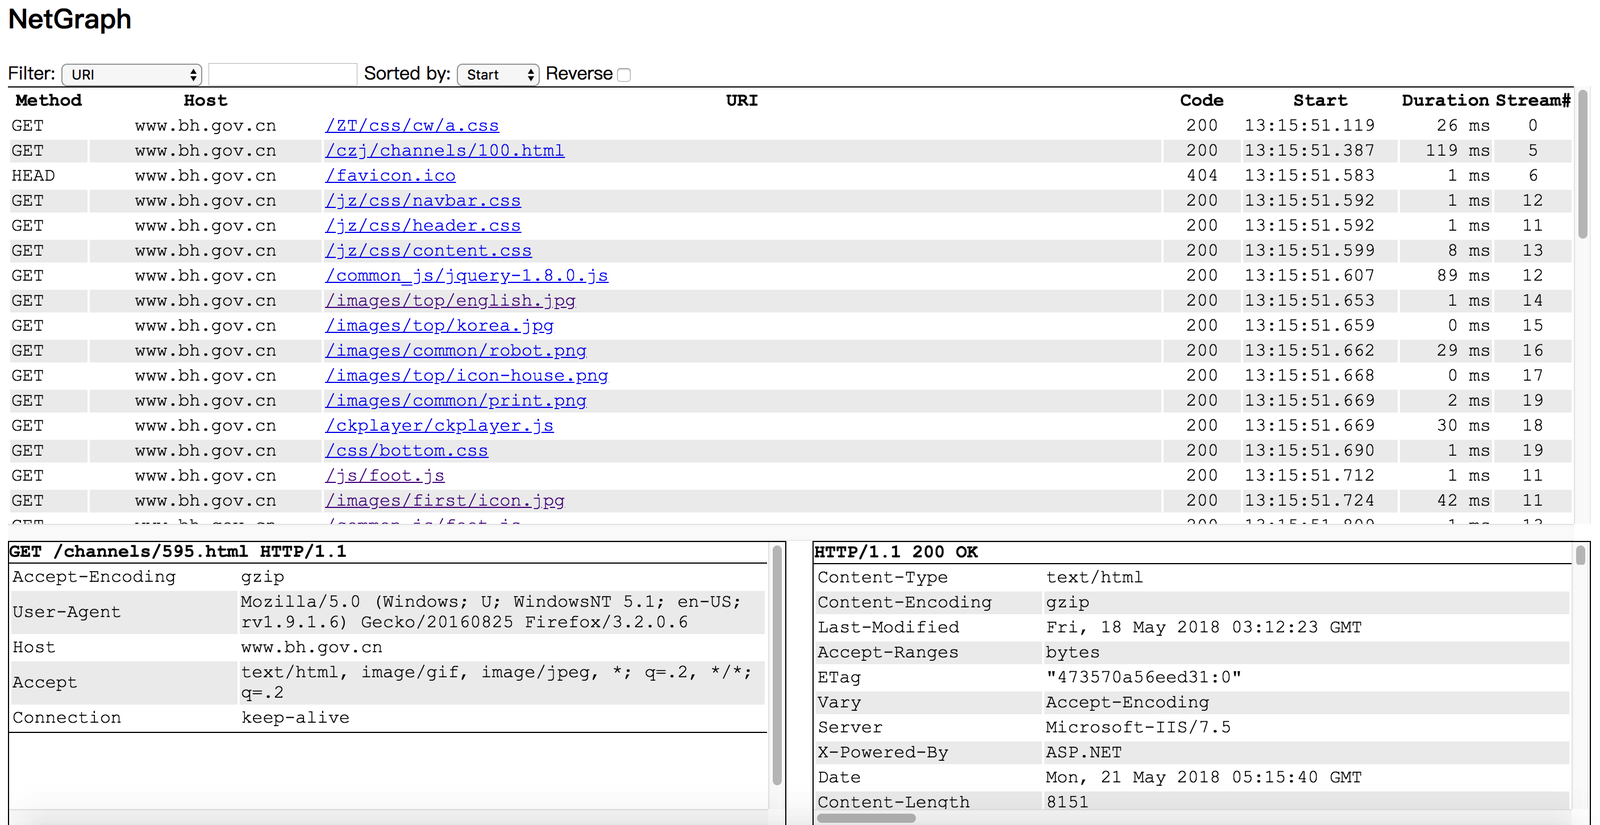 ga0/netgraph
A cross platform http sniffer with a web UI
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
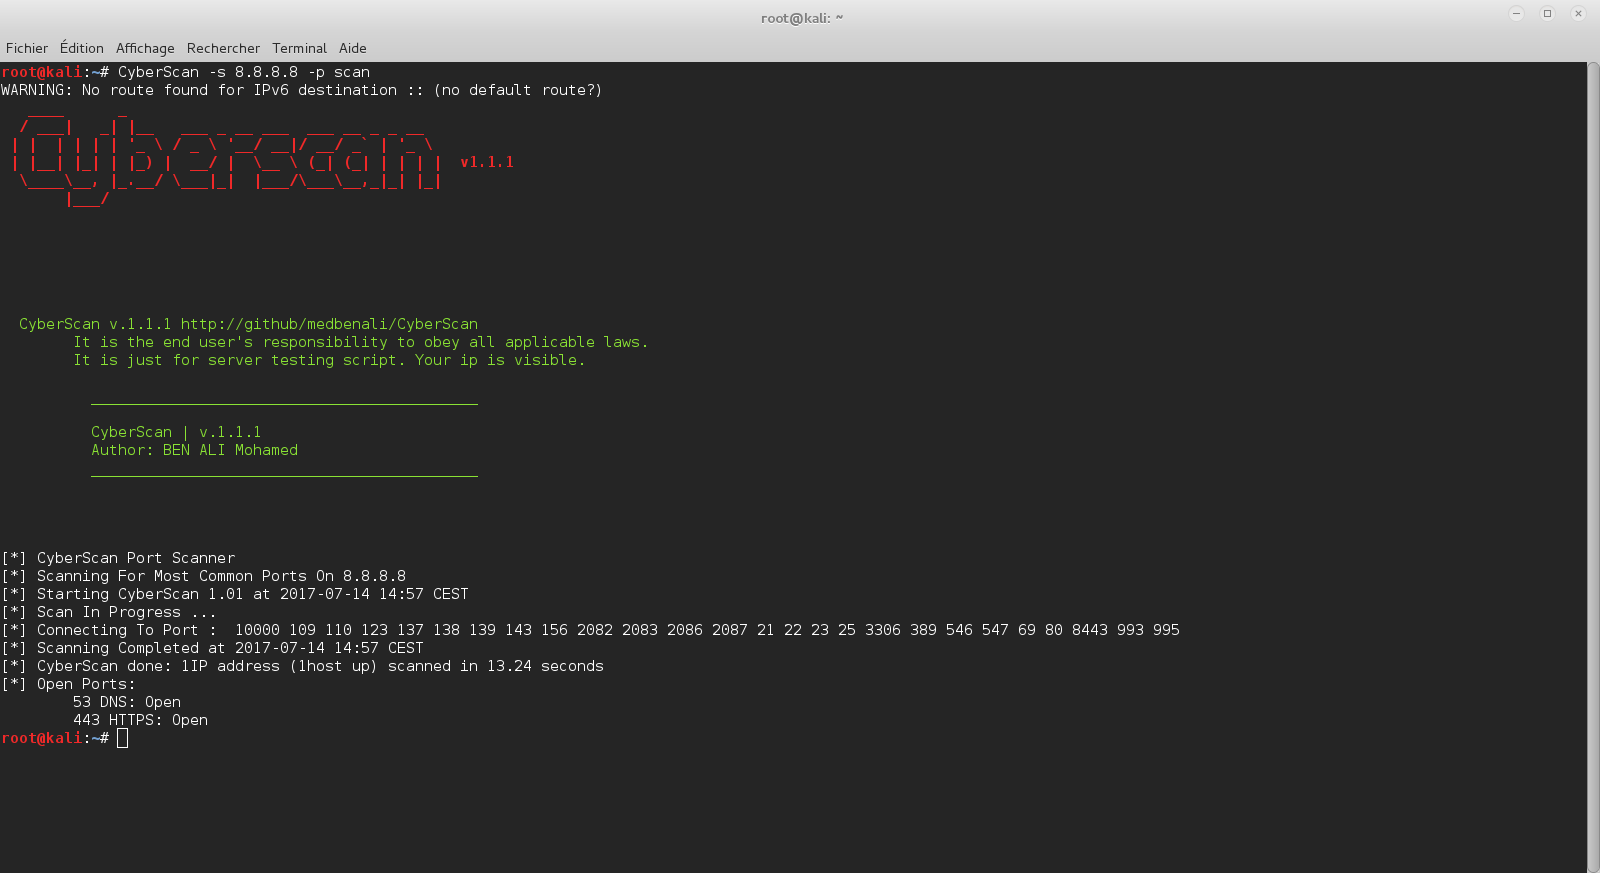 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
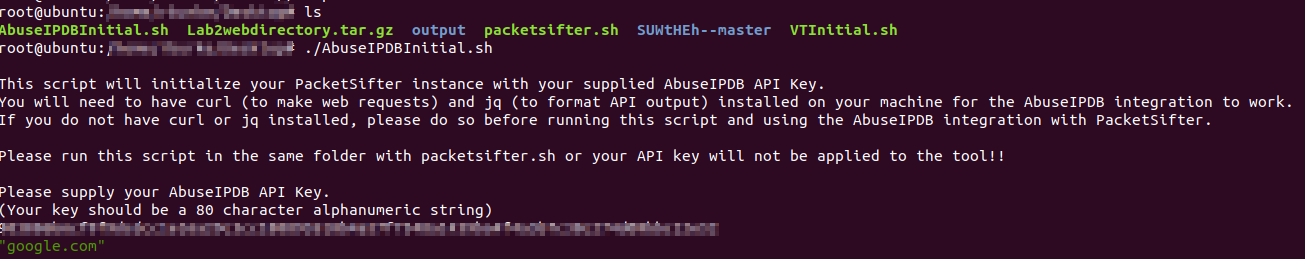 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…