

 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
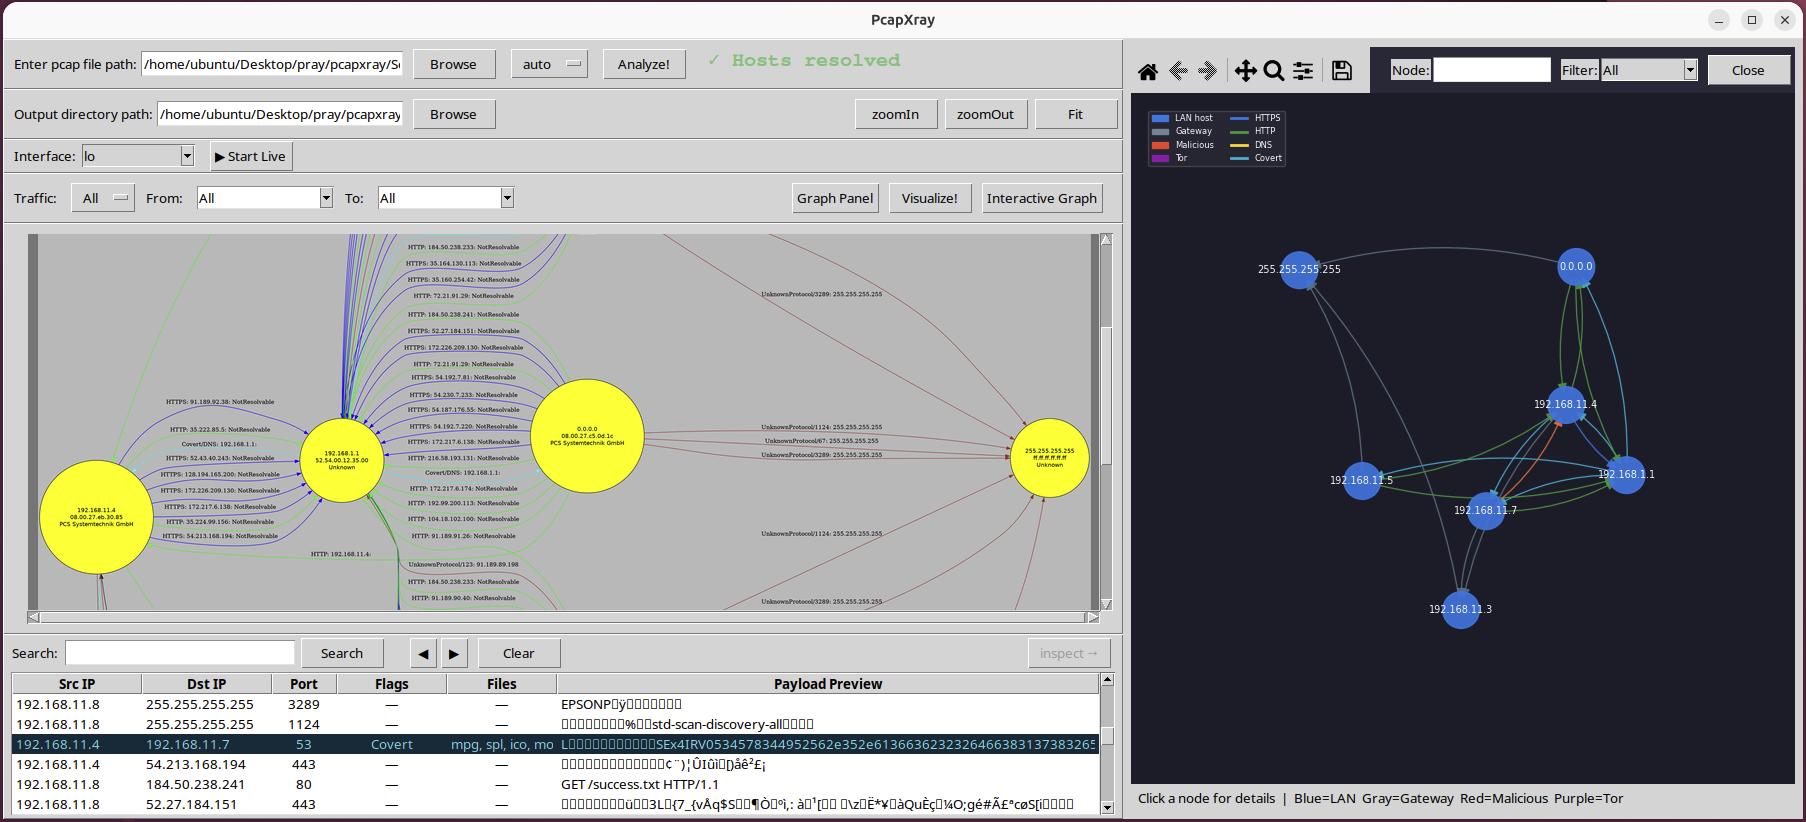 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
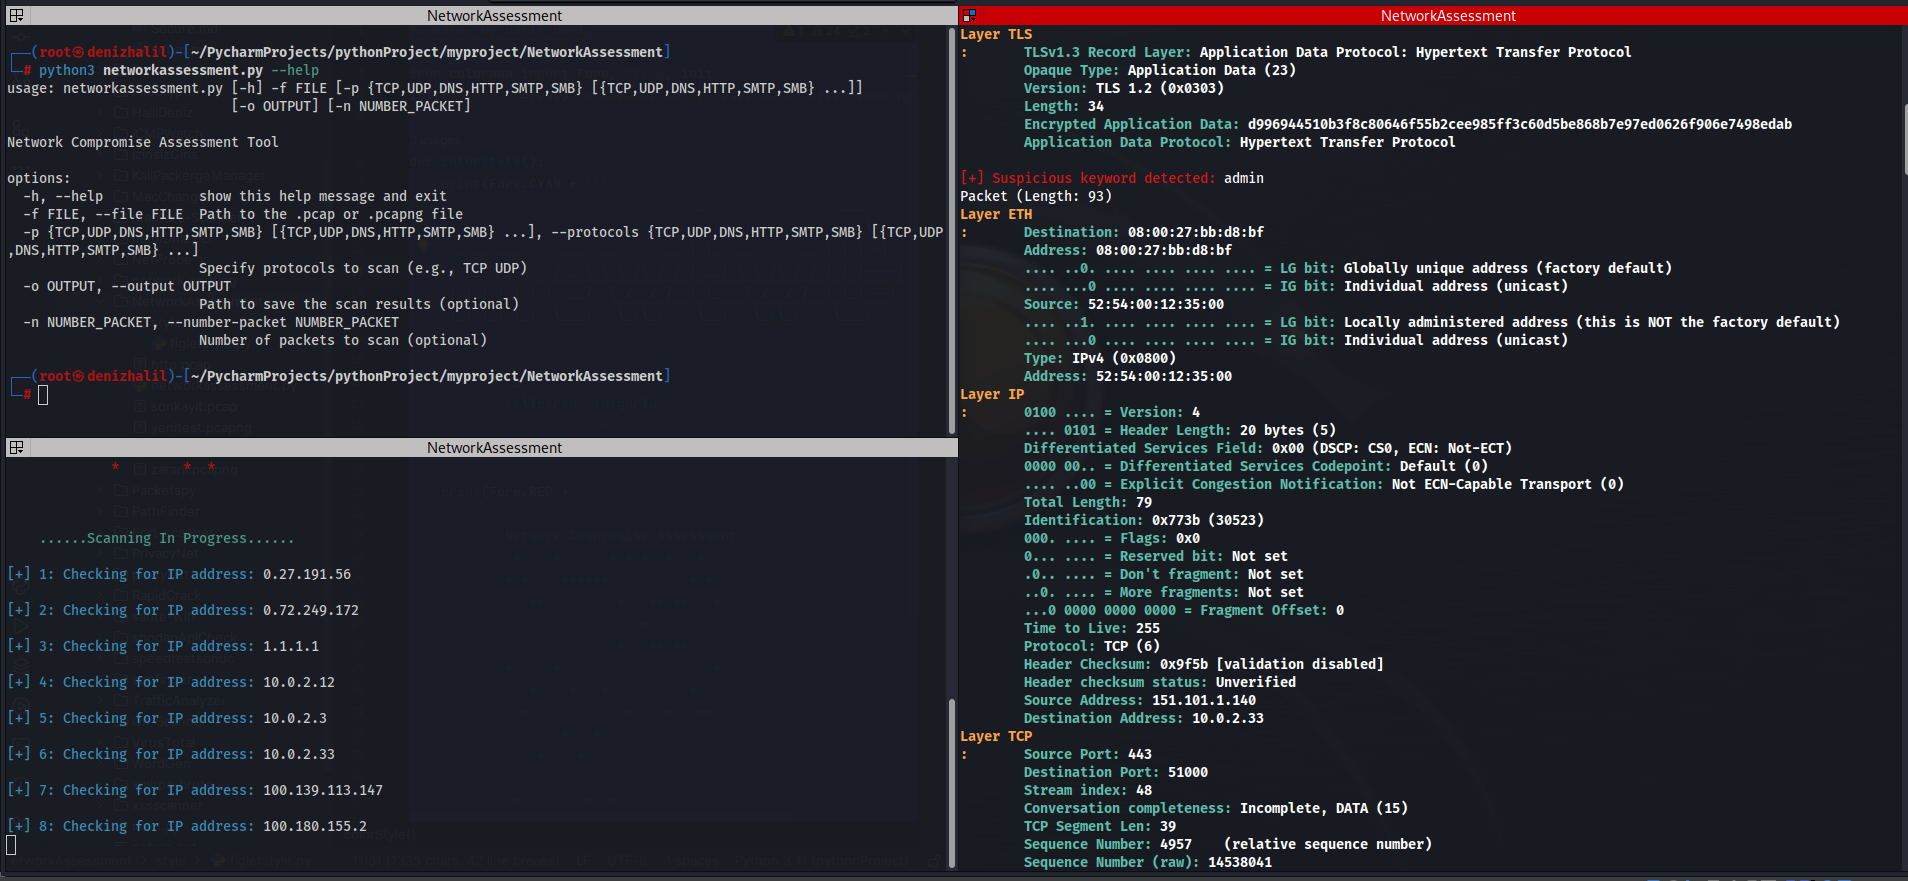 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
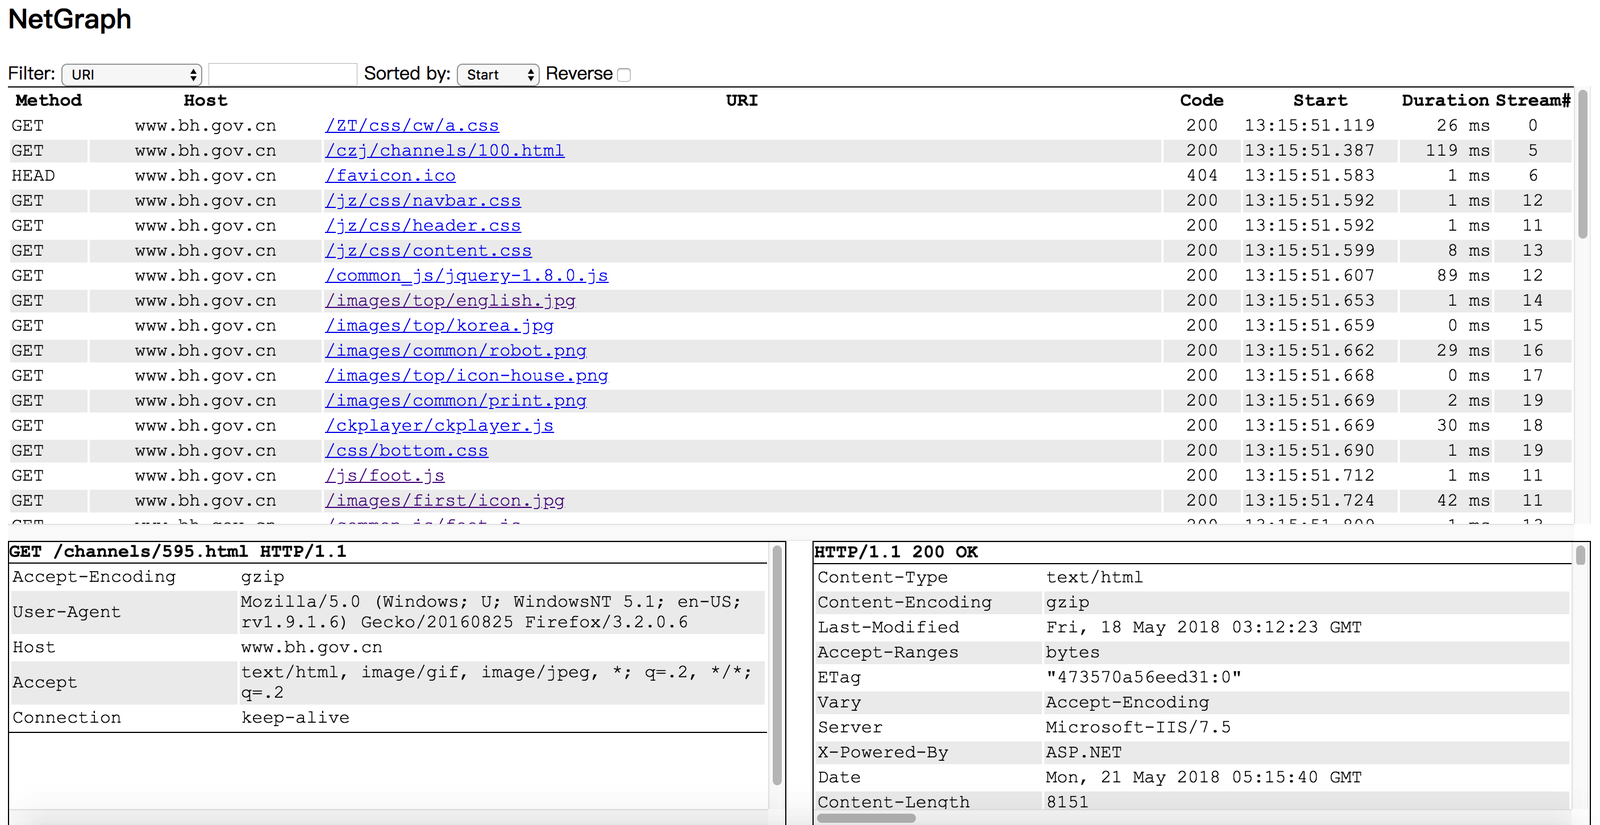 ga0/netgraph
A cross platform http sniffer with a web UI
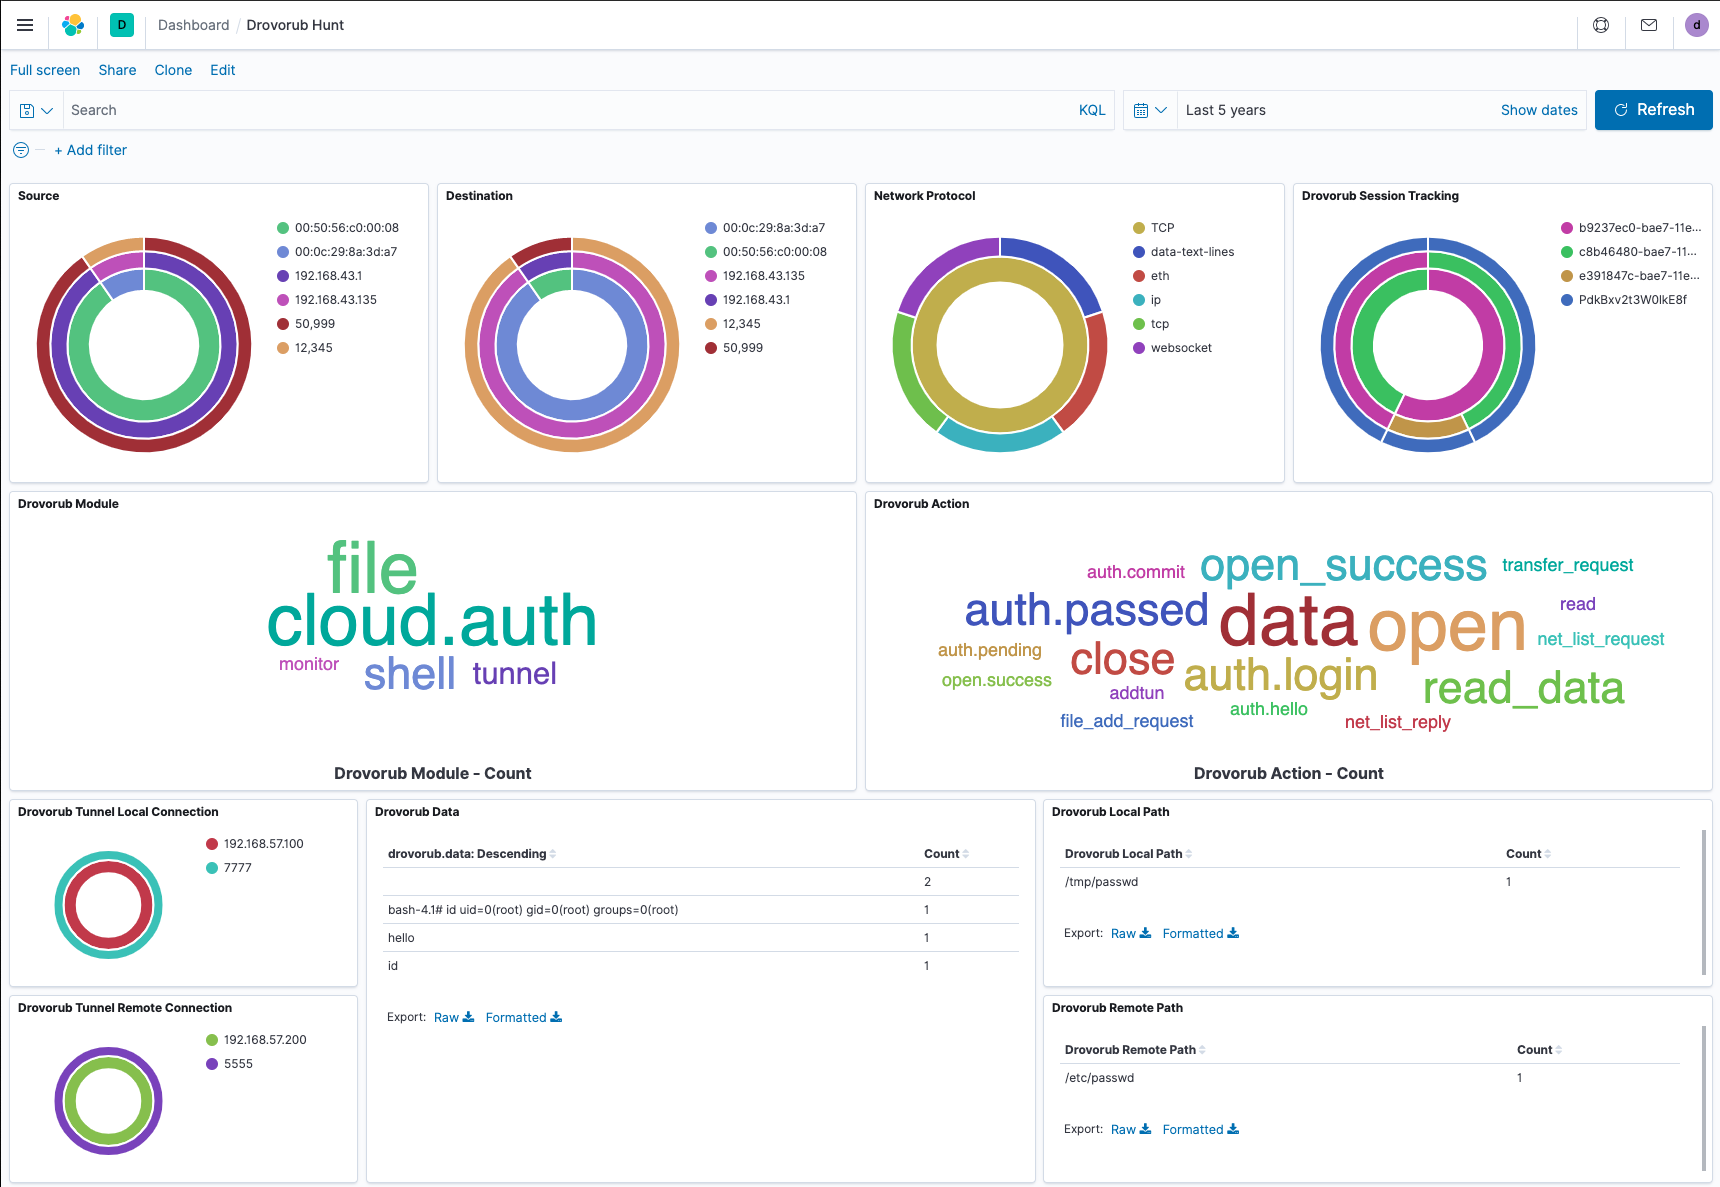 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
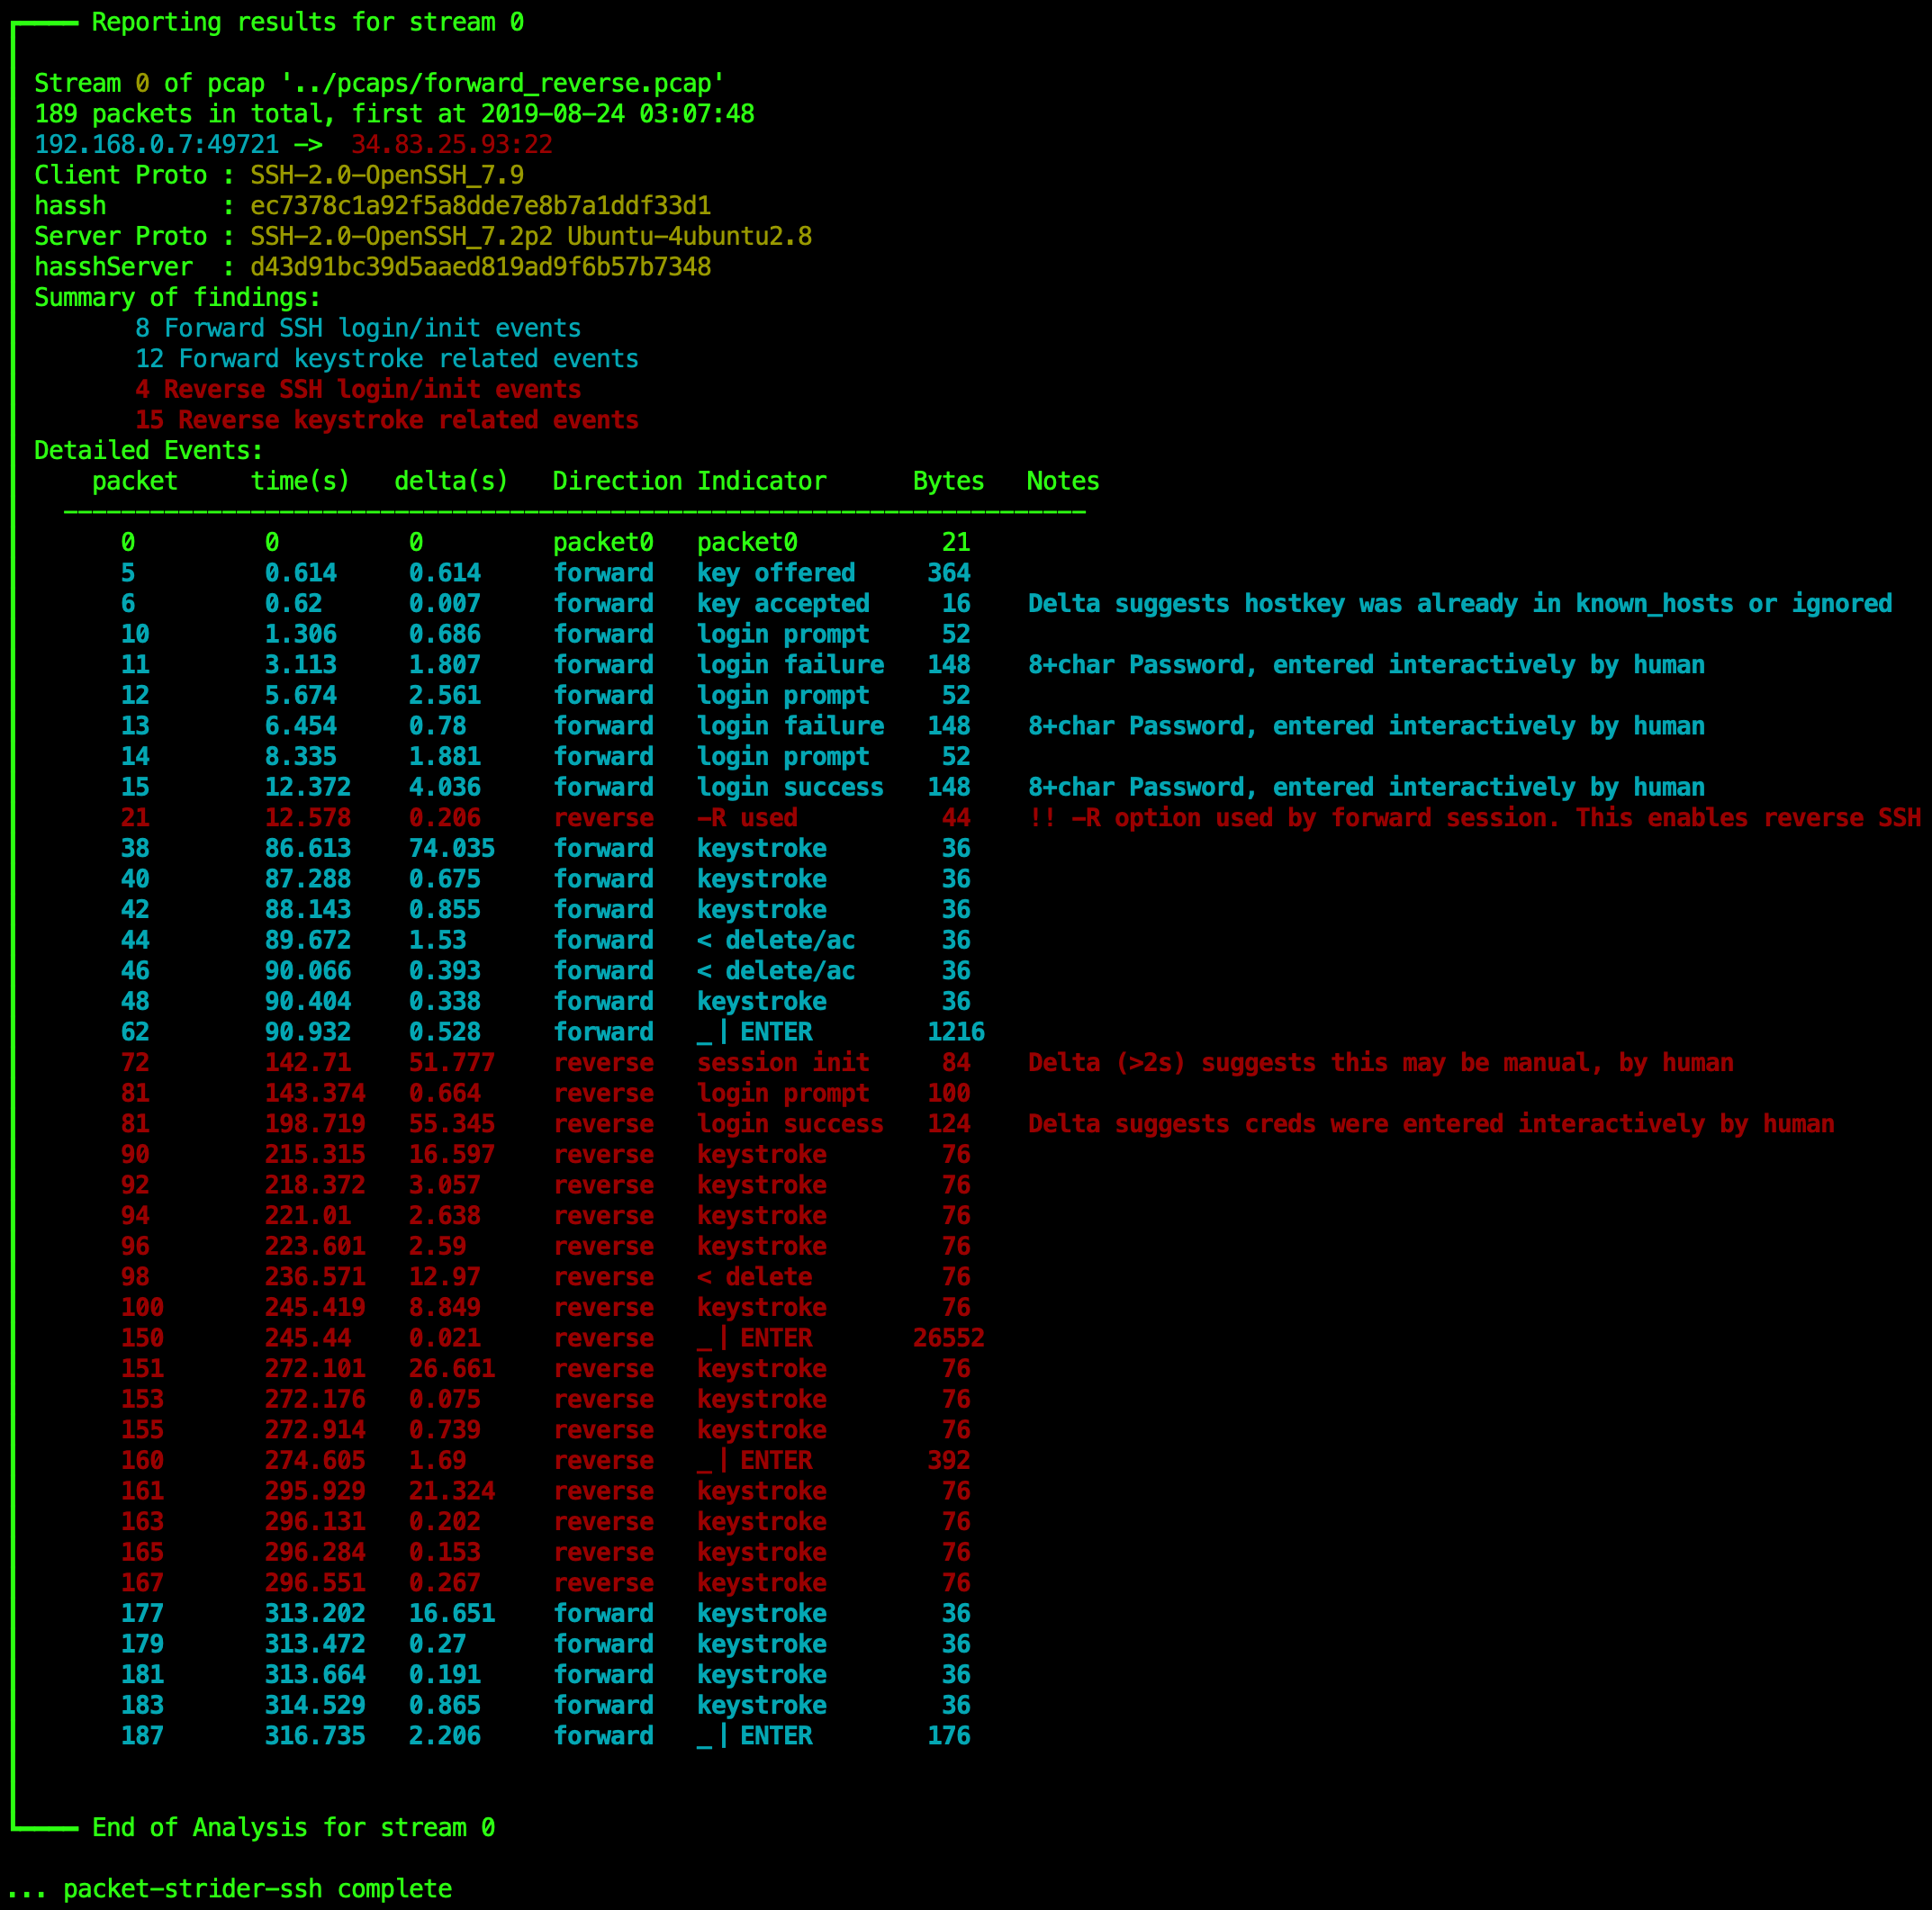 benjeems/packetstrider
A network packet forensics tool for SSH
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…