
Wireshark
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
dns-analysisforensicsnetwork-forensics+3
1.6k
wireshark/wiresharkWireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
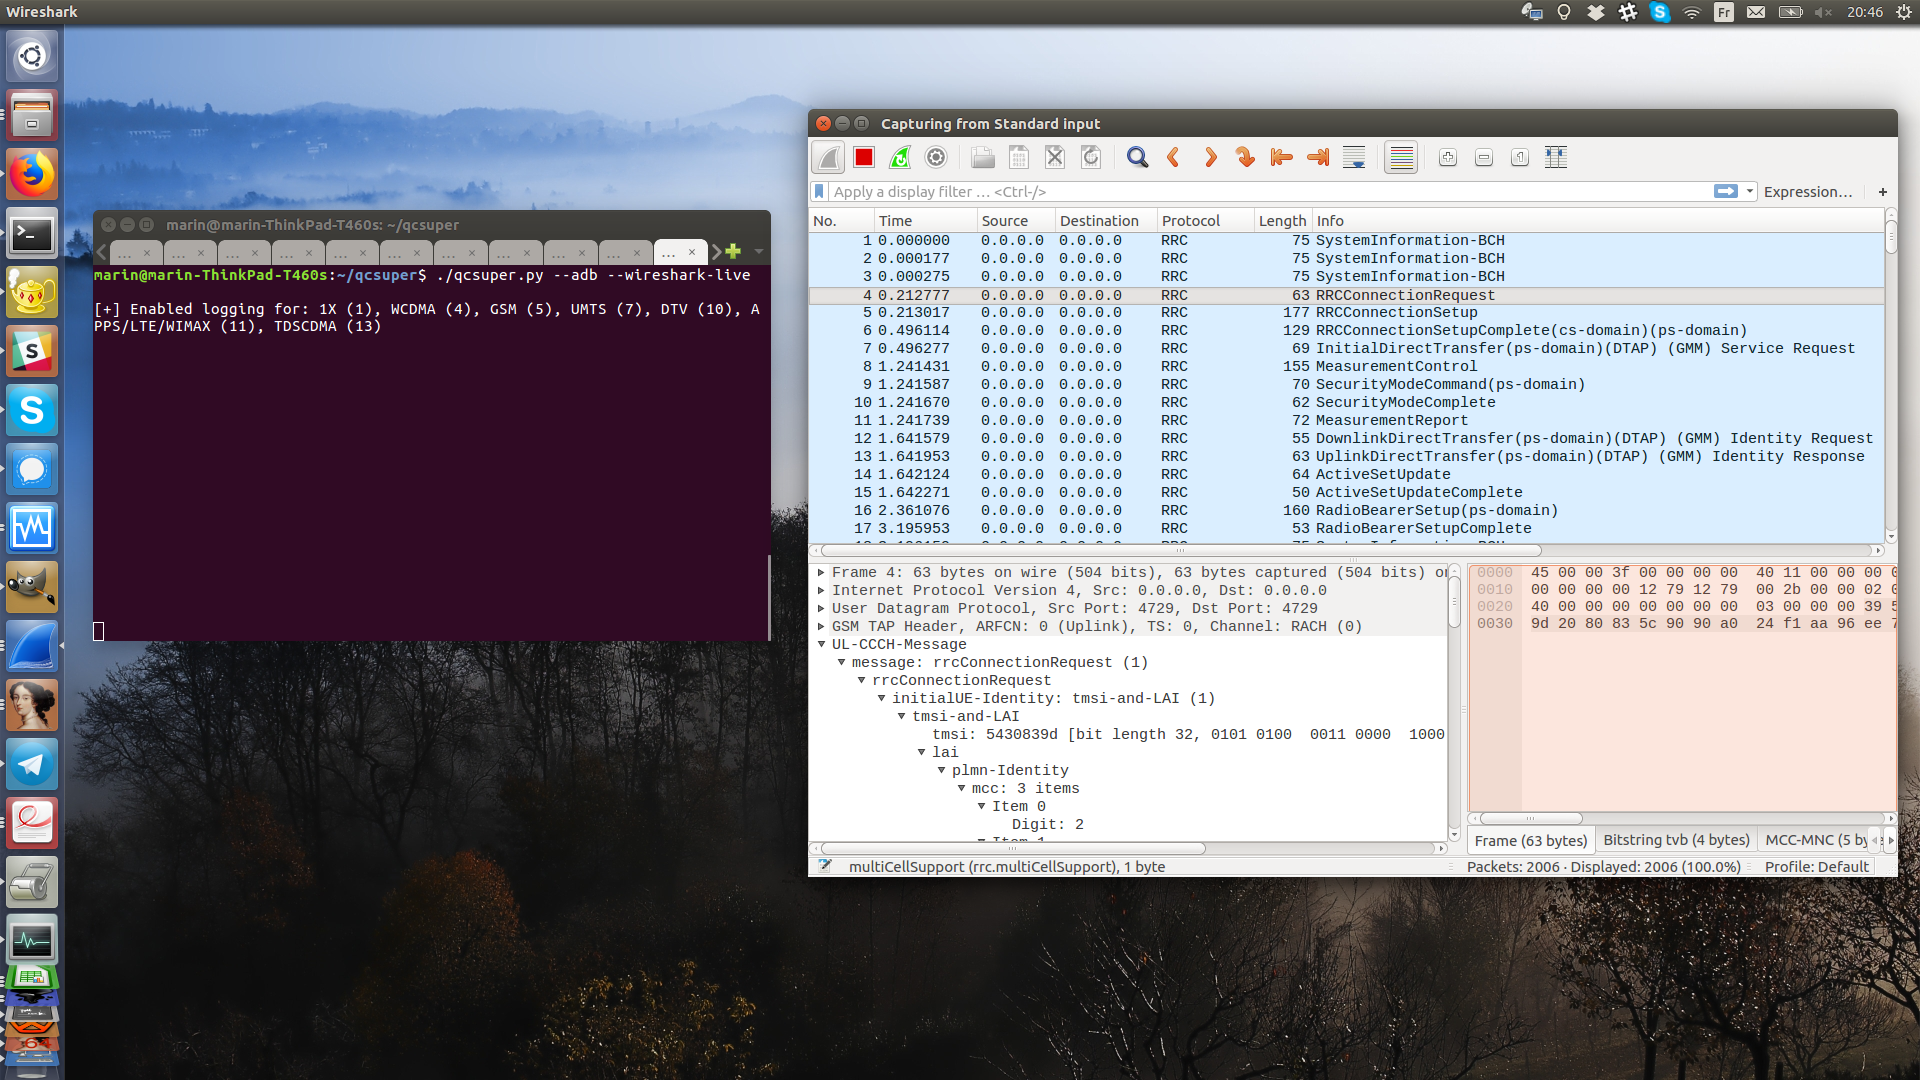 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 trinadh-dasari-cyber/eternalblue-ms17-010-research
Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
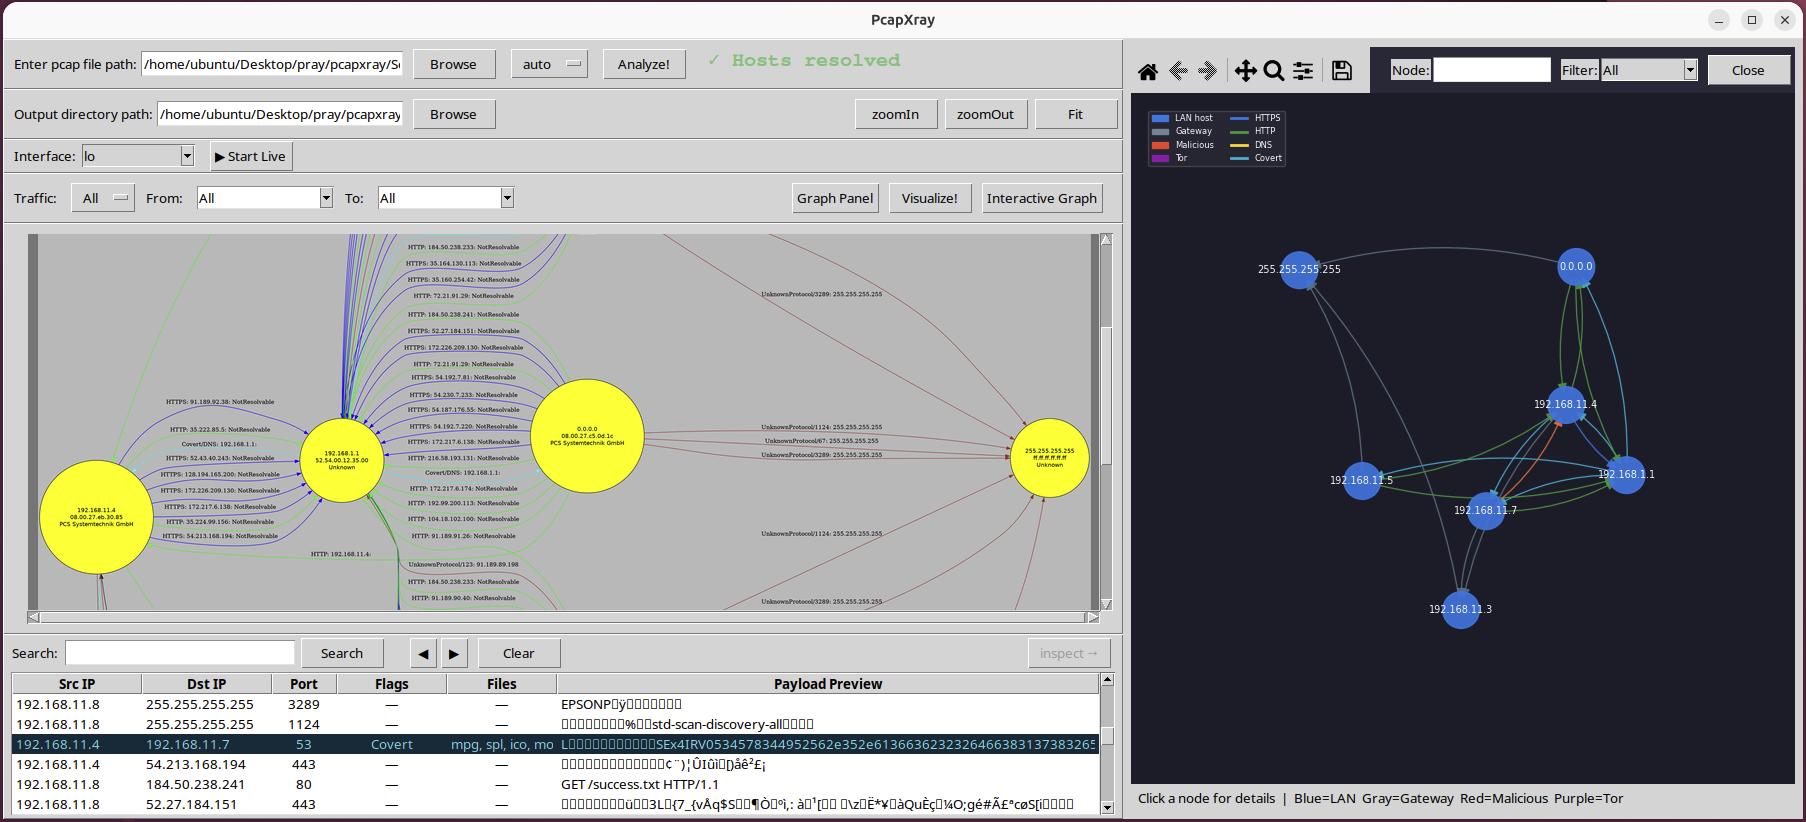 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.
 simsong/tcpflow
TCP/IP packet demultiplexer. Download from: