

wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
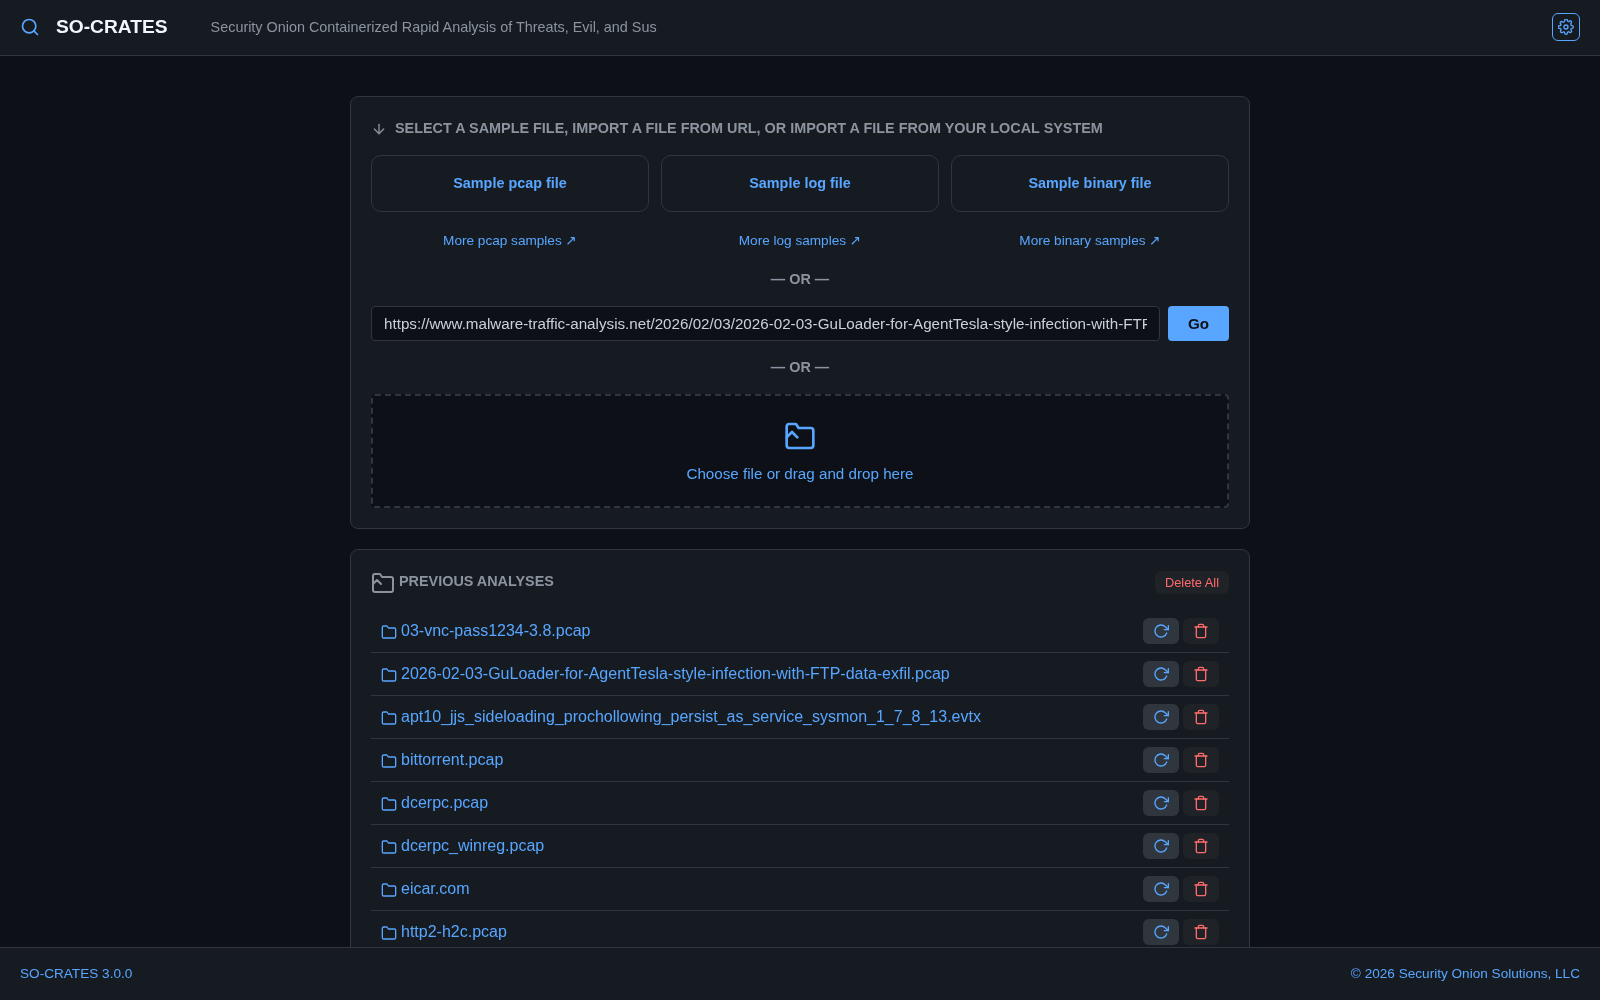 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
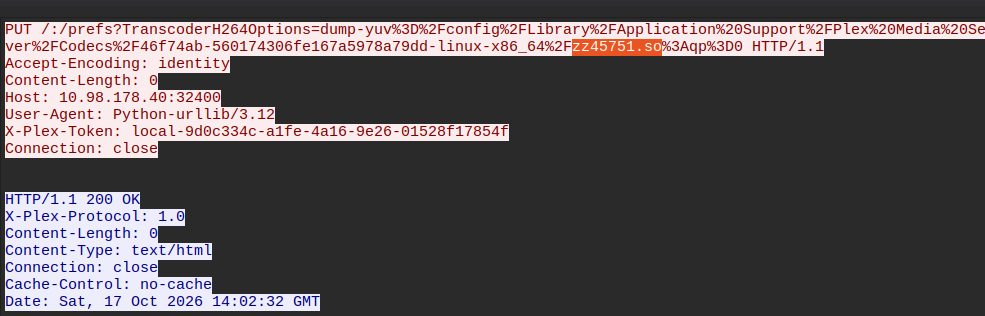 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
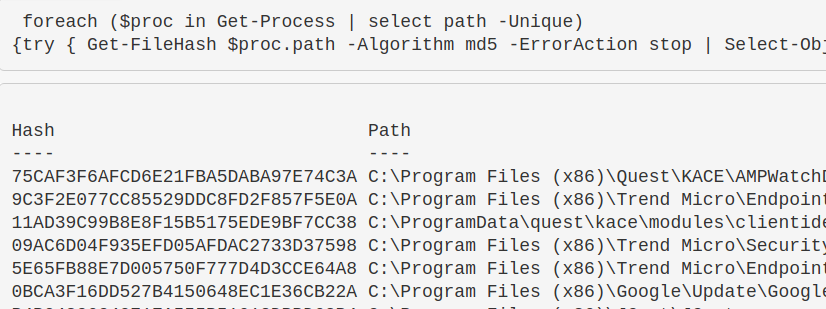 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…