timesketch
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k
google/timesketchCollaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
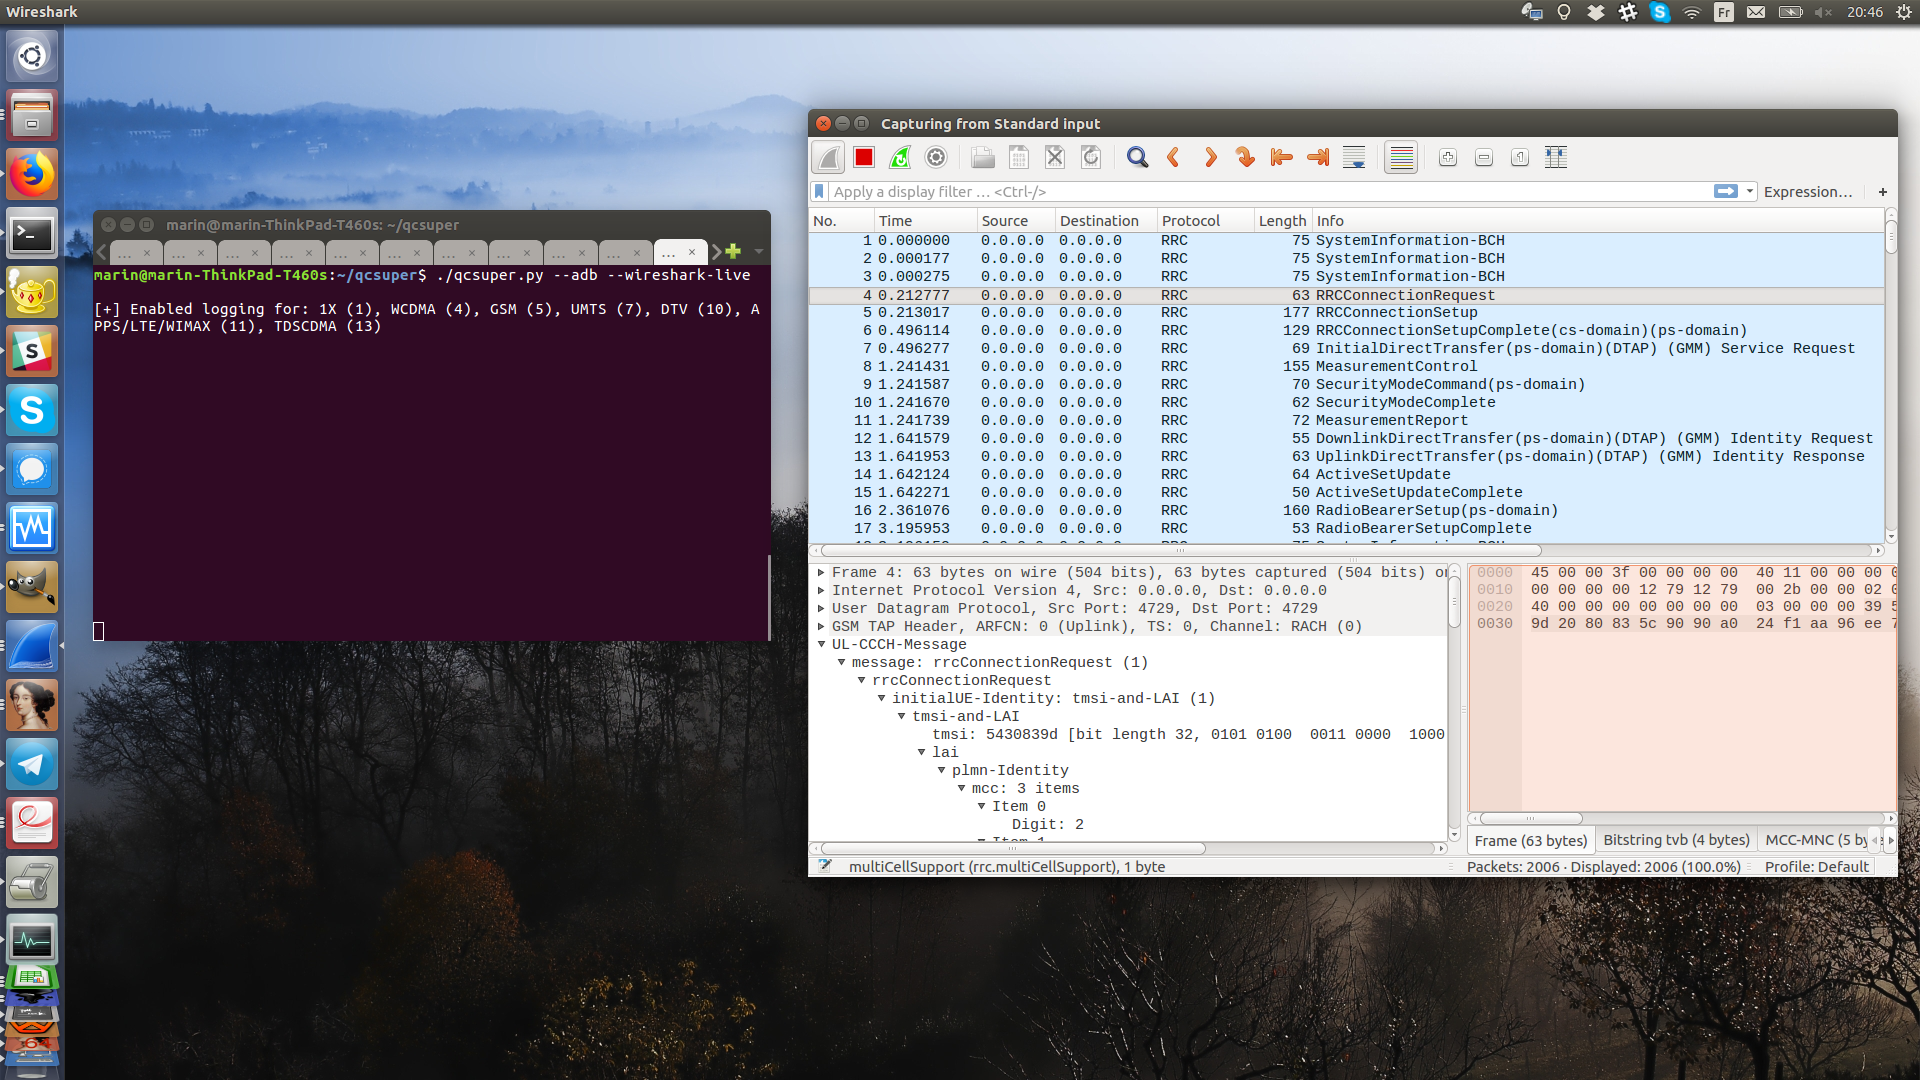 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
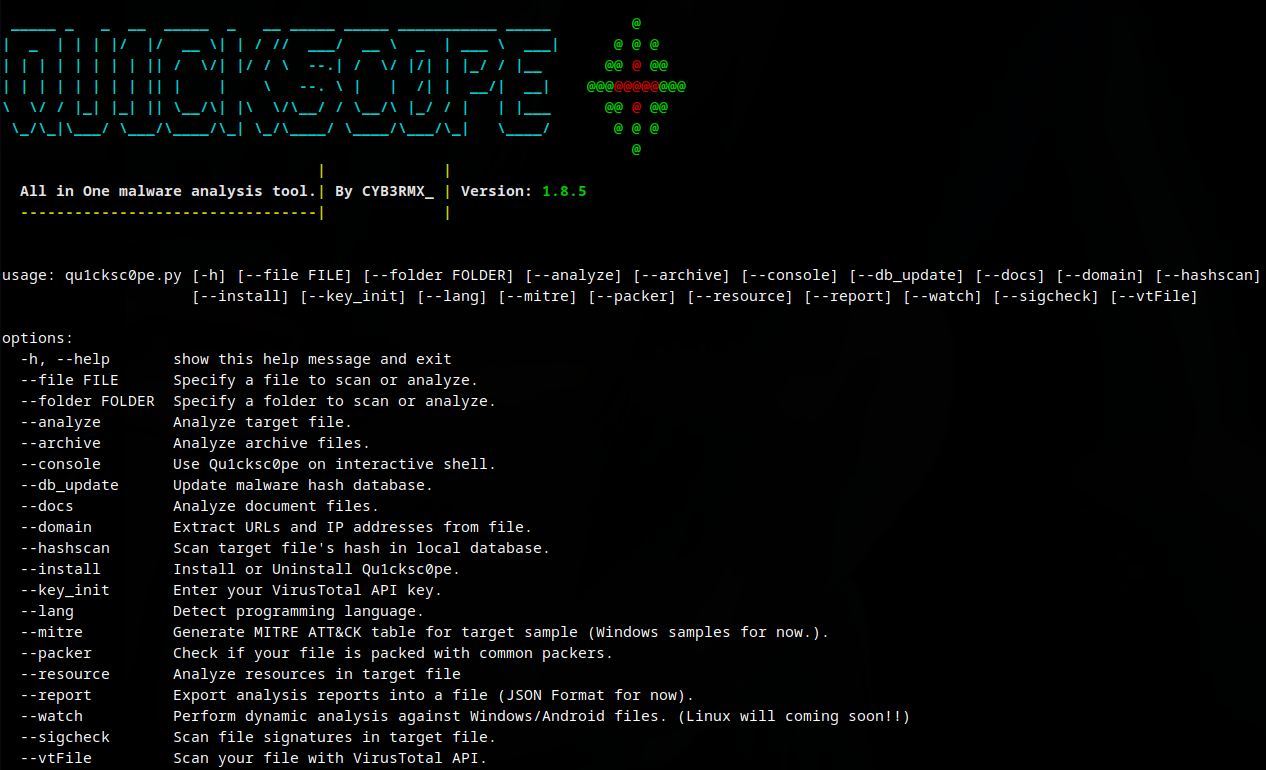 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 cristianzsh/forensictools
Collection of forensic tools
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 cyberhatcoil/acf
Android Connections Forensics