


 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
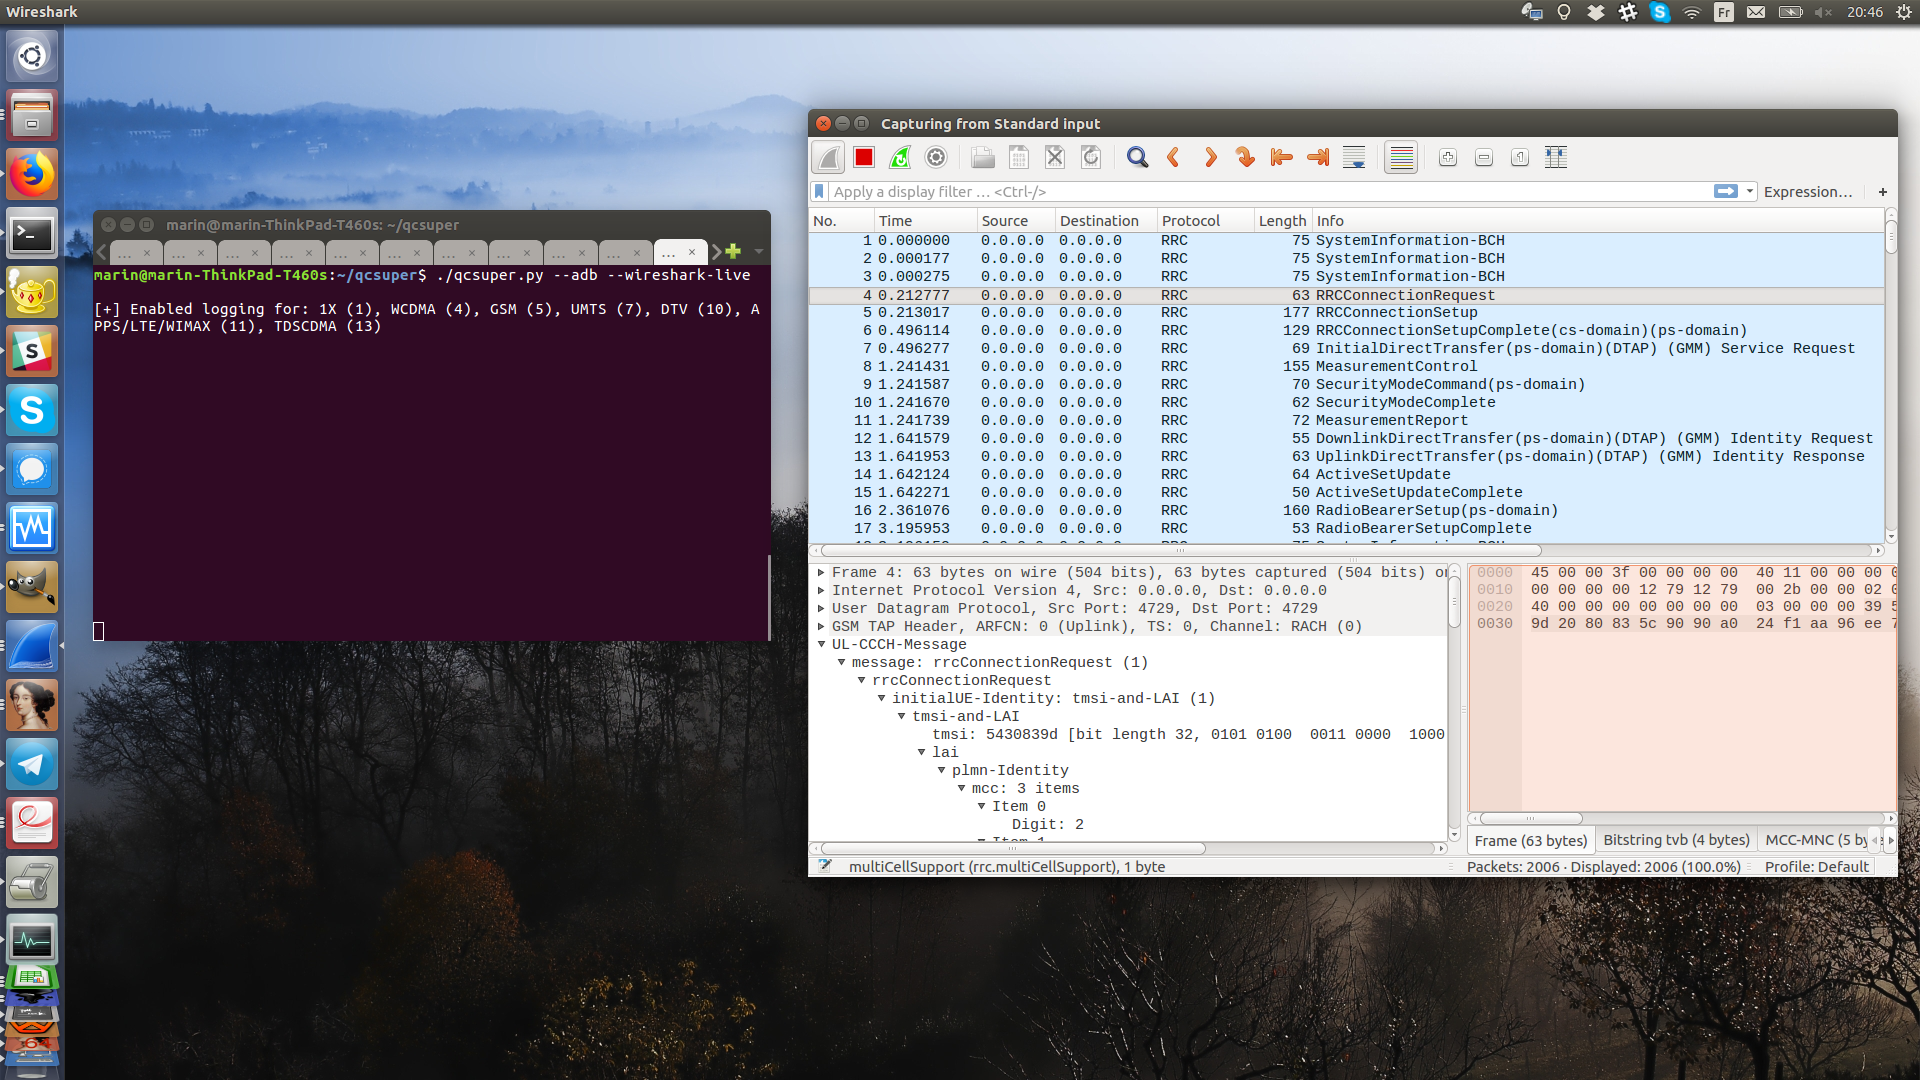 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
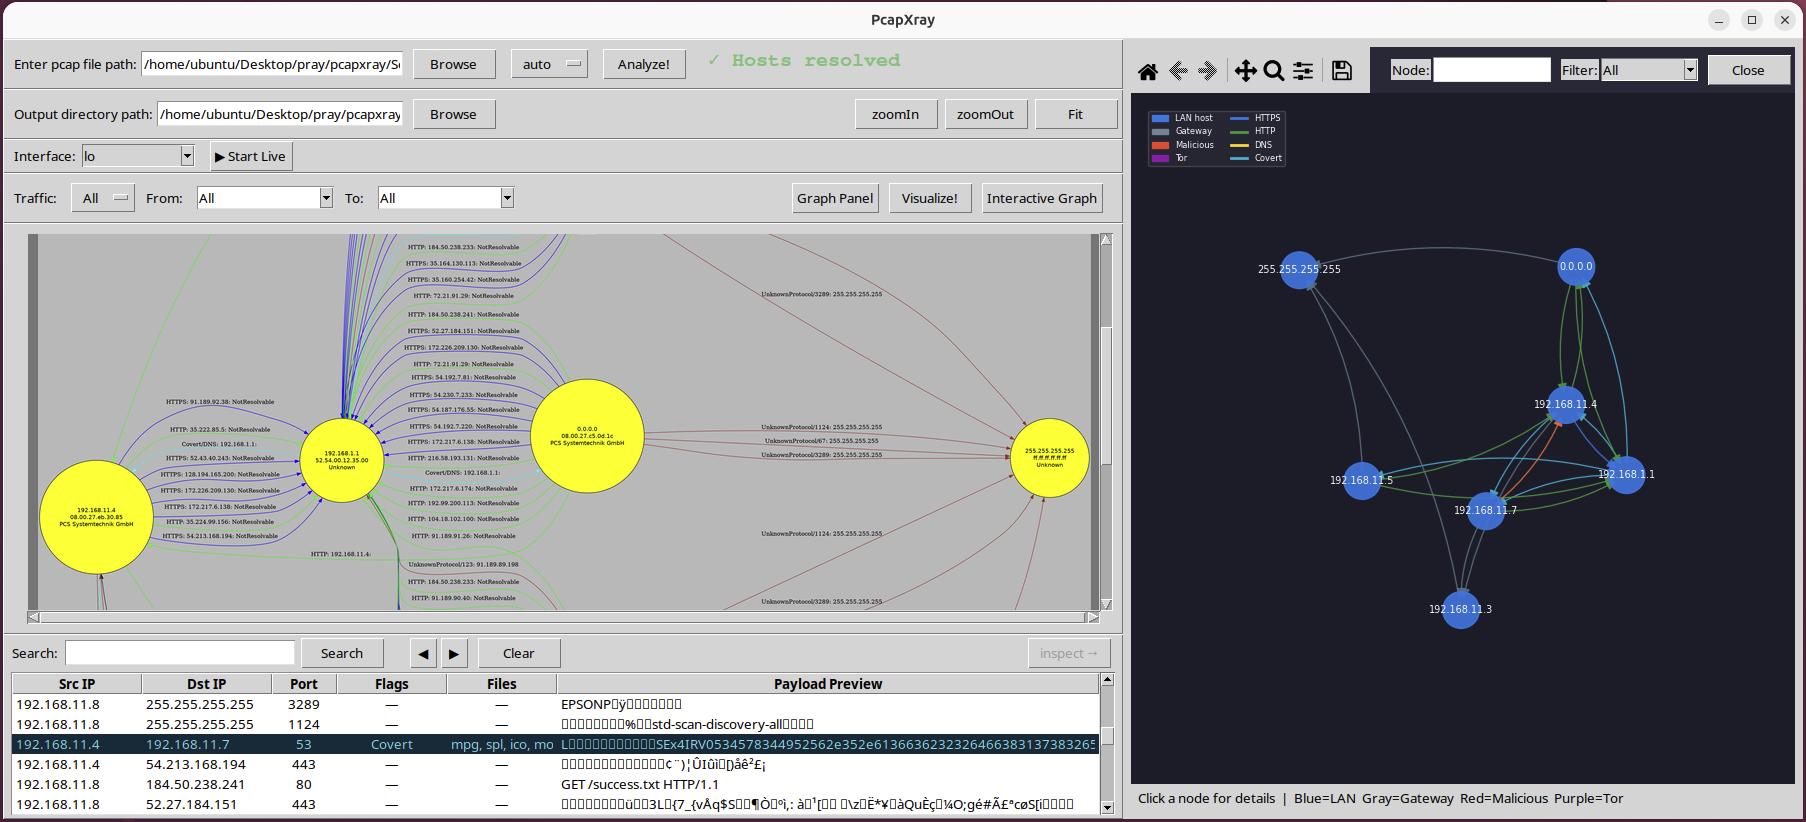 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
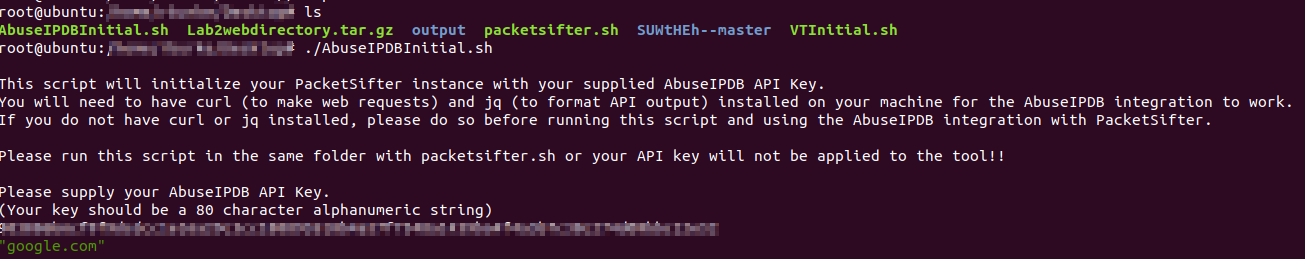 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 omriher/captipper
Malicious HTTP traffic explorer