
Wireshark
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
dns-analysisforensicsnetwork-forensics+3
1.6k
wireshark/wiresharkWireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
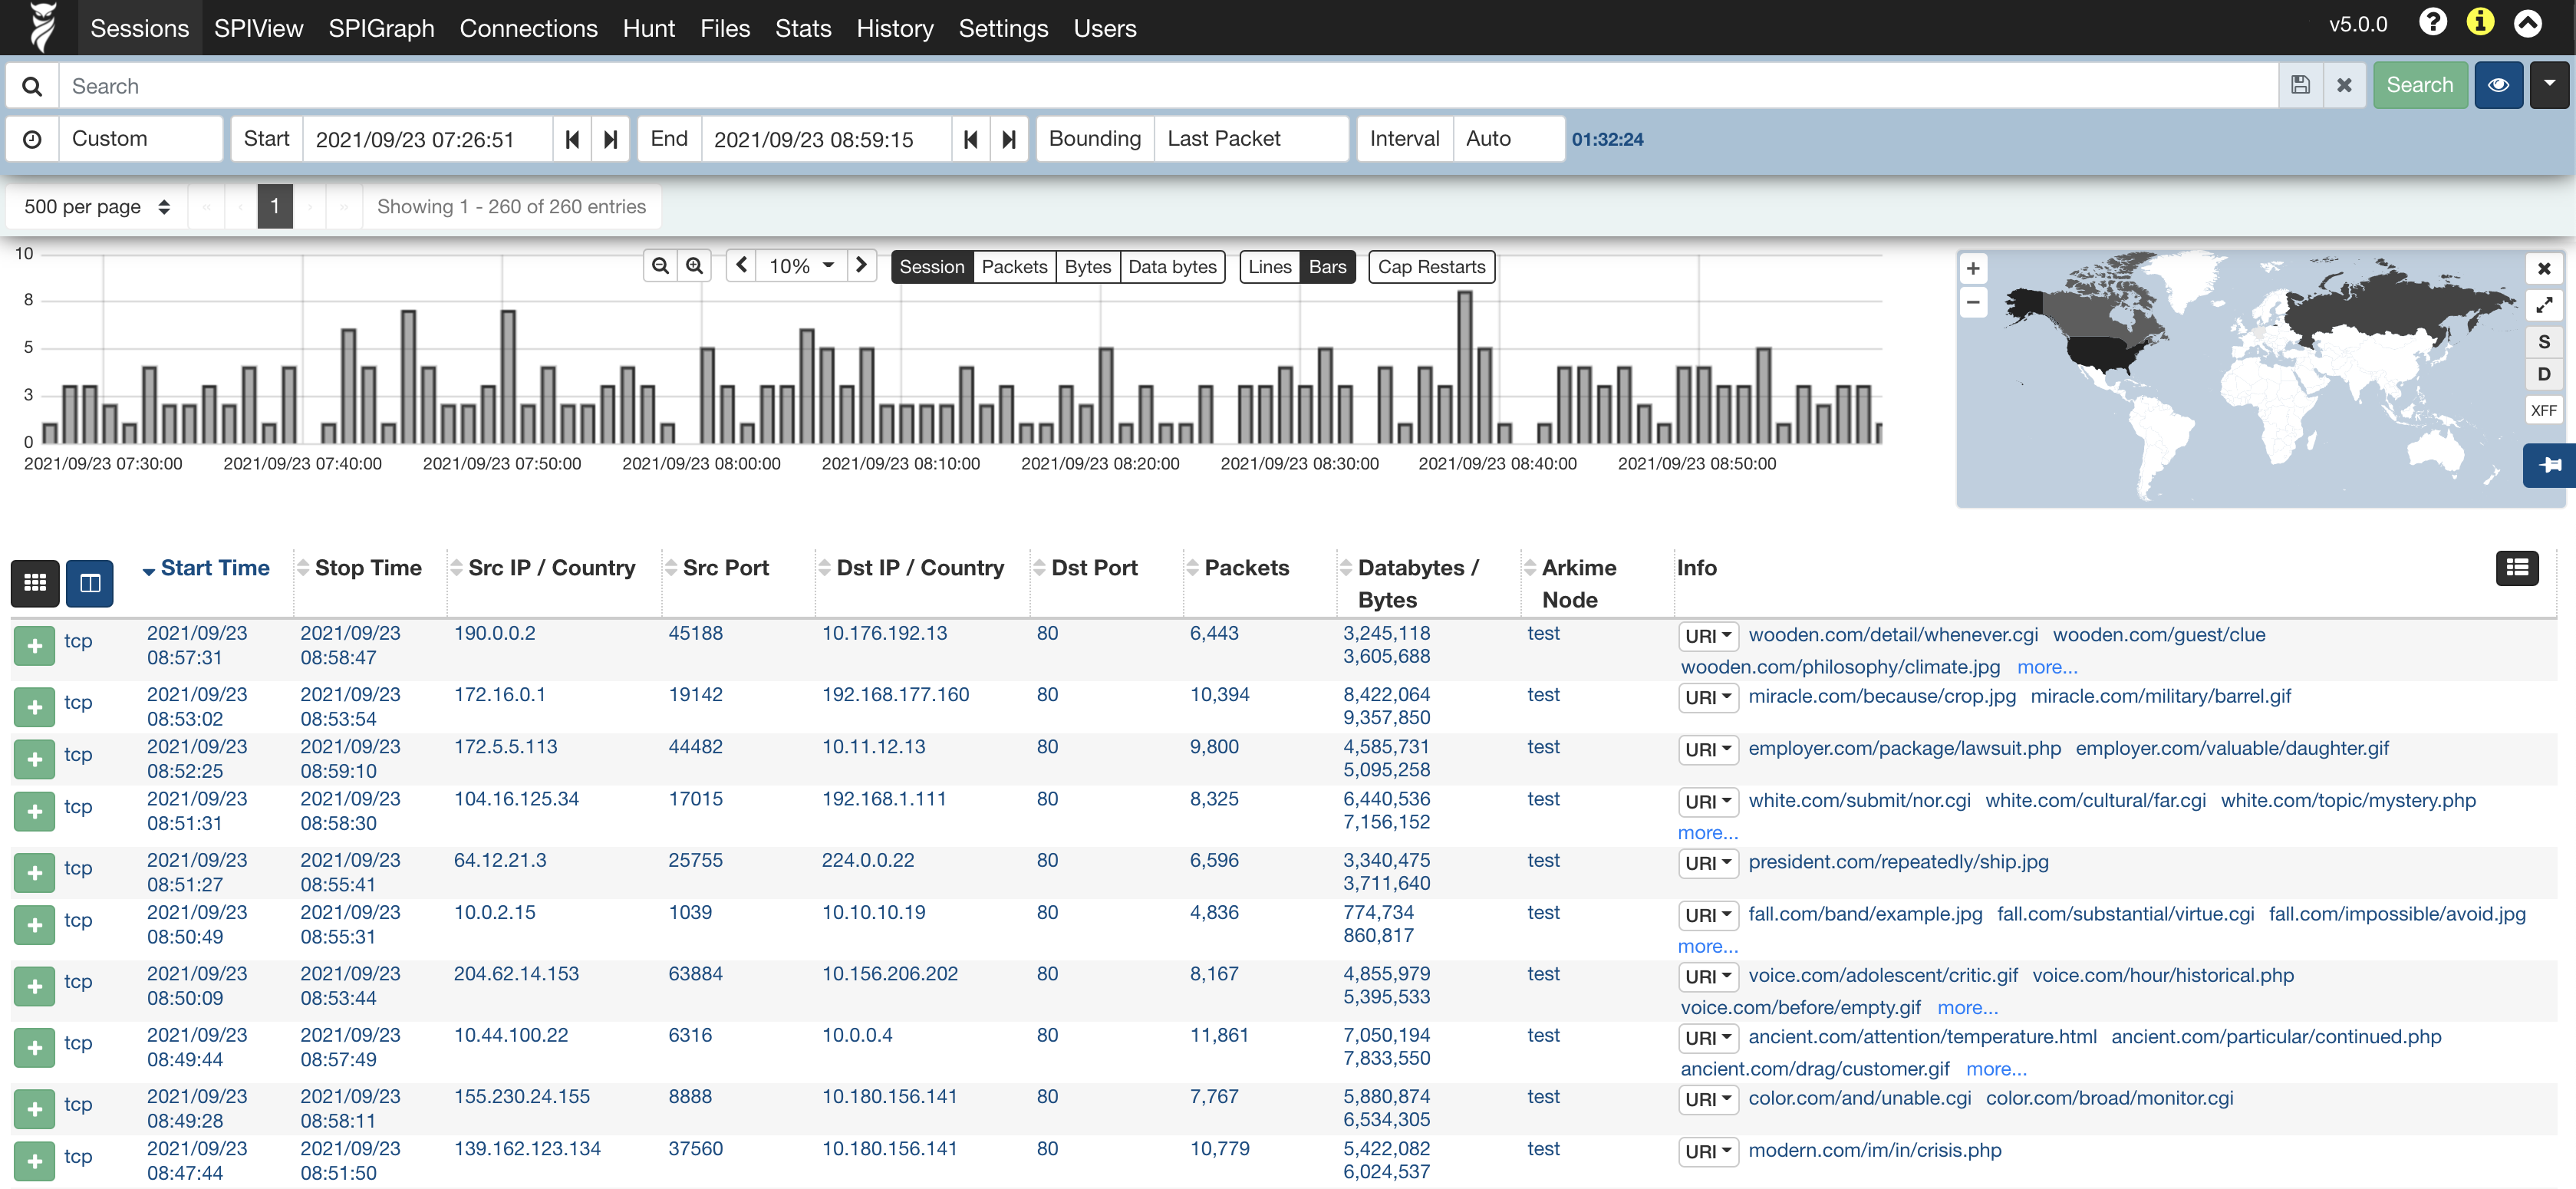 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 darnellwashingtonjr94-art/sandb0x-xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
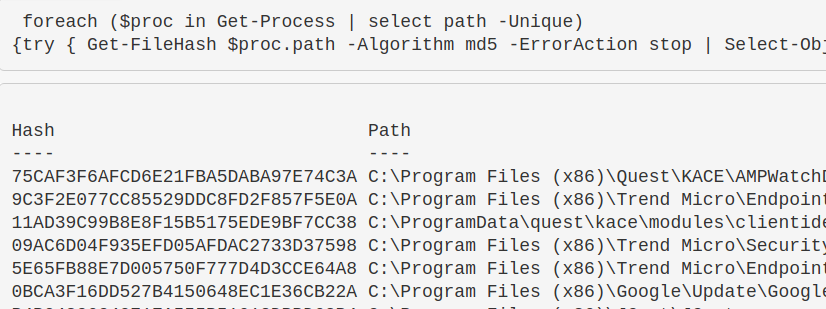 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
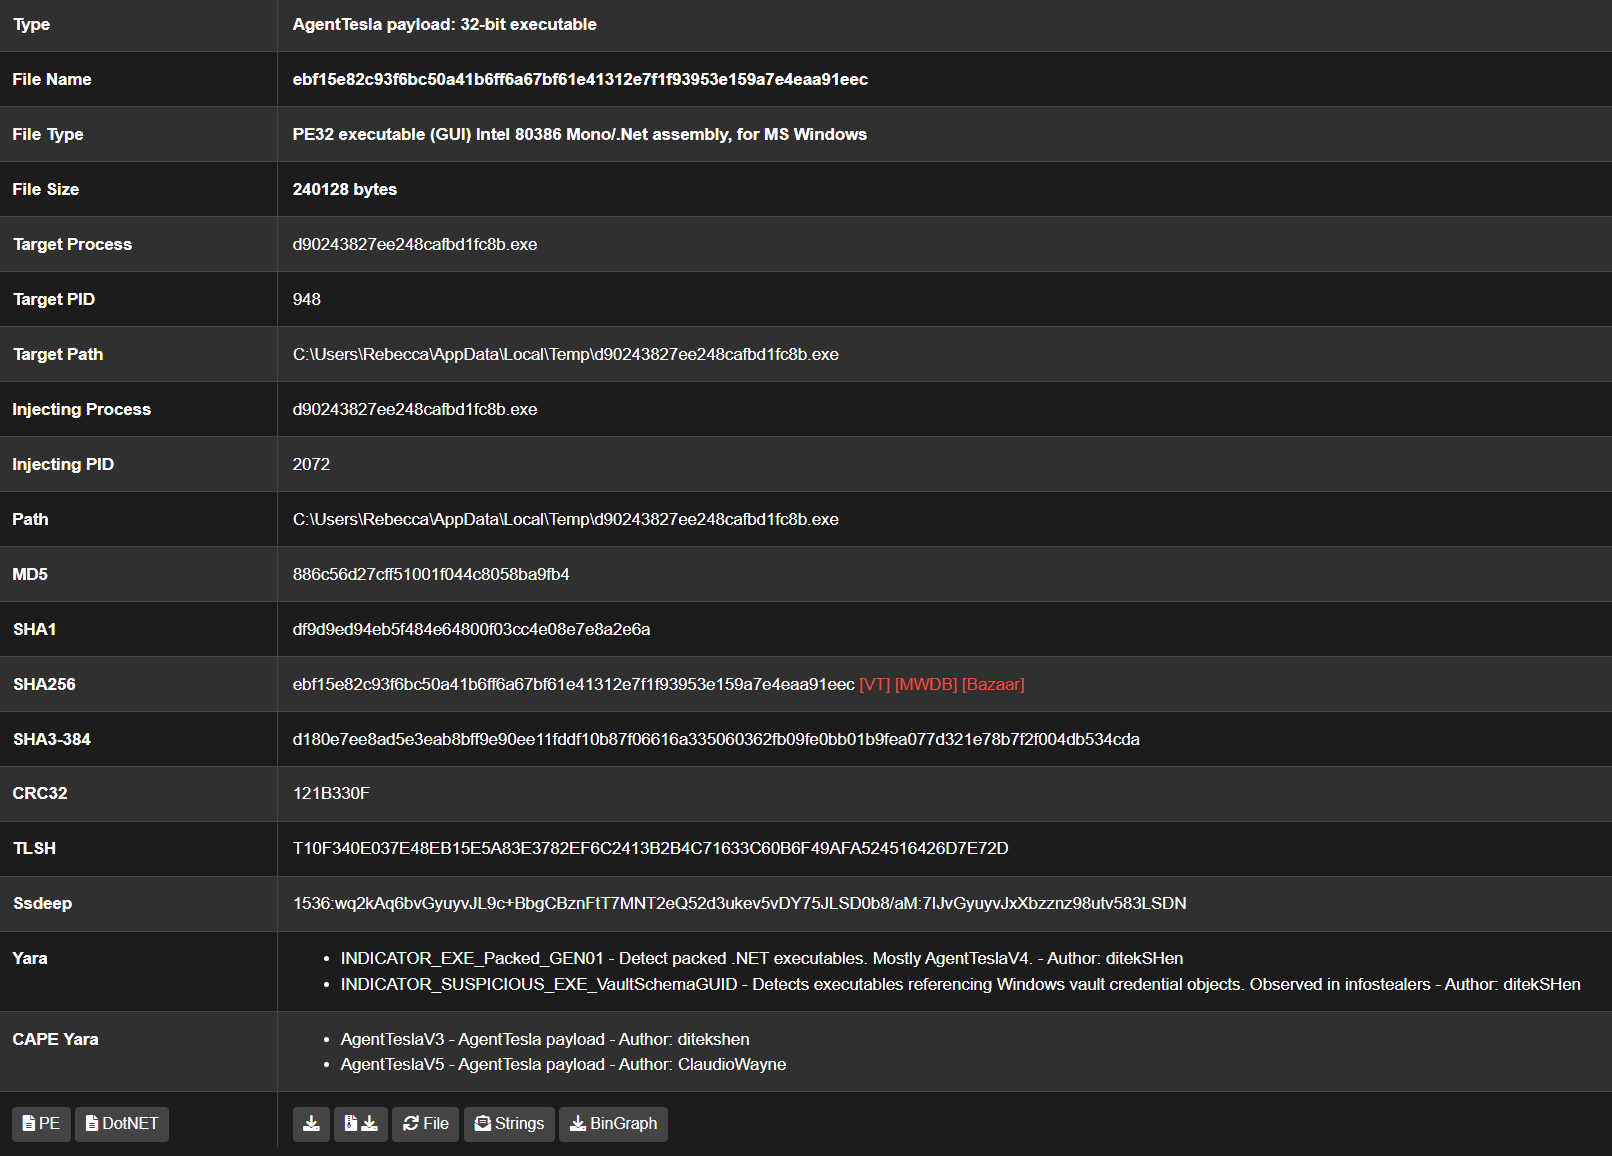 kevoreilly/capev2
Malware Configuration And Payload Extraction