

timesketch
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k
google/timesketchCollaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards

 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
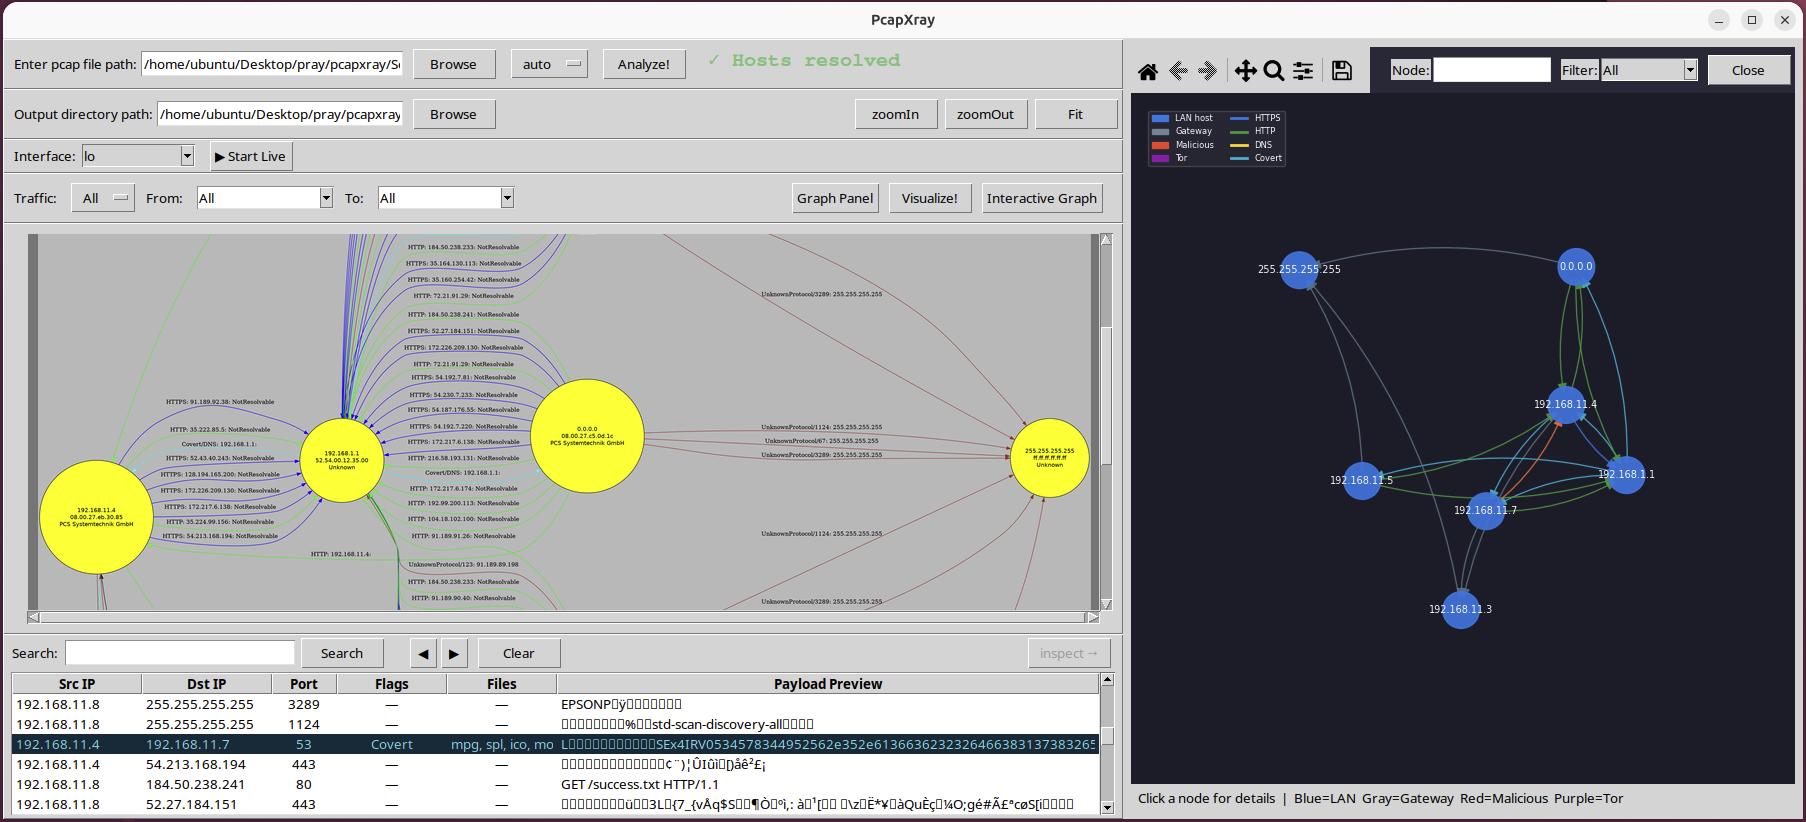 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
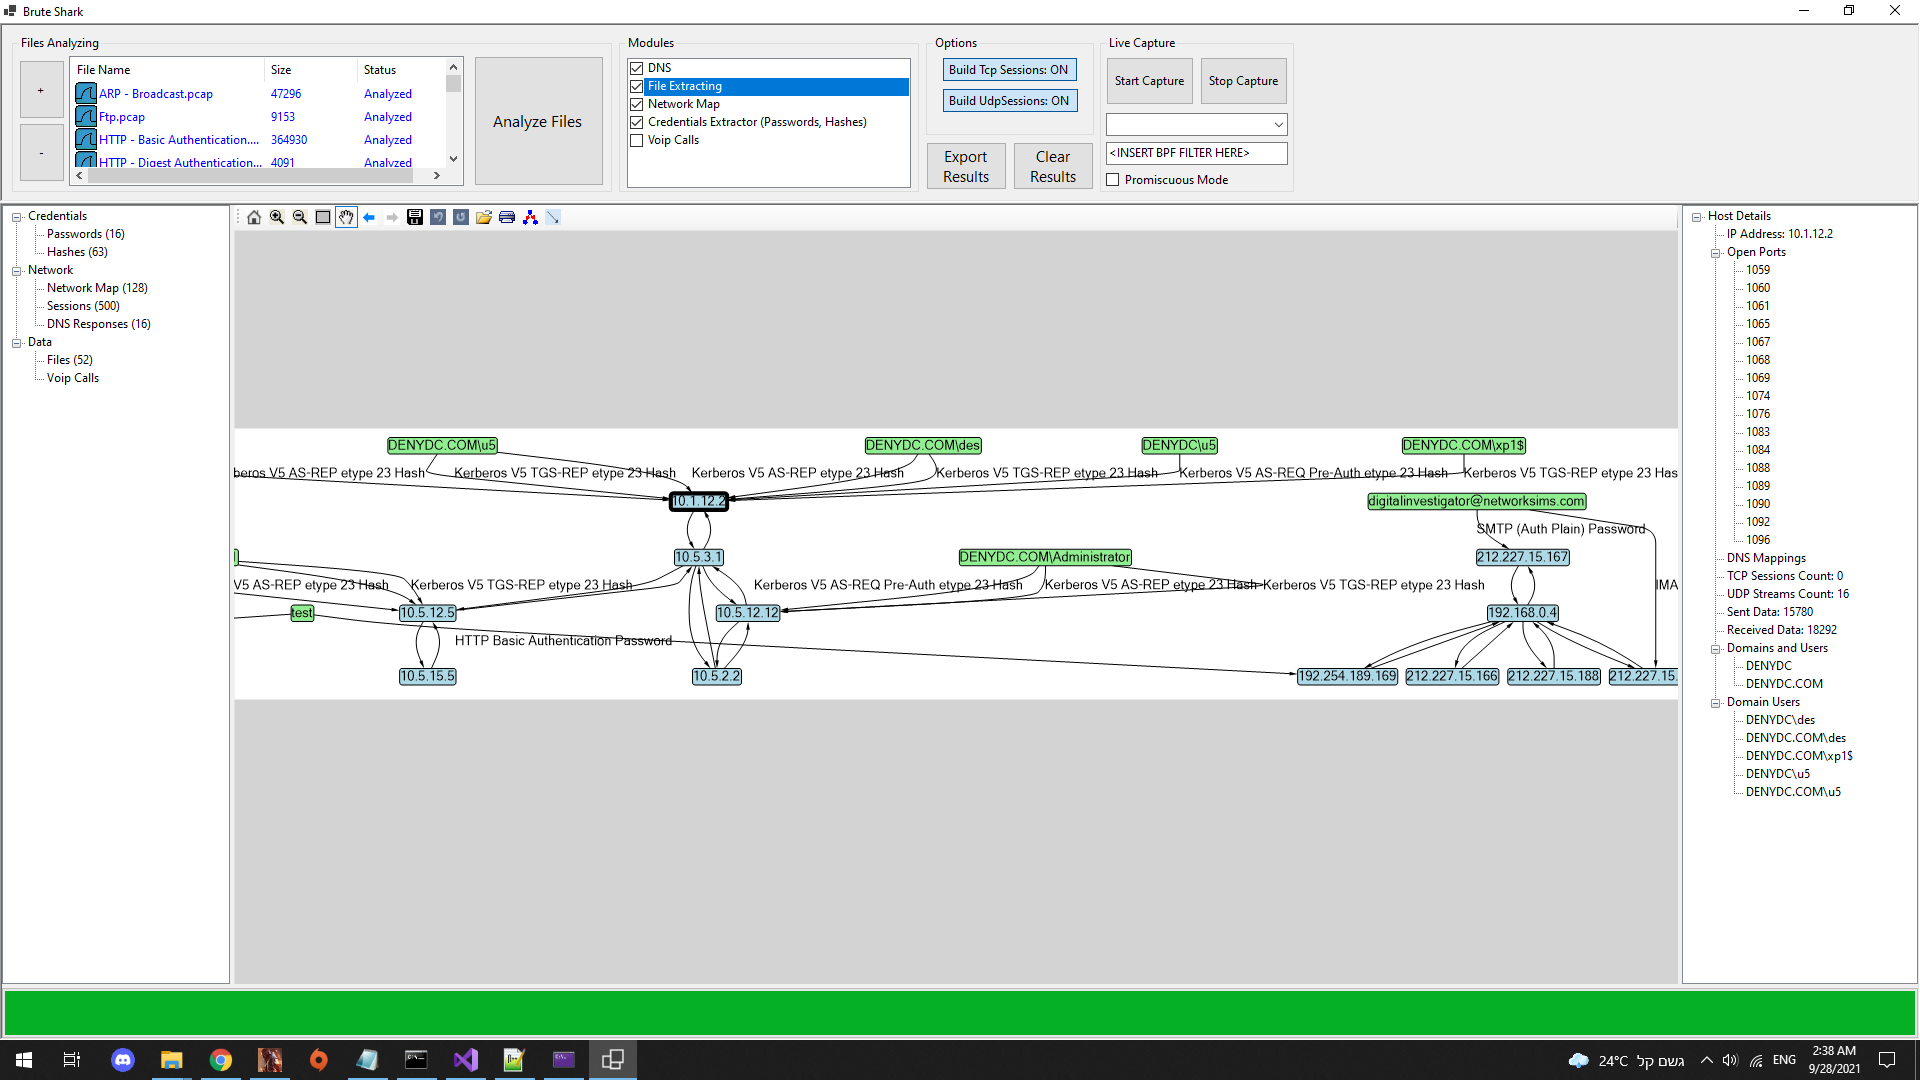
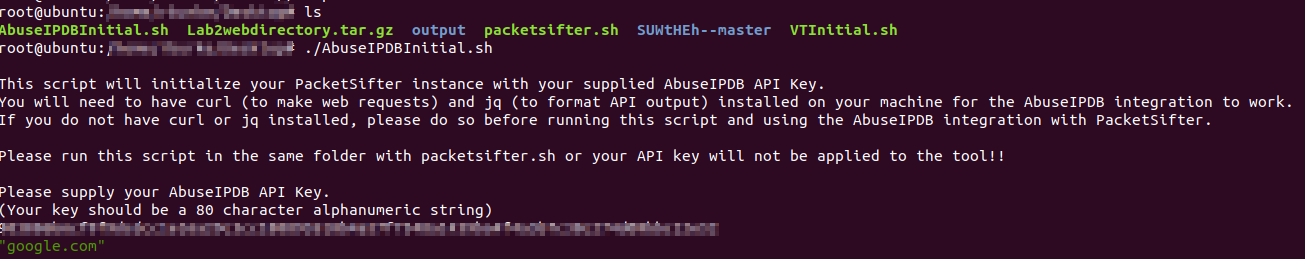 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
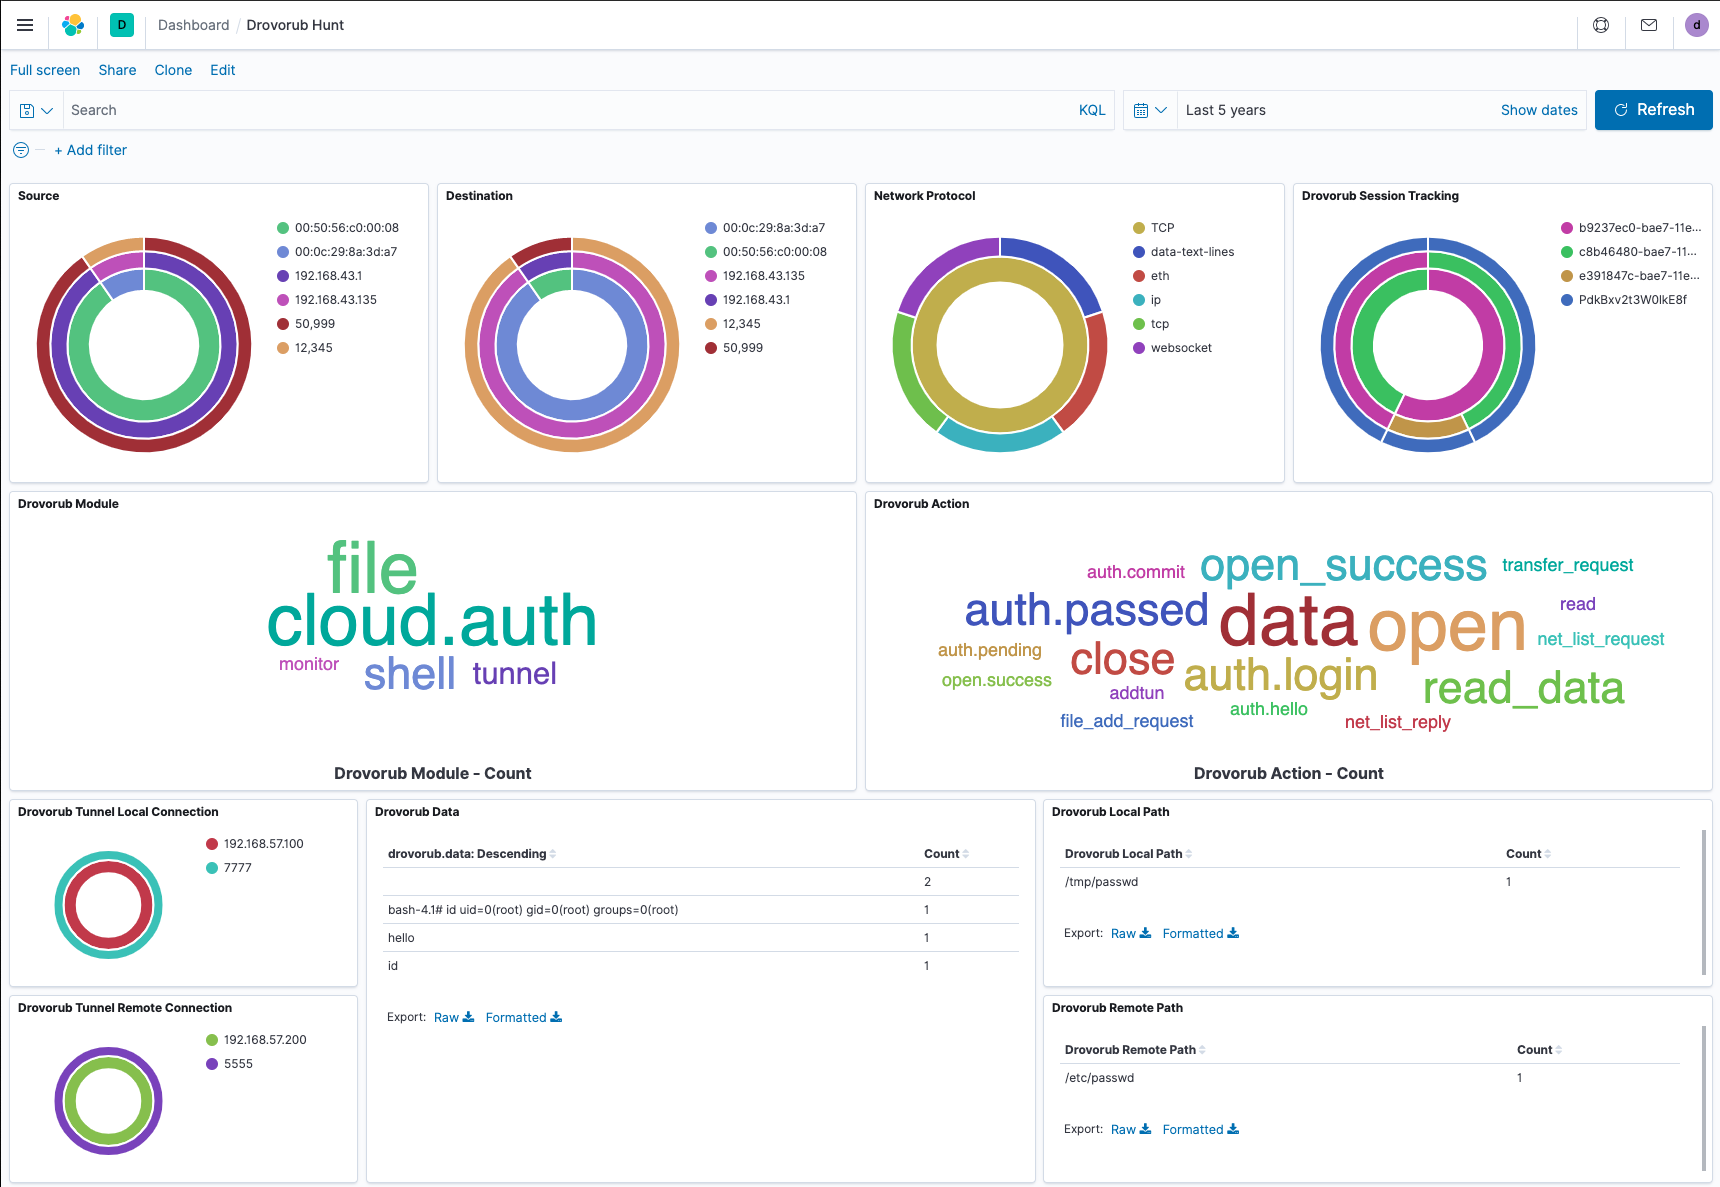 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
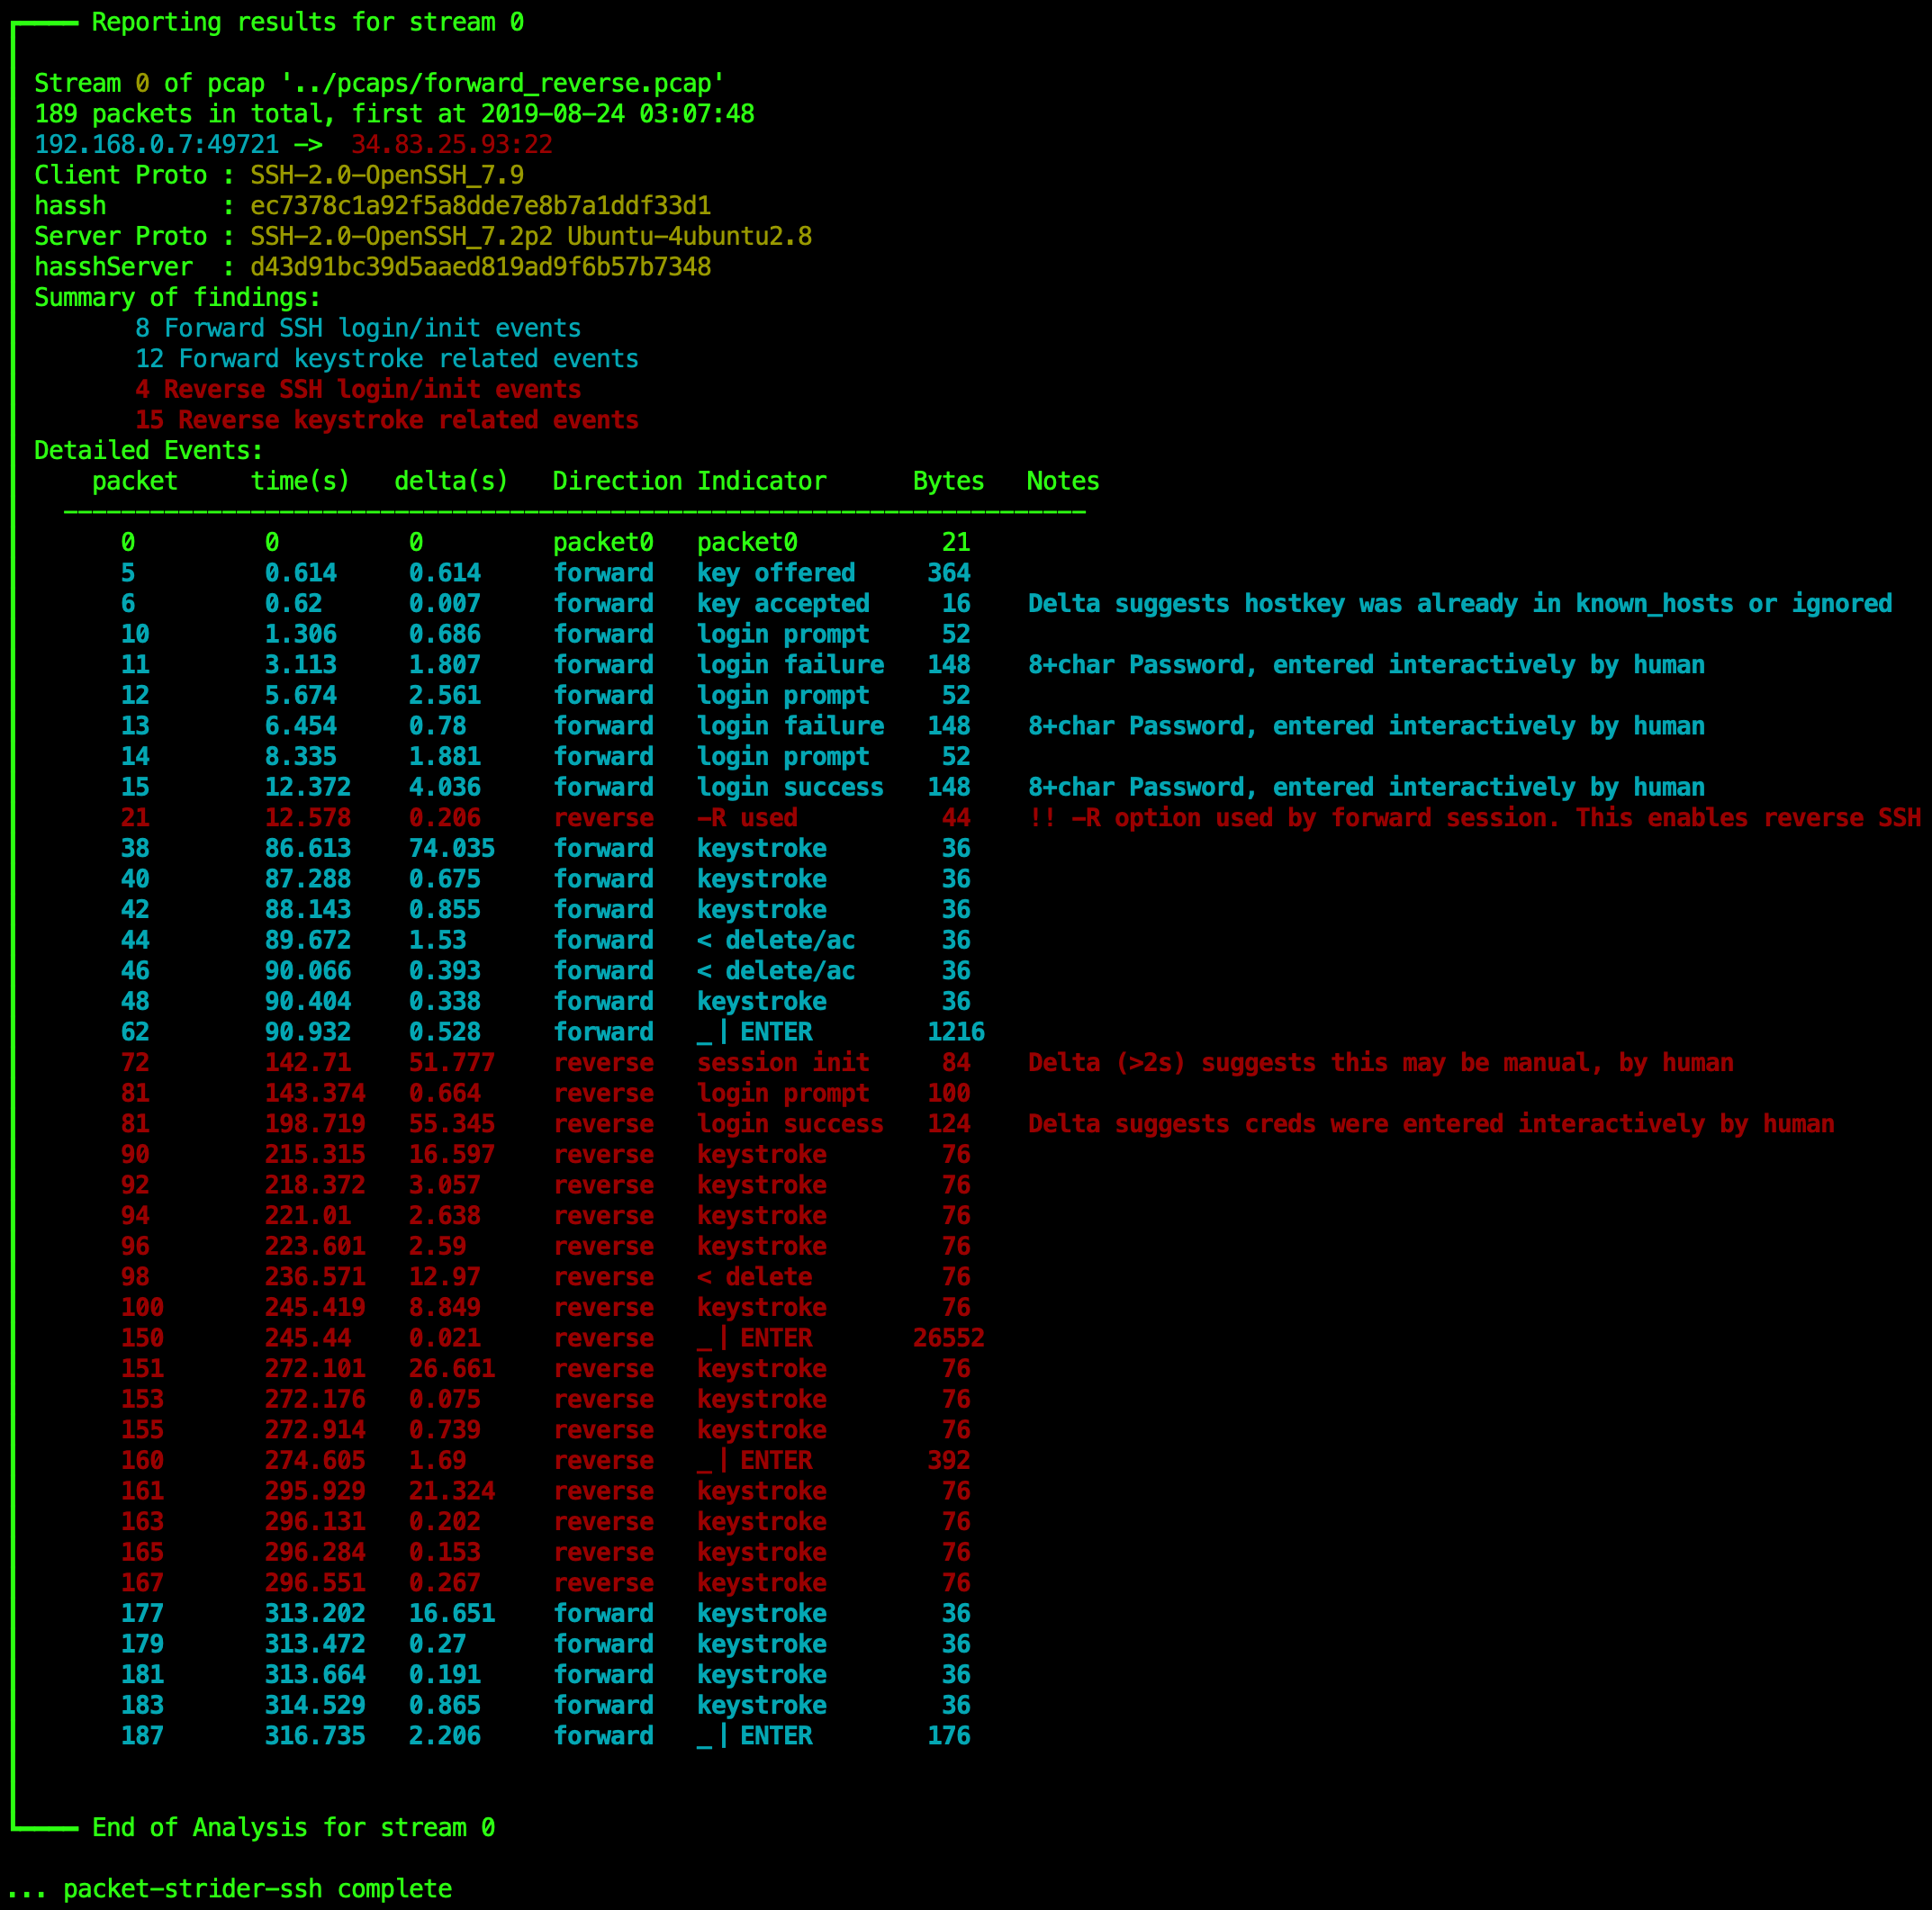 benjeems/packetstrider
A network packet forensics tool for SSH
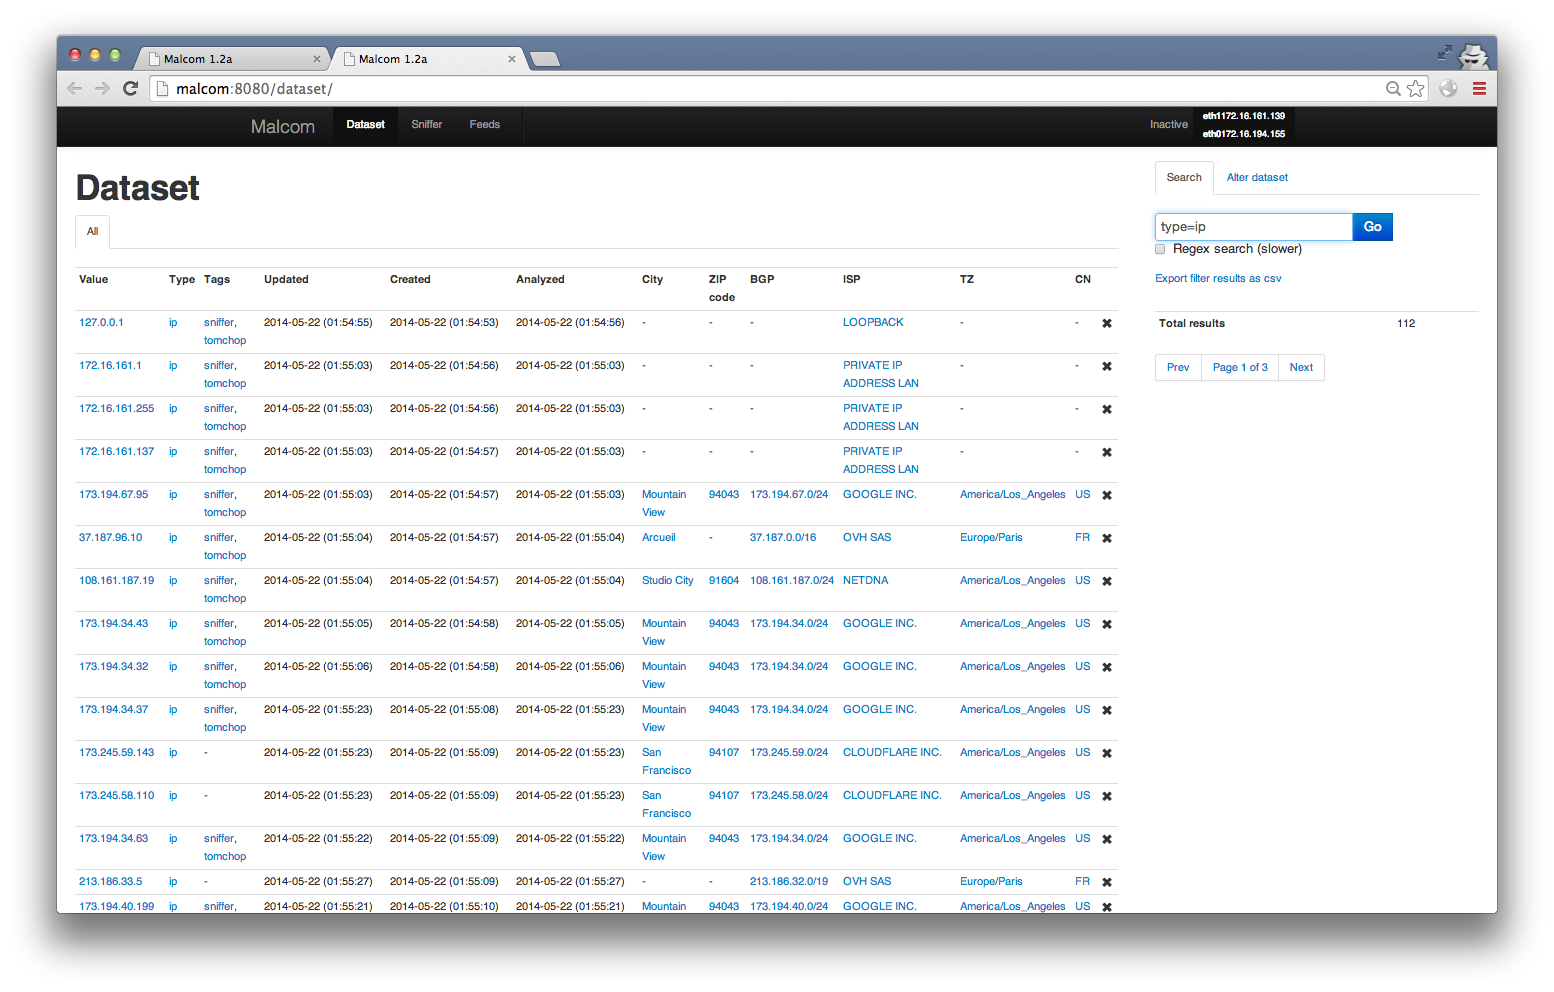 tomchop/malcom
Malcom - Malware Communications Analyzer