

DFIR-Companion
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
ai-securitydefensive-toolsdigital-forensics+9
182 days ago
hasamba/dfir-companionDFIR forensics companion server + capture extension
 prox0959/omnitriage
Zero-dependency, sub-second Windows live digital forensics & incident response (DFIR) triage engine for USB responders.
 mohamedbrek/soc335-cve-2024-49138-exploitation-detected
LetsDefend SOC lab investigating CVE-2024-49138 and related malicious activity.
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 google/gopacket
Provides packet processing capabilities for Go
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 darnellwashingtonjr94-art/sandb0x-xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
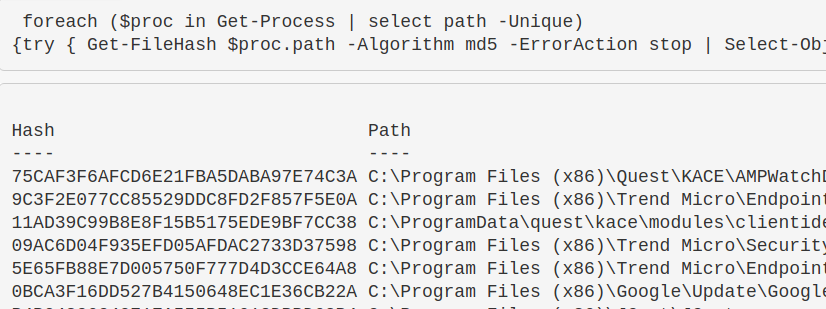 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 awakecoding/wireshark-rdp
Wireshark RDP resources
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.