
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
gopacket preview

gopacket

GitHubgoogle/gopacket

Provides packet processing capabilities for Go

network-forensicsnetwork-securitypacket-sniffing-analysis+1
6.8k
1 year ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k18h 30m ago
keepass-exfil-forensics preview

keepass-exfil-forensics

GitHubpugazhendii22/keepass-exfil-forensics

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
ctfdata-exfiltrationdigital-forensics+6
1 month ago
RITA-J preview

RITA-J

GitHubcyb3r-monk/rita-j

Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.

anomaly-detectiondns-analysislog-analysis+3
2164 years ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
command-and-controlcryptographydigital-forensics+4
372 years ago
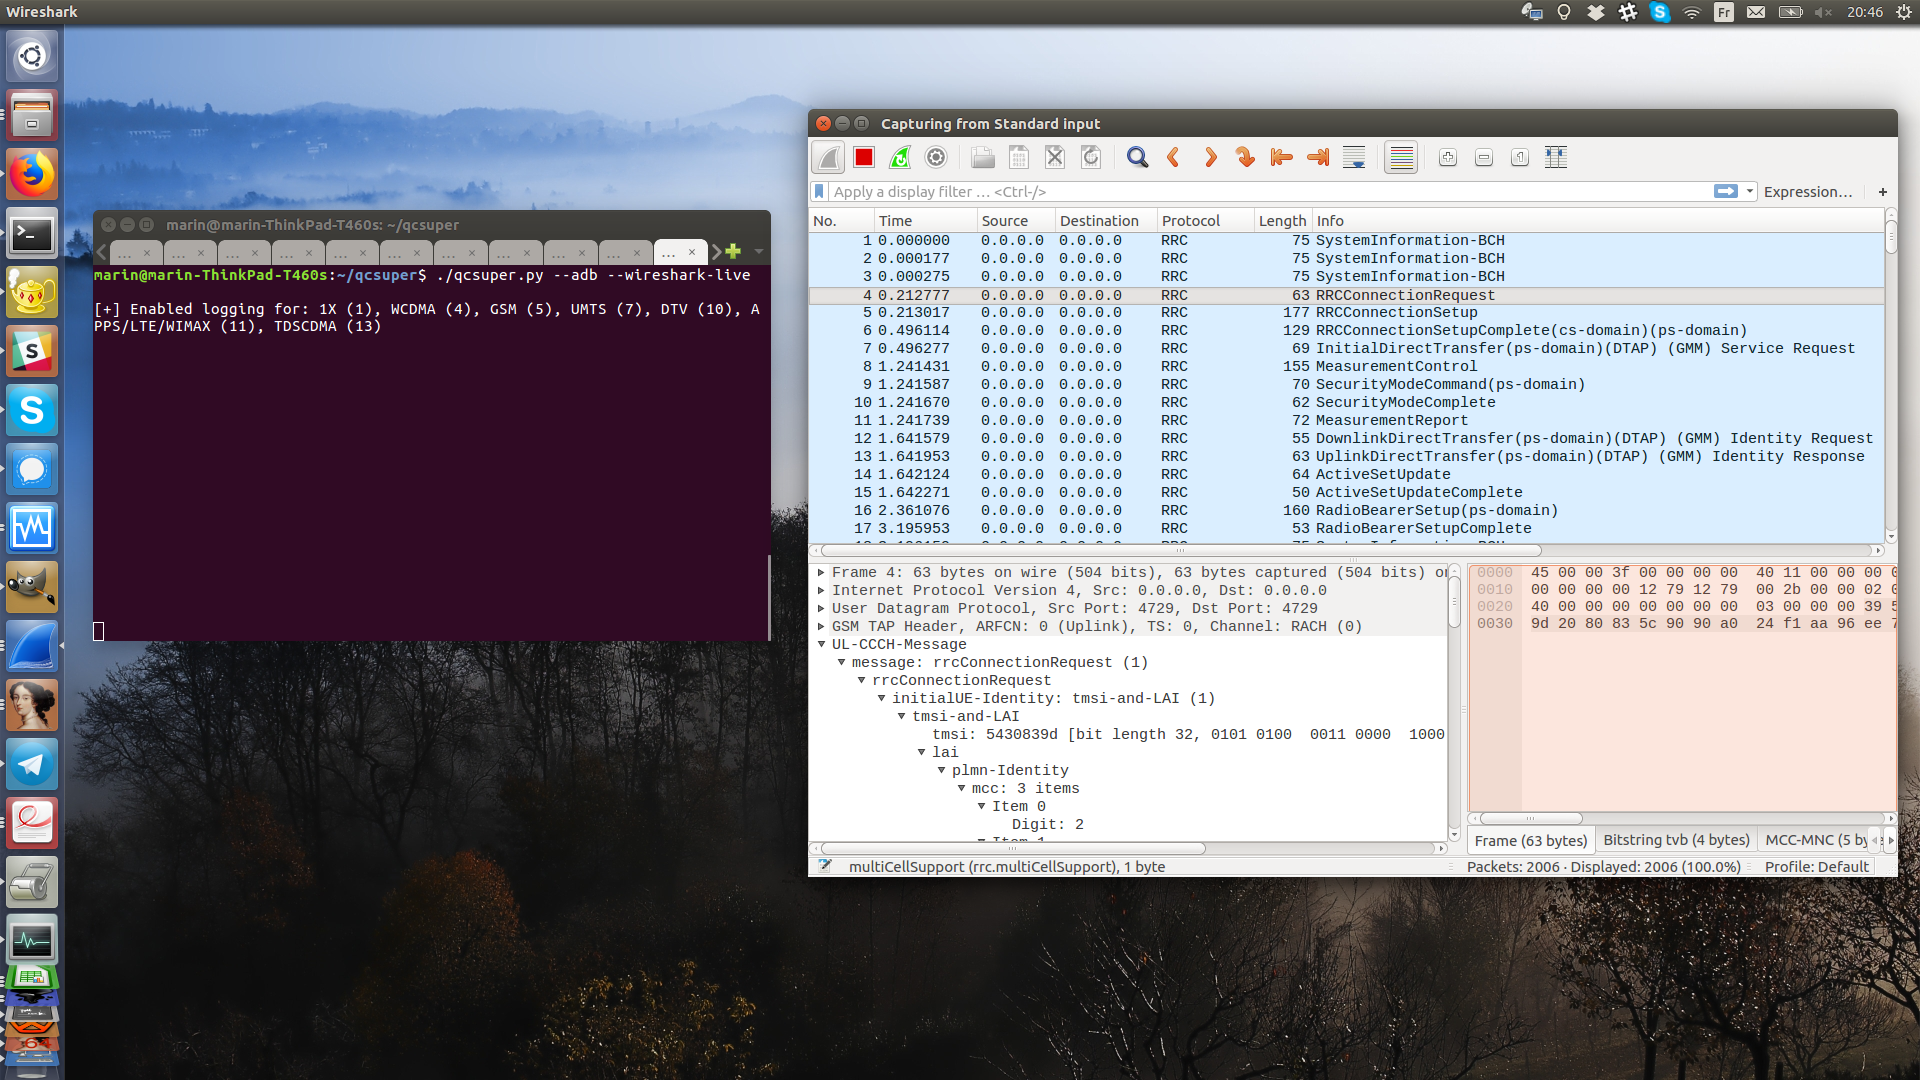
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.6k1 month ago
CVE-2019-11043-Vulnerability preview

CVE-2019-11043-Vulnerability

GitHubmagentabear/cve-2019-11043-vulnerability

Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…

educationexploitationlabs-practice+8
9 months ago
suricata preview

suricata

GitHuboisf/suricata

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
anomaly-detectionanti-botdefensive-tools+9
6.6k1 month ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

Selective protocol extractor from PCAPs or interfaces

incident-responsenetwork-forensicsnetwork-security+1
511 years ago
pcap-burp preview

pcap-burp

GitHubnccgroup/pcap-burp

Pcap importer for Burp
network-forensicspacket-sniffing-analysispenetration-testing+2
1145 years ago
ndff preview

ndff

GitHubknqyf263/ndff

A flow-based network monitor with Deep Packet Inspection

dns-analysislog-analysisnetwork-forensics+2
289 years ago
CorelightForSplunk preview

CorelightForSplunk

GitHubcorelight/corelightforsplunk

Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.

anomaly-detectionincident-responselog-analysis+4
21 year ago
zeek-community-id preview

zeek-community-id

GitHubcorelight/zeek-community-id

Zeek support for Community ID flow hashing.
log-analysisnetwork-forensicsnetwork-security+1
373 years ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol

intrusion-detectionlog-analysisnetwork-forensics+2
115 years ago
zeek-spicy-ipsec preview

zeek-spicy-ipsec

GitHubcorelight/zeek-spicy-ipsec

A Zeek IPSec protocol analyzer based on Spicy.

intrusion-detectionnetwork-forensicsnetwork-security+1
811 months ago
zeek-spicy-ospf preview

zeek-spicy-ospf

GitHubcorelight/zeek-spicy-ospf

A Zeek OSPF packet analyzer based on Spicy.
anomaly-detectionnetwork-forensicsnetwork-mapping+2
81 year ago
zeek-spicy-wireguard preview

zeek-spicy-wireguard

GitHubcorelight/zeek-spicy-wireguard

A Zeek Wireguard protocol analyzer based on Spicy.
network-forensicsnetwork-securitypacket-sniffing-analysis
76 months ago
ipdecap preview

ipdecap

GitHublpefferkorn/ipdecap

Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…

encryption-decryption-toolsforensicsnetwork-forensics+3
357 years ago
Previous1234Next