

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
honeypot-data preview

honeypot-data

GitHub0x4d31/honeypot-data

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…

incident-responseinformation-gatheringioc-management+4
44
8 days ago
SecLog preview

SecLog

GitHubseclog-open/seclog

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
anomaly-detectiondynamic-analysis-sandboxingeducation+6
211 days ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
122 months ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k18h 14m ago
security-writeups preview

security-writeups

GitHubalzeaty1/security-writeups

CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
ctfeducationlabs-practice+5
1 month ago
keepass-exfil-forensics preview

keepass-exfil-forensics

GitHubpugazhendii22/keepass-exfil-forensics

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…

ctfdata-exfiltrationdigital-forensics+6
2 months ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…

command-and-controlcryptographydigital-forensics+4
372 years ago
ACF preview

ACF

GitHubcyberhatcoil/acf

Android Connections Forensics
digital-forensicsmobile-forensicsnetwork-forensics+2
3310 years ago
Baskerville preview

Baskerville

GitHubnccgroup/baskerville

Selective protocol extractor from PCAPs or interfaces
incident-responsenetwork-forensicsnetwork-security+1
512 years ago
ipdecap preview

ipdecap

GitHublpefferkorn/ipdecap

Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
encryption-decryption-toolsforensicsnetwork-forensics+3
348 years ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
data-exfiltrationdigital-forensicsforensics+5
139 years ago
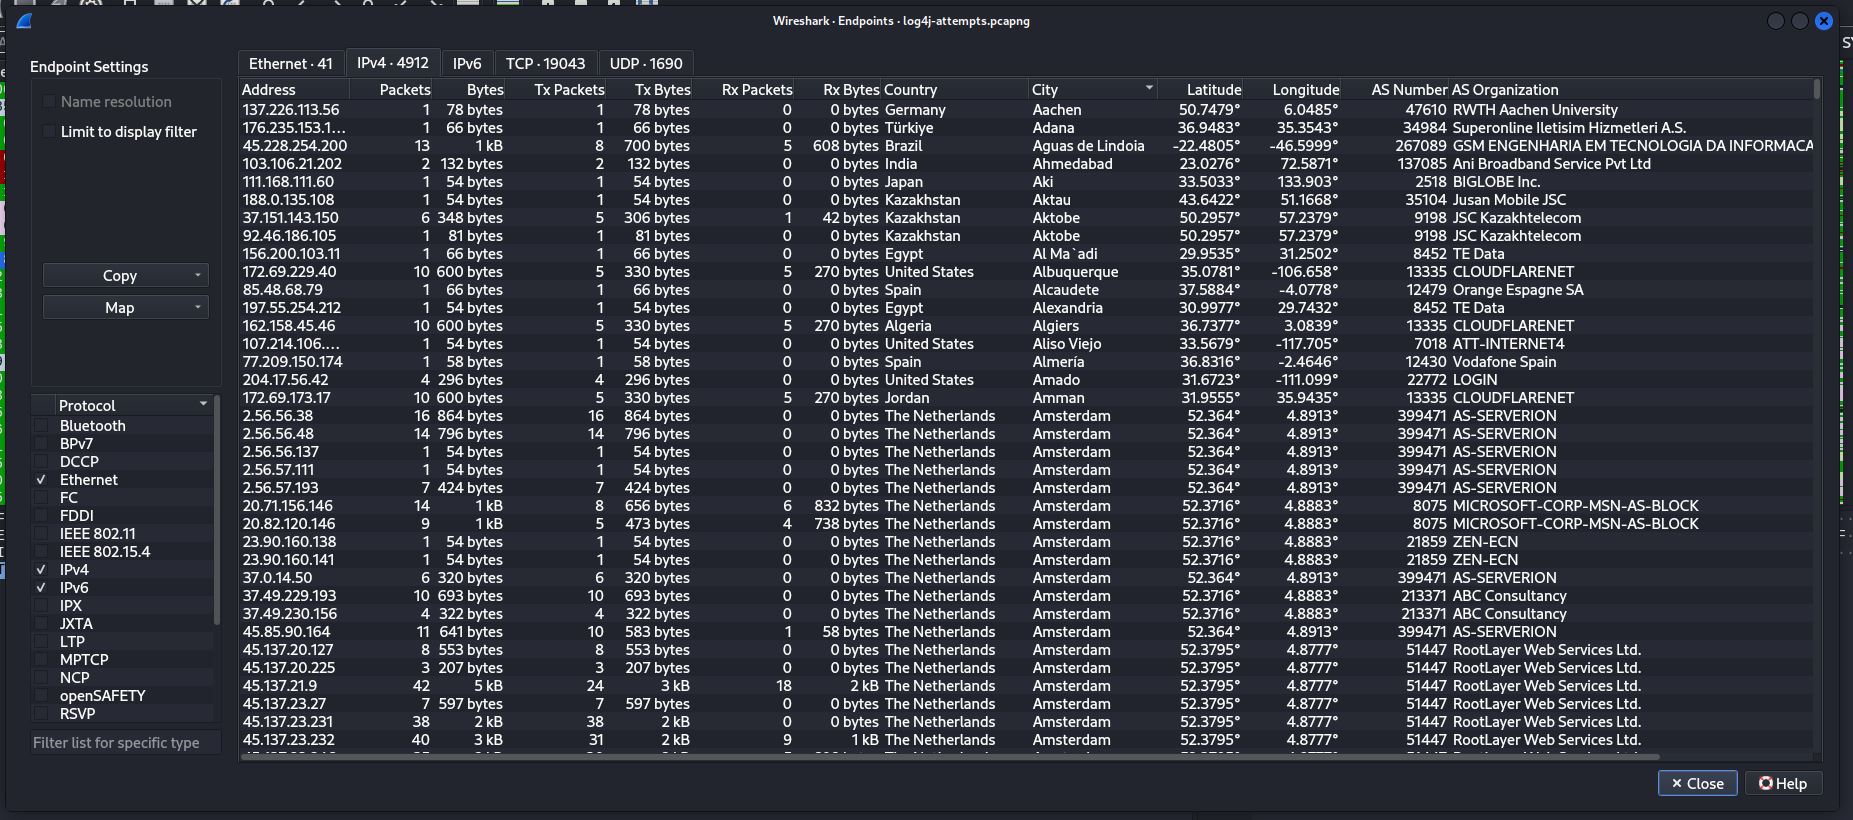
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
32 years ago
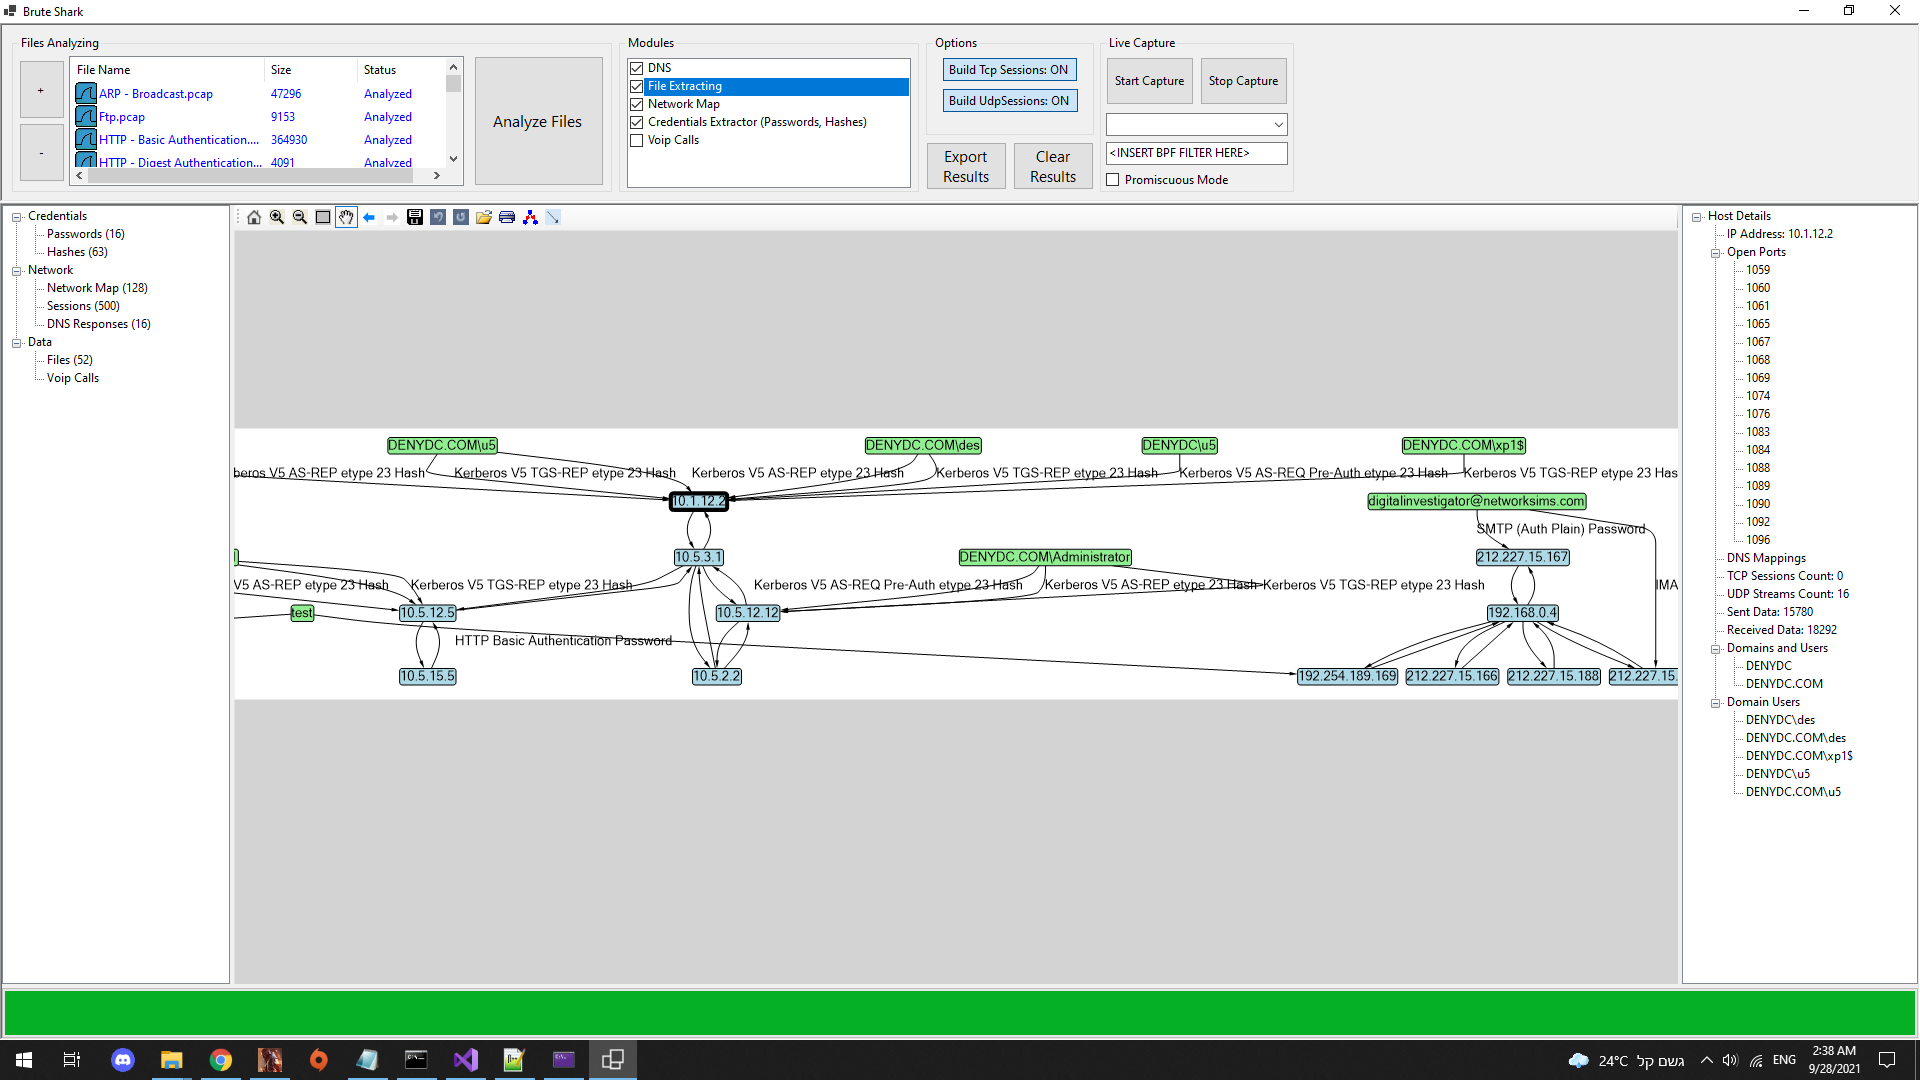
BruteShark preview

BruteShark

GitHubodedshimon/bruteshark

Network Analysis Tool

dns-analysisforensicshash-analysis+4
3.4k5 years ago
OpenWire-CVE-2023-46604-Investigation preview

OpenWire-CVE-2023-46604-Investigation

GitHubaelshimony-cloud/openwire-cve-2023-46604-investigation

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
command-and-controldigital-forensicsexploitation+7
4 months ago
Android-Projector-C2-Malware preview

Android-Projector-C2-Malware

GitHubkavan00/android-projector-c2-malware

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
android-securitycommand-and-controldigital-forensics+9
181 month ago
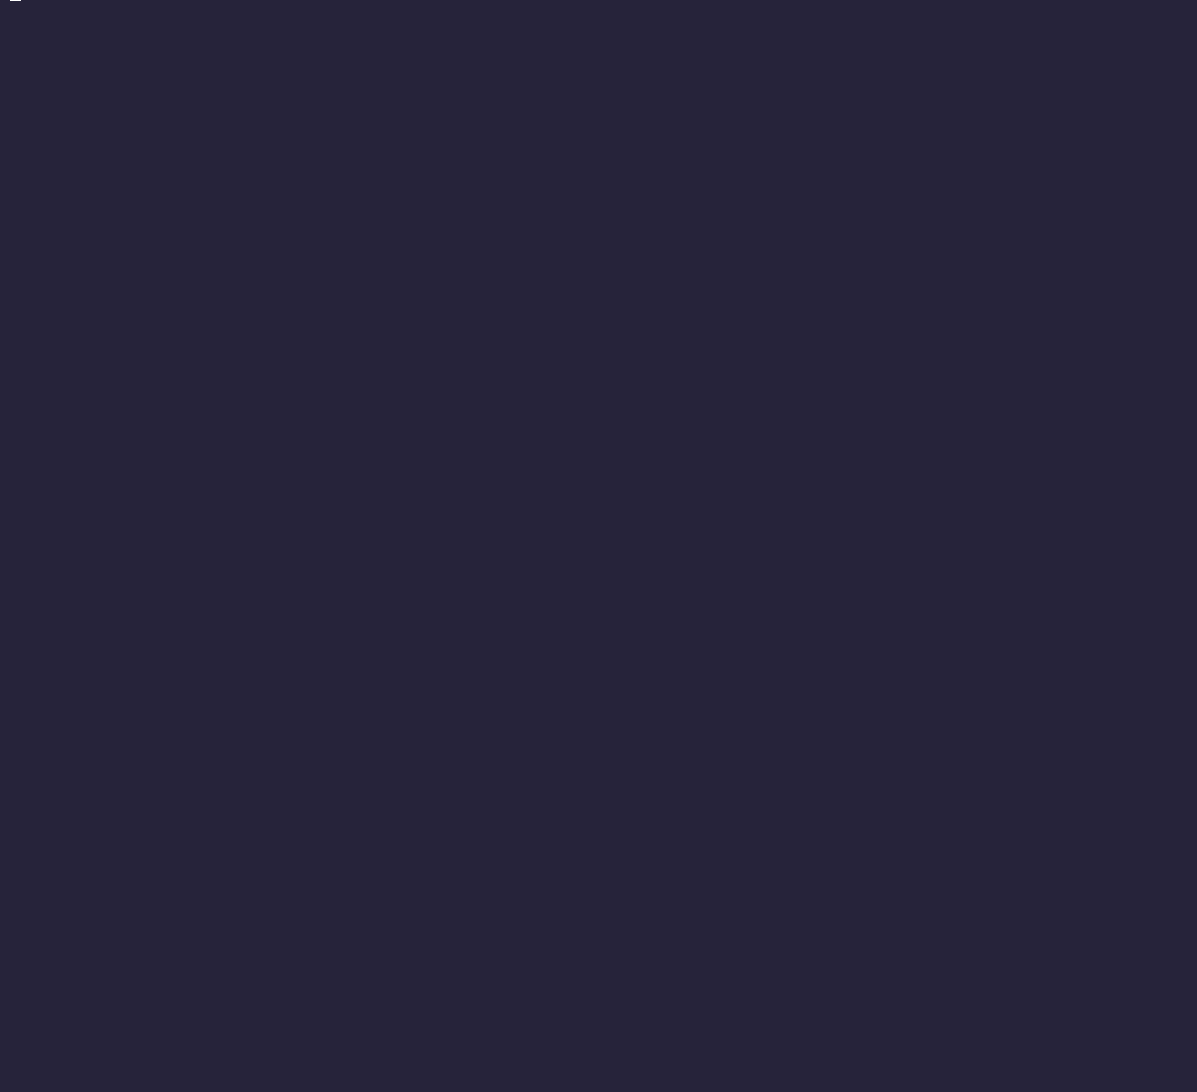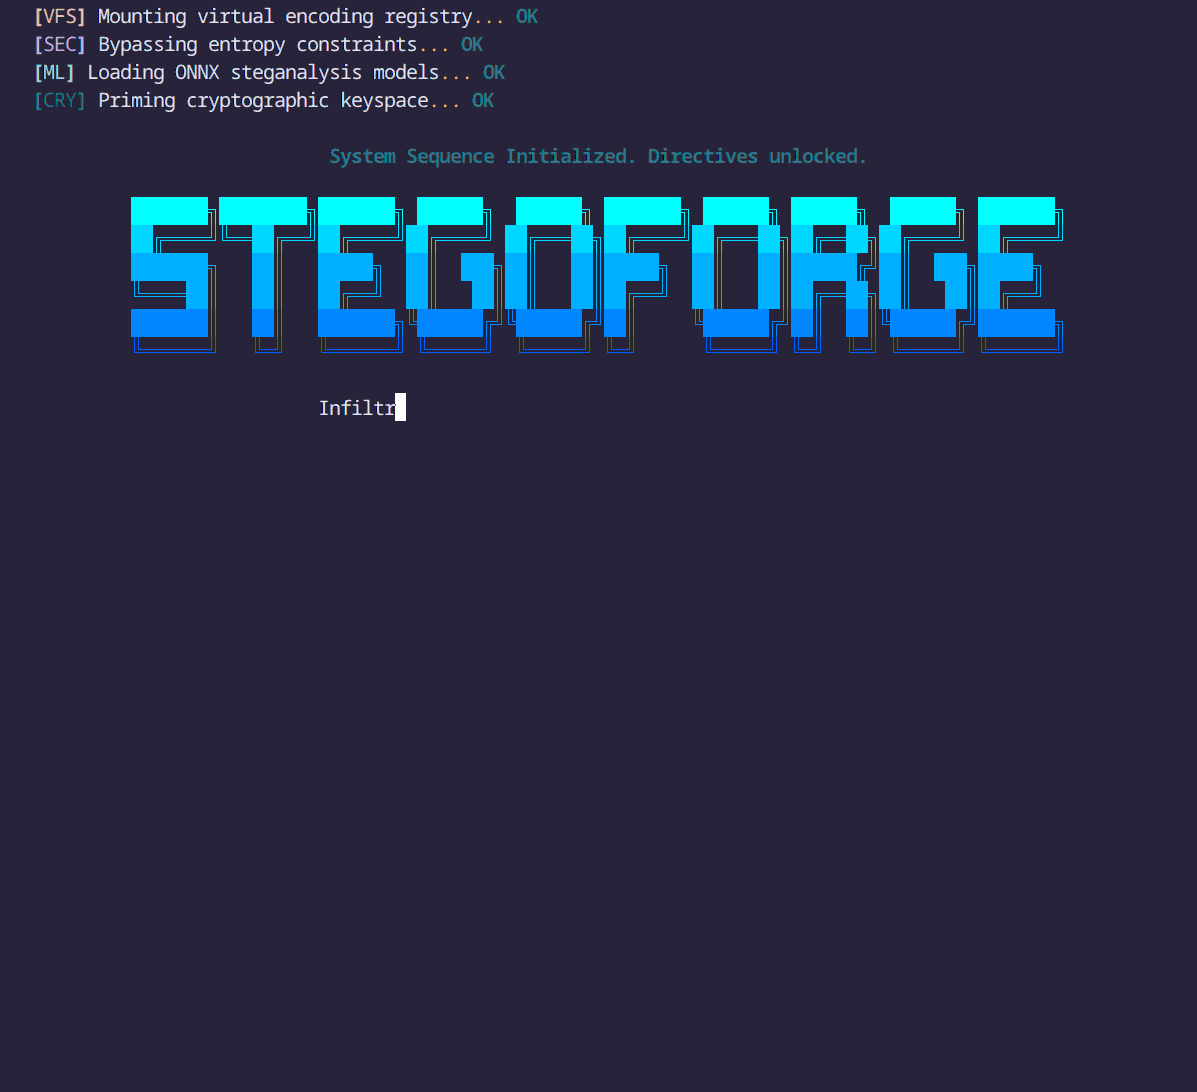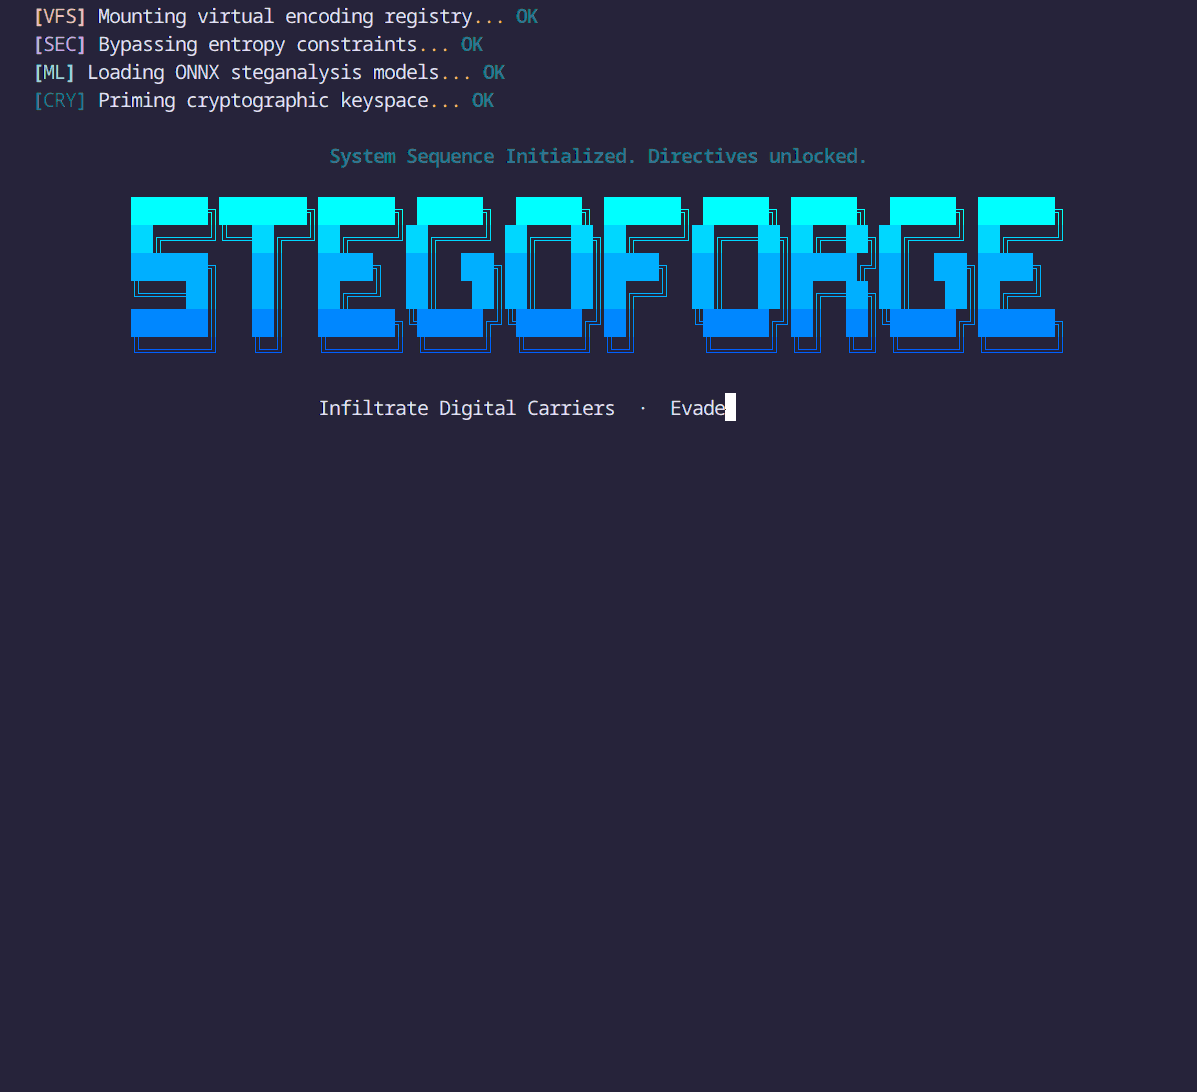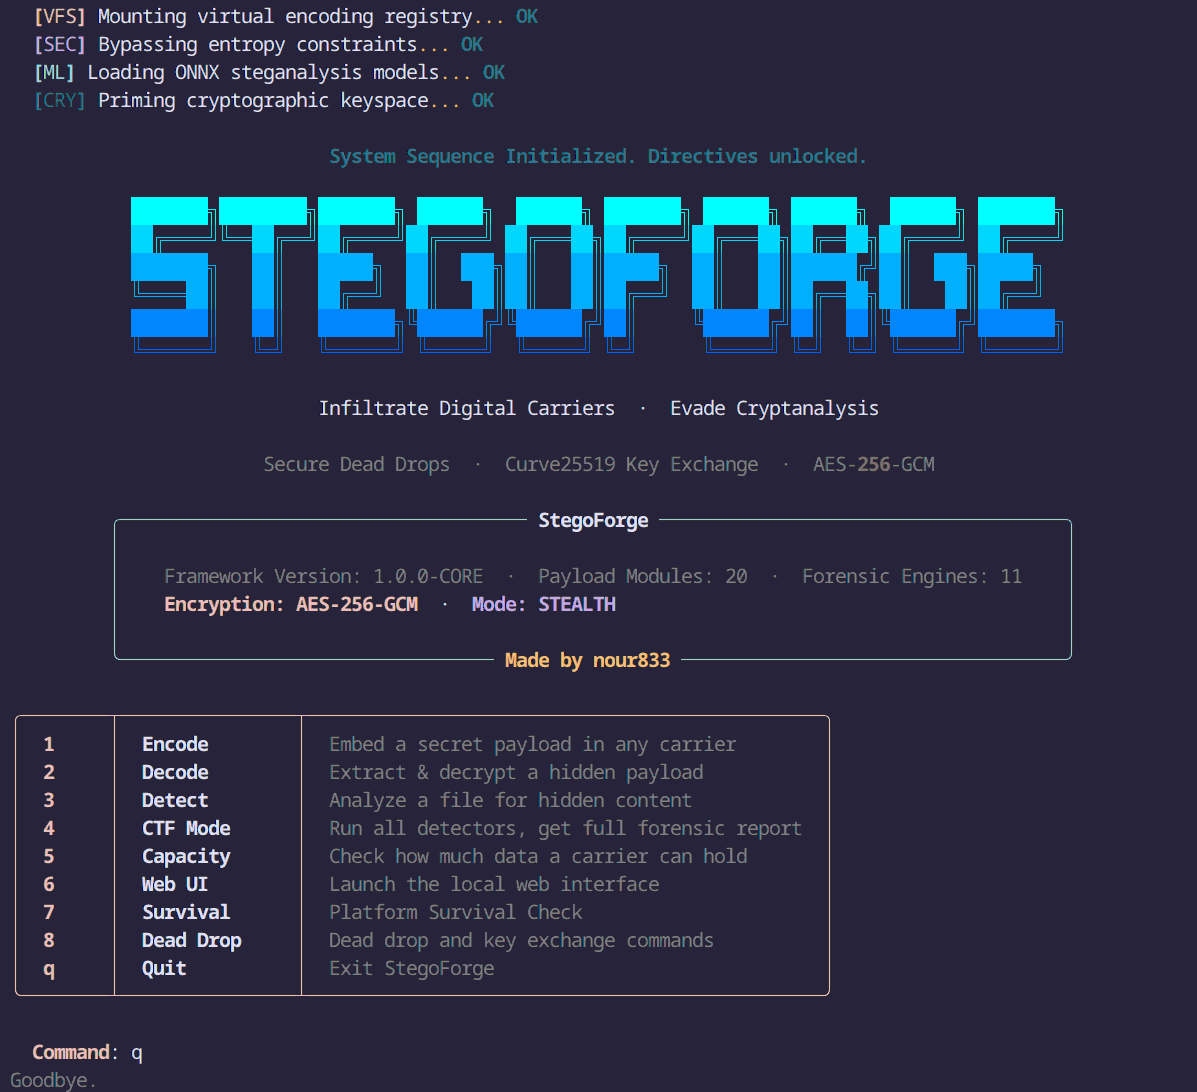
StegoForge preview

StegoForge

GitHubnour833/stegoforge

The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
cryptographyctfdata-exfiltration+8
57511 days ago
shadow-fleet-tracker-light preview

shadow-fleet-tracker-light

GitHubformerlab/shadow-fleet-tracker-light

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally

data-exfiltrationdigital-forensicsdns-analysis+9
426 months ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4895 years ago
Previous12Next