

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
29 results
honeypot-data preview

honeypot-data

GitHub0x4d31/honeypot-data

Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
incident-responseinformation-gatheringioc-management+4
29
5 days ago
plex2shell_pcap preview

plex2shell_pcap

GitHubboredhackerblog/plex2shell_pcap

Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…

exploitationincident-responsenetwork-forensics+3
112 days ago
security-vulnerability-in-Microsoft-Office. preview

security-vulnerability-in-Microsoft-Office.

GitHubahmed-tarek22752/security-vulnerability-in-microsoft-office.

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

digital-forensicseducationincident-response+6
218 days ago
citrix-netscaler-cve-2026-88771-iocs preview

citrix-netscaler-cve-2026-88771-iocs

GitHubwatchtowrlabs/citrix-netscaler-cve-2026-88771-iocs

Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…

command-and-controldefensive-toolsincident-response+5
23 days ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
6028 days ago
security-writeups preview

security-writeups

GitHubalzeaty1/security-writeups

CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.

ctfeducationlabs-practice+5
1 month ago
keepass-exfil-forensics preview

keepass-exfil-forensics

GitHubpugazhendii22/keepass-exfil-forensics

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
ctfdata-exfiltrationdigital-forensics+6
2 months ago
CVE-2019-11043-Vulnerability preview

CVE-2019-11043-Vulnerability

GitHubmagentabear/cve-2019-11043-vulnerability

Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
educationexploitationlabs-practice+8
10 months ago
Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation preview

Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation

GitHubzedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
digital-forensicseducationincident-response+7
12 months ago
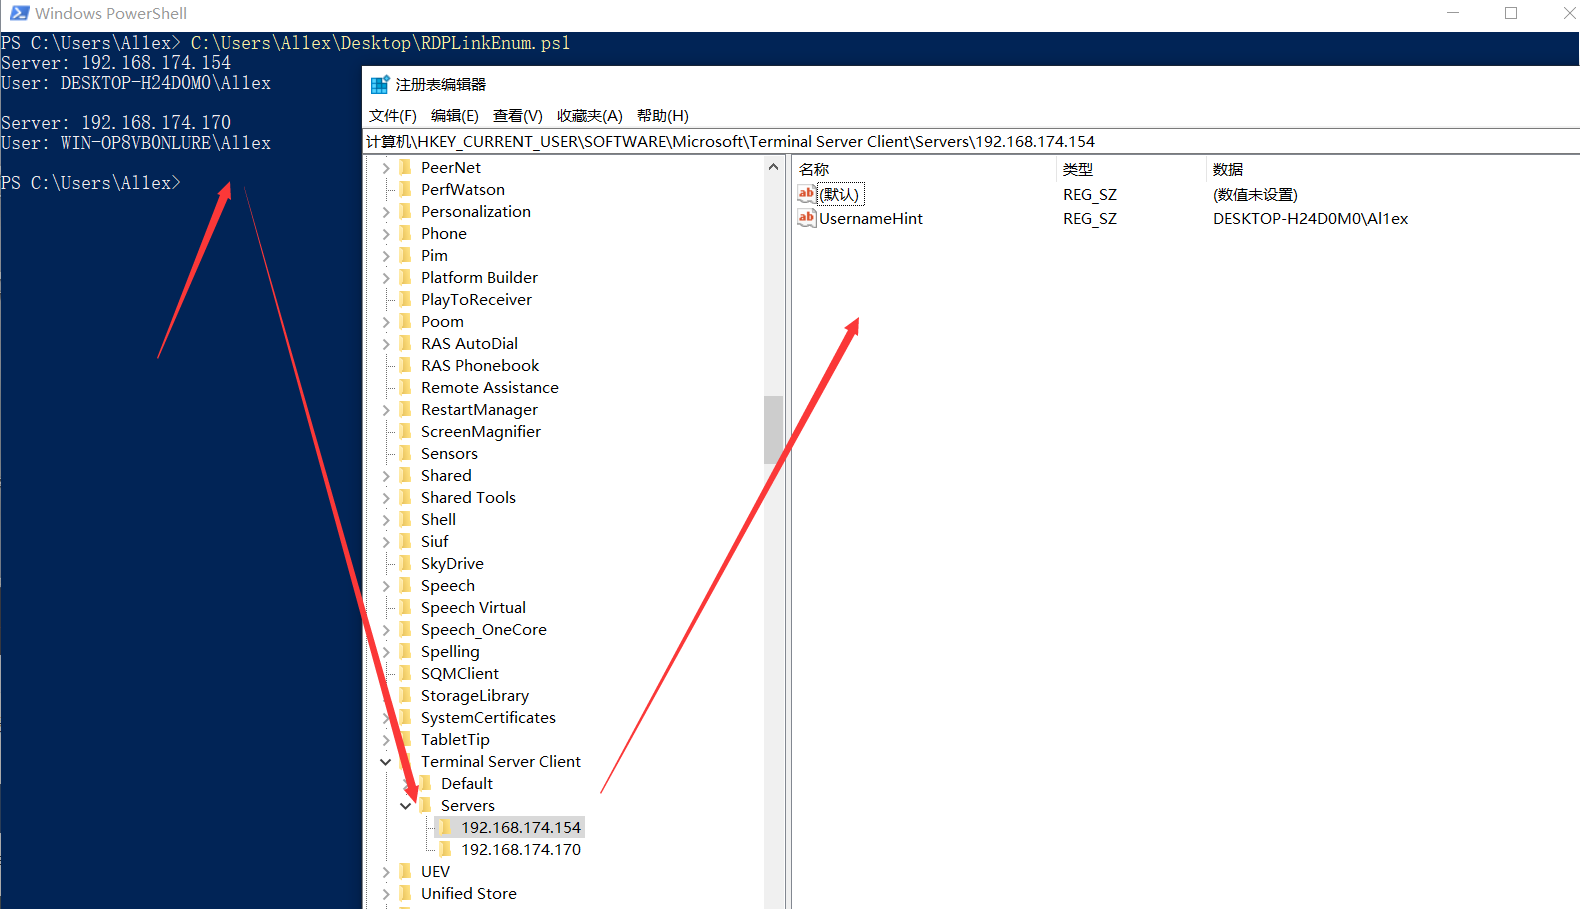
RDPLinkEnum preview

RDPLinkEnum

GitHubal1ex/rdplinkenum

RDPLinkEnum

digital-forensicsforensicsincident-response+3
55 years ago
pcap-burp preview

pcap-burp

GitHubnccgroup/pcap-burp

Pcap importer for Burp

network-forensicspacket-sniffing-analysispenetration-testing+2
1145 years ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:
data-recoverydigital-forensicsdisk-forensics+9
1.4k18 days ago
plugxdecoder preview

plugxdecoder

GitHubkcreyts/plugxdecoder

Decodes PlugX traffic and encrypted/compressed artifacts
digital-forensicsencryption-decryption-toolsforensics+3
3813 years ago
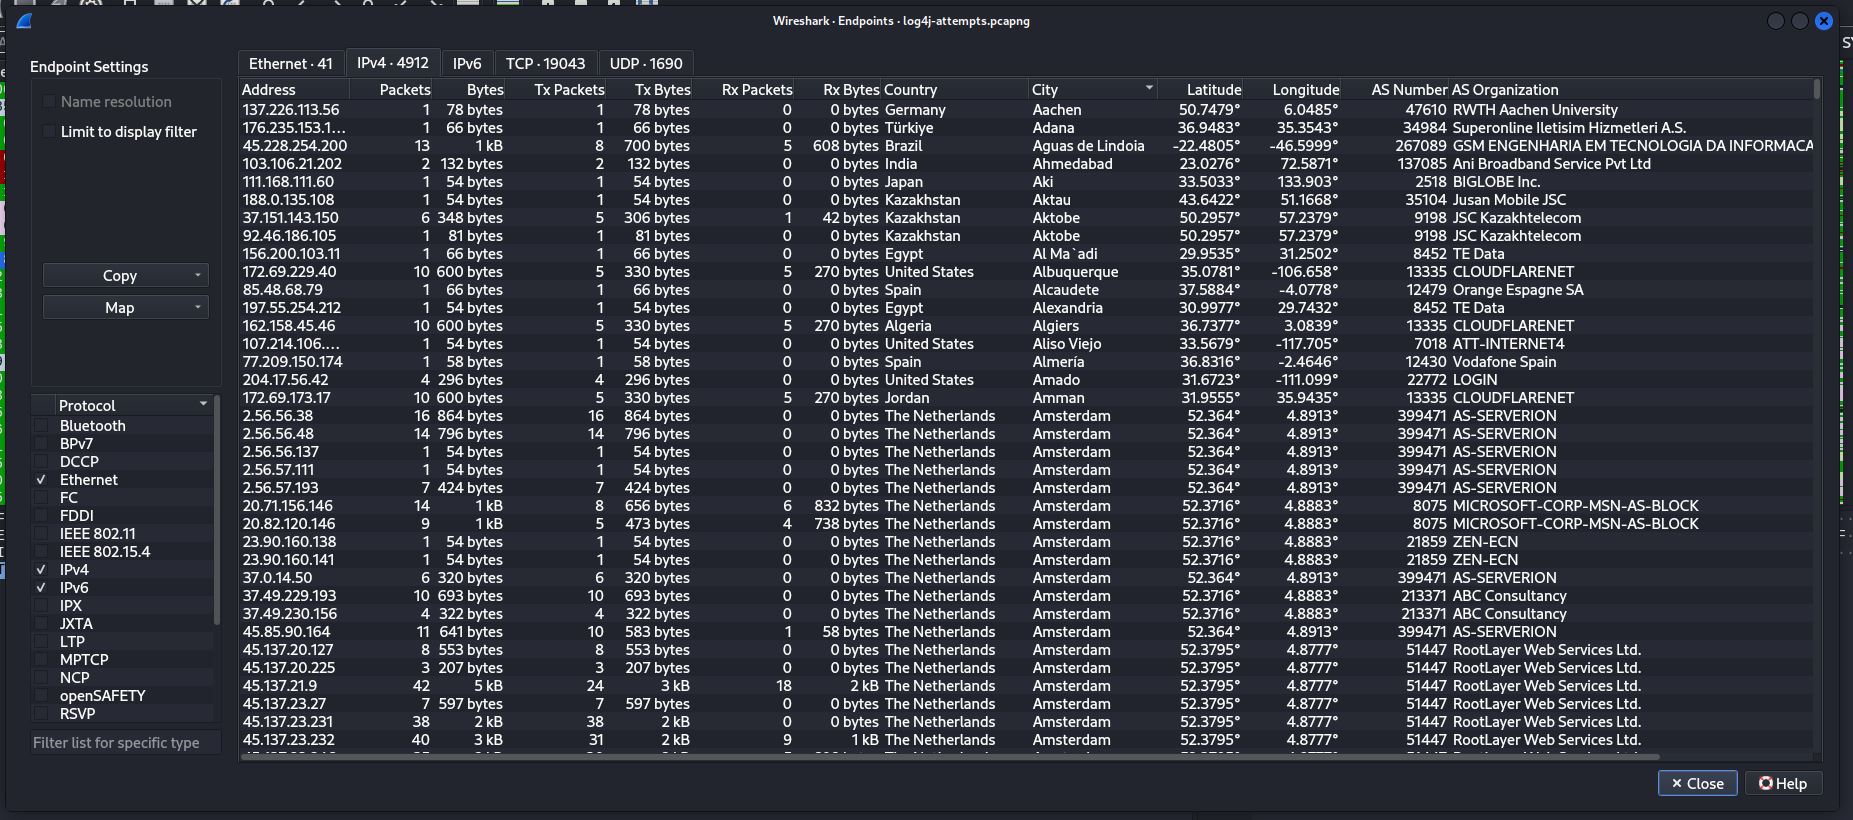
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

command-and-controldigital-forensicseducation+9
32 years ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
lab_xz_backdoor preview

lab_xz_backdoor

GitHubstevehenderson/lab_xz_backdoor

Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
educationexploitationforensics+6
14 months ago
eternalblue-ms17-010-research preview

eternalblue-ms17-010-research

GitHubtrinadh-dasari-cyber/eternalblue-ms17-010-research

Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…
educationexploitationlabs-practice+3
5 months ago
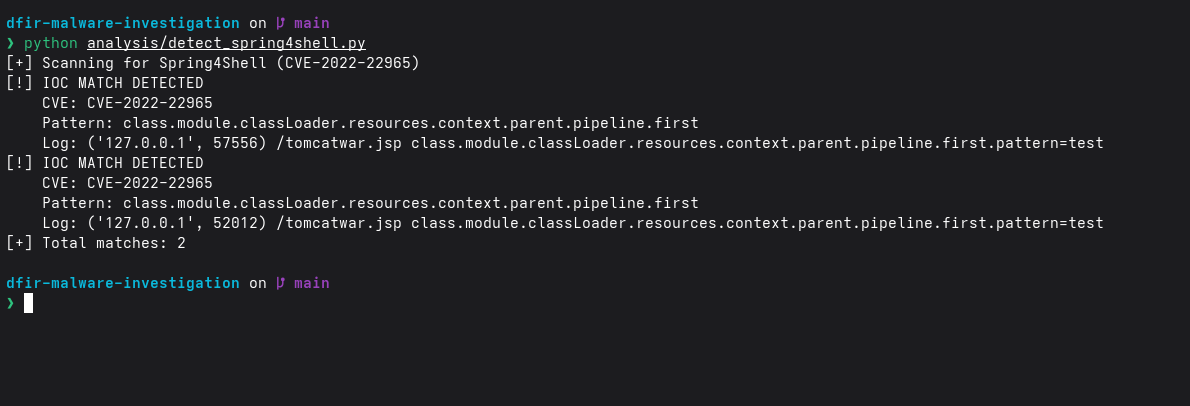
dfir-malware-investigation preview

dfir-malware-investigation

GitHubsuyash-r-k/dfir-malware-investigation

Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

digital-forensicseducationincident-response+9
9 months ago
Previous12Next