

awesome-dfir-skills
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
tsale/awesome-dfir-skillsA curated collection of DFIR skills and workflows for InfoSec practitioners.
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
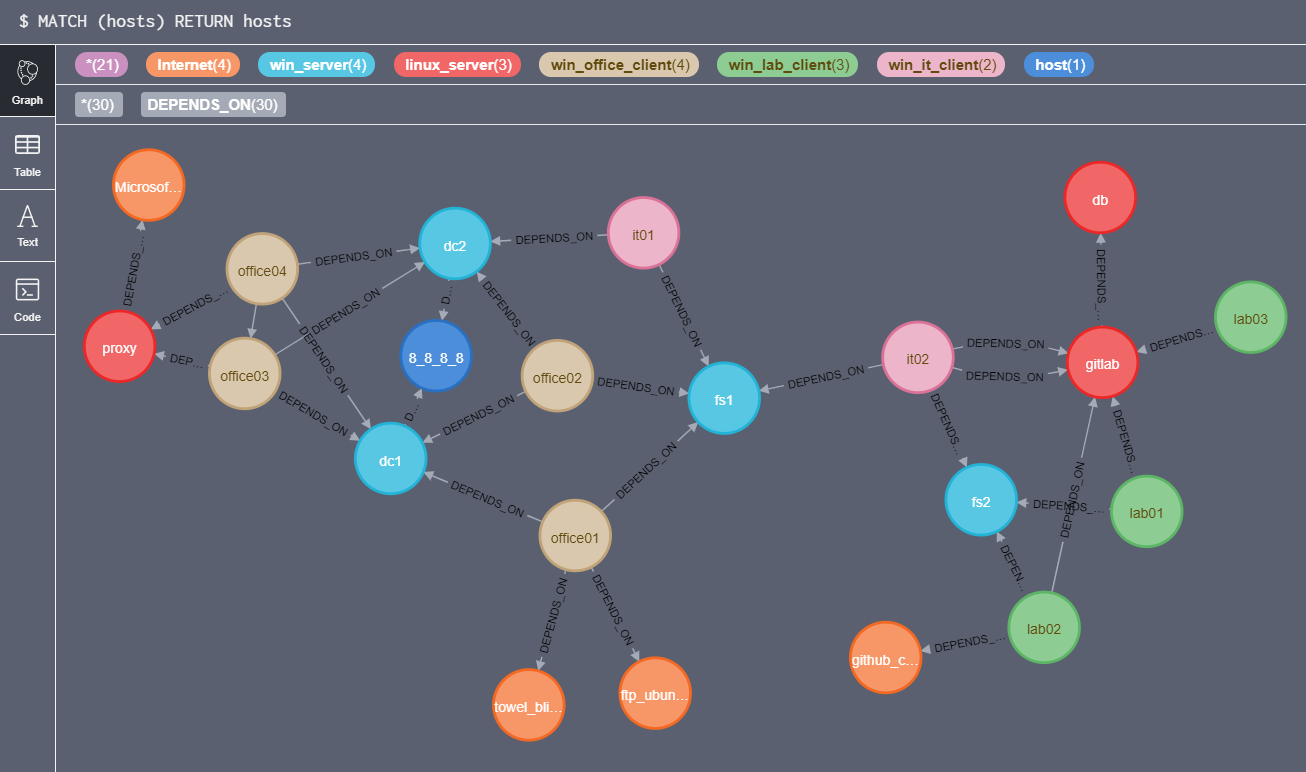 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format