

wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
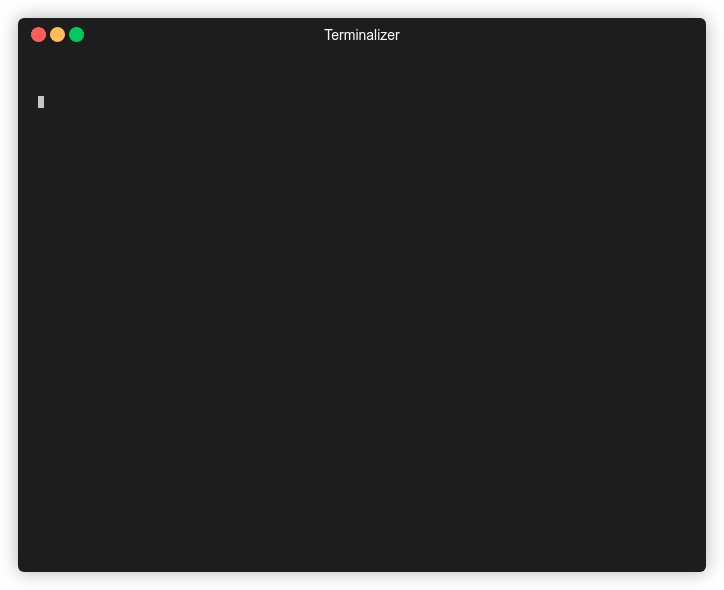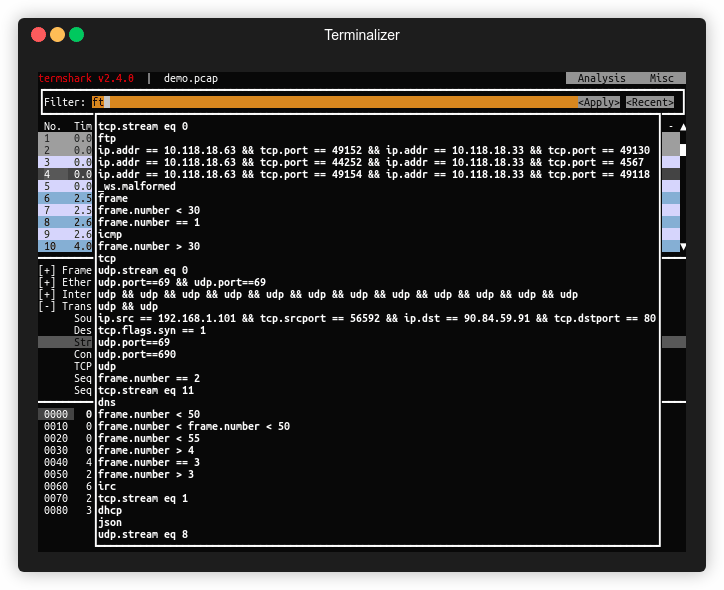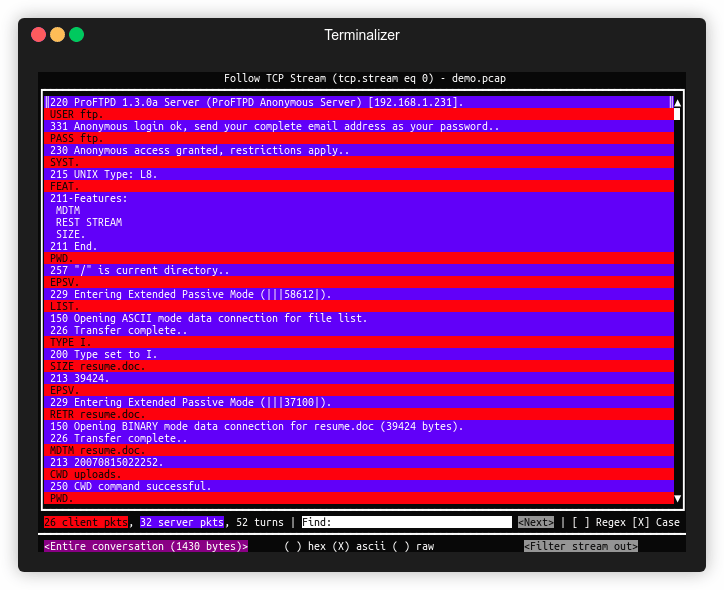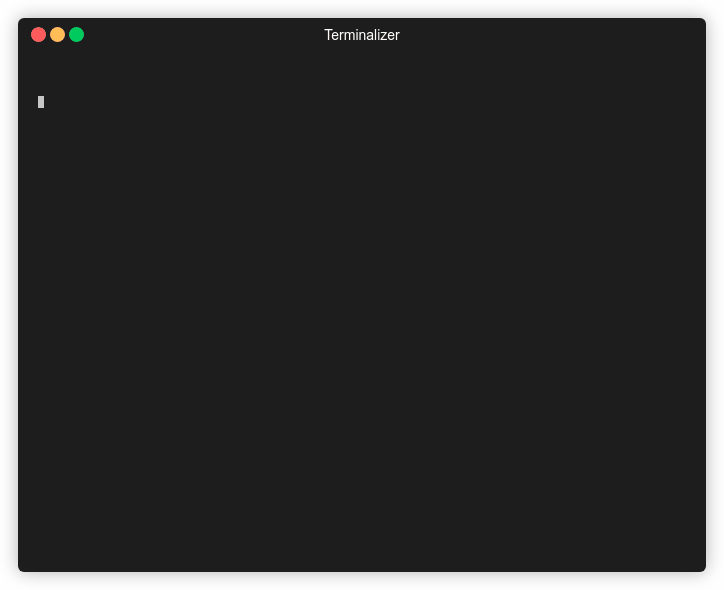 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
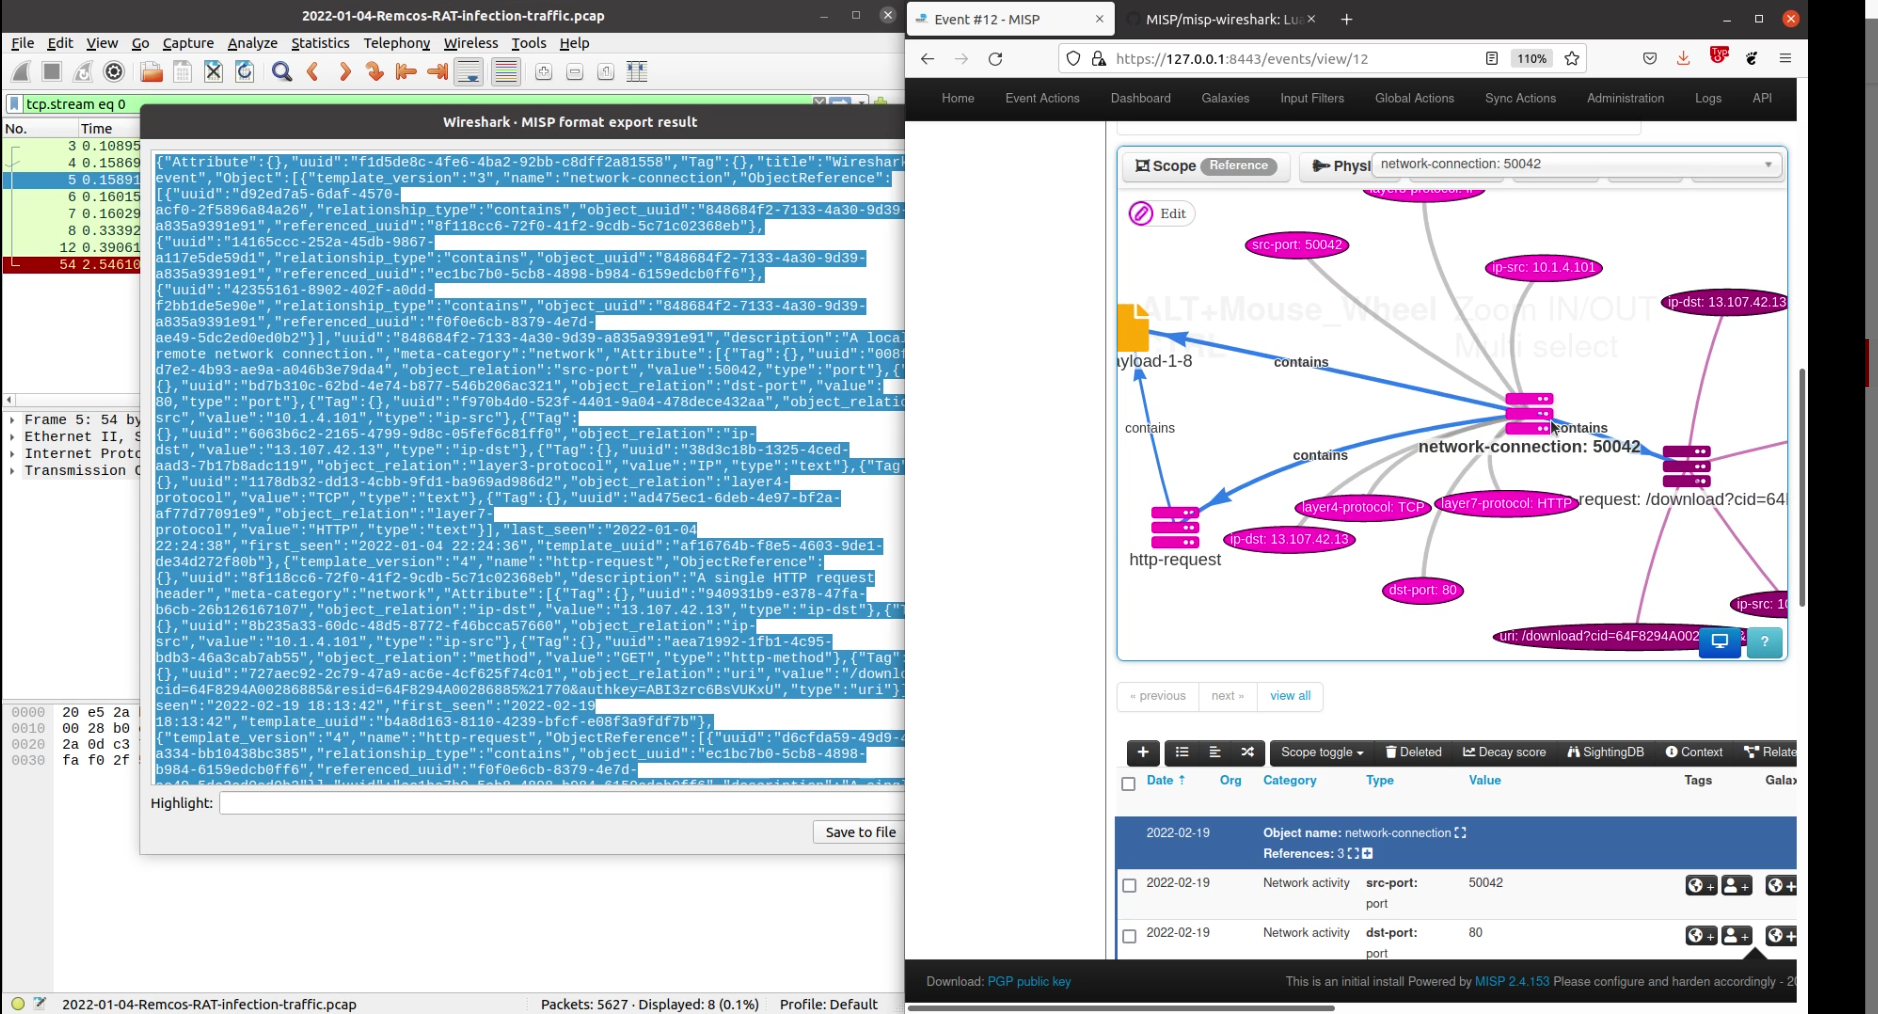 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
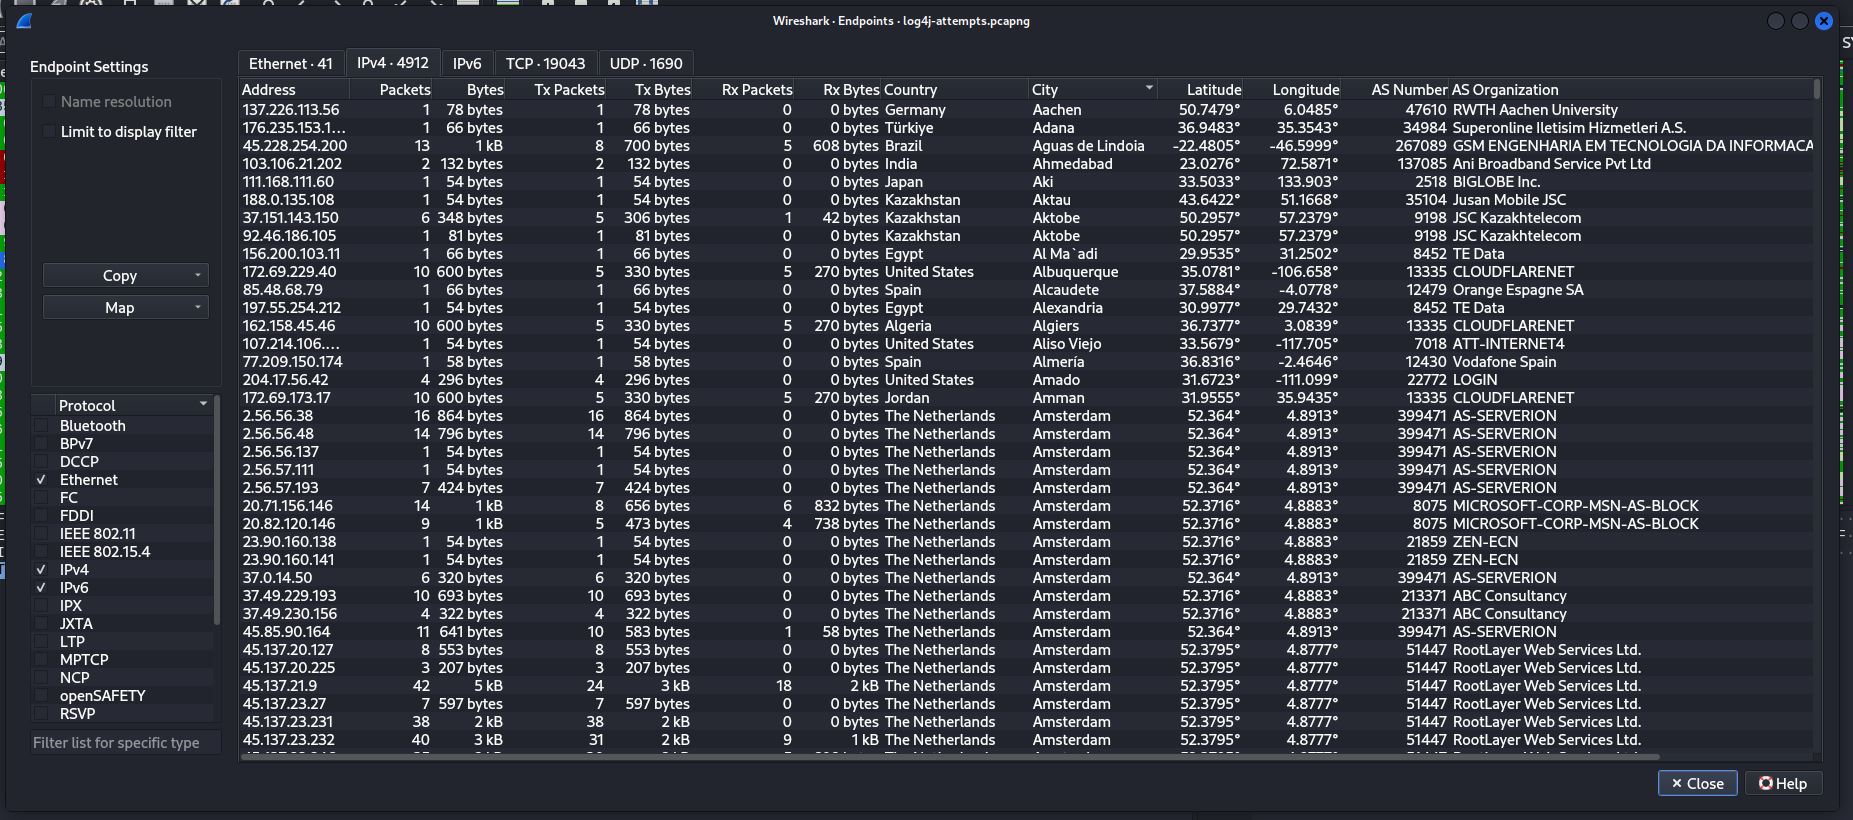 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 awakecoding/wireshark-rdp
Wireshark RDP resources
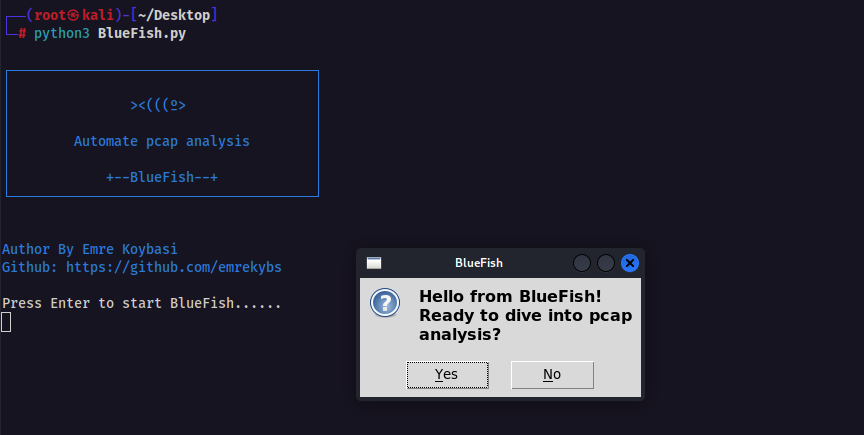 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 trinadh-dasari-cyber/eternalblue-ms17-010-research
Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…