dns_watchdog_windows2
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
anomaly-detectiondefensive-toolsdns-analysis+5
microlaser/dns_watchdog_windows2PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
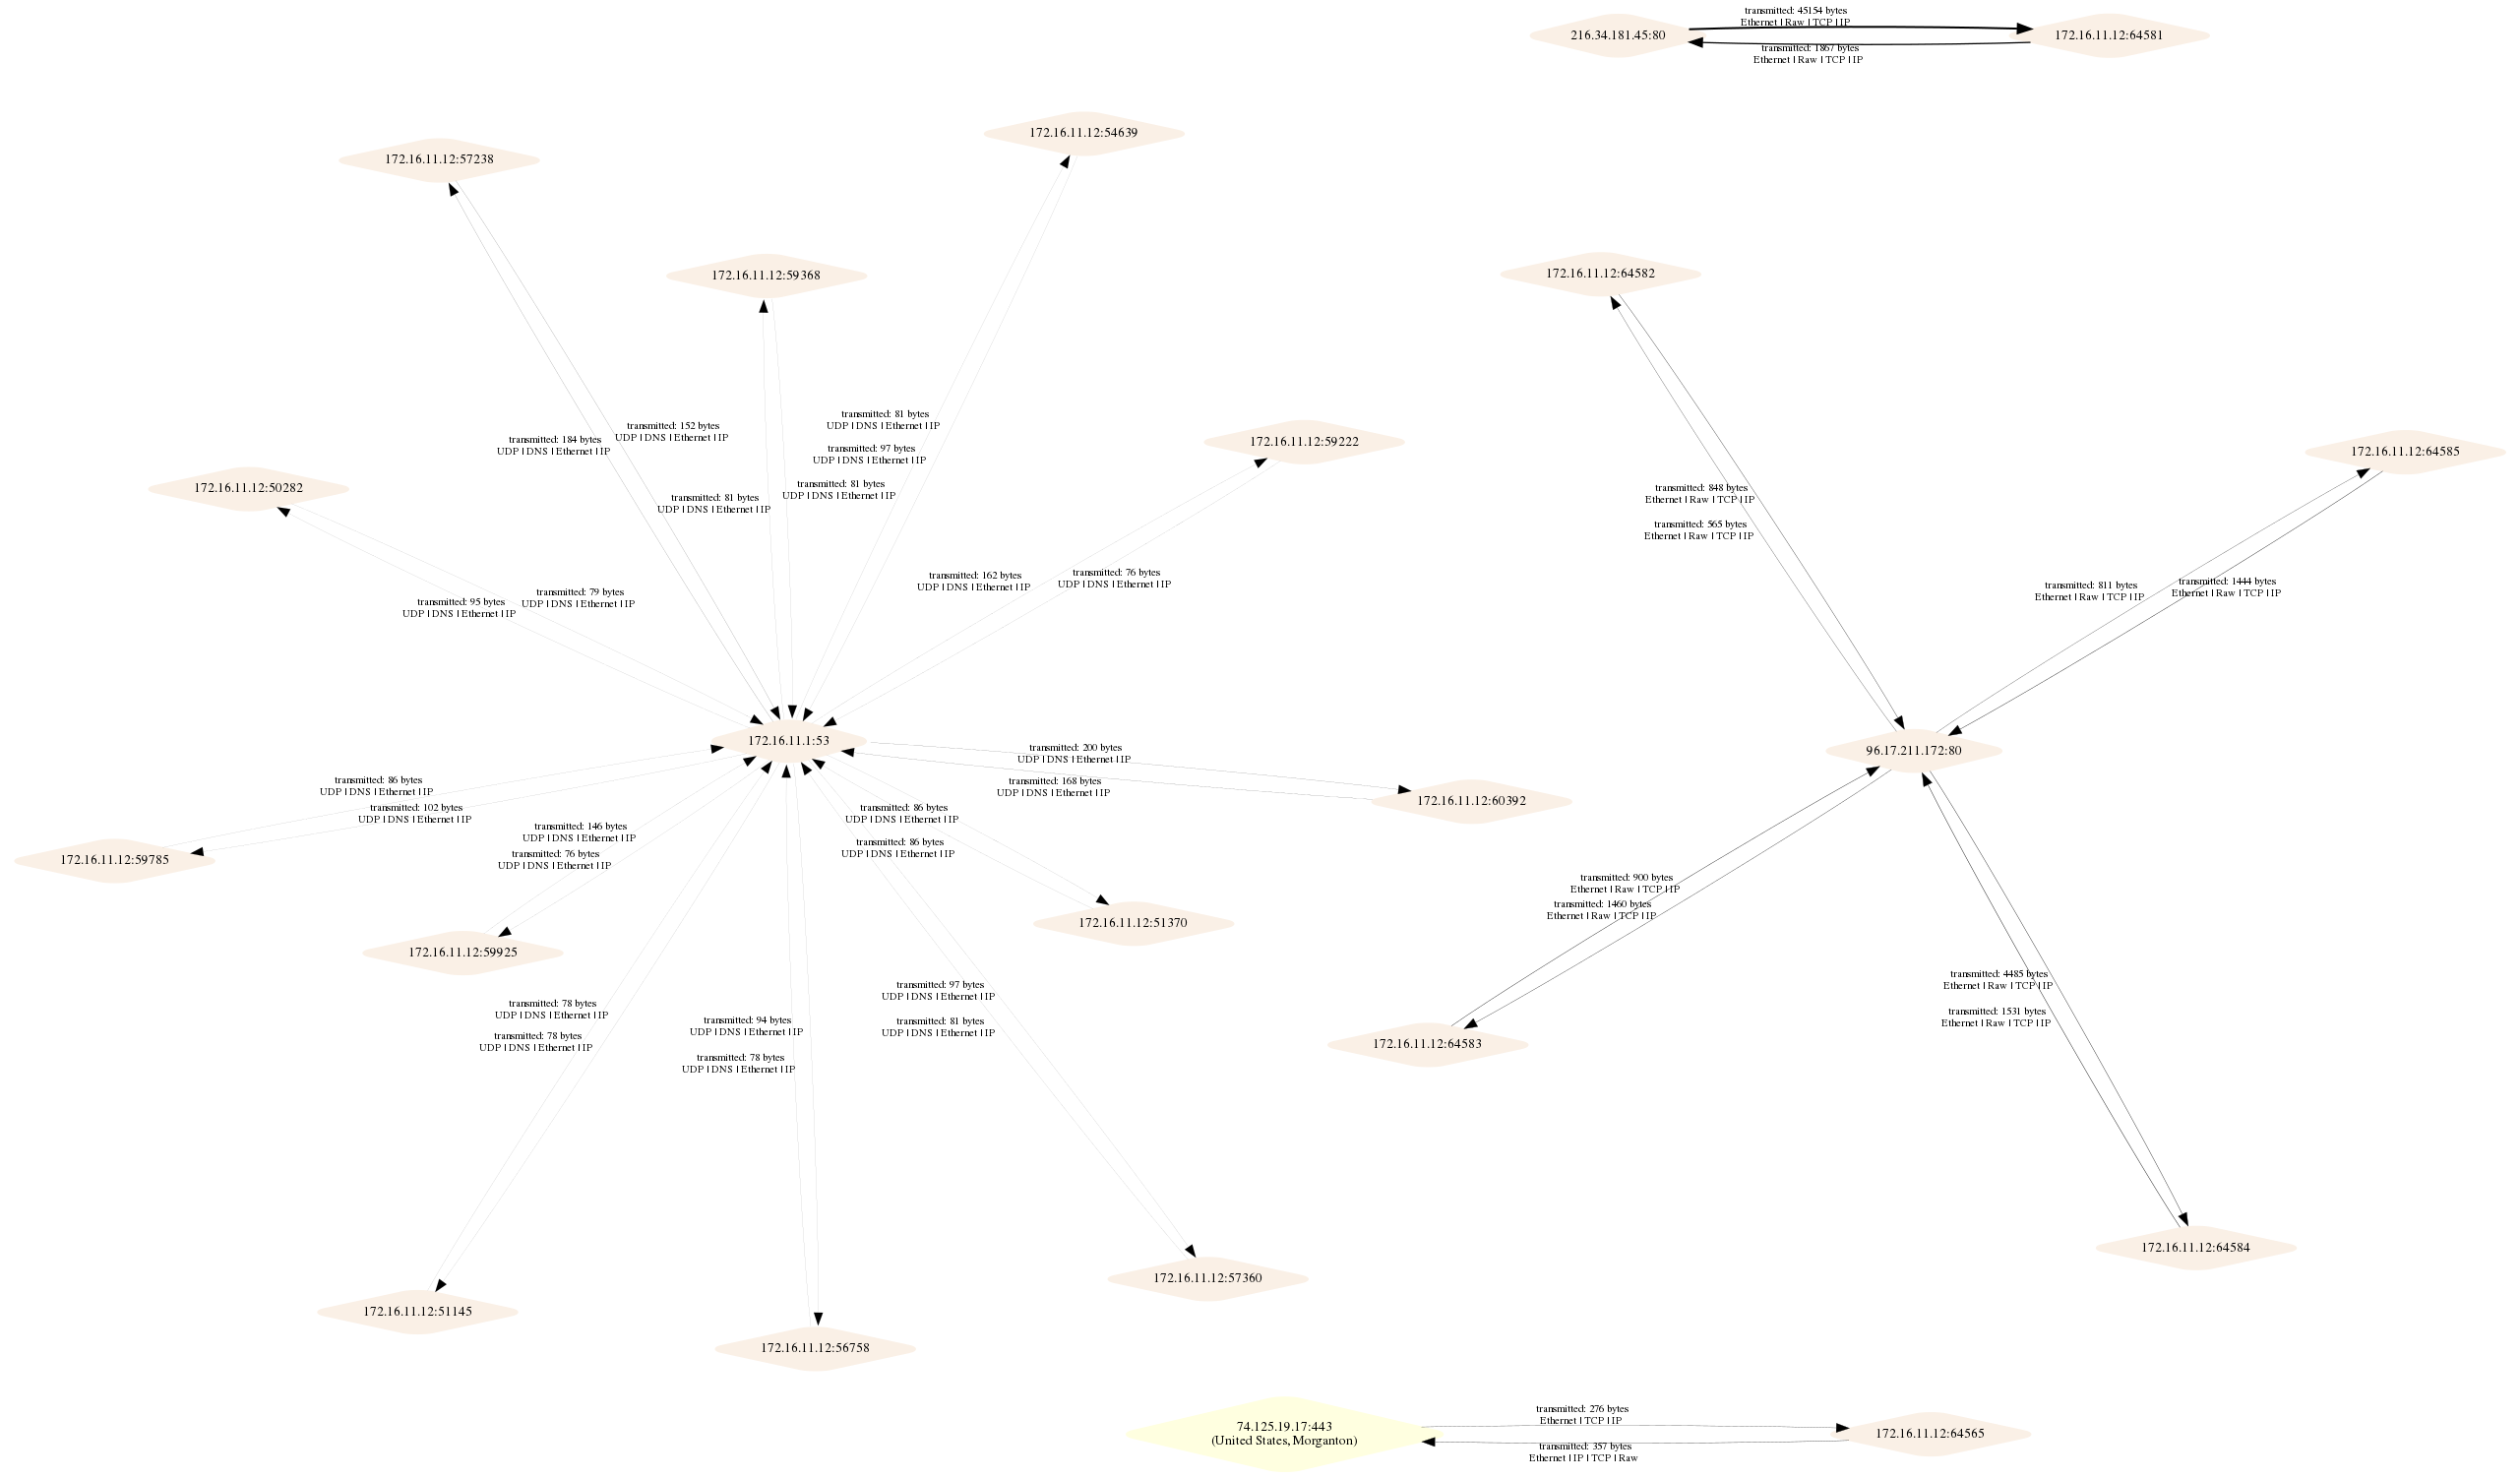 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
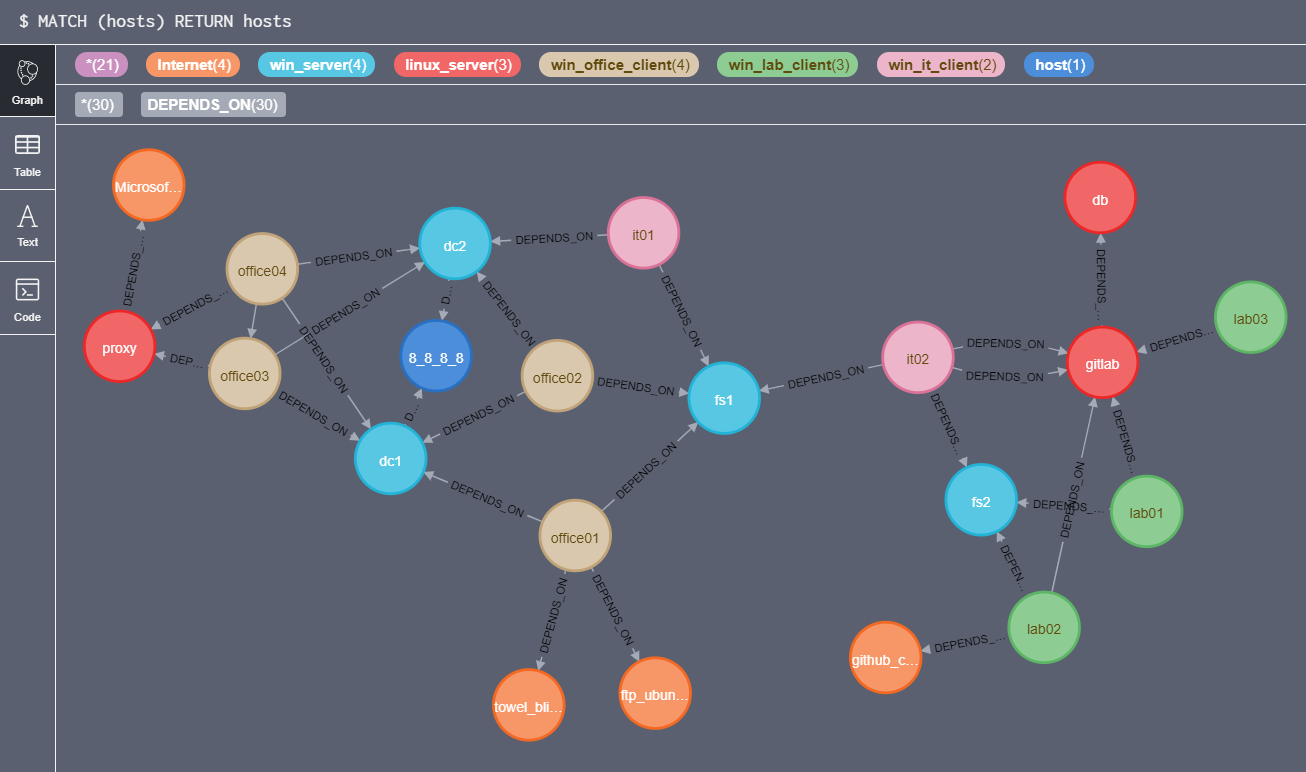 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 synacktiv/pcapan
A pcap capture analysis helper
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 z4l4mi/ipgeo
Extracts IP addresses from pcap/pcapng network traffic files and generates CSV reports with geolocation, ISP, and organizational details for each IP.
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
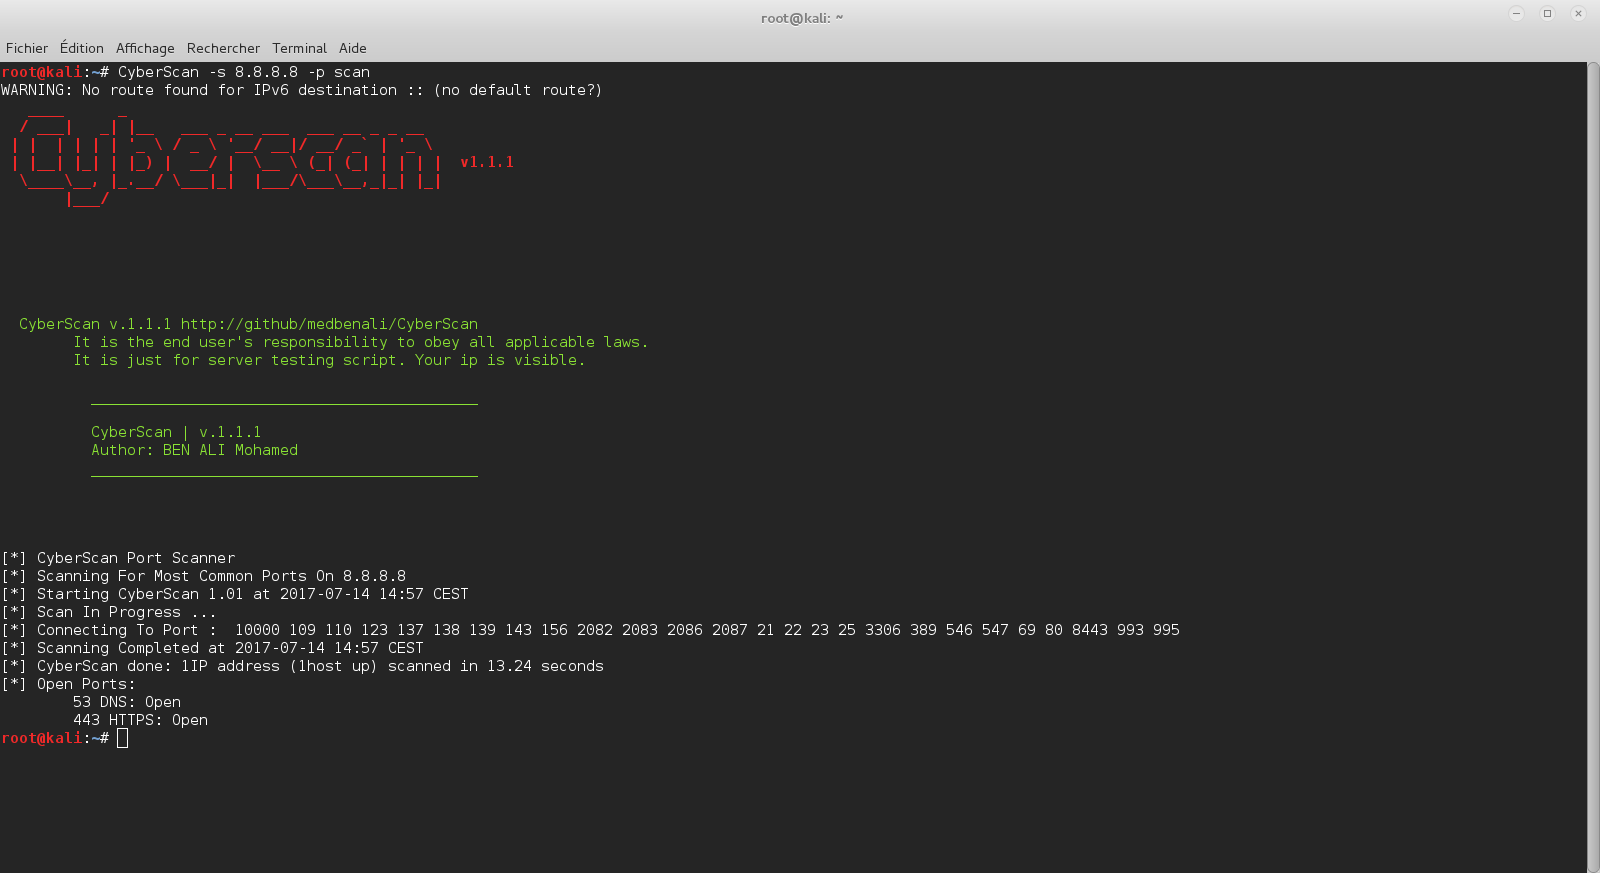 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
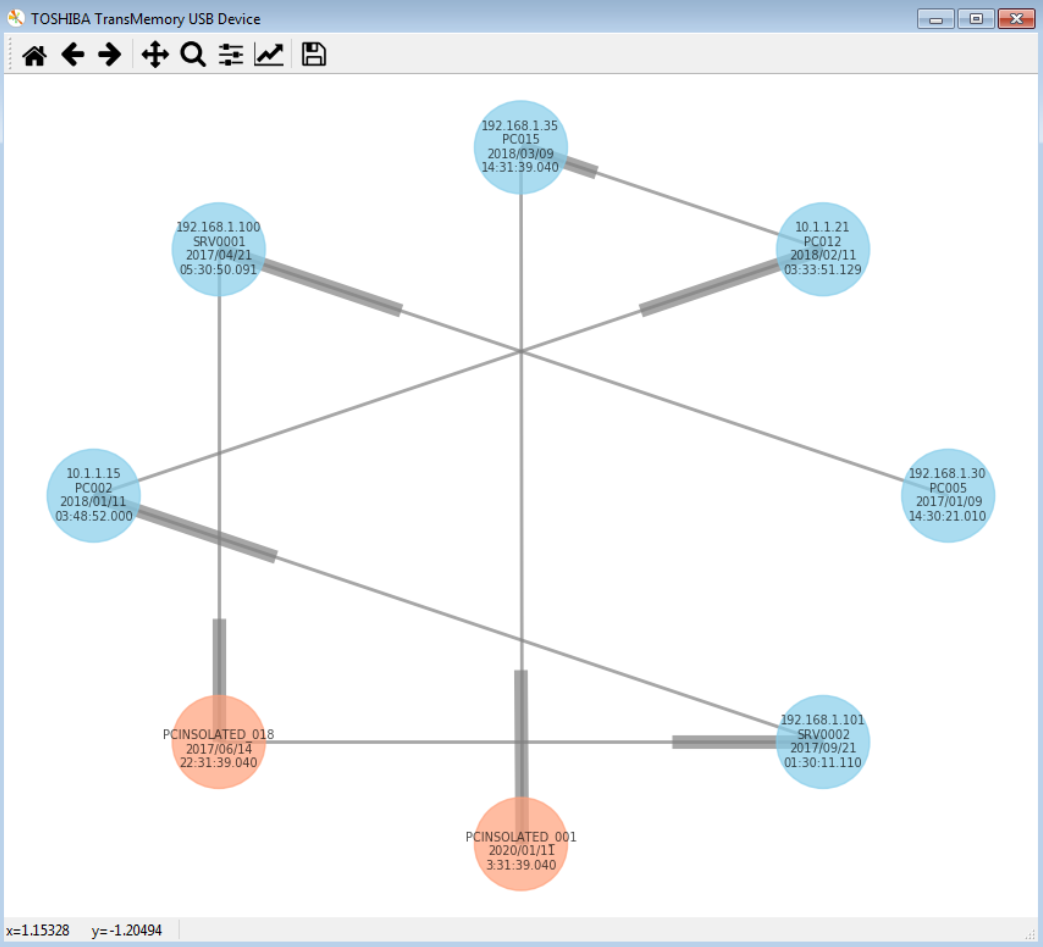 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)