

termshark
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
network-forensicsnetwork-securitypacket-sniffing-analysis+1
10.0k
gcla/termsharkA terminal UI for tshark, inspired by Wireshark
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 darnellwashingtonjr94-art/sandb0x-xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
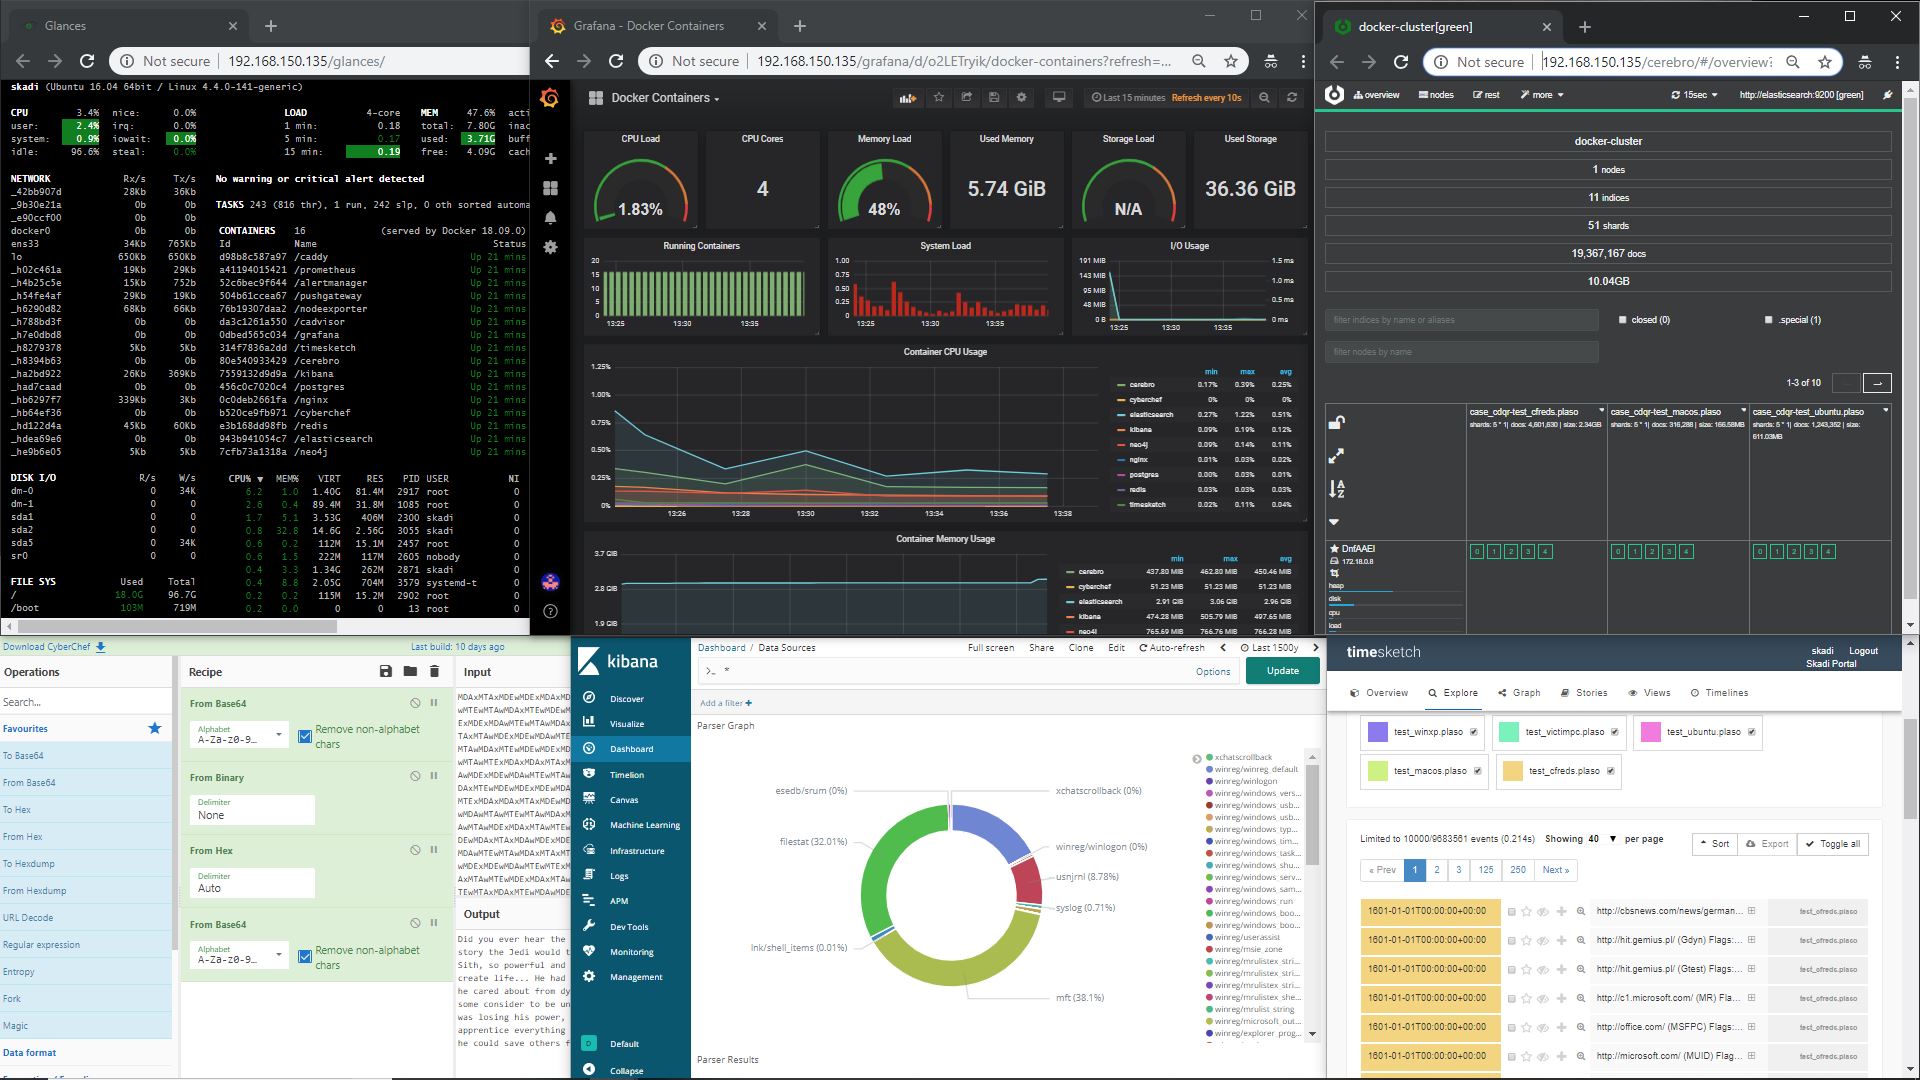 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 cyberhatcoil/acf
Android Connections Forensics
 cristianzsh/forensictools
Collection of forensic tools
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
