
android-c-sharp-rat-server
 advancedhacker101/android-c-sharp-rat-server
This is a plugin for the c# R.A.T server providing extension to android based phone systems
android-securitycommand-and-controldata-exfiltration+3
20
advancedhacker101/android-c-sharp-rat-serverThis is a plugin for the c# R.A.T server providing extension to android based phone systems
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
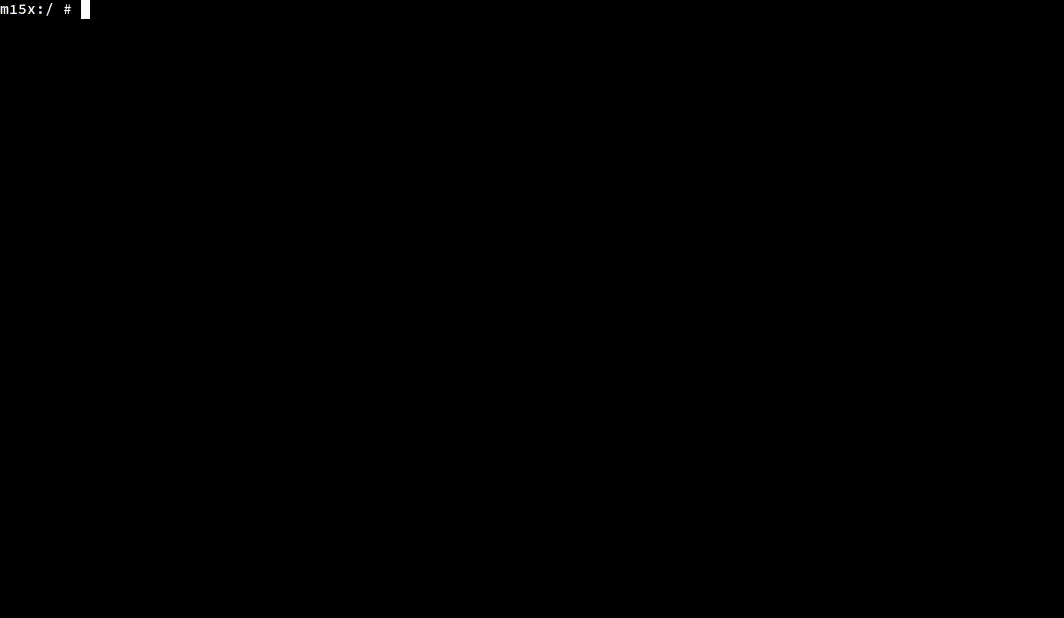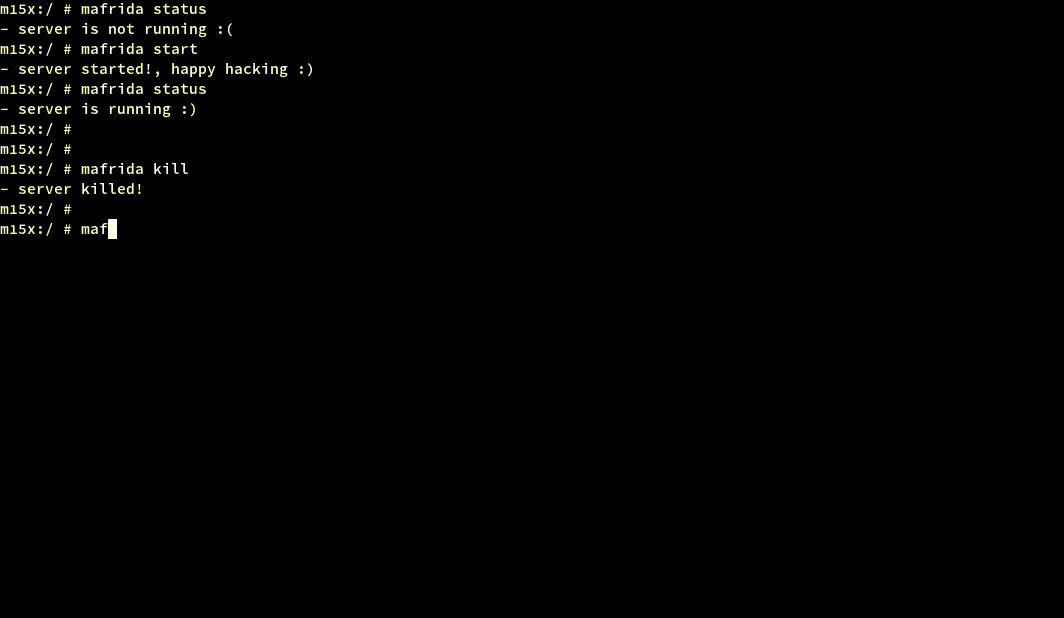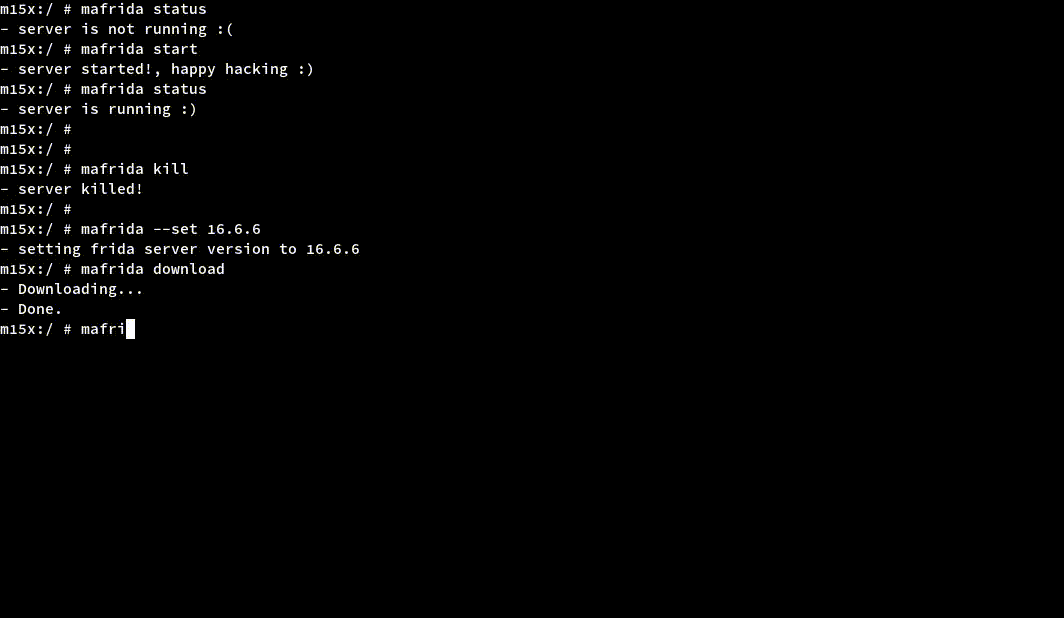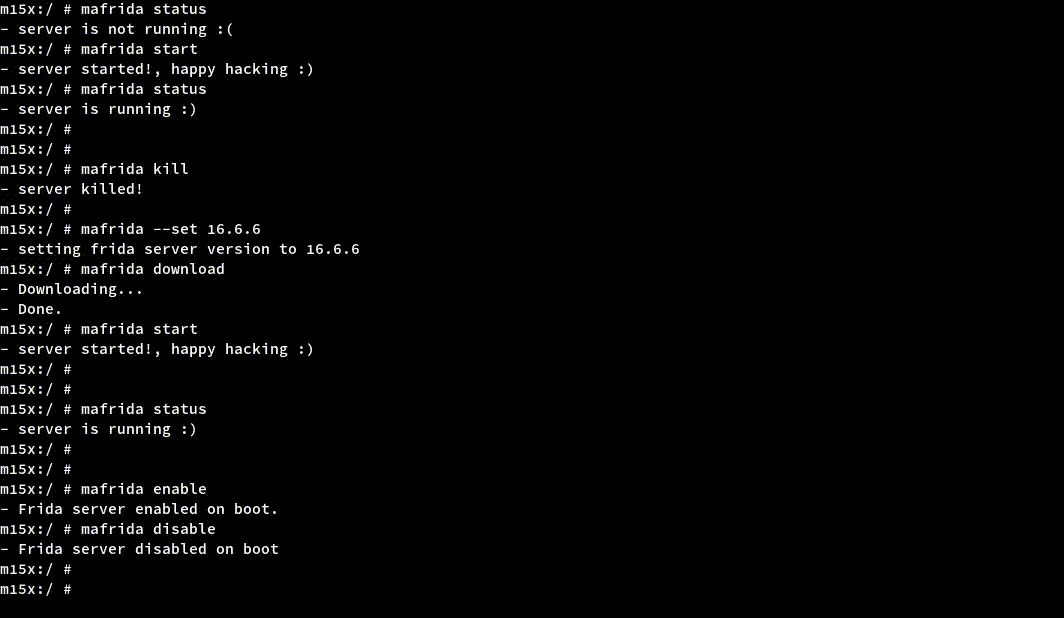 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 eudemonics/scaredycat
Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
 george0papasotiriou/cve-2026-22011-ios-mdm-profile-delivery-over-http
PoC Flask server for CVE-2026-22011 that serves a malicious iOS MDM enrollment profile over HTTP, enabling man-in-the-middle interception and device…
 mbeweoo/flash-exploit-defense-system
Comprehensive multi-layer defense system against Adobe Flash CVE exploits (CVE-2012-0754, CVE-2015-xxxx, CVE-2016-xxxx, CVE-2018-xxxx) with browser,…
 shaikusaf/frameworks_native_aosp10_r33_shaikusaf-frameworks_native_aosp10_r33_cve-2020-0226
Exploit for CVE-2020-0226 targeting Android 10 native frameworks. Provides a proof-of-concept for a critical elevation-of-privilege vulnerability in…
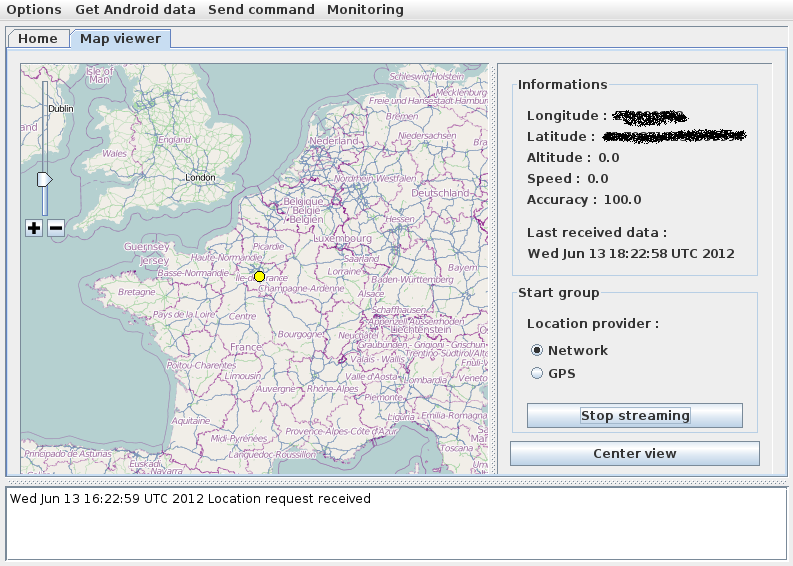
 designativedave/androrat
Remote Administration Tool for Android devices