
ghostlock-a17
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
android-securitybinary-exploitationexploitation+4
18
mobilehackinglab/ghostlock-a17Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 betalphafai/cve-2015-6640
Proof-of-concept exploit for Android kernel privilege escalation vulnerability CVE-2015-6640, demonstrating the flaw and providing a reference for…
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 xcodeon1/ssh-killv2
SSH brute-force tool targeting jailbroken iPhones with default 'alpine' password, featuring network scanning, wordlist-based cracking, and file…
 ele7enxxh/cve-2014-7911
Proof-of-concept exploit for Android local privilege escalation (CVE-2014-7911) targeting Nexus5 with ROP chain and heap spraying to gain system uid.
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 supersonic/wallbreak
Exploit app for CVE-2021-39670 and CVE-2021-39690, two permanent denial-of-service vulnerabilities in Android's wallpaper system
 georgiev-martin/nofrak
Proof Of Concept for Android. NoFrak is designed to prevent fracking attacks, as described in "Breaking and Fixing Origin-Based Access Control in…
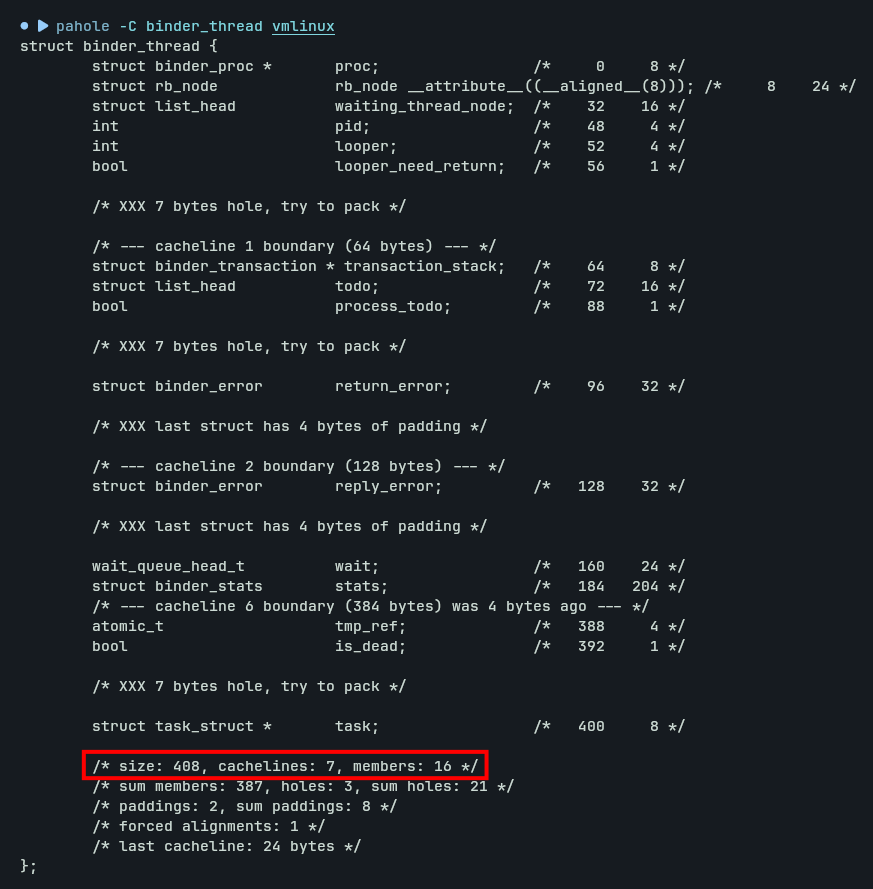 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 infiniteloopers/cve-2019-11932
Technical write-up and exploit code for CVE-2019-11932, a double-free vulnerability in WhatsApp for Android that leads to remote code execution via a…
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
 koozxcv/cve-2014-7911-cve-2014-4322_get_root_privilege
CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!
 thebl4ckph4nt0m/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13. This repo demonstrates how to exploit…