
frida-interception-and-unpinning
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
android-securityios-securitymobile-app-pentesting+4
2.3k
httptoolkit/frida-interception-and-unpinningFrida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
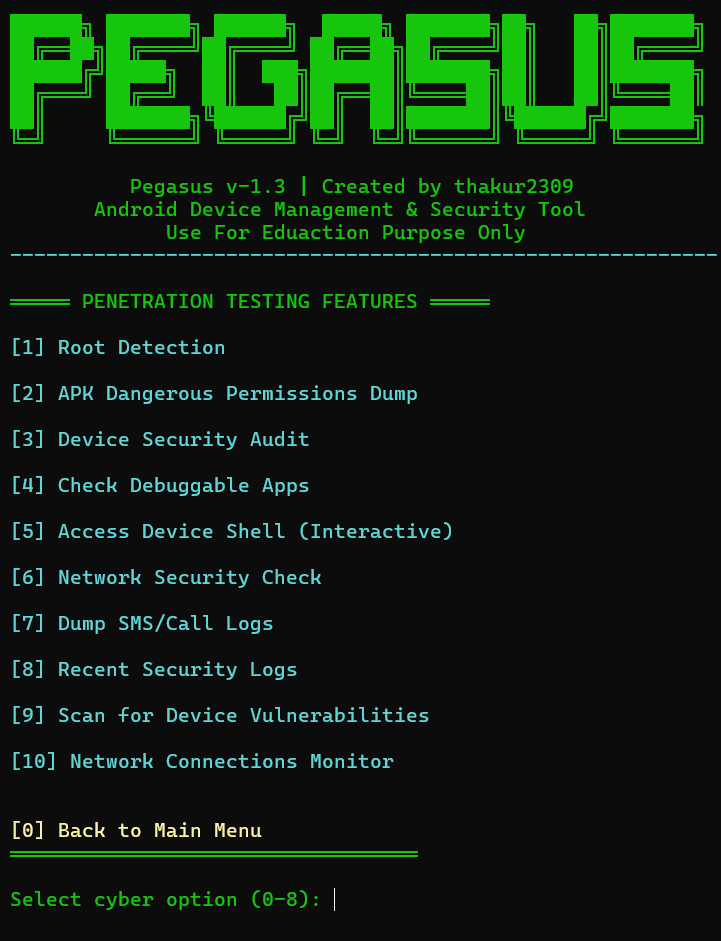 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 prey/prey-android-client
Android client for Prey: reliable device tracking and security tool
 chichou/vscode-frida
Unofficial frida extension for VSCode
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
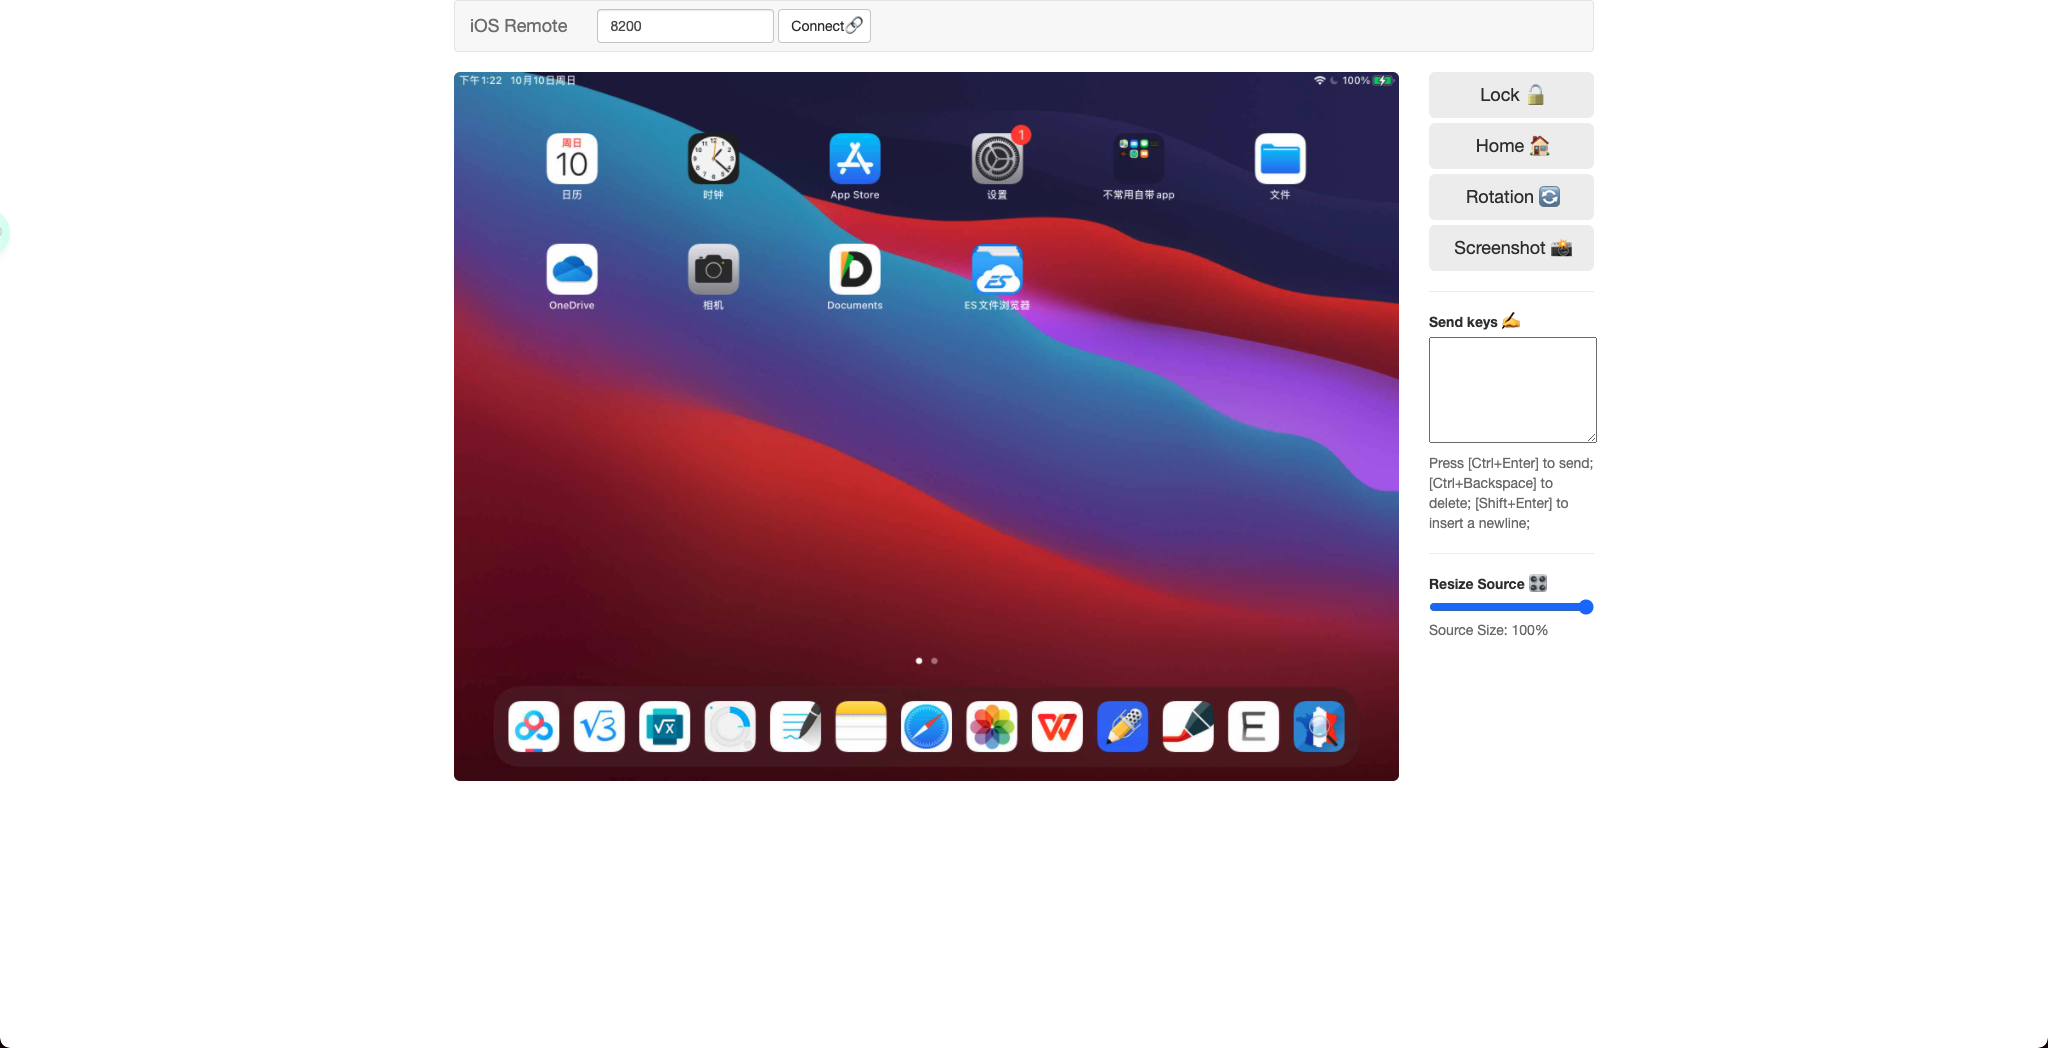 dimcyan/ios-remote
Display and control your iOS device
 0x36/weightbufs
ANE kernel r/w exploit for iOS 15 and macOS 12
 packetlss/android-locdump
android location service cache dumper
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…

 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
 geosn0w/cve-2025-24203-ios-exploit-with-error-logging
Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
 xiaobailovesstirring/ghostlock-k419-adapter
GhostLock (CVE-2026-43499) adapter for 4.19.152-perf+ Android kernel