
cve-2026-43499
 catxiaoshi/cve-2026-43499
PD2229B的43499(ghostlock)可行性研究
android-securitybinary-exploitationexploitation+4
catxiaoshi/cve-2026-43499PD2229B的43499(ghostlock)可行性研究
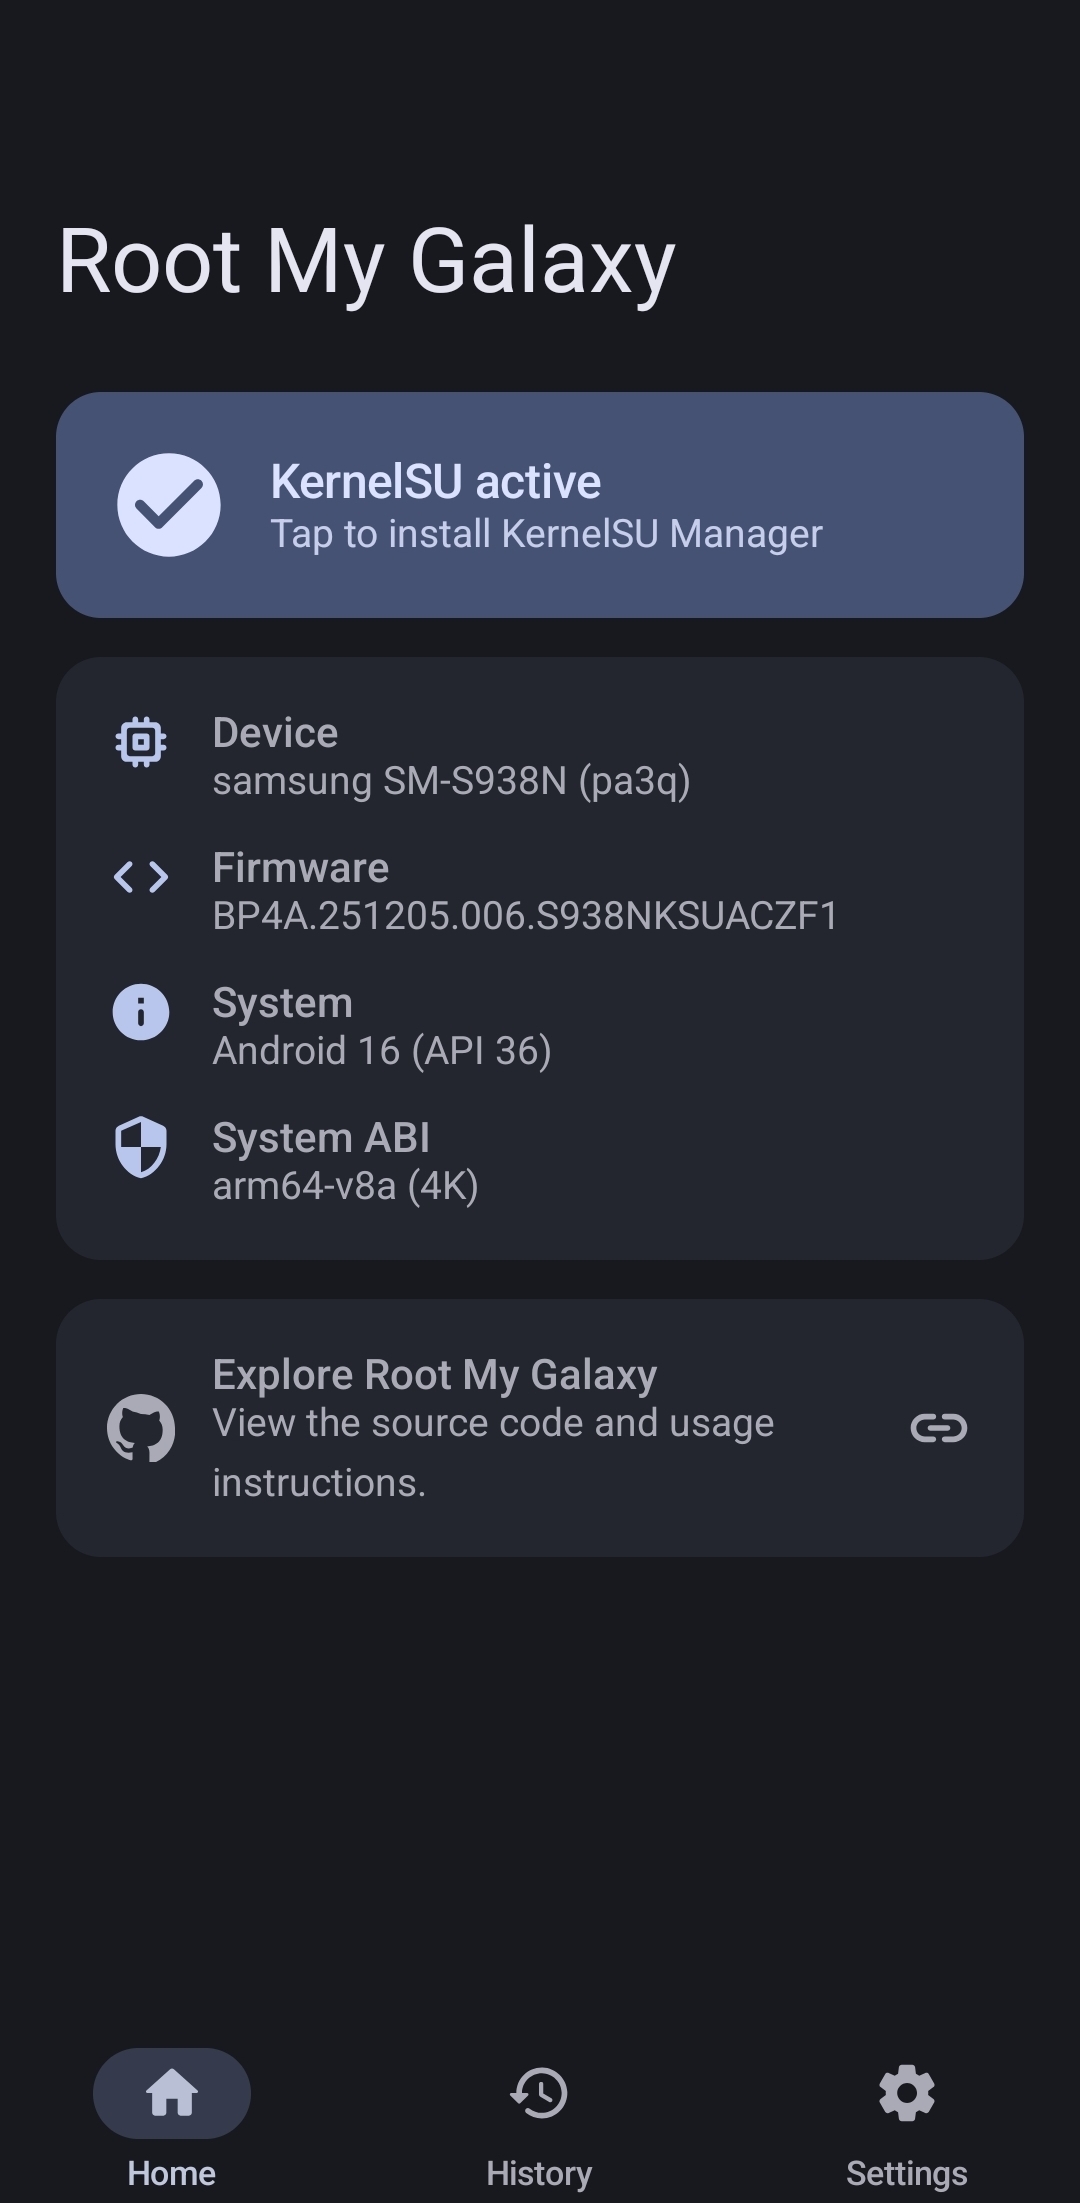 ohlookitstheirs/root-my-galaxy-tests
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499 (Note: Fork)
 lazybear8372/cve-2020-23349_lab
Educational Android lab for CVE-2020-23349 in Sina Weibo SDK 4.2.7
 justsoman/cve-2026-43499-jinghu
CVE-2026-43499 exploit reproduction on jinghu (Xiaomi Pad 7 Ultra)
 lazybear8372/cve-2023-31014_lab
Educational Android lab for CVE-2023-31014 implicit intent hijacking
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 justsoman/cybermeowfia-ace3
CVE-2026-43499 exploit with OnePlus Ace3 support
 b0b0505/cve-2016-0846-poc
Proof-of-concept exploit for CVE-2016-0846, an Android privilege escalation vulnerability, demonstrating exploitation techniques for security…
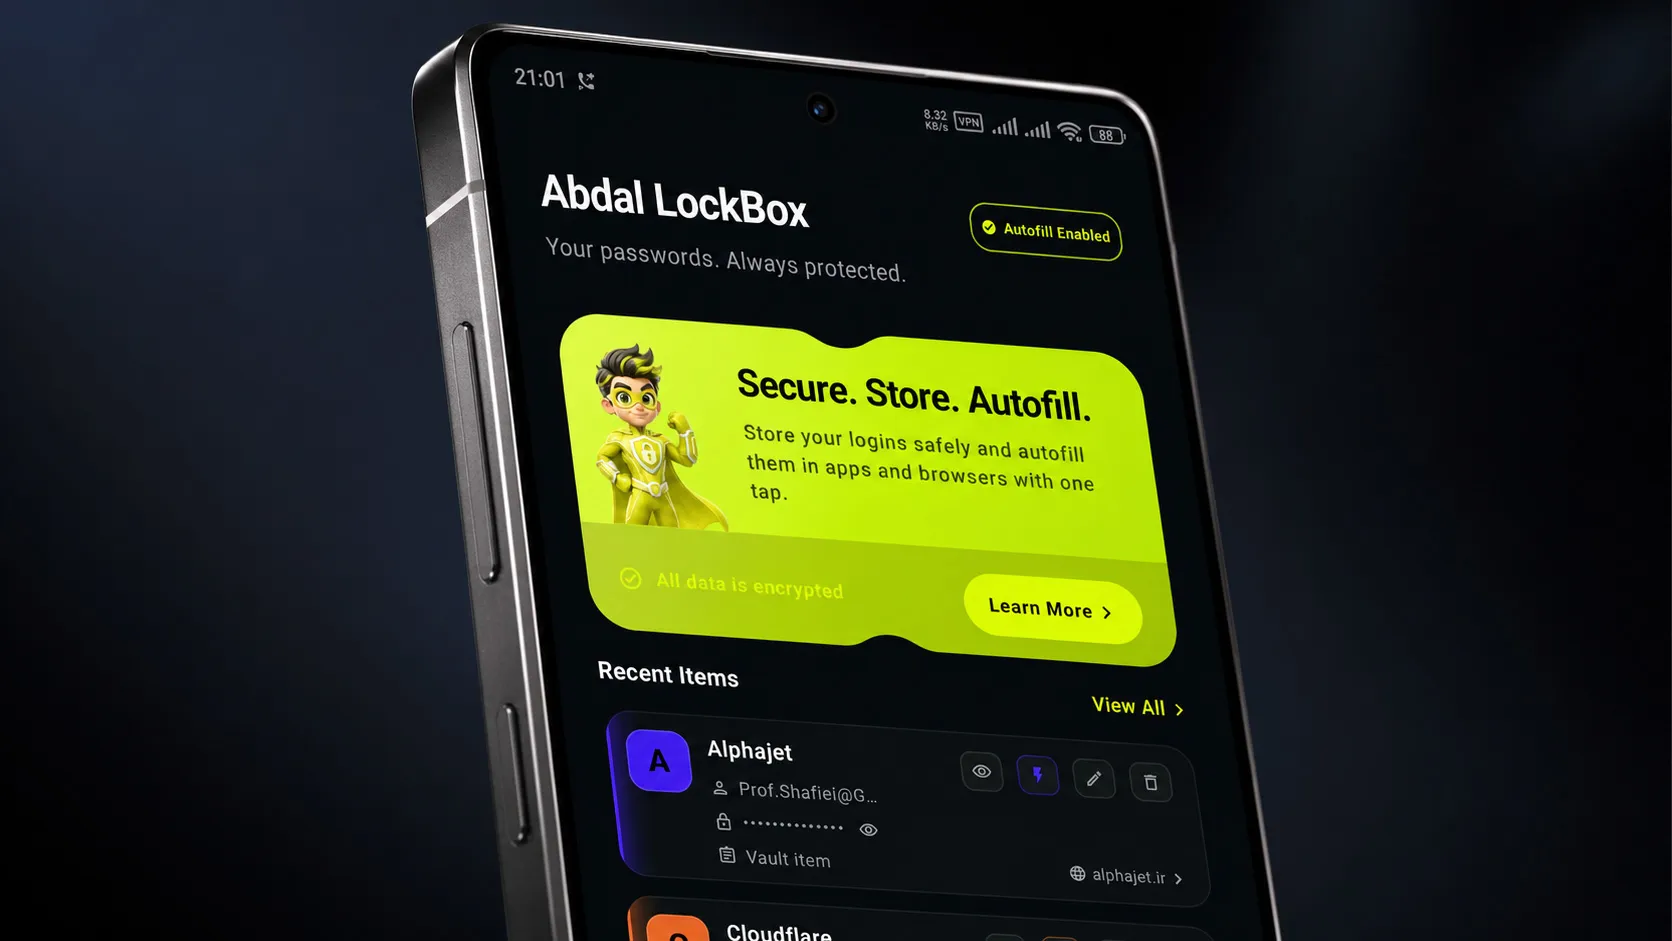
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 rebelle3/cve-2017-7117
Educational exploit for CVE-2017-7117, a type-confusion and use-after-free vulnerability in iOS 10.3.4 JavaScriptCore, demonstrating memory spraying…
 diyiqiuye/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
 wabzqem/covidsafe-cve-2020-12717-exploit
Code for exploit for CVE-2020-12717
 danielebert/cve-2016-5195
DirtyCOW Exploit for Android
 sentinel-aidefense/cve-2026-0163-exp
CVE-2026-0163 Exploit
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 kananosa/cve-2026-43499-for-xiaomi-17t-chagall
CVE-2026-43499 reproduce in Xiaomi 17T. (kernelsu incomplete)
 winslowe/cve-2024-4309-analysis
BGT-Pentest-LAB Final Project: Xiaomi HyperOS System Updater OTA Signature Verification Bypass (CVE-2024-4309) Deep Analysis.
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…