
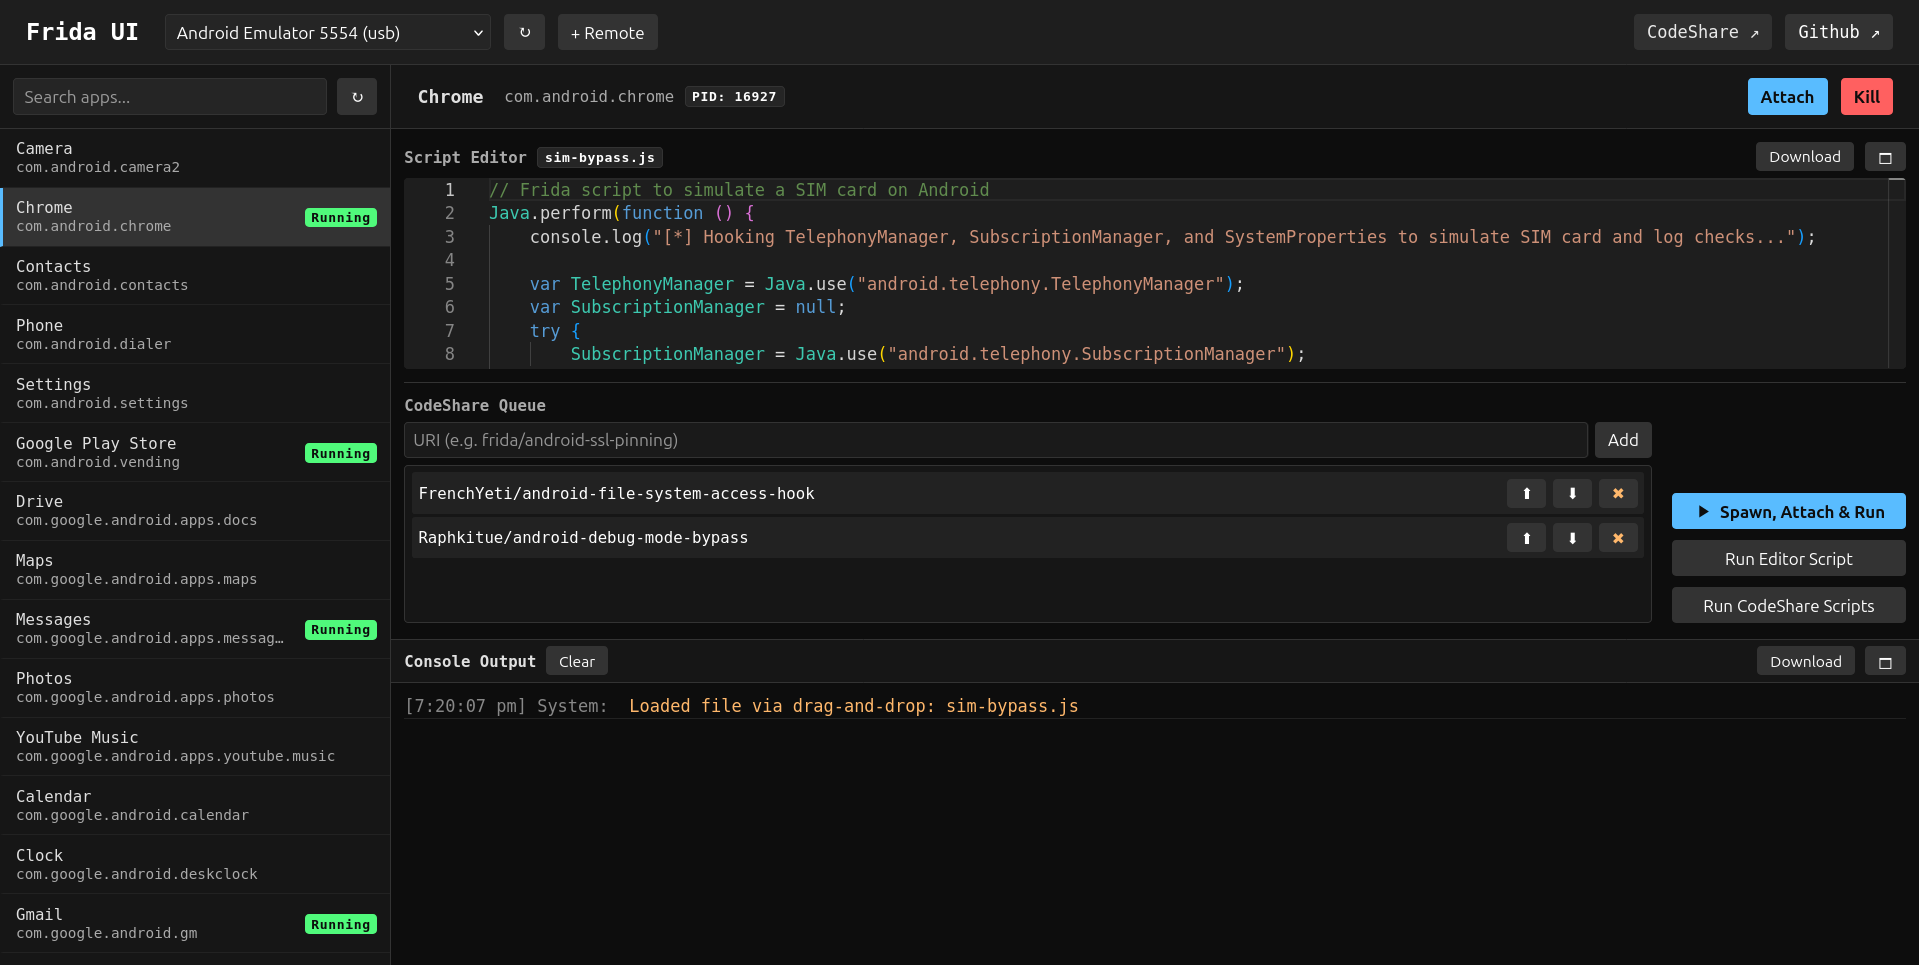
frida-ui
 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
android-securitydebuggersdynamic-analysis-sandboxing+5
243
adityatelange/frida-uiInteract with Frida devices, processes, and scripts directly from your browser.
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 geosn0w/pentagram-exploit-tester
A test app to check if your device is vulnerable to CVE-2021-30955
 r0rt1z2/huawei-unlock
Unlock your Huawei device with ADB (CVE-2019-2215)
 roeeh/bootmodechecker
This app checks if you're vulnerable to CVE-2016-8467 and/or if your bootmode property has been tampered with.
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 focused.hunts/the.vault
Privacy-first password manager with local storage and bring-your-own-cloud sync across Google Drive, Microsoft OneDrive, and Dropbox. Your…
 roeeh/conscryptchecker
This app verifies if your device is still vulnerable to CVE-2015-3825 / CVE-2015-3837, aka "One Class to Rule Them All", by checking if it contains…
 pwnaccelerator/stagefright-cve-2015-3864
PoC - Binary patches for CVE-2015-3864 (NOT for production, use at your own risk)
 sunnyjiang/shellshocker-android
This is an Android Application that helps you detect if your machine that run bash is vulnerable by CVE-2014-6271
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…