

fleet
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
cloud-securityconfiguration-auditingdefensive-tools+4
6.9k
fleetdm/fleetOpen-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 alterakey/trueseeing
Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
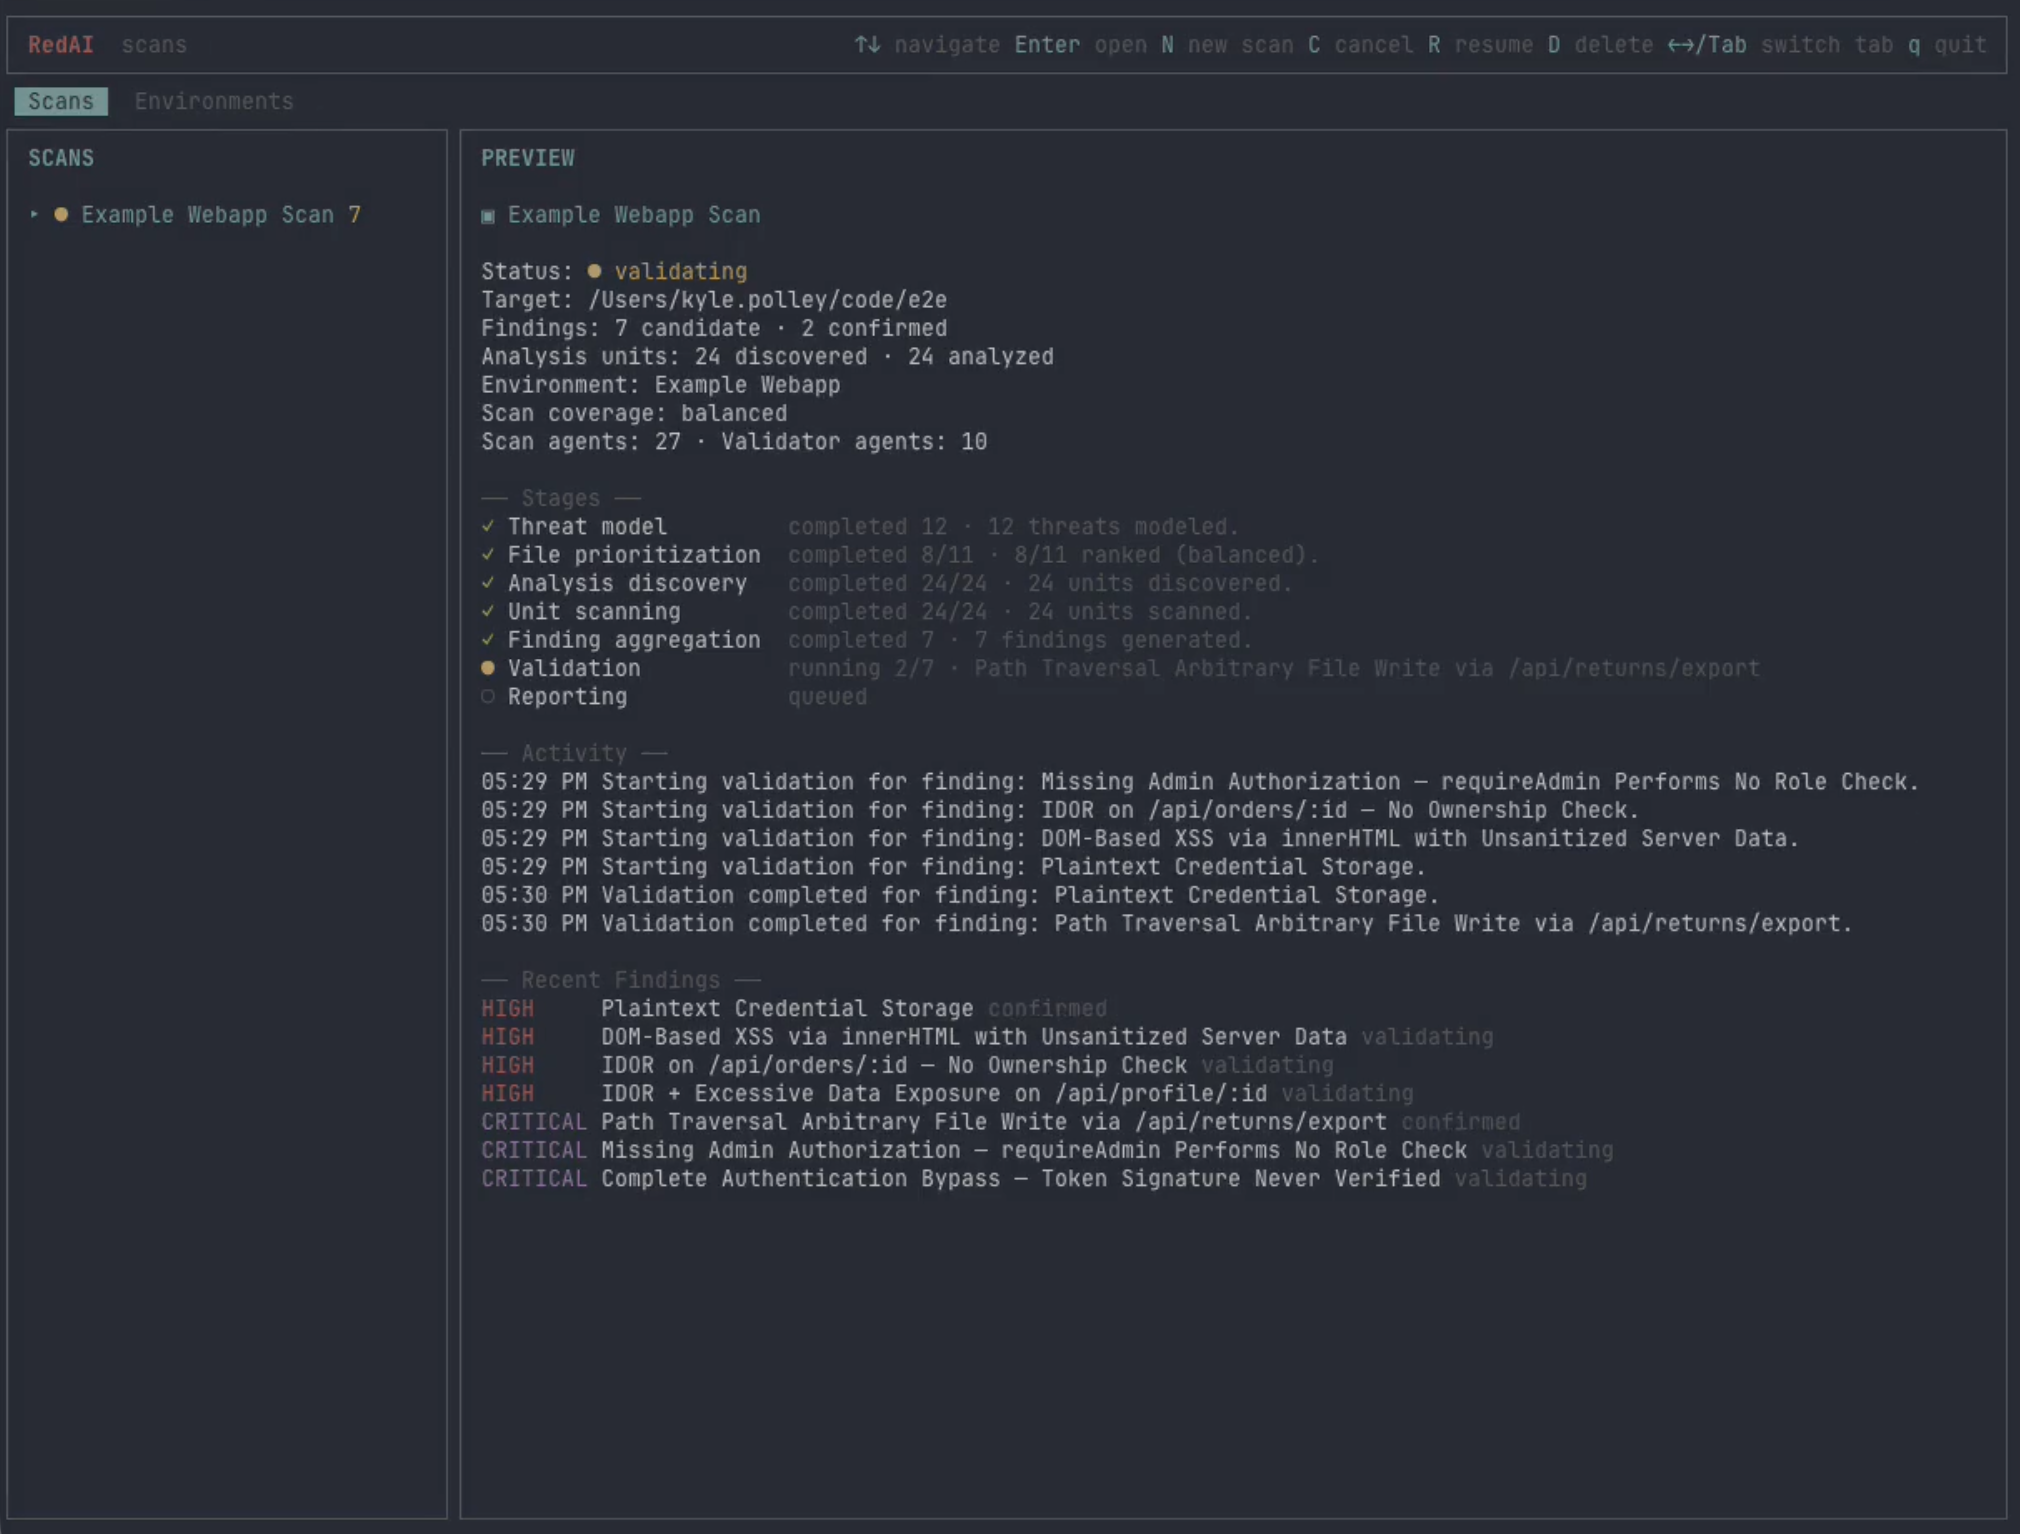 kpolley/redai
AI-driven vulnerability discovery and live validation
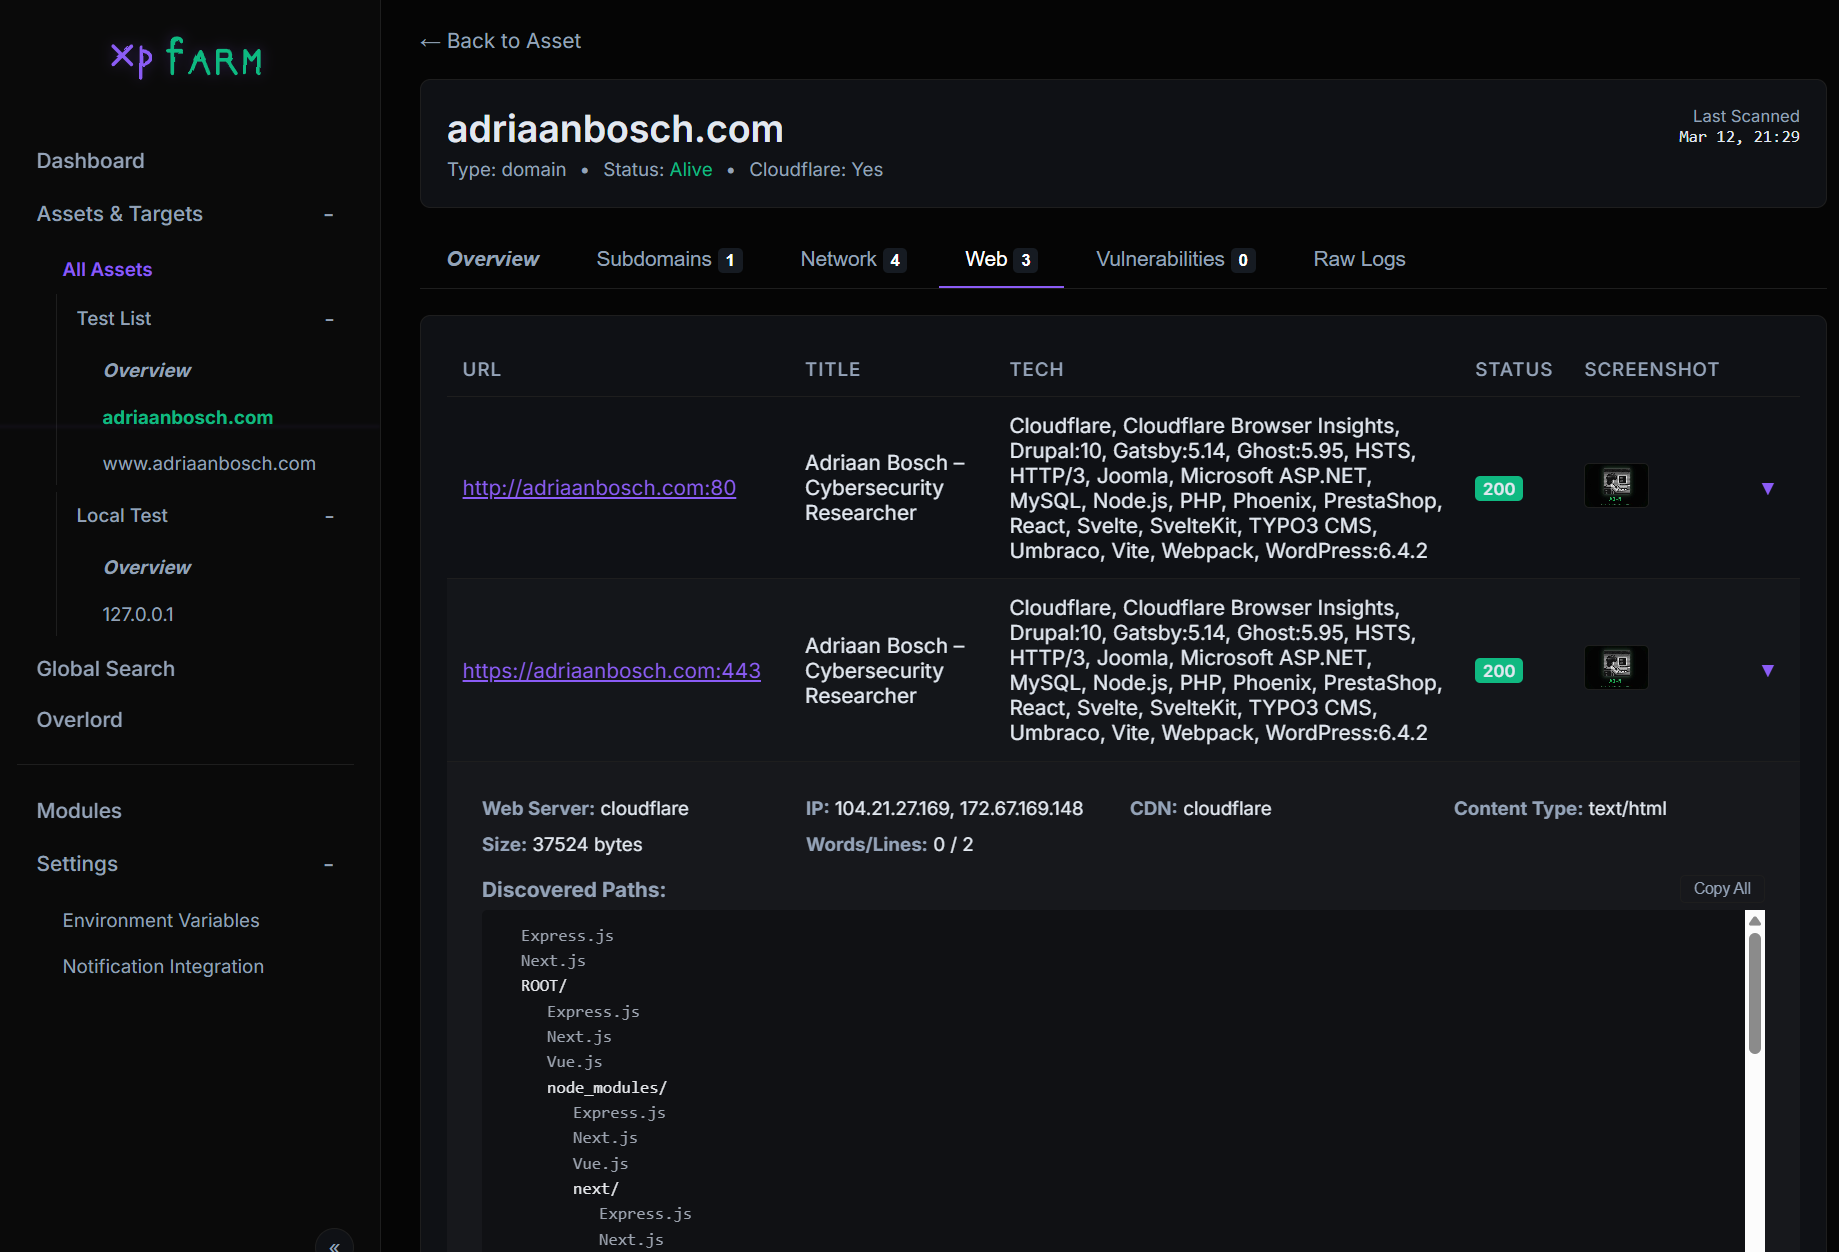 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
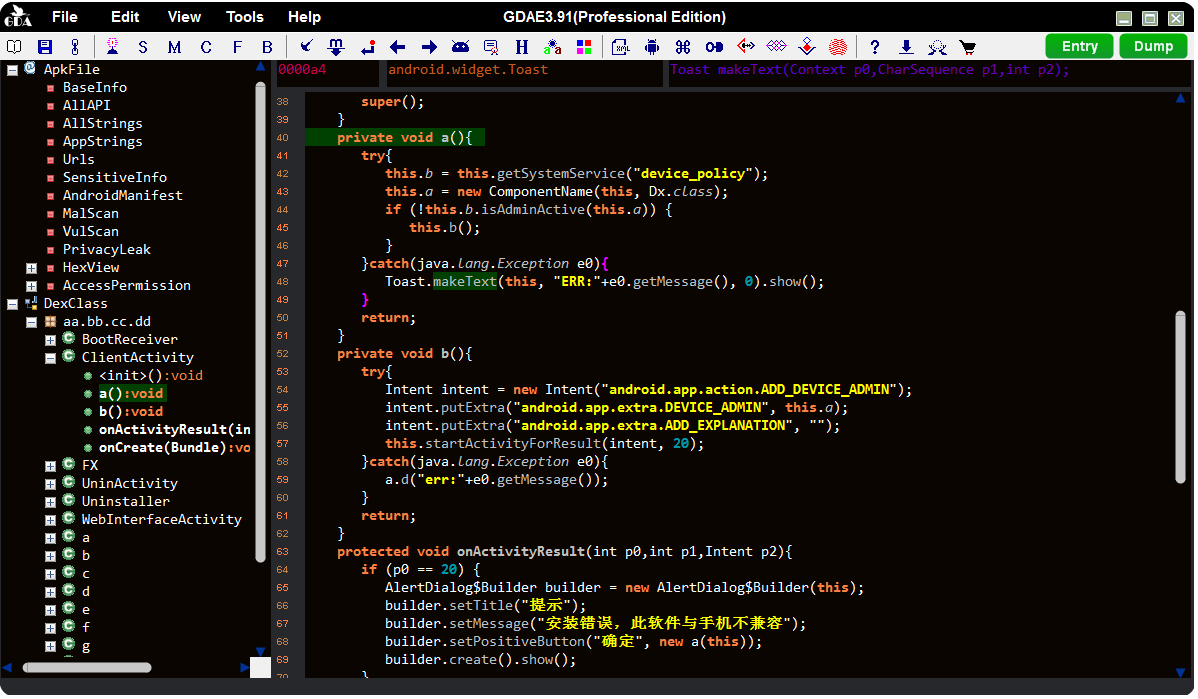 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 darkz2012/qualcomm-vulnerability-scanner
A tool to scan Android devices for the recently exploited Qualcomm flaw CVE-2026-21385, providing a simple and efficient way to identify vulnerable…
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
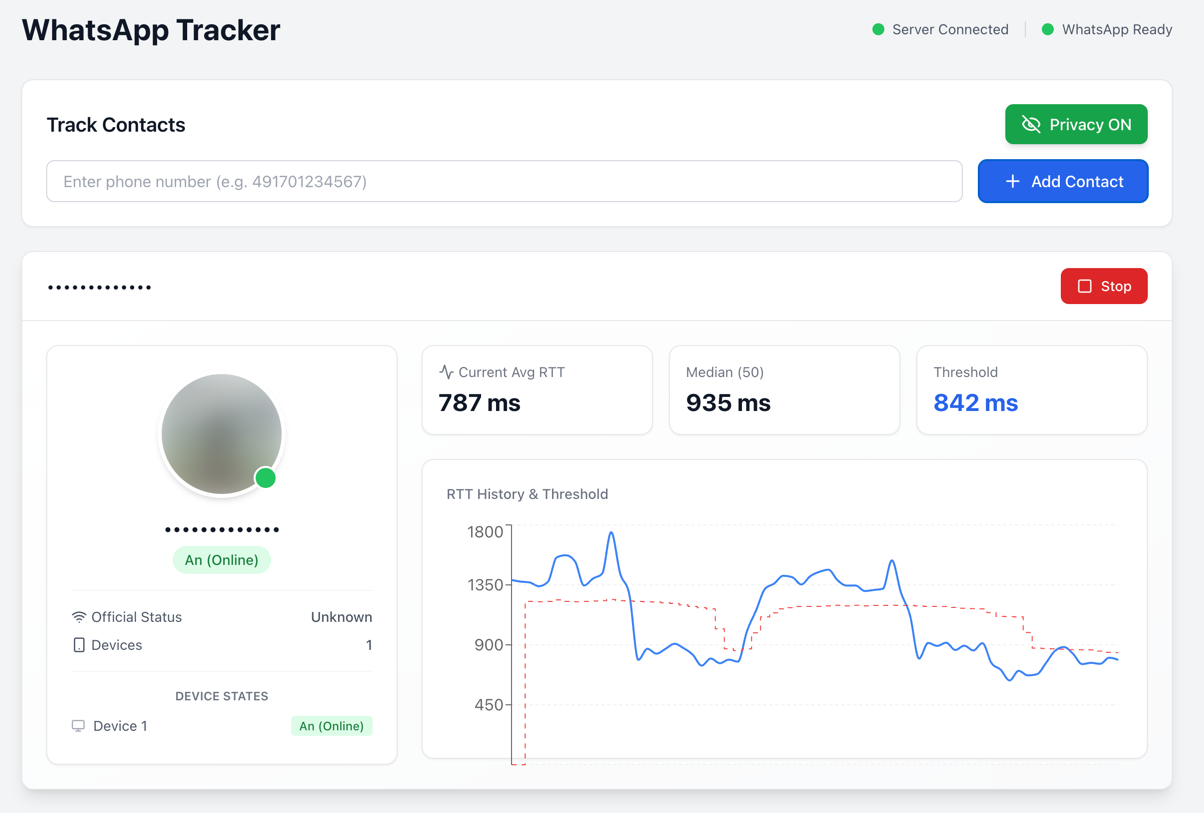 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 ajayantoisdev/wasonar
WhatsApp Intelligence & Resource Exhaustion Tool. Features real-time device tracking, silent RTT probing, and protocol stress testing for security…