CVE-2026-0073
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
android-securityauthenticationcryptography+5
umarrehmansiddiqui/cve-2026-0073Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 adityatelange/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
 elevenpaths/devicepairedtool
Tool for testing and auditing Bluetooth device pairing security, identifying vulnerabilities in wireless pairing protocols and hardware IoT…
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
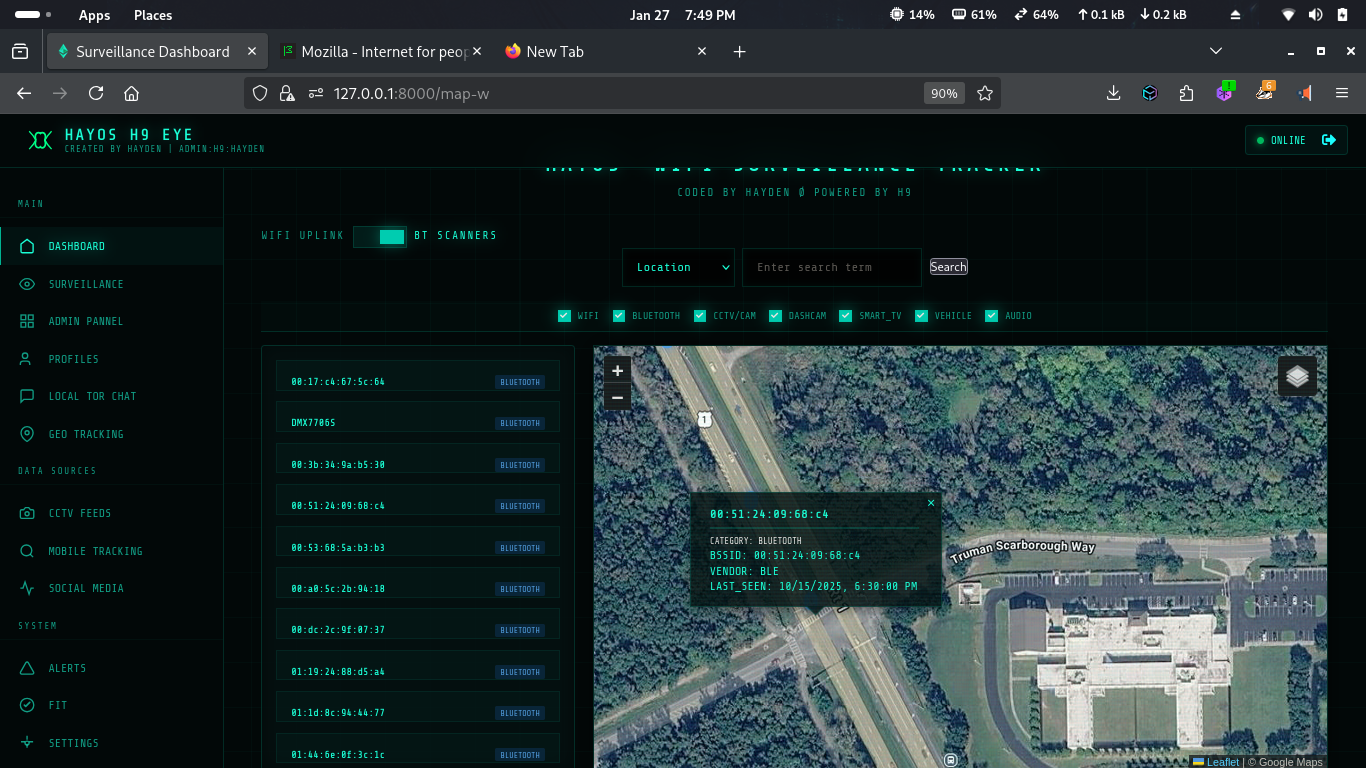 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 aau-network-security/hostage
Low Interaction Mobile Honeypot