

cve-2023-6931-pipa
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
android-securitybinary-exploitationexploitation+6
yutori-natsu/cve-2023-6931-pipaKernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
 mke84/neo8-ghostlock-adaptation
iQOO Neo8 (PD2301, 5.10.246 GKI) CVE-2026-43499 GhostLock 适配 · 48 宏 target.h + offsets.json + 15 轮实测 log · 只缺 write layer
 deancyl/s9180-rootmygalaxy
RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox
 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.
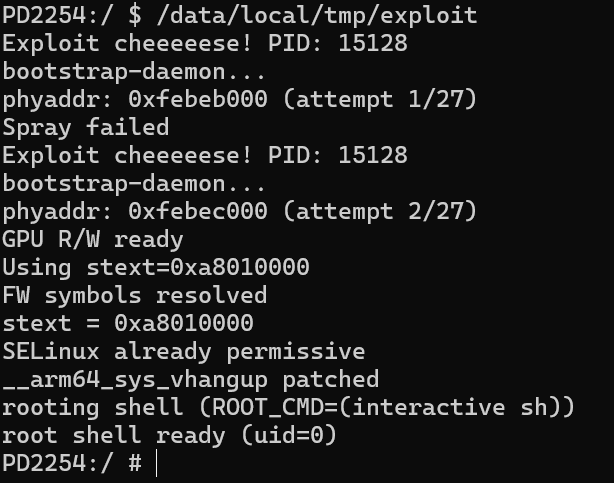 xianwan1314/cve-2025-21479-iqoo11pro
CVE-2025-21479 (Qualcomm Adreno GPU) reproduction notes for vivo iQOO 11 Pro (PD2254) - authorized research
 imeiplus/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
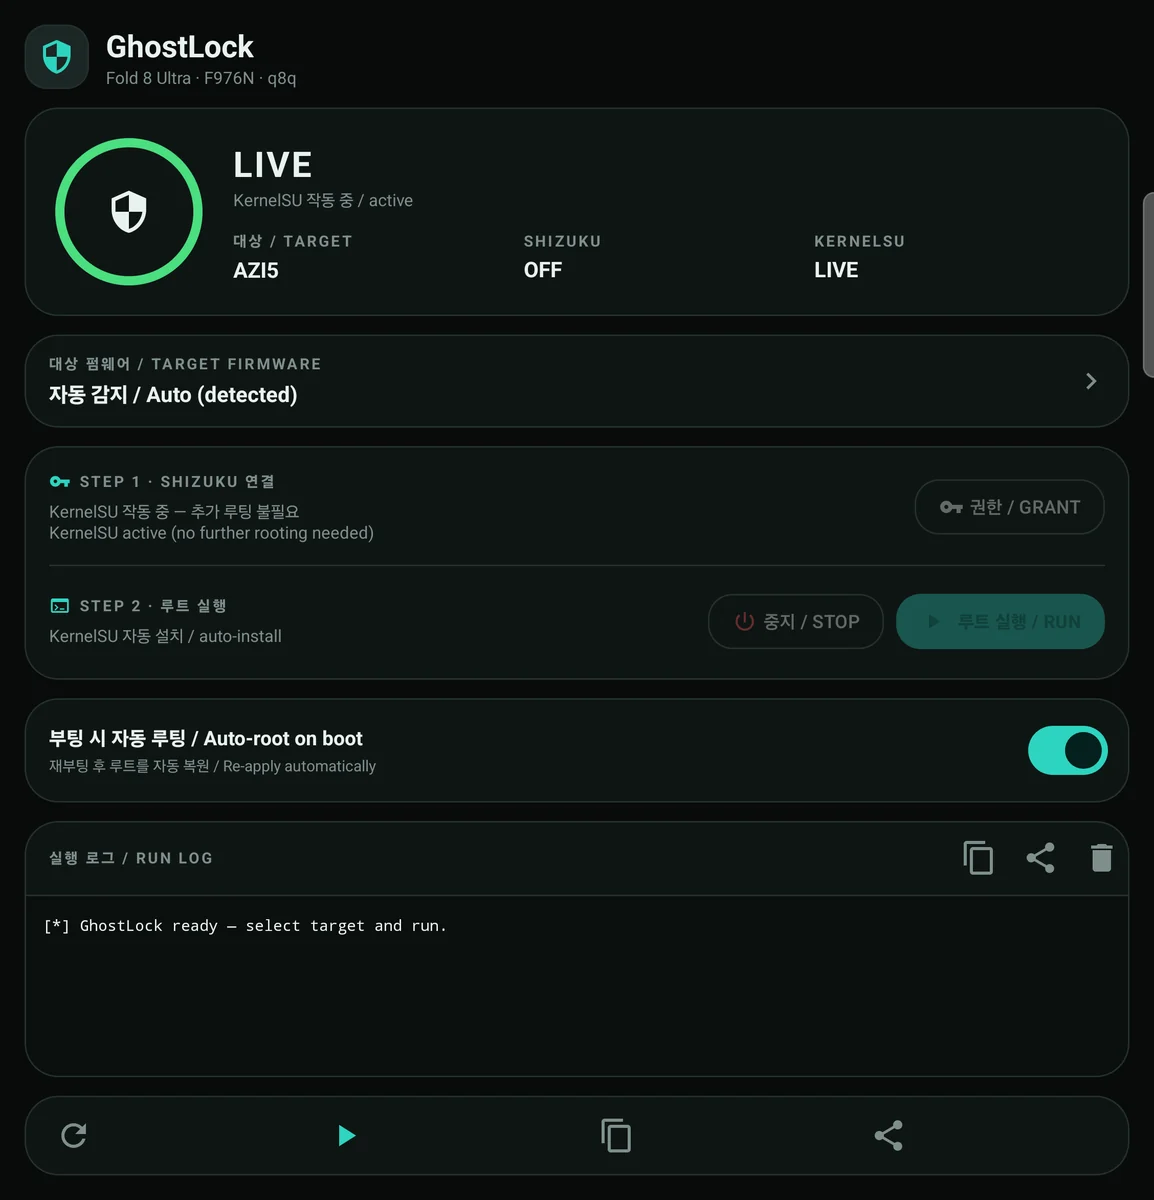 coey0814/fold8-ultra-root-f976n
One-tap KernelSU installer for the Galaxy Z Fold 8 Ultra (SM-F976N / q8q) using the CVE-2026-43499 late-load exploit via Shizuku. Supports…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 anksgls-sj/-help-vivo-y200i-5.10.218-gki-cve-2026-43499-stack-reclaim-reaches-0x300-need-0x318
Research notes and PoC development for CVE-2026-43499 (GhostLock) kernel UAF on vivo Y200i Android 14, covering futex PI-chain stack-reclaim…
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 rmdycz/k80pro-miro-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0