
JADXecute
 lauriewired/jadxecute
JADX-gui scripting plugin for dynamic decompiler manipulation
android-securitycode-analysisdebuggers+6
lauriewired/jadxecuteJADX-gui scripting plugin for dynamic decompiler manipulation
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
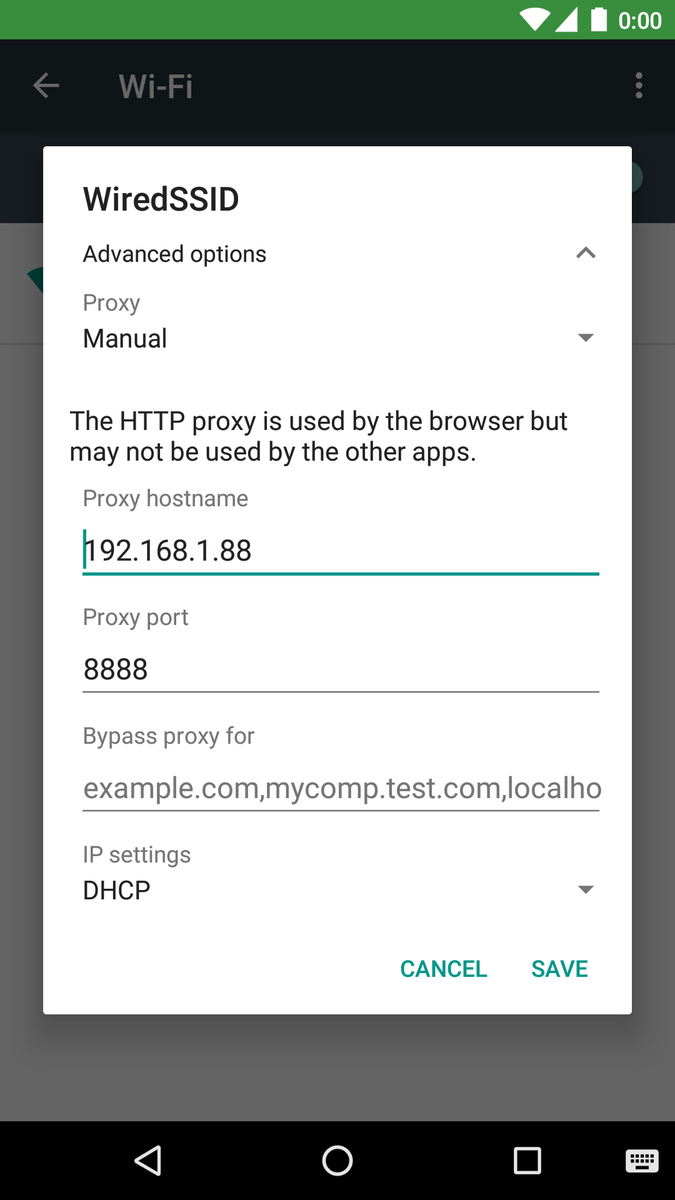 thyrlian/charles-proxy-mobile-guide
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.