Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Main repo for hosting release binaries

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

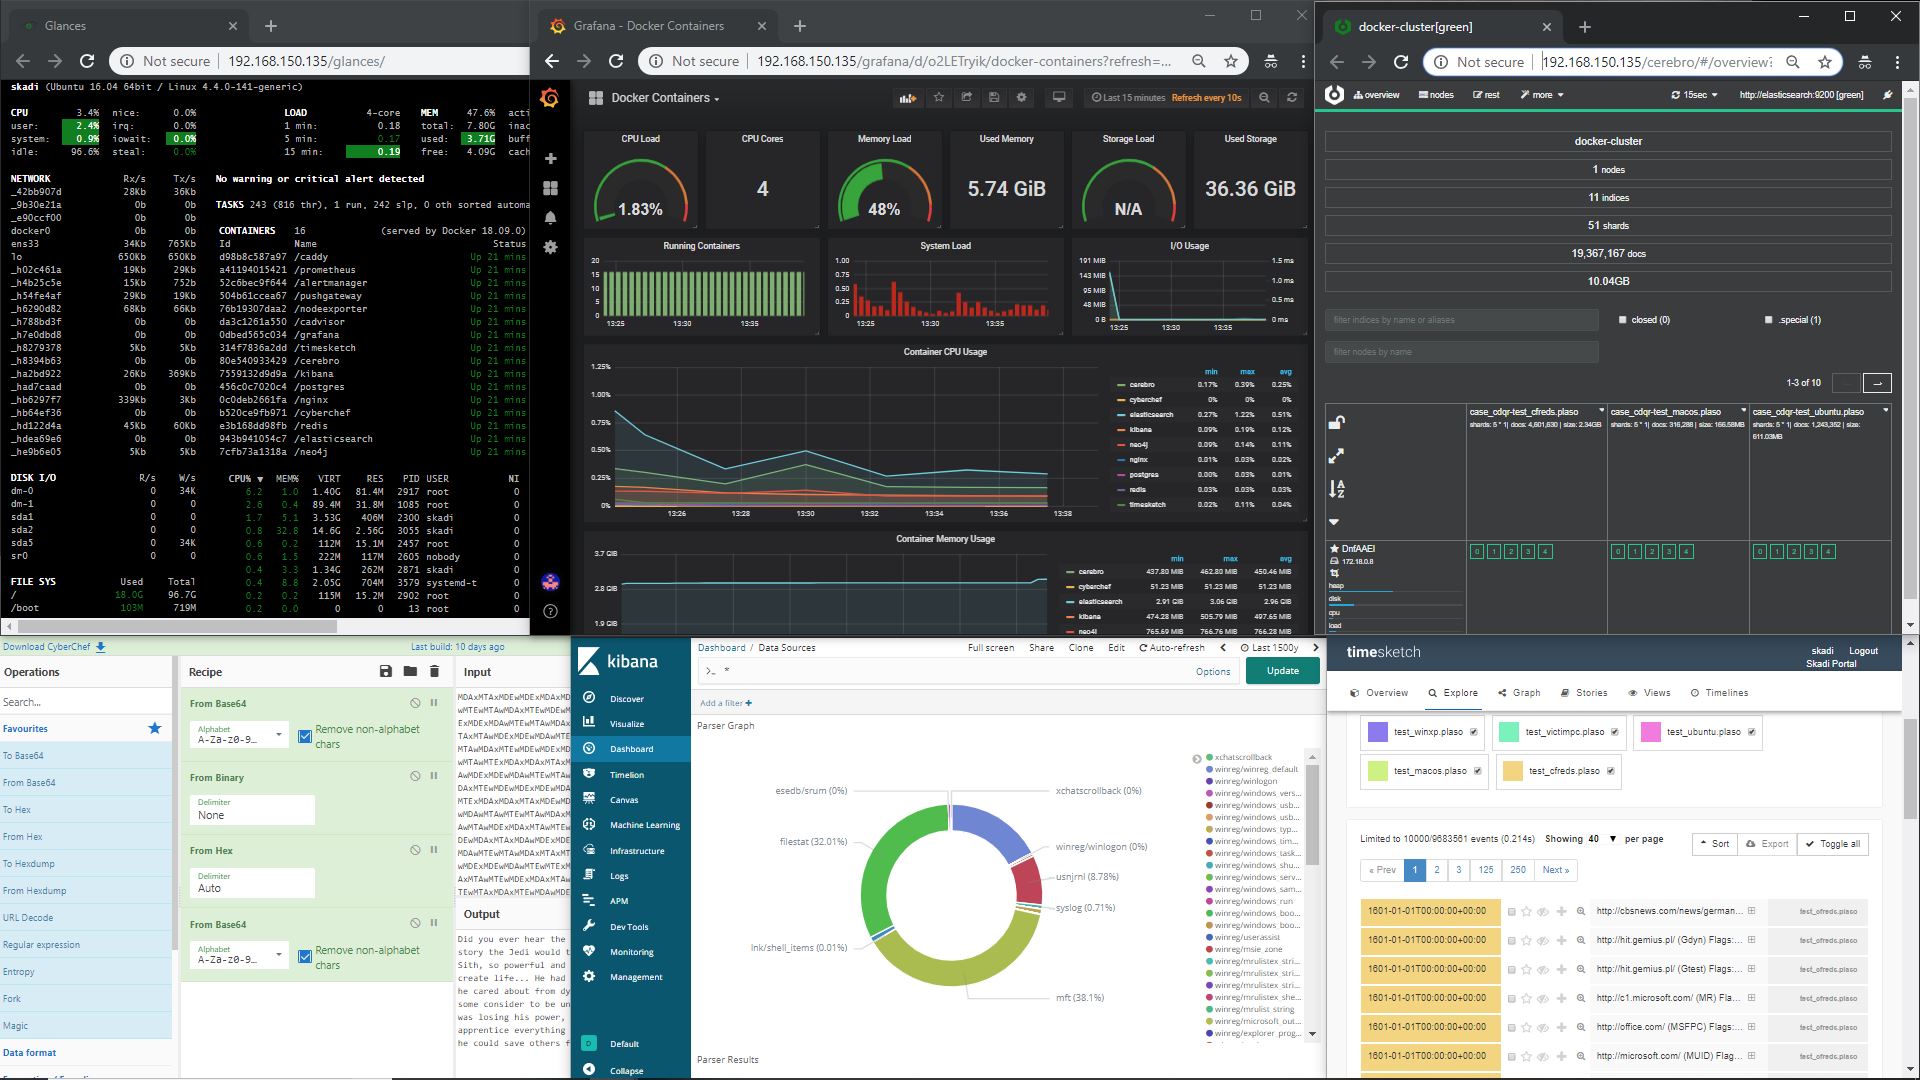
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

Reverse engineering and pentesting for Android applications

Free hands-on digital forensics labs for students and faculty

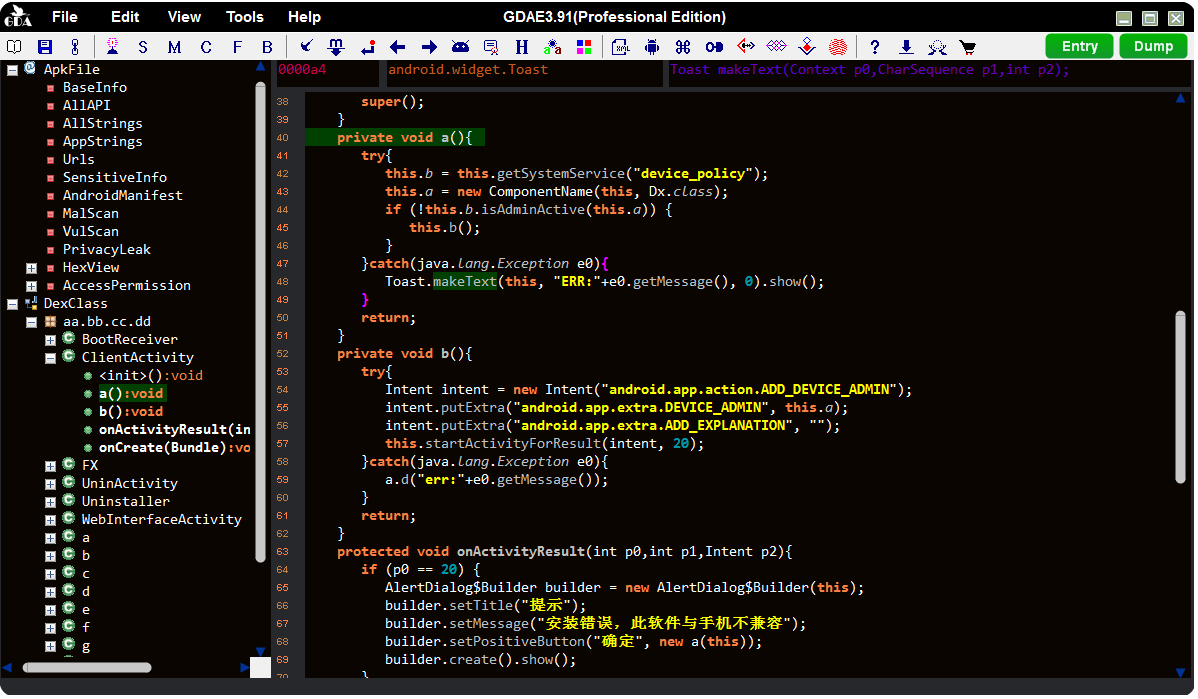
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

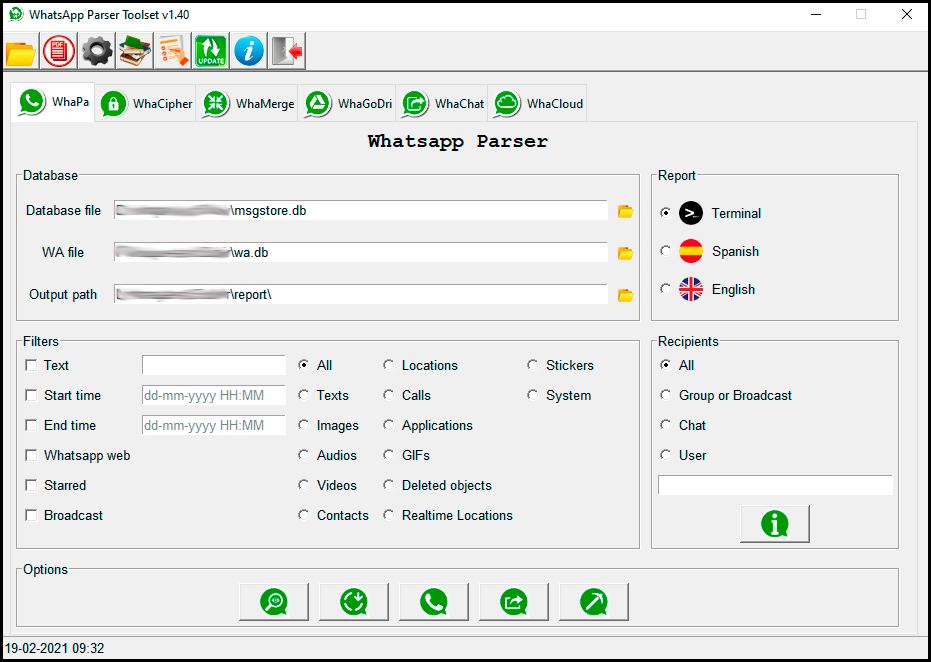
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

Radare2 and Frida better together.


Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

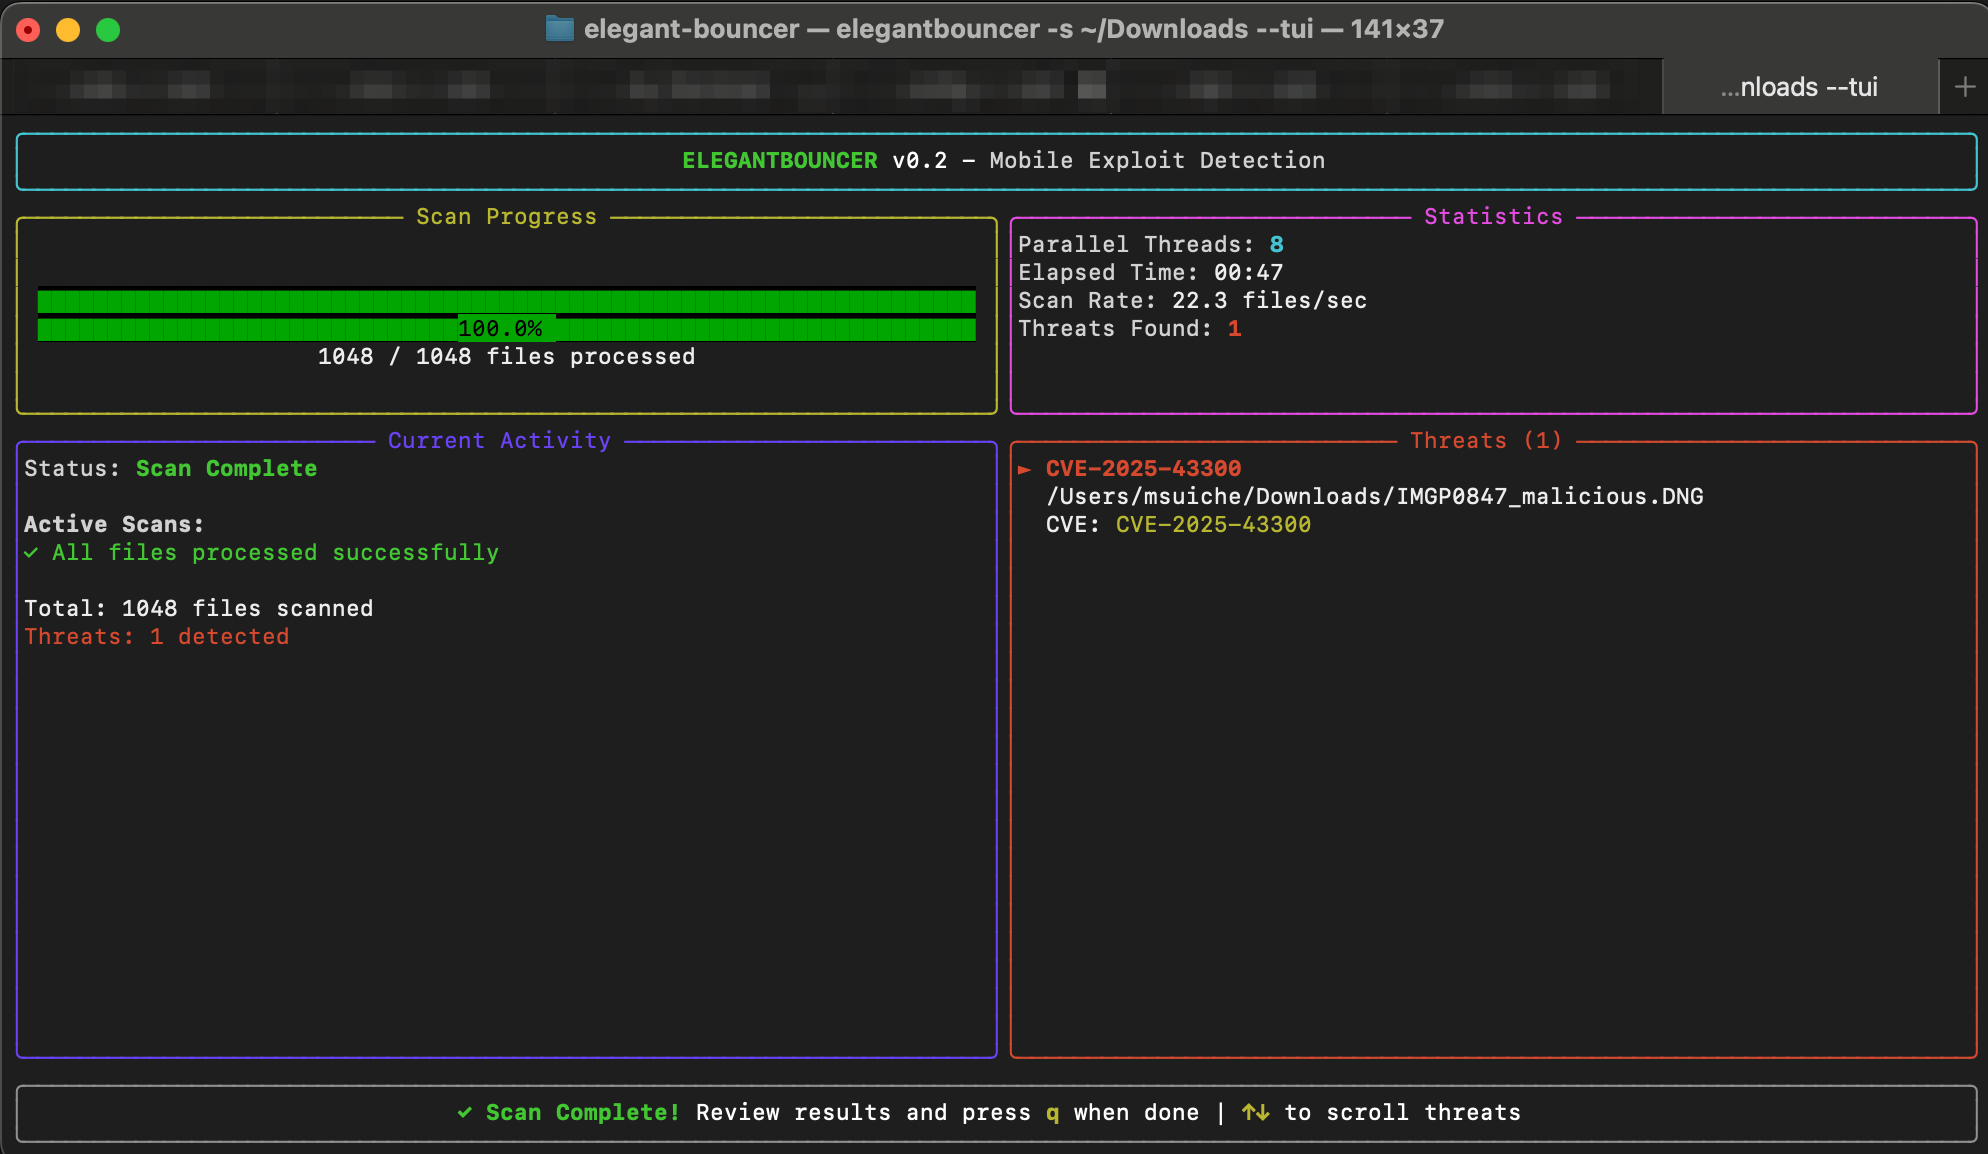
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

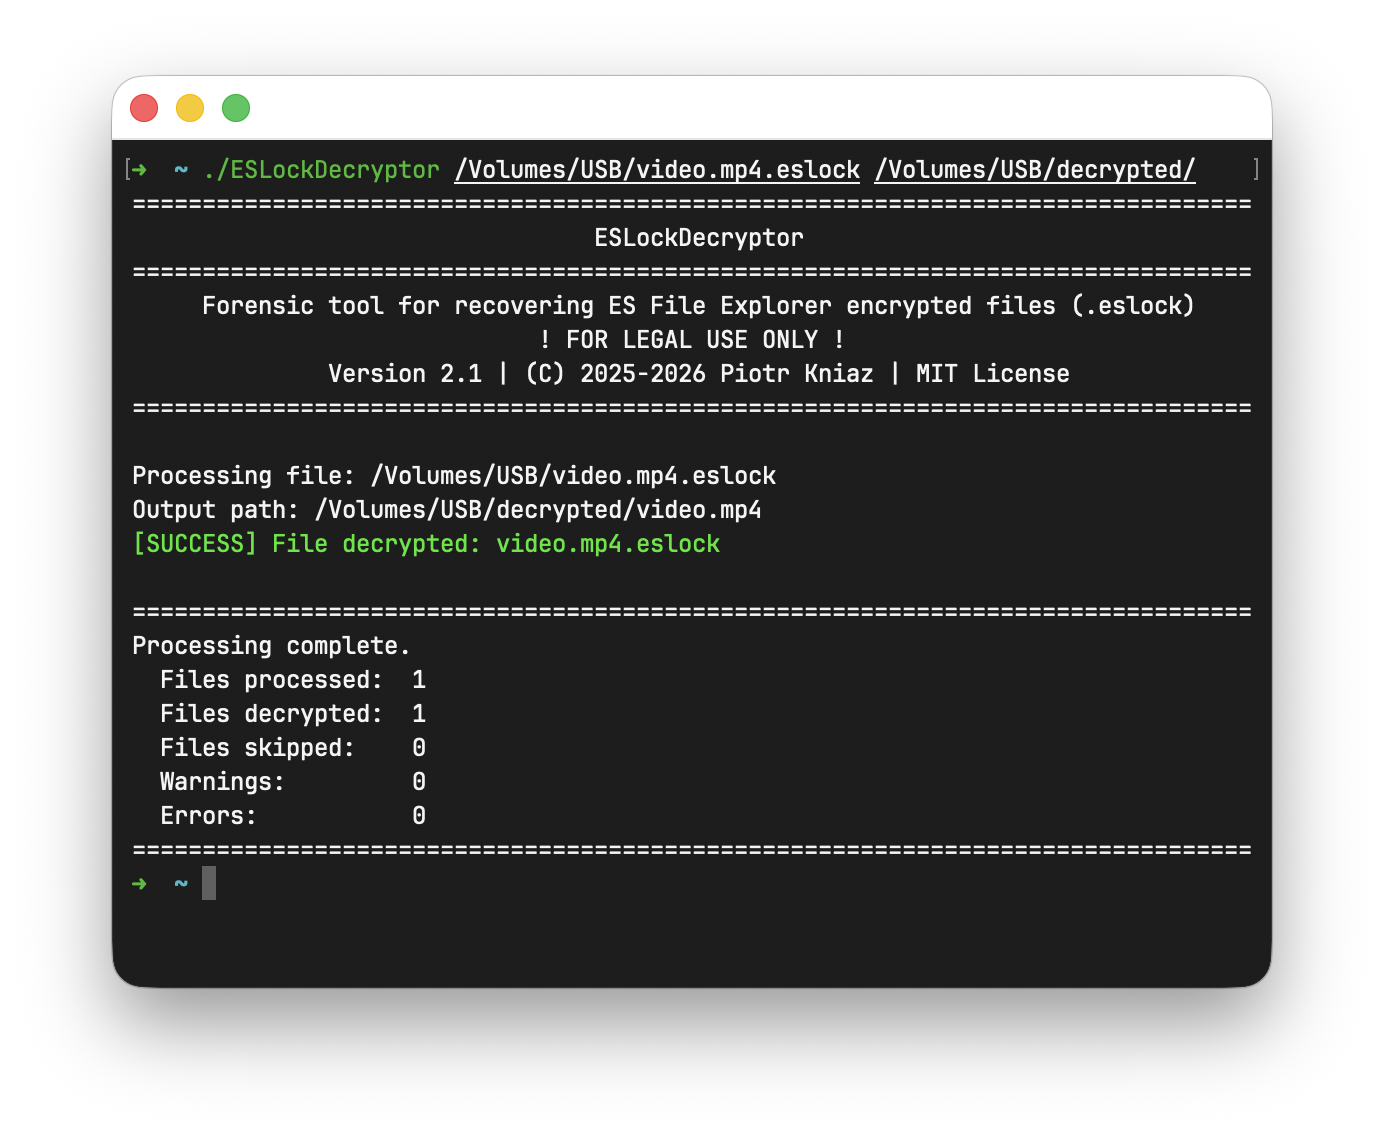
Utility for recovering ES File Explorer encrypted files (.eslock)

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.