

jadx
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
50.8k1 day ago
skylot/jadxCommand-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 levilutz/cve-2021-30860
Scan for evidence of CVE-2021-30860 (FORCEDENTRY) exploit
 nowsecure/r2frida
Radare2 and Frida better together.
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
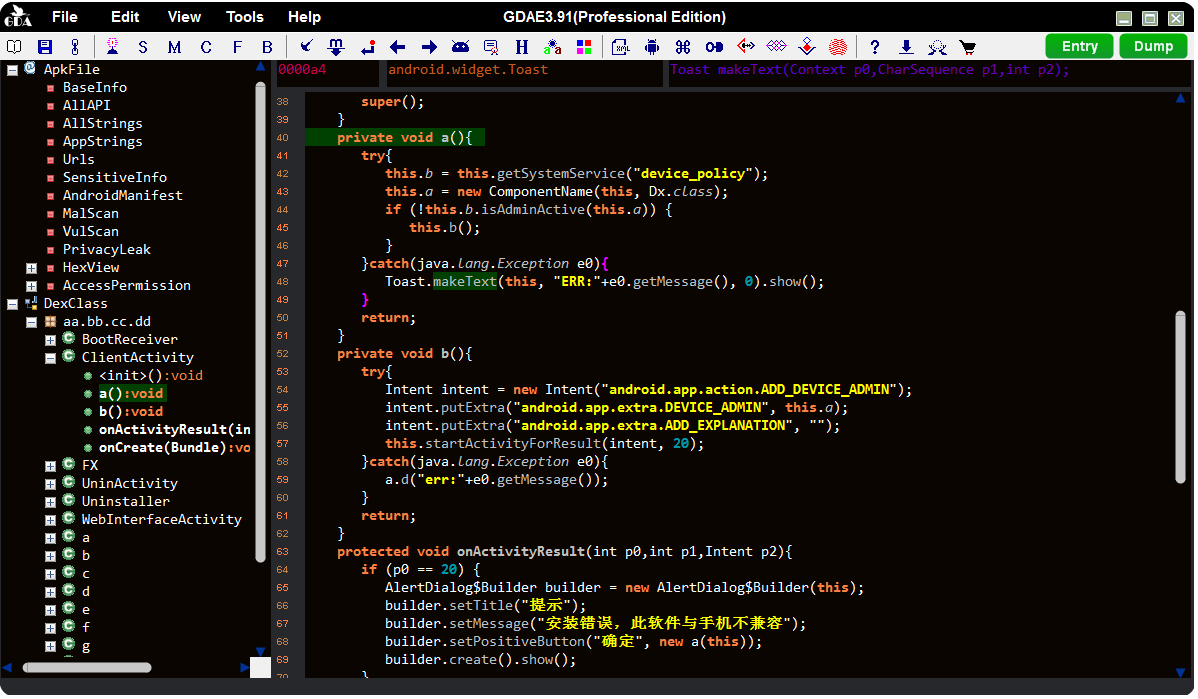 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 frida/frida
Main repo for hosting release binaries