
LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
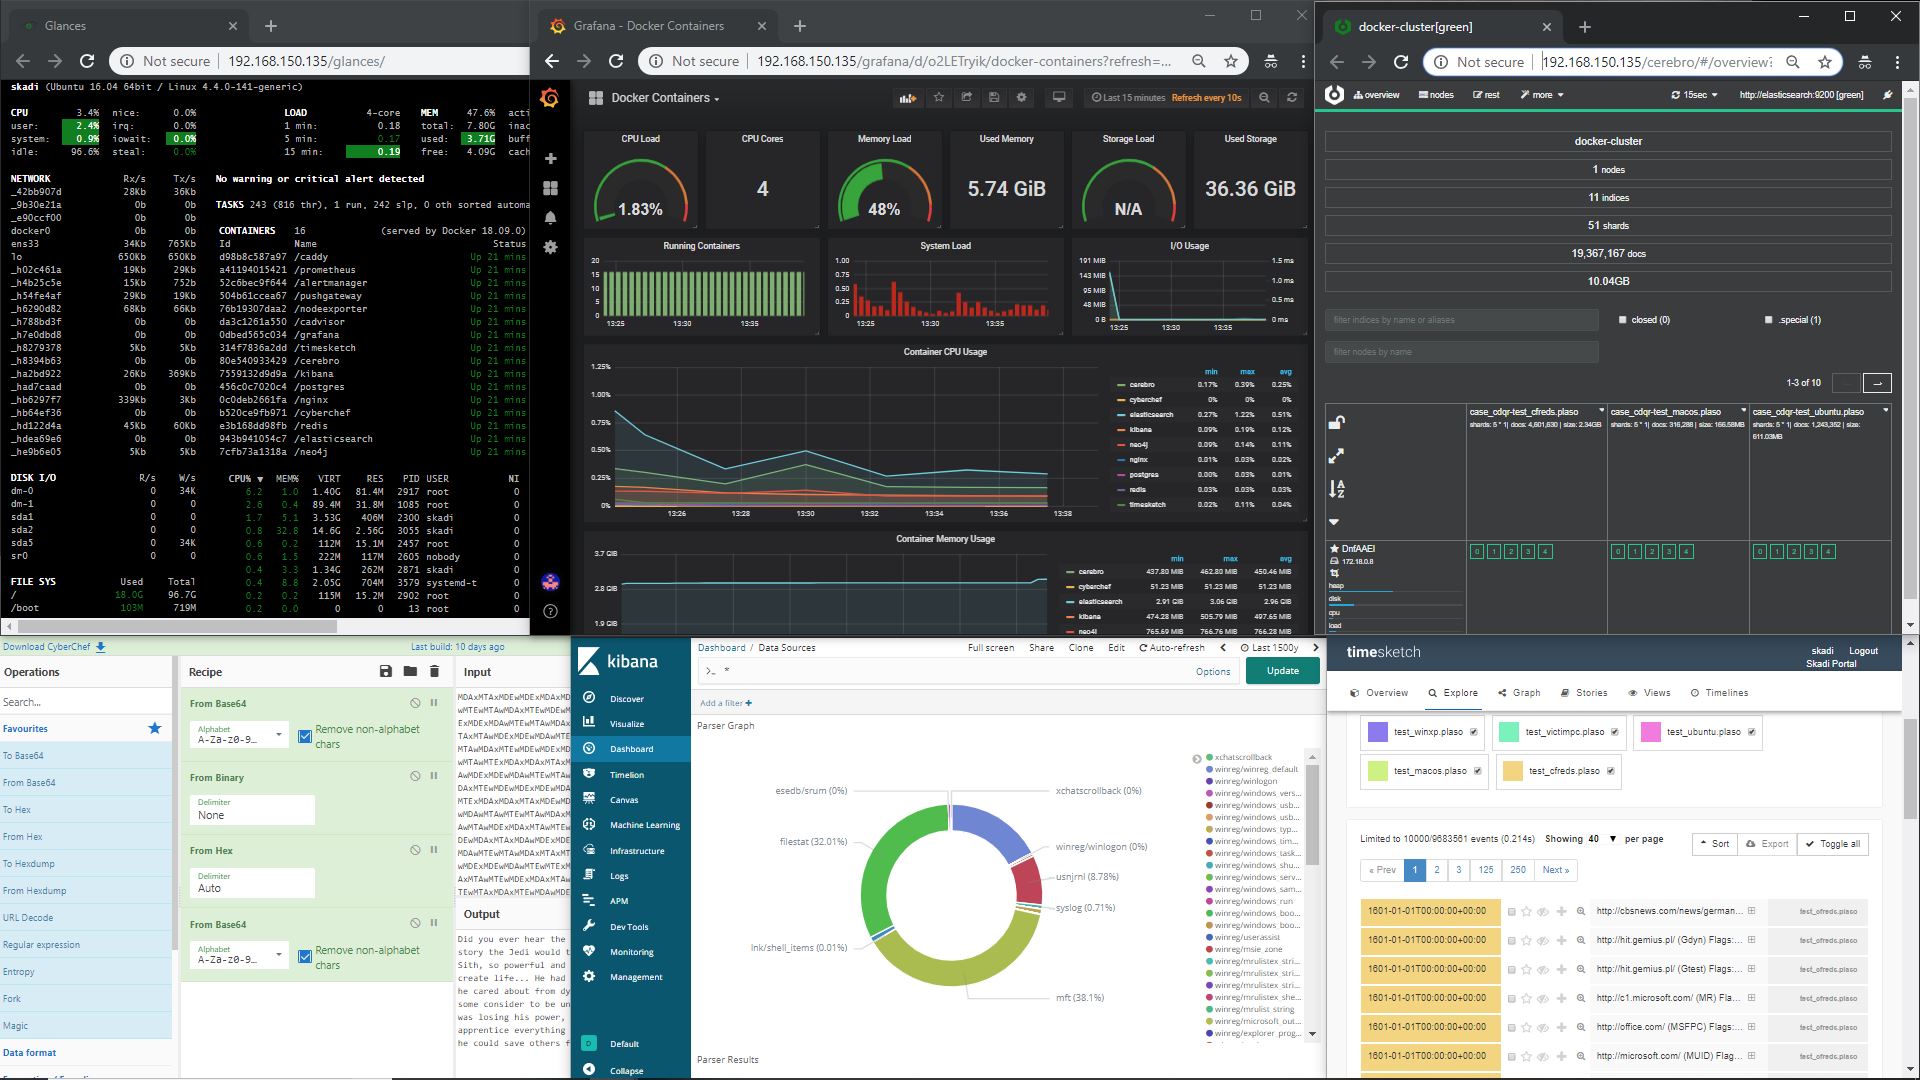 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 andrewrathbun/dfirartifactmuseum
The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 androguard/androguard
Reverse engineering and pentesting for Android applications
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
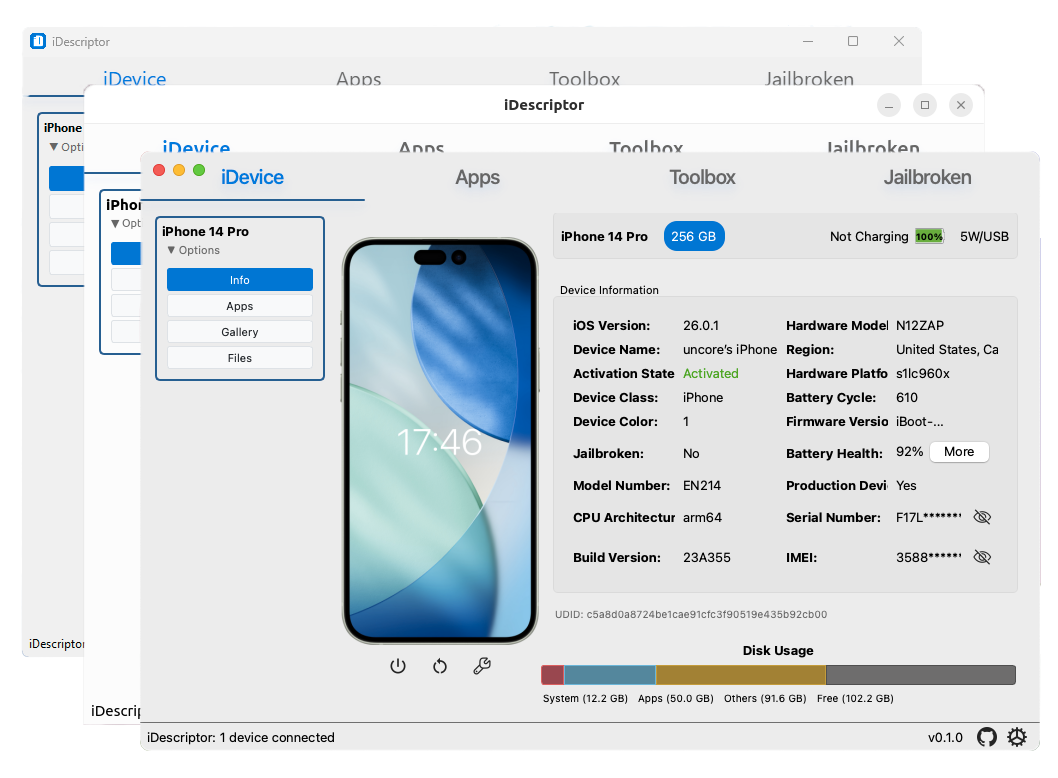 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
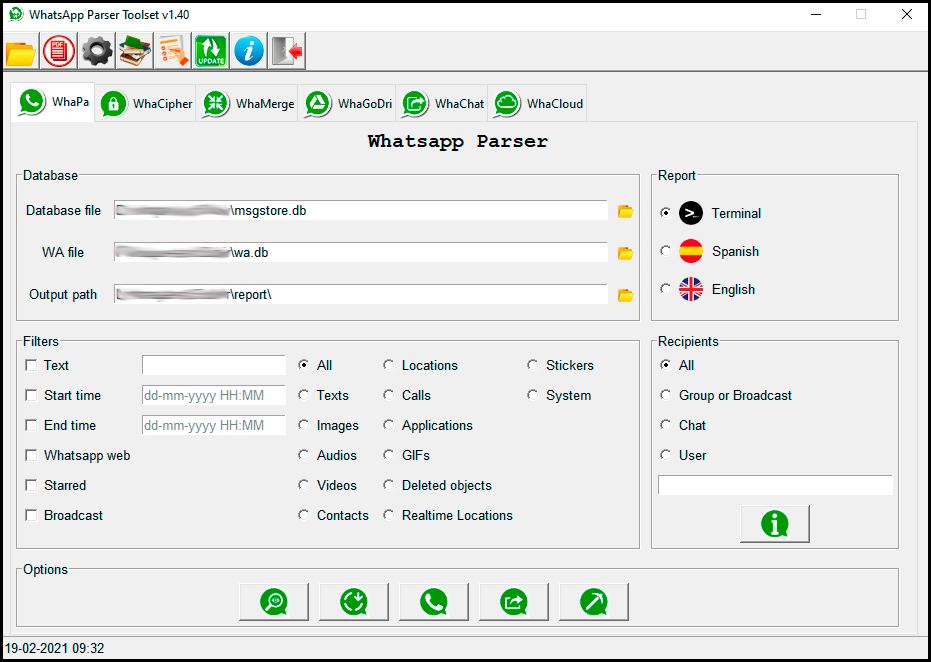 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
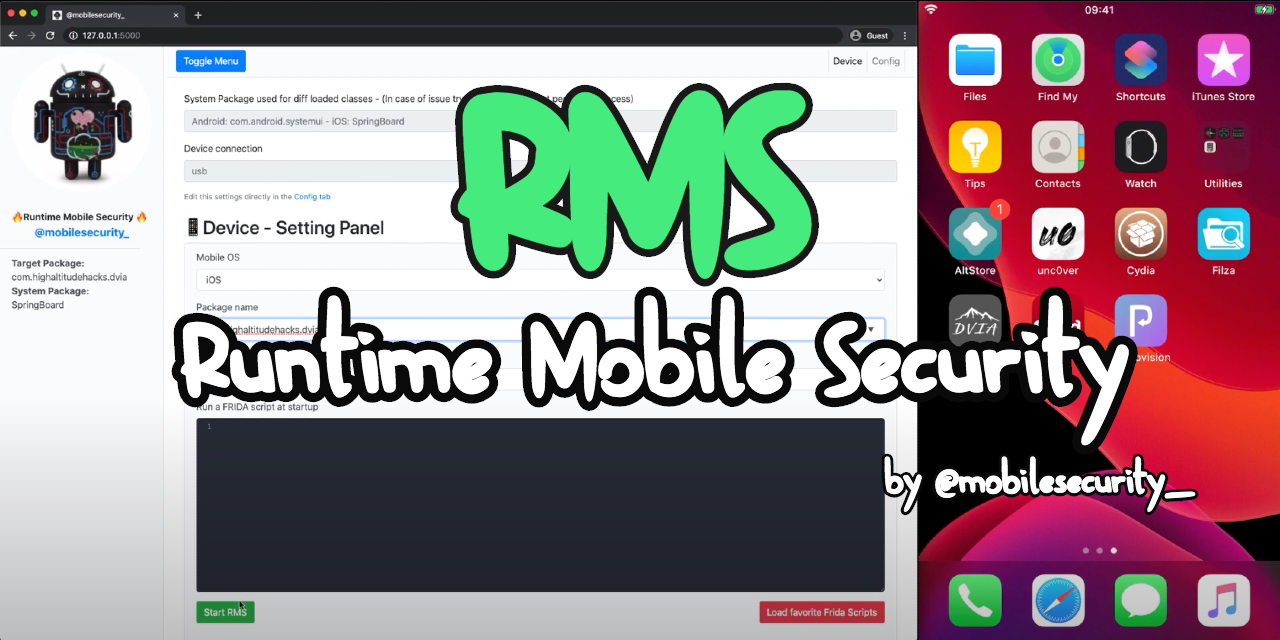 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…