
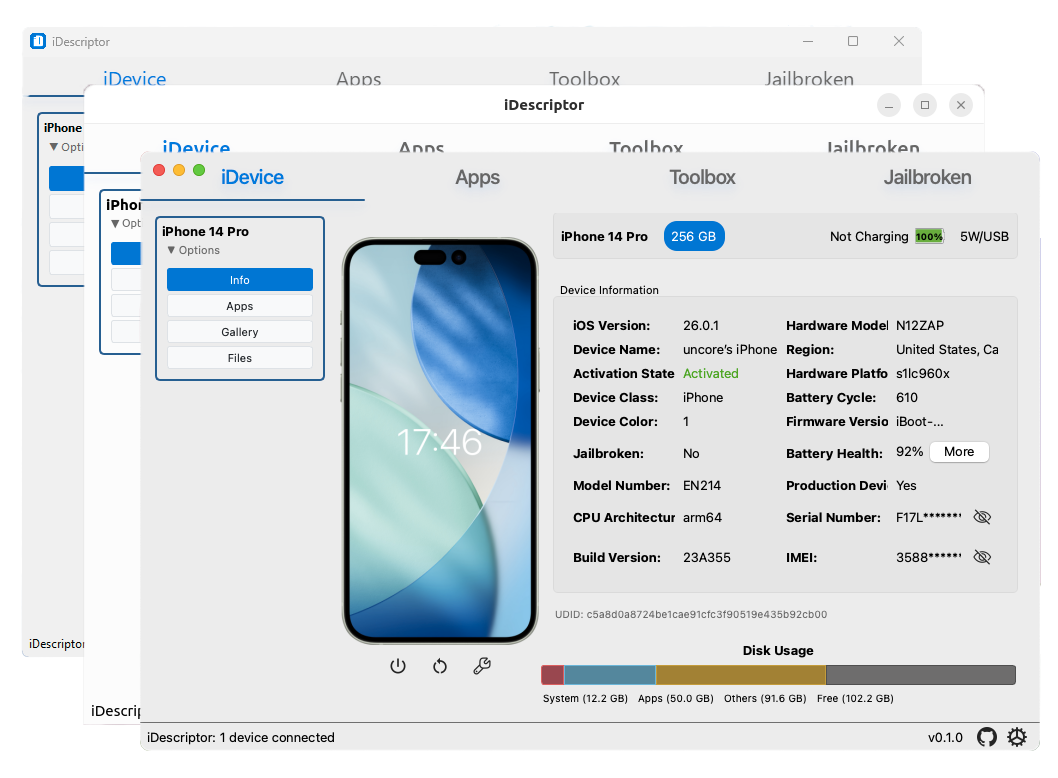
iDescriptor
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.7k
idescriptor/idescriptorprivacy-first, open-source and free idevice management tool written in Rust and Qt
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
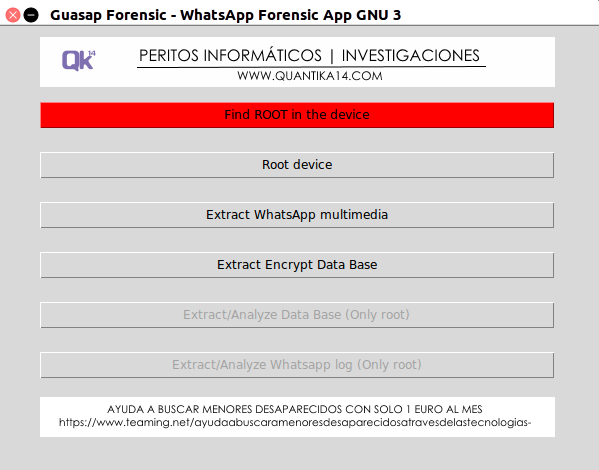 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
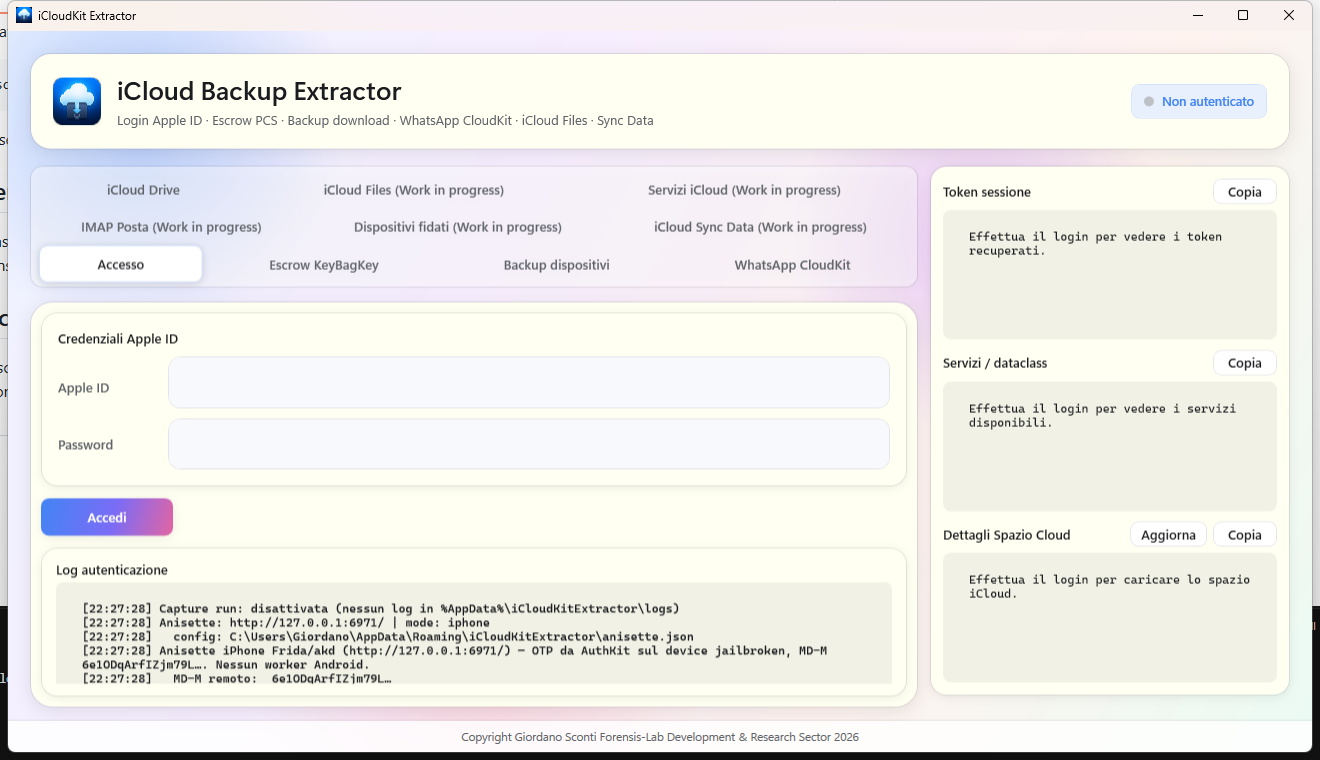 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…