

Telegrip
 telegrip/telegrip
GUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…
data-recoverydigital-forensicsforensics+1
19
telegrip/telegripGUI forensic tool for acquiring and analyzing Telegram data from Android devices. Parses messages, media, and metadata; generates integrity-verified…
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
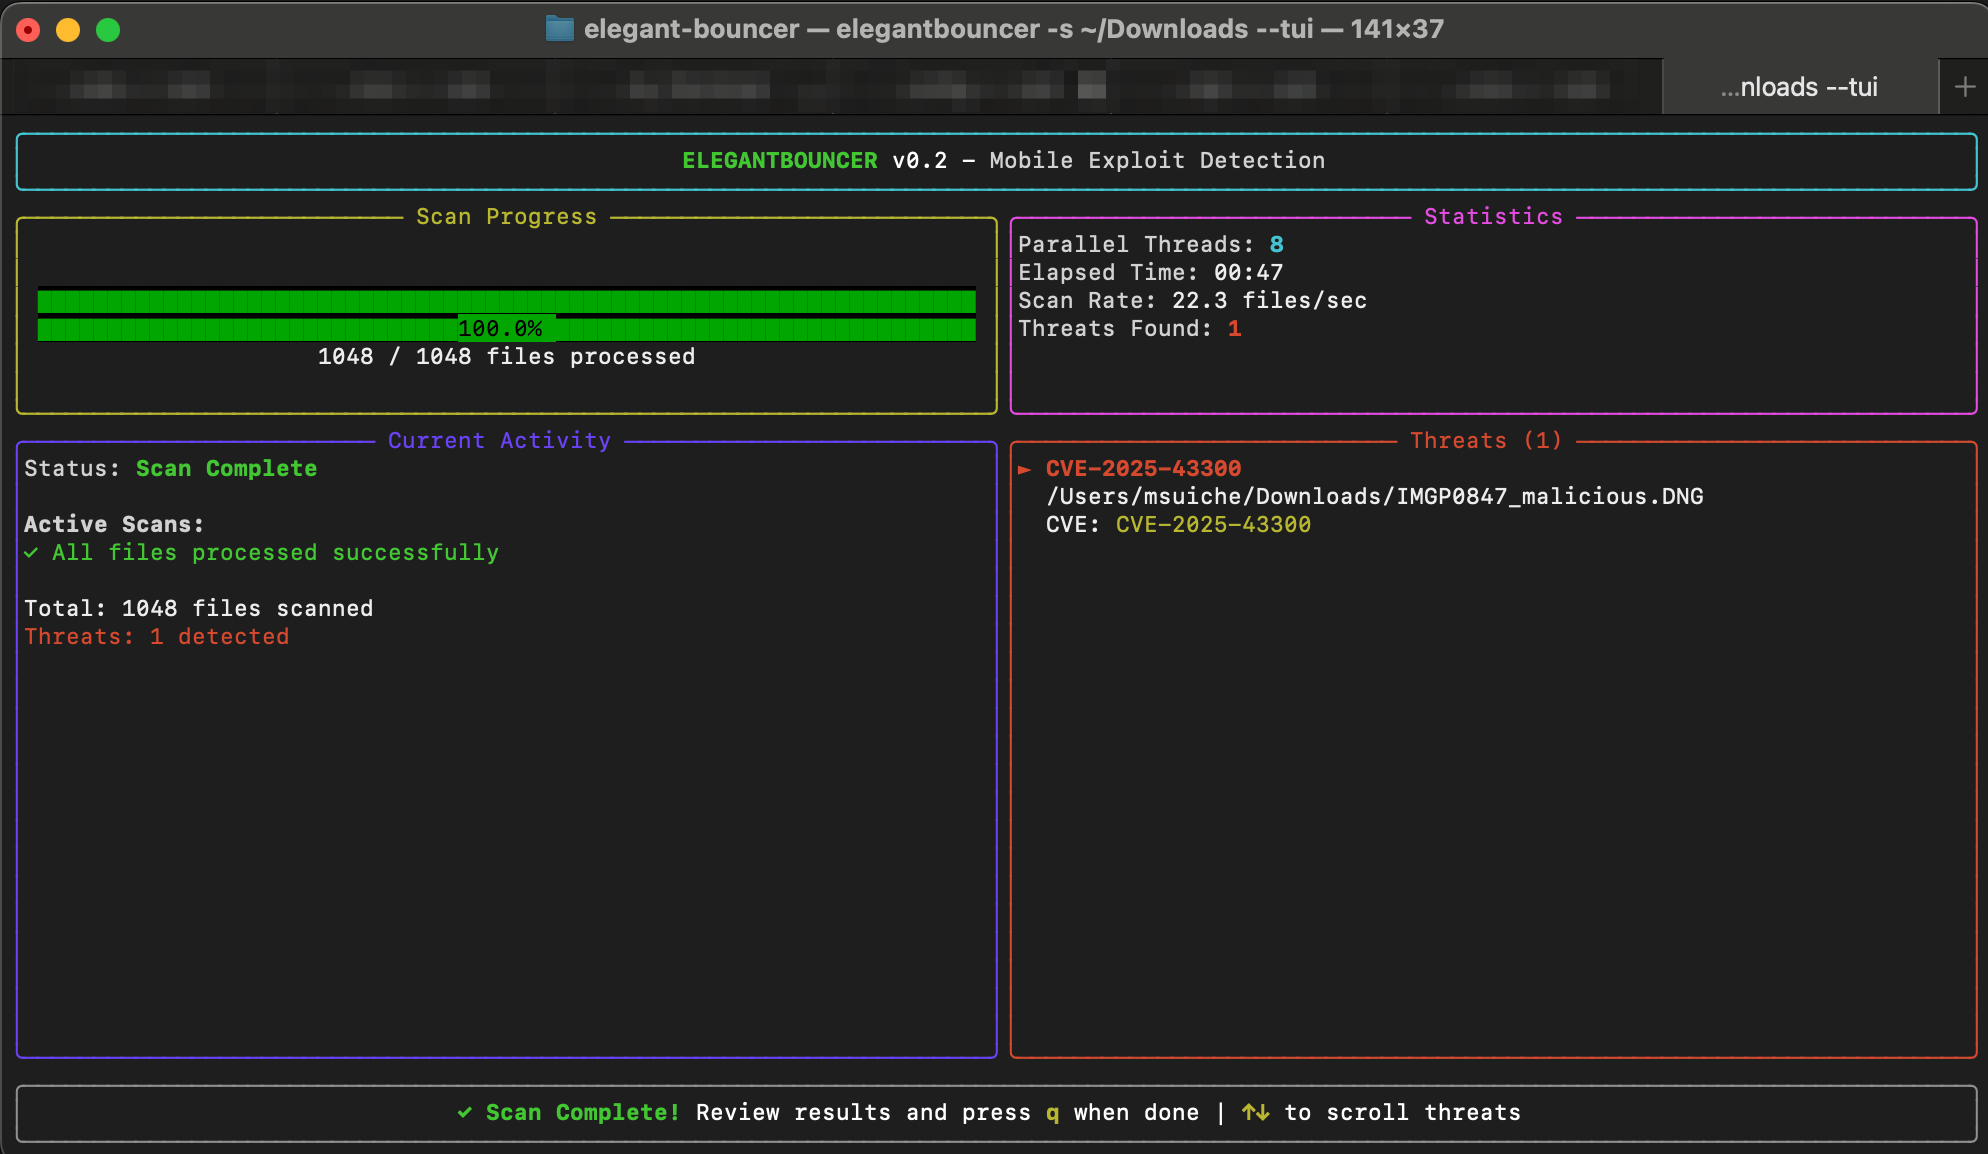 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
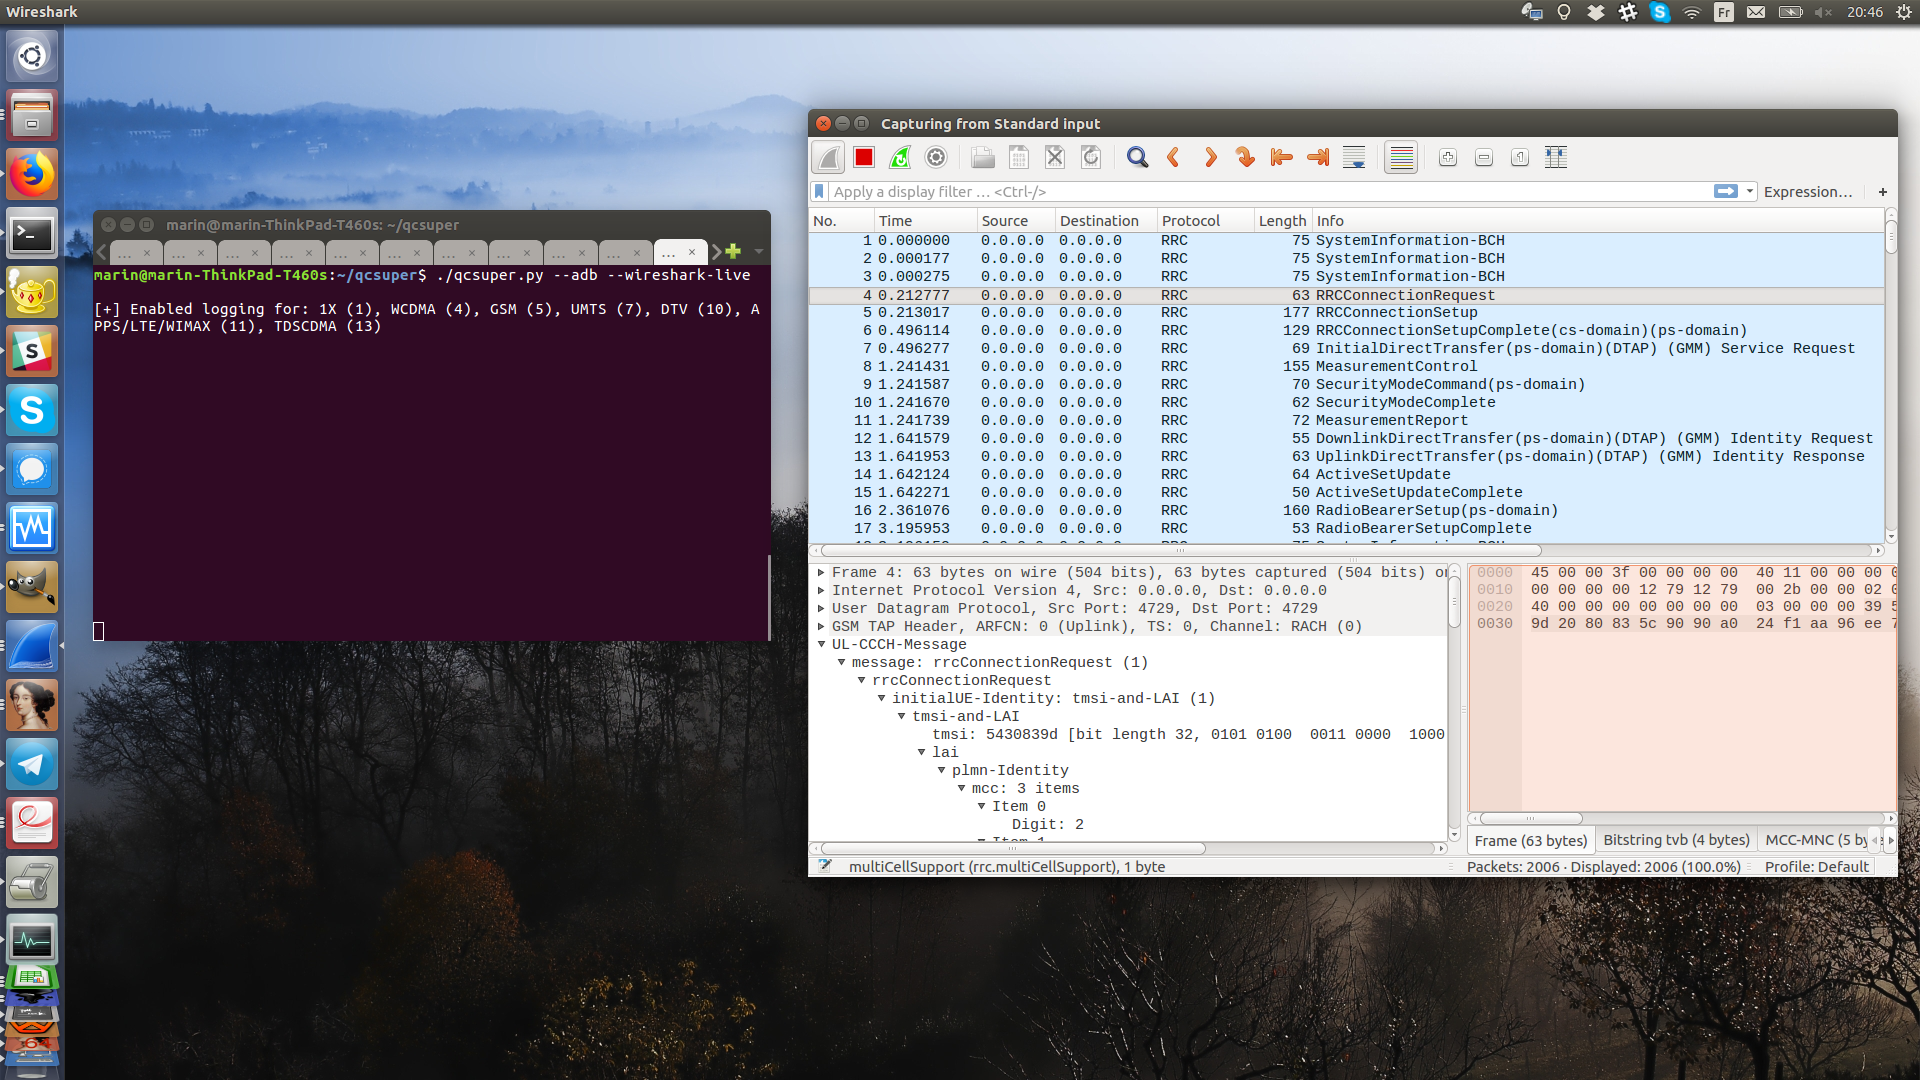 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

 simsong/bulk_extractor
This is the development tree. Production downloads are at:
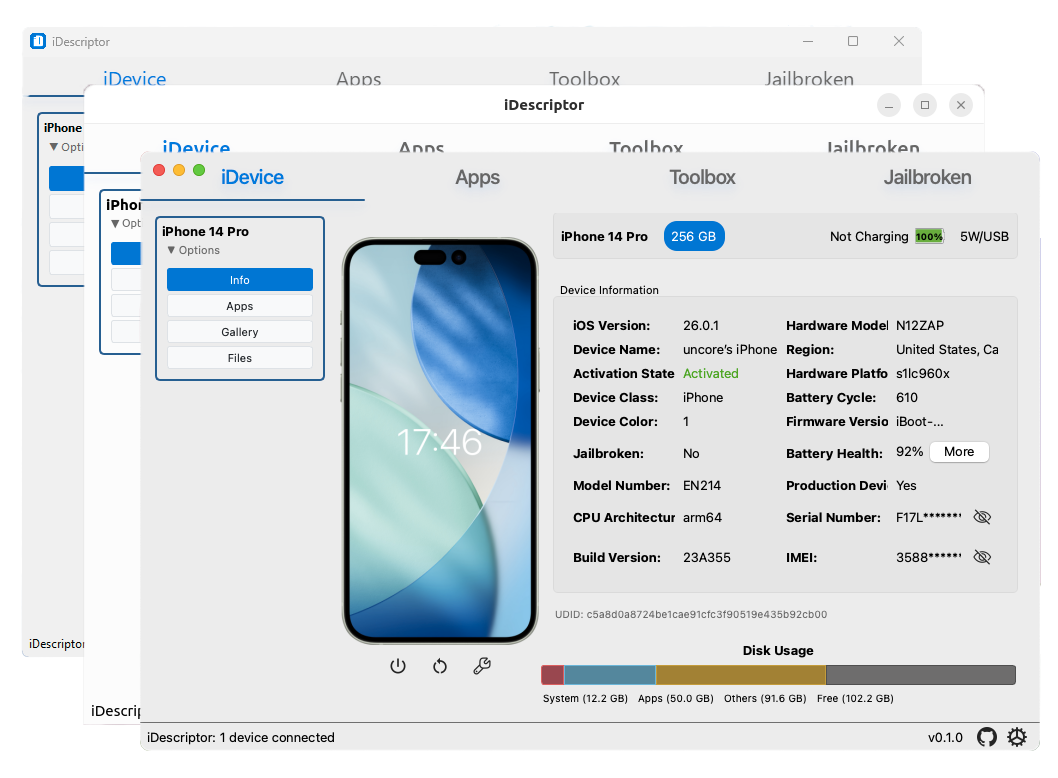 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 ddz/whatsapp-media-decrypt
Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.