
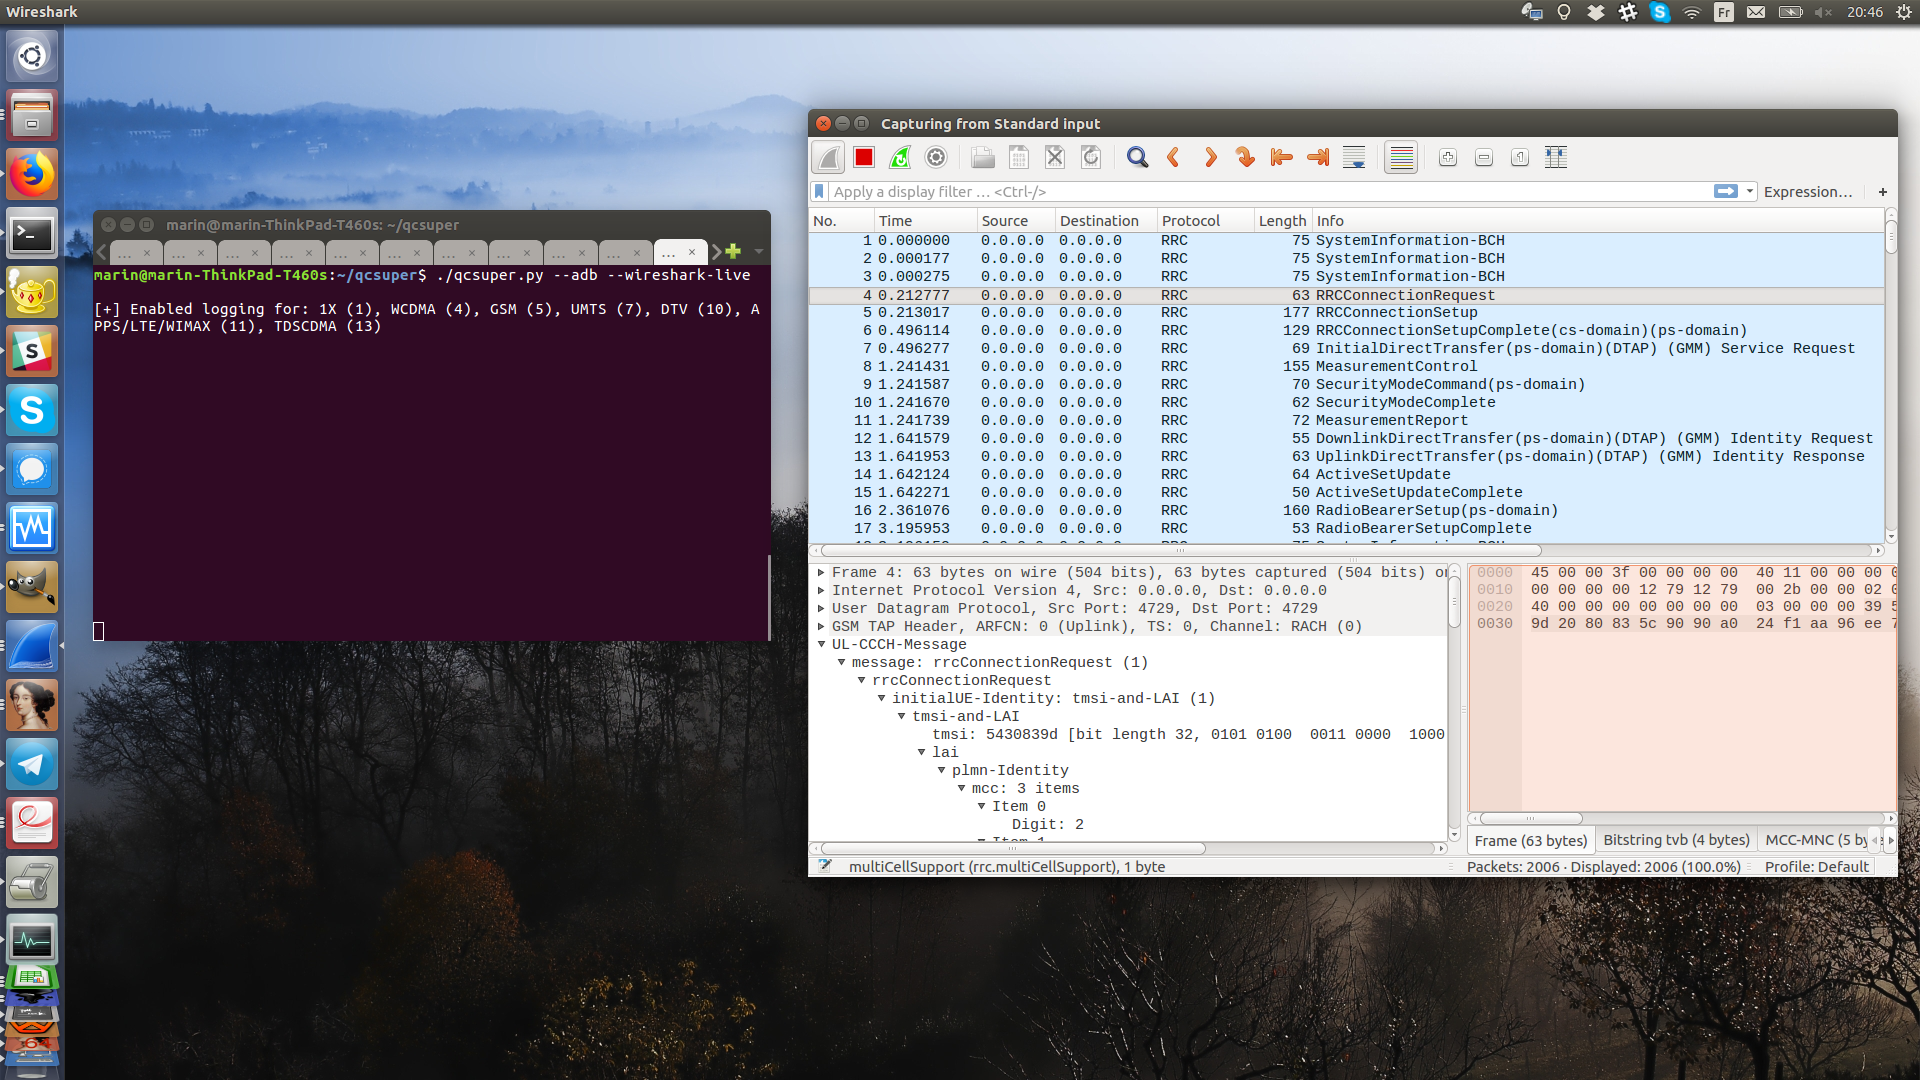
QCSuper
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
p1sec/qcsuperQCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 nowsecure/android-forensics
Open source Android Forensics app and framework
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 cyberhatcoil/acf
Android Connections Forensics
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252

 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.