

iDescriptor
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.1k
idescriptor/idescriptorprivacy-first, open-source and free idevice management tool written in Rust and Qt
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 frida/frida
Main repo for hosting release binaries
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 nowsecure/r2frida
Radare2 and Frida better together.
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
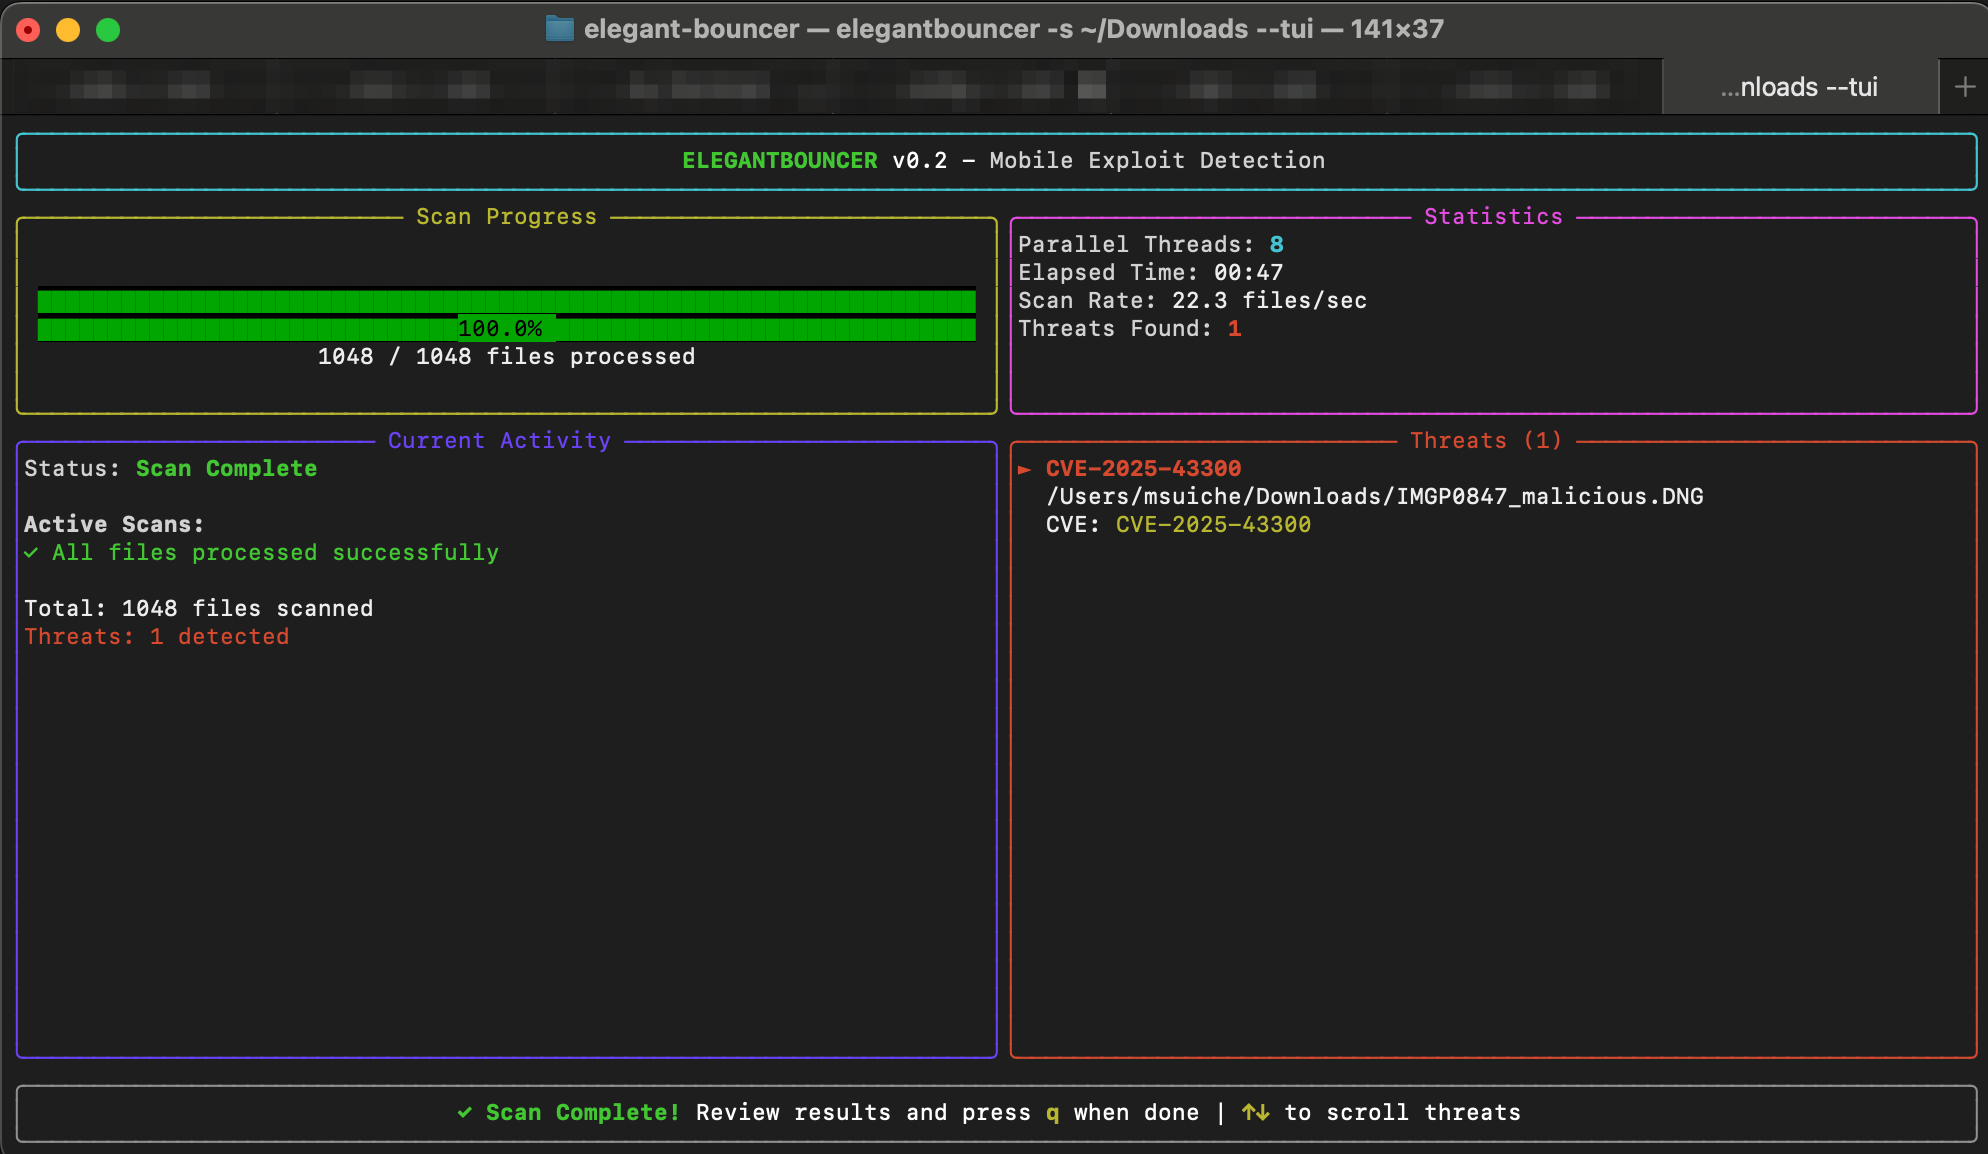 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 androguard/androguard
Reverse engineering and pentesting for Android applications
 andrewrathbun/dfirartifactmuseum
The goal of this repo is to archive artifacts from all versions of various OS's and categorizing them by type. This will help with artifact…