


 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
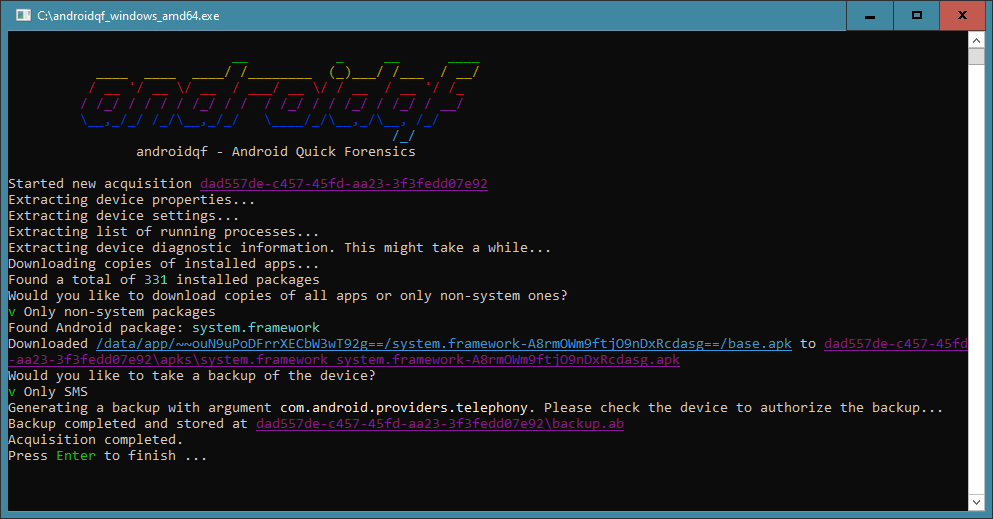 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 frida/frida
Main repo for hosting release binaries
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
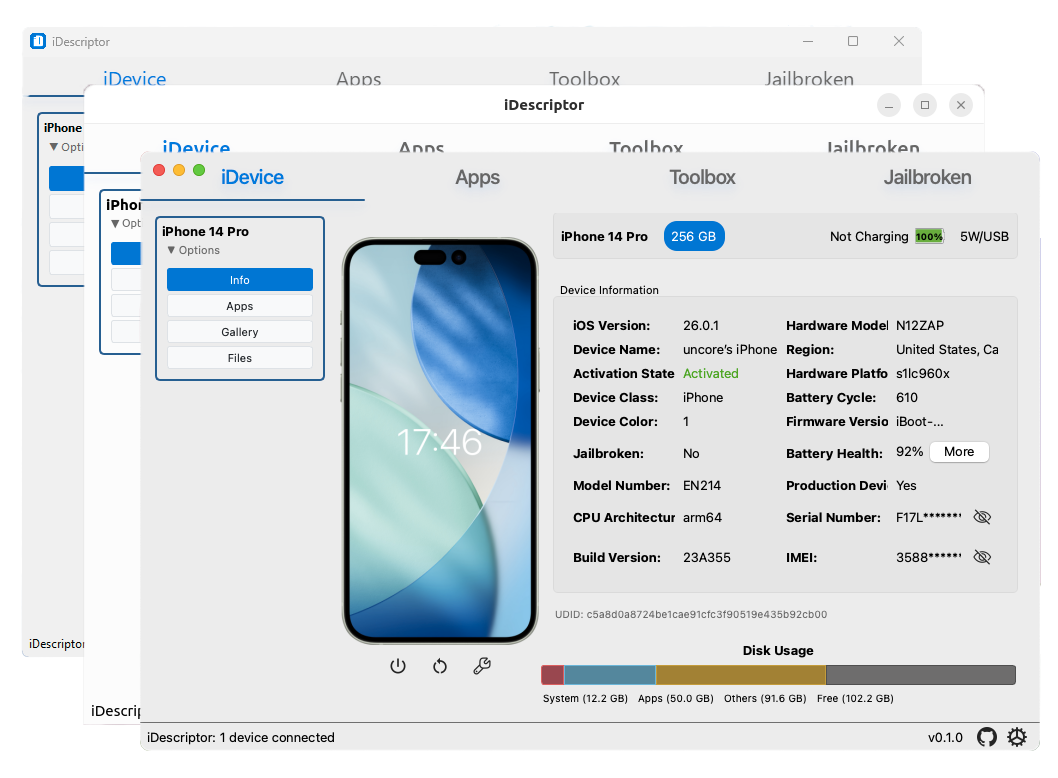 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
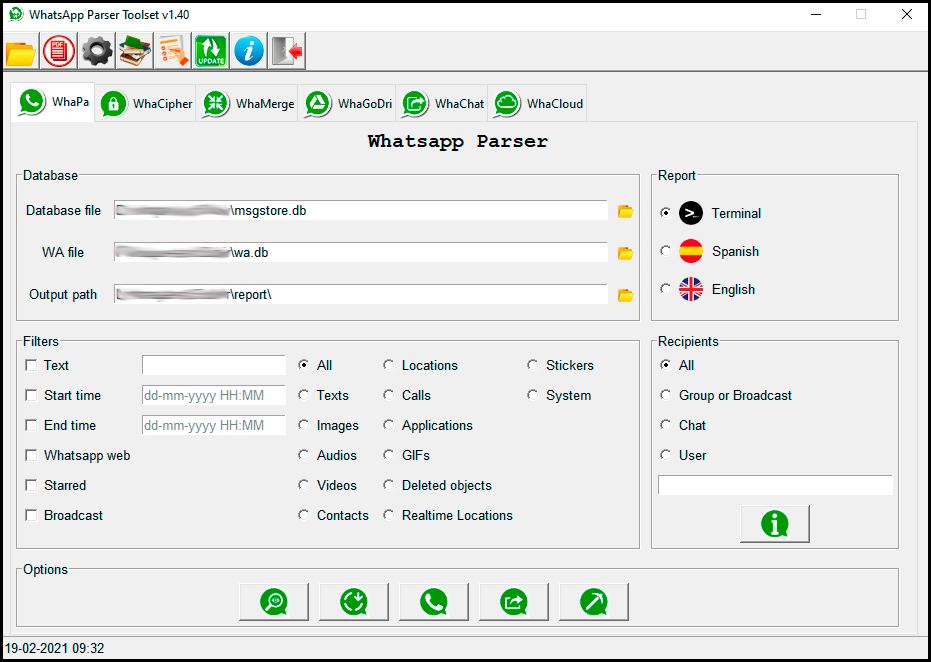 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…