

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.2k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
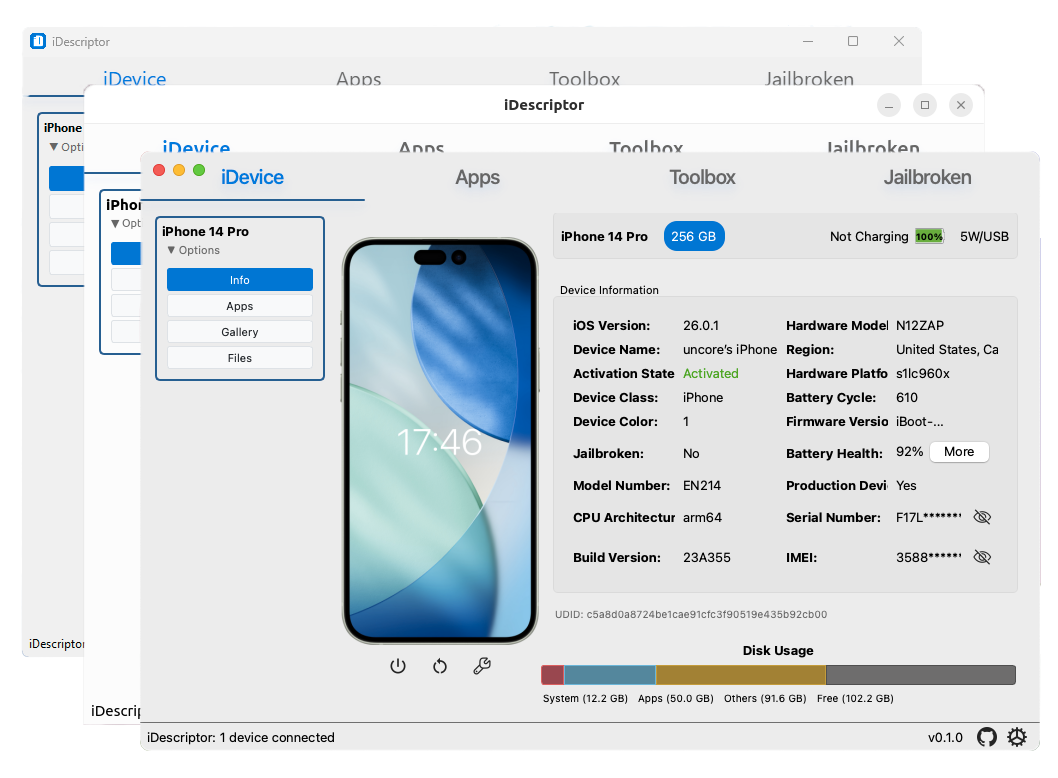 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

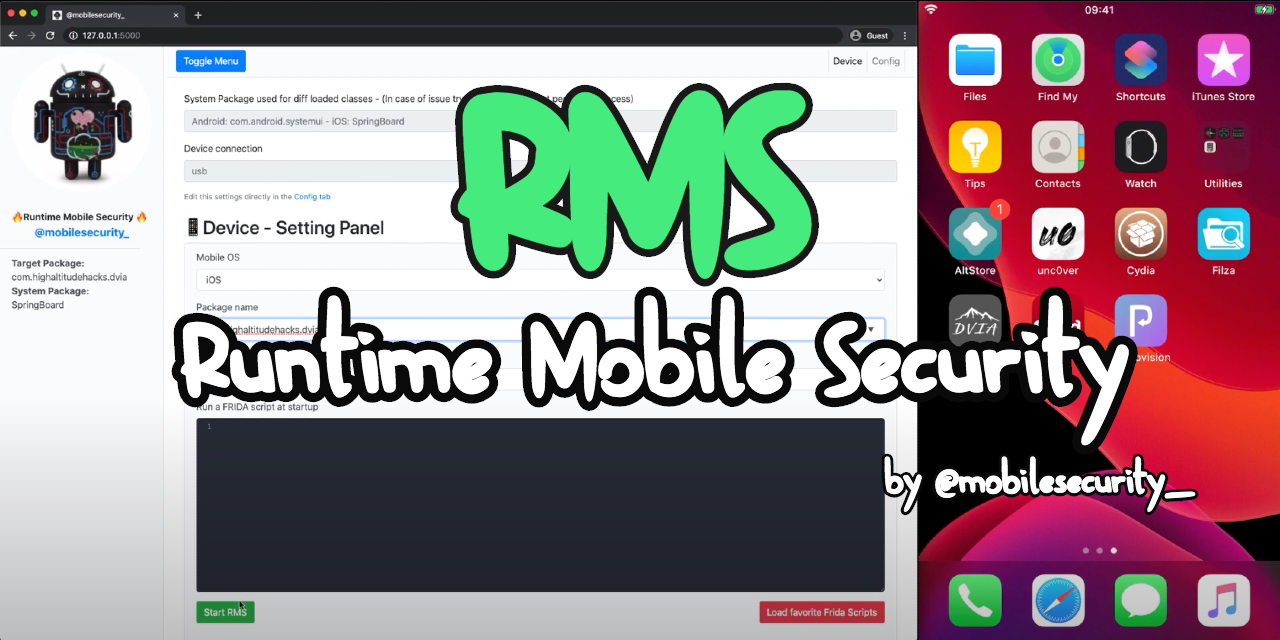 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 quantika14/guasap-whatsapp-foresincs-tool
WhatsApp Forensic Tool
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS