

jshookmcp
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
ai-securitybinary-analysisdebuggers+9
2.1k
vmoranv/jshookmcpA search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 nowsecure/r2frida
Radare2 and Frida better together.
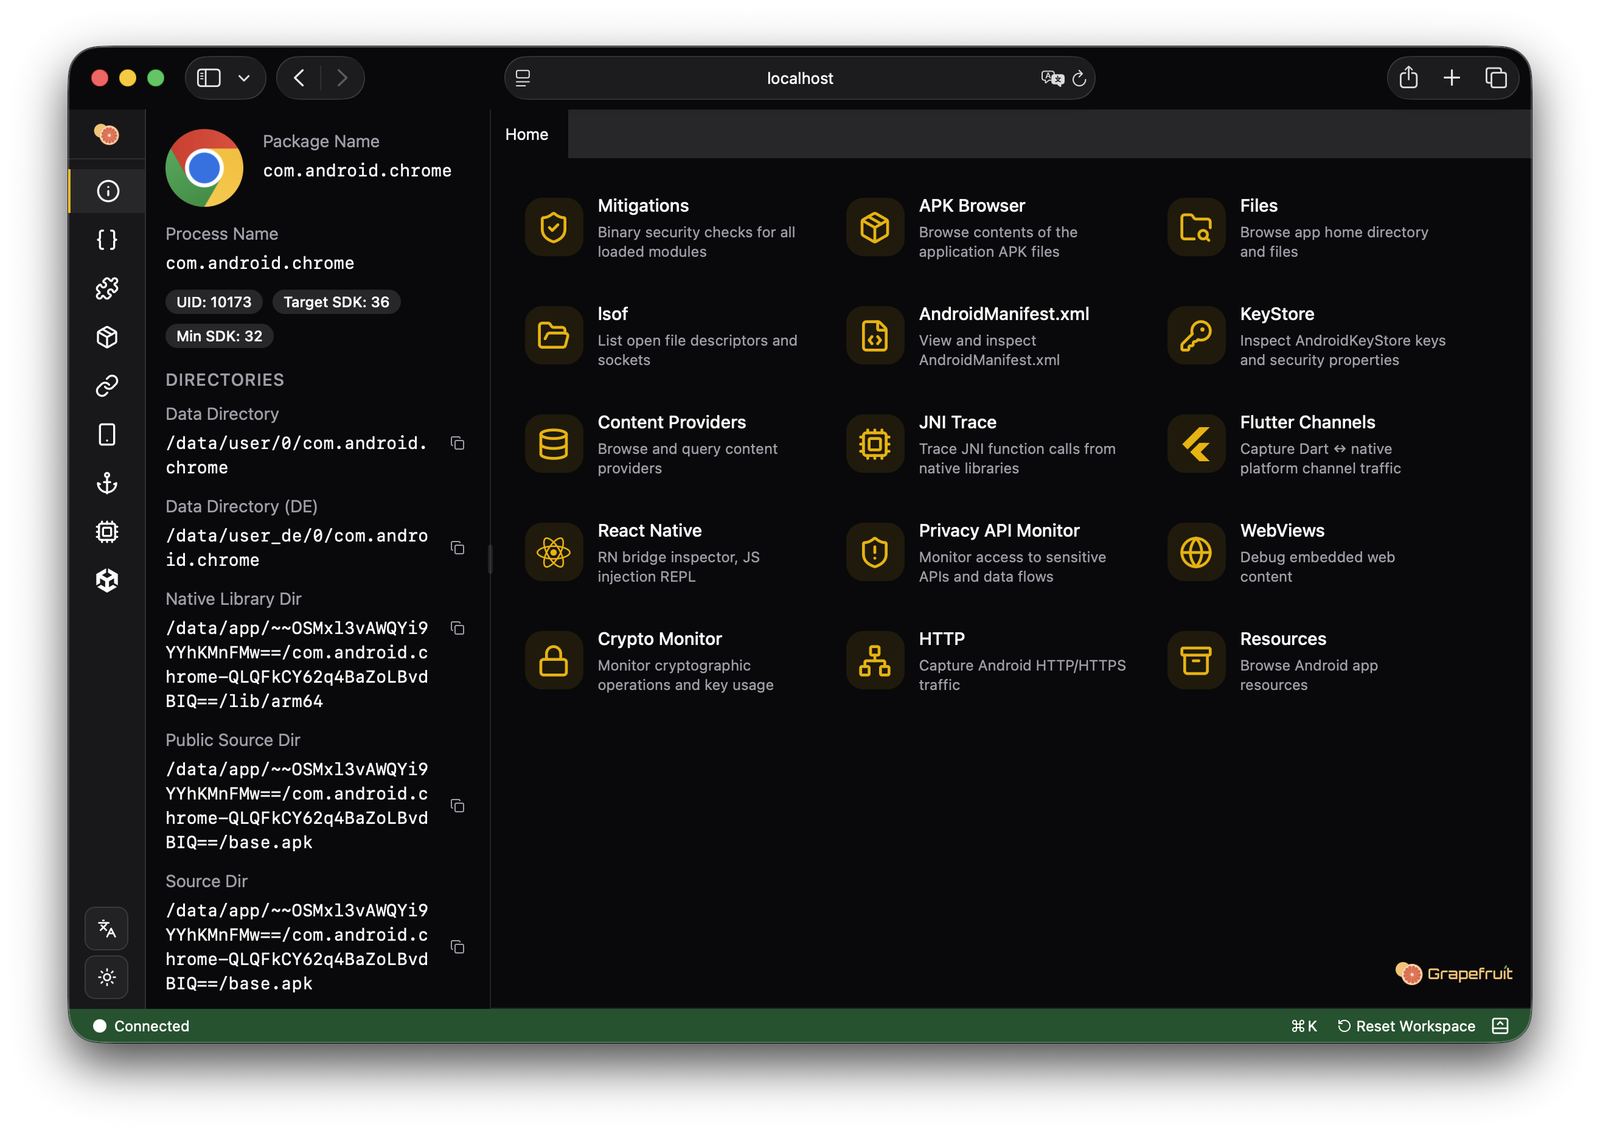 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
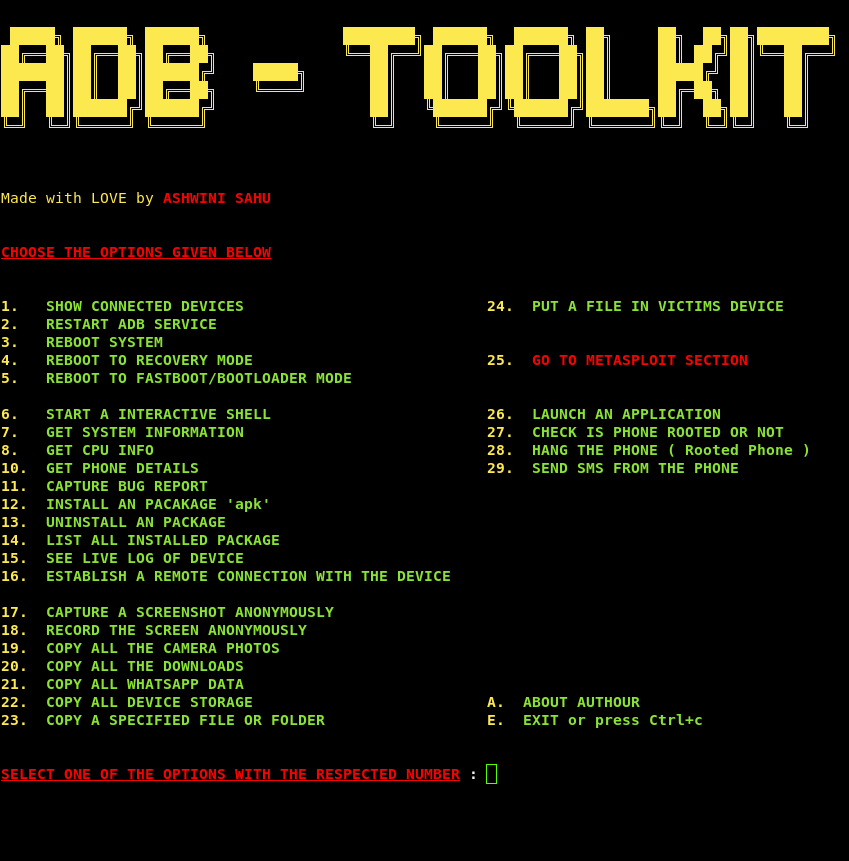 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
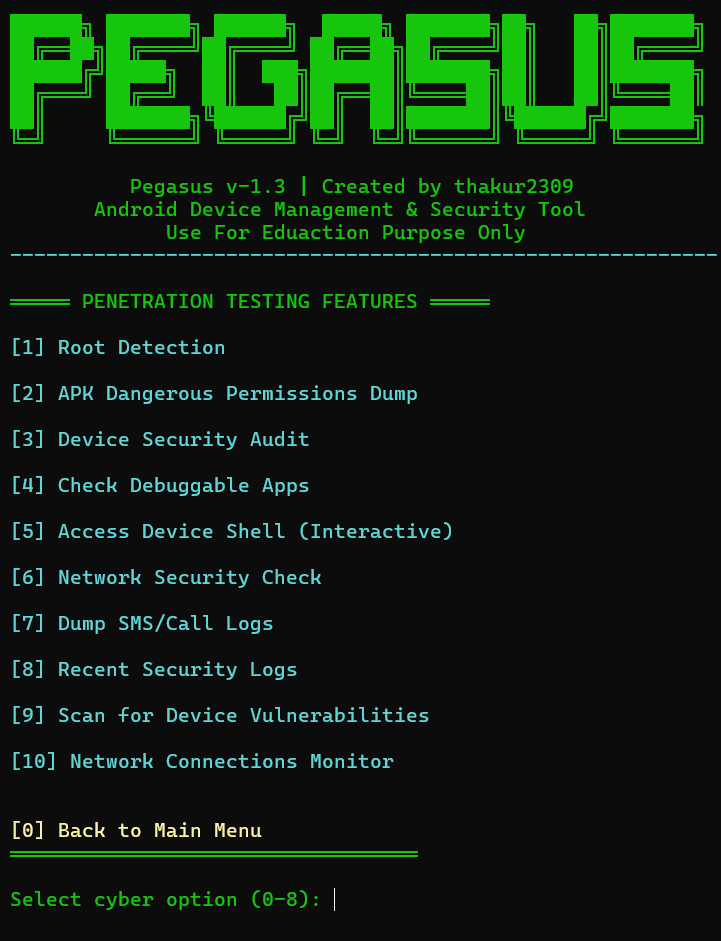 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
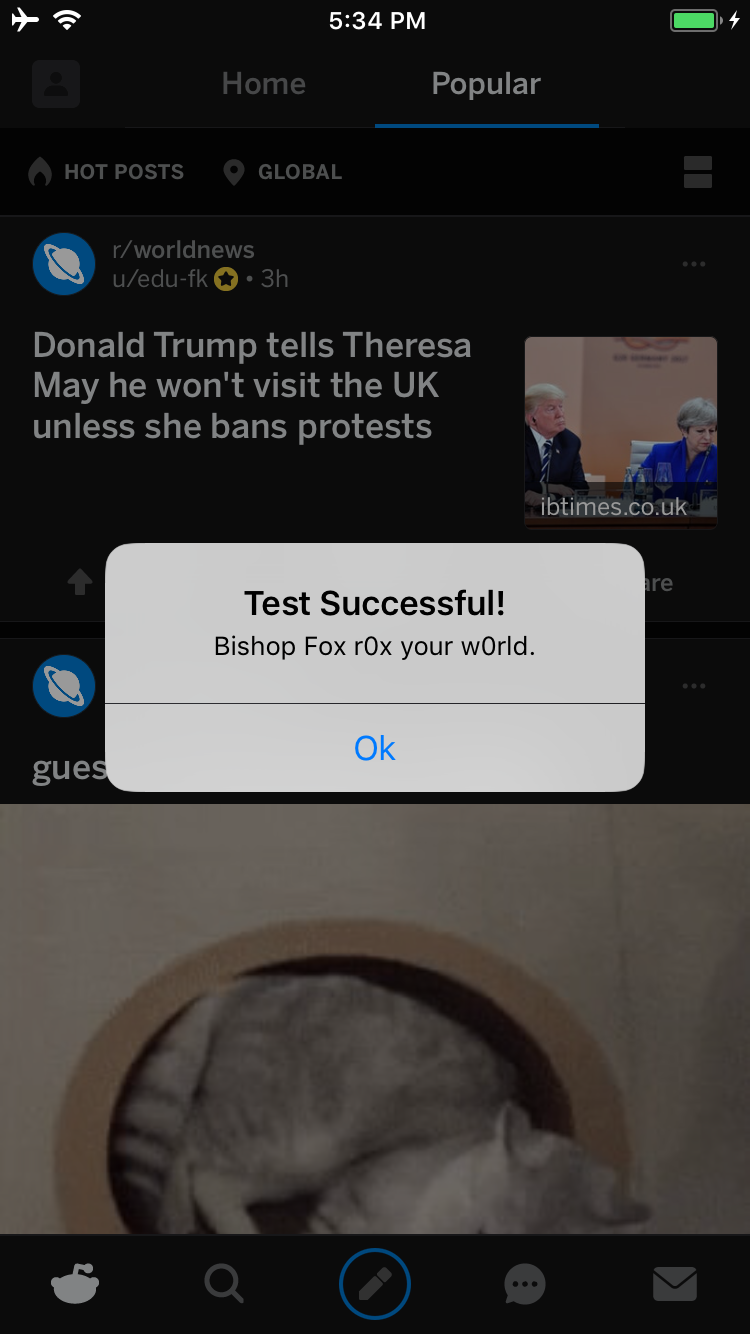 bishopfox/bfinject
Dylib injection for iOS 11.0 - 11.1.2 with LiberiOS and Electra jailbreaks
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 dmayer/idb
idb is a tool to simplify some common tasks for iOS pentesting and research
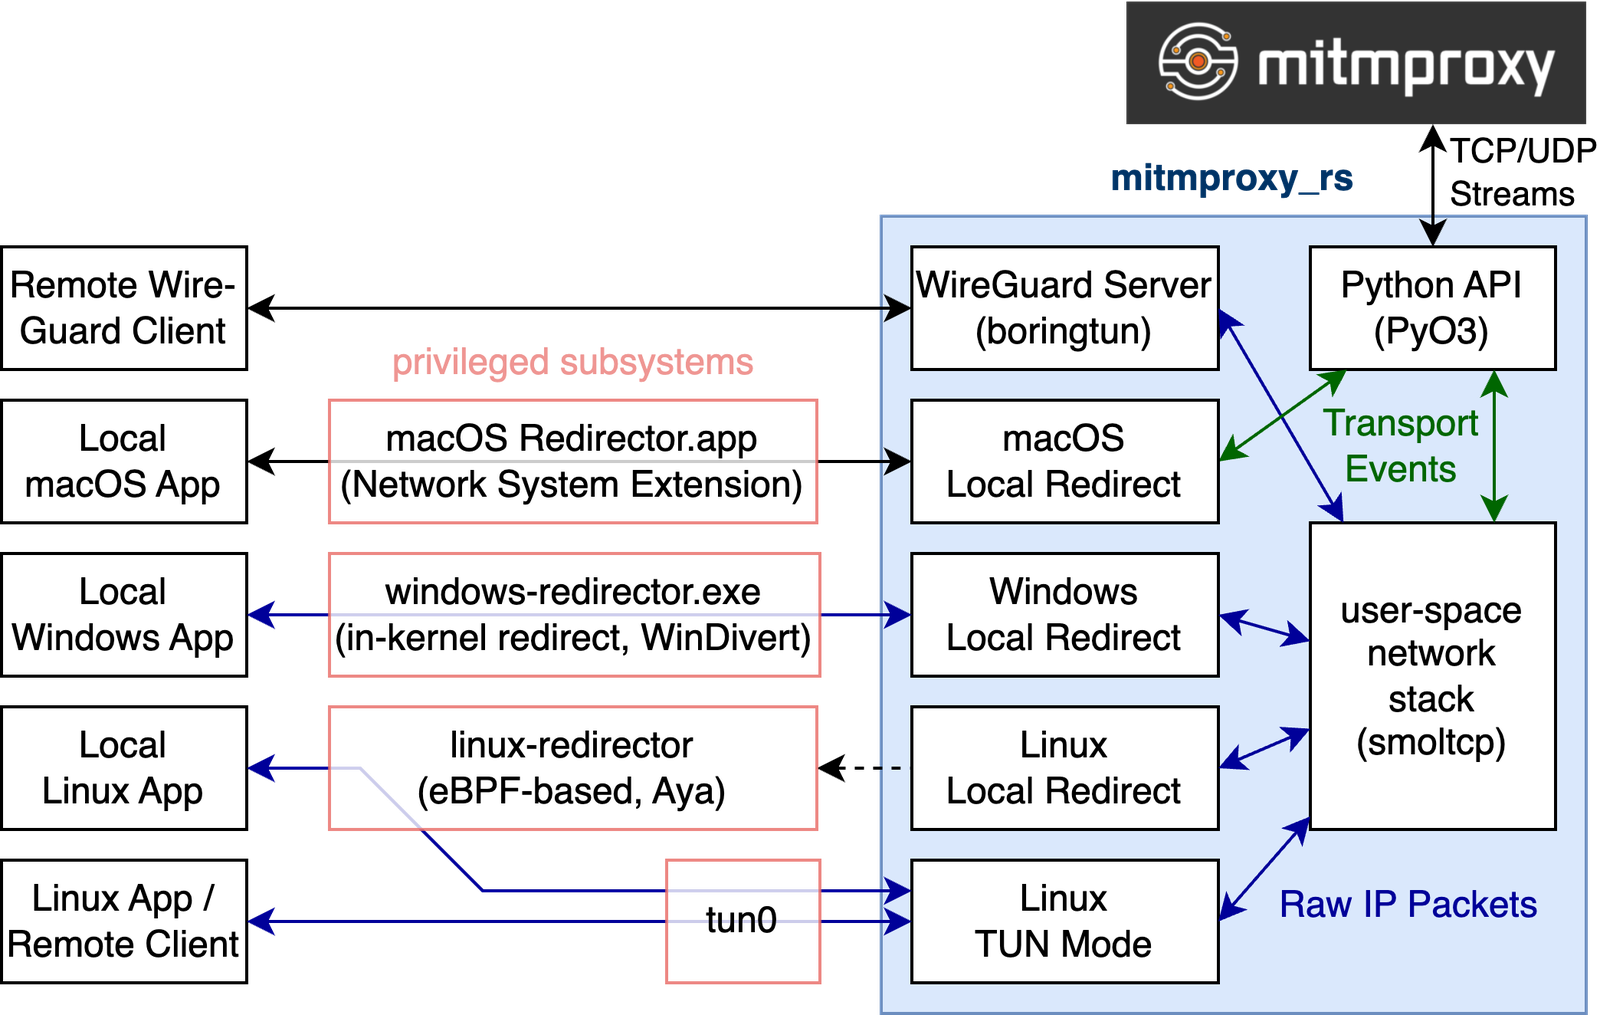 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 chichou/vscode-frida
Unofficial frida extension for VSCode