
Frida-Labs
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
android-securitybinary-analysisctf+6
1.3k7 months ago
dere-ad2001/frida-labsThe repo contains a series of challenges for learning Frida for Android Exploitation.
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 chichou/vscode-frida
Unofficial frida extension for VSCode
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
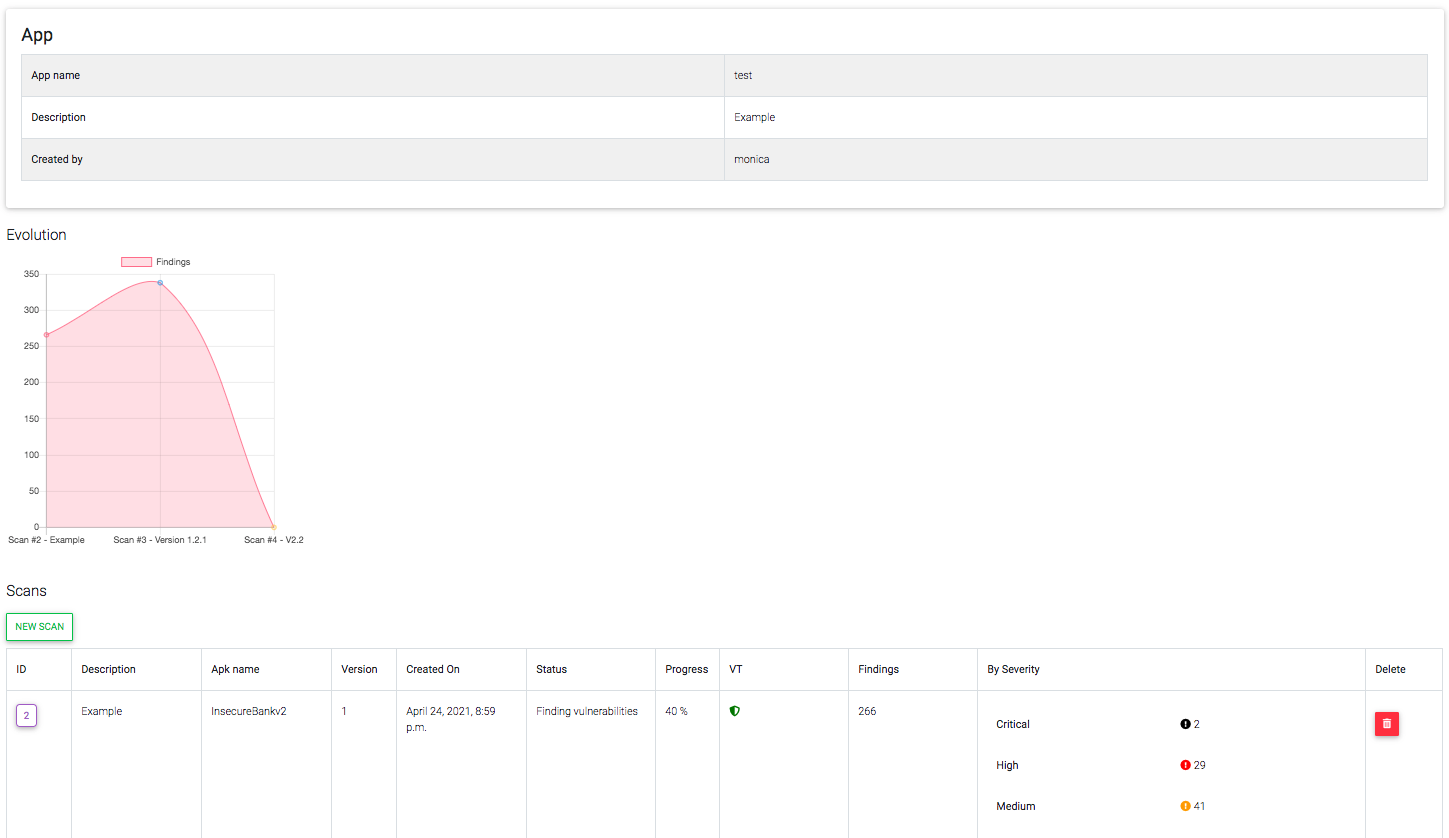 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 mzfr/slicer
A tool to automate the boring process of APK recon
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
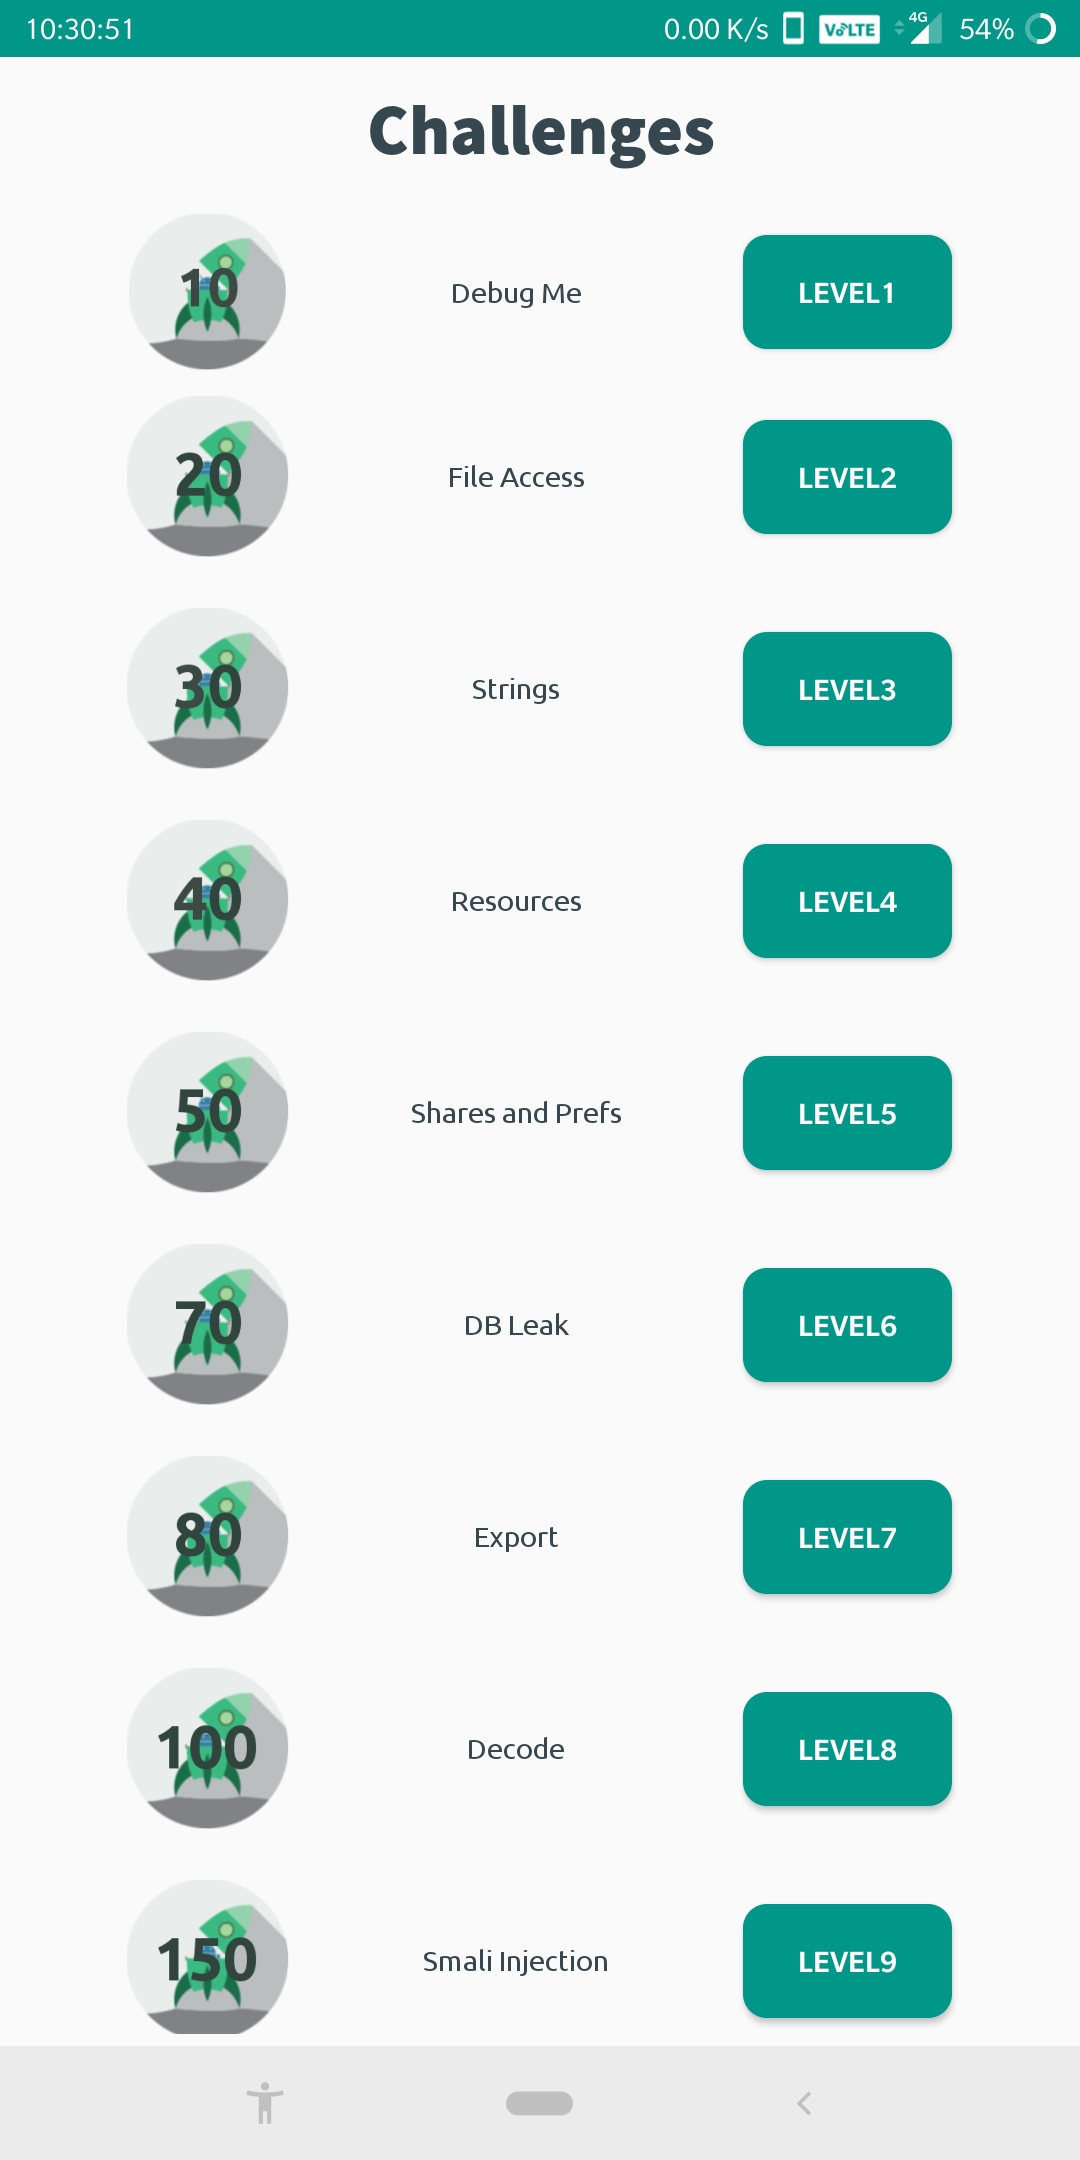 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 logicalhacking/dvhma
Intentionally vulnerable hybrid Android app for security professionals to test tools and techniques, and for developers to learn common hybrid mobile…
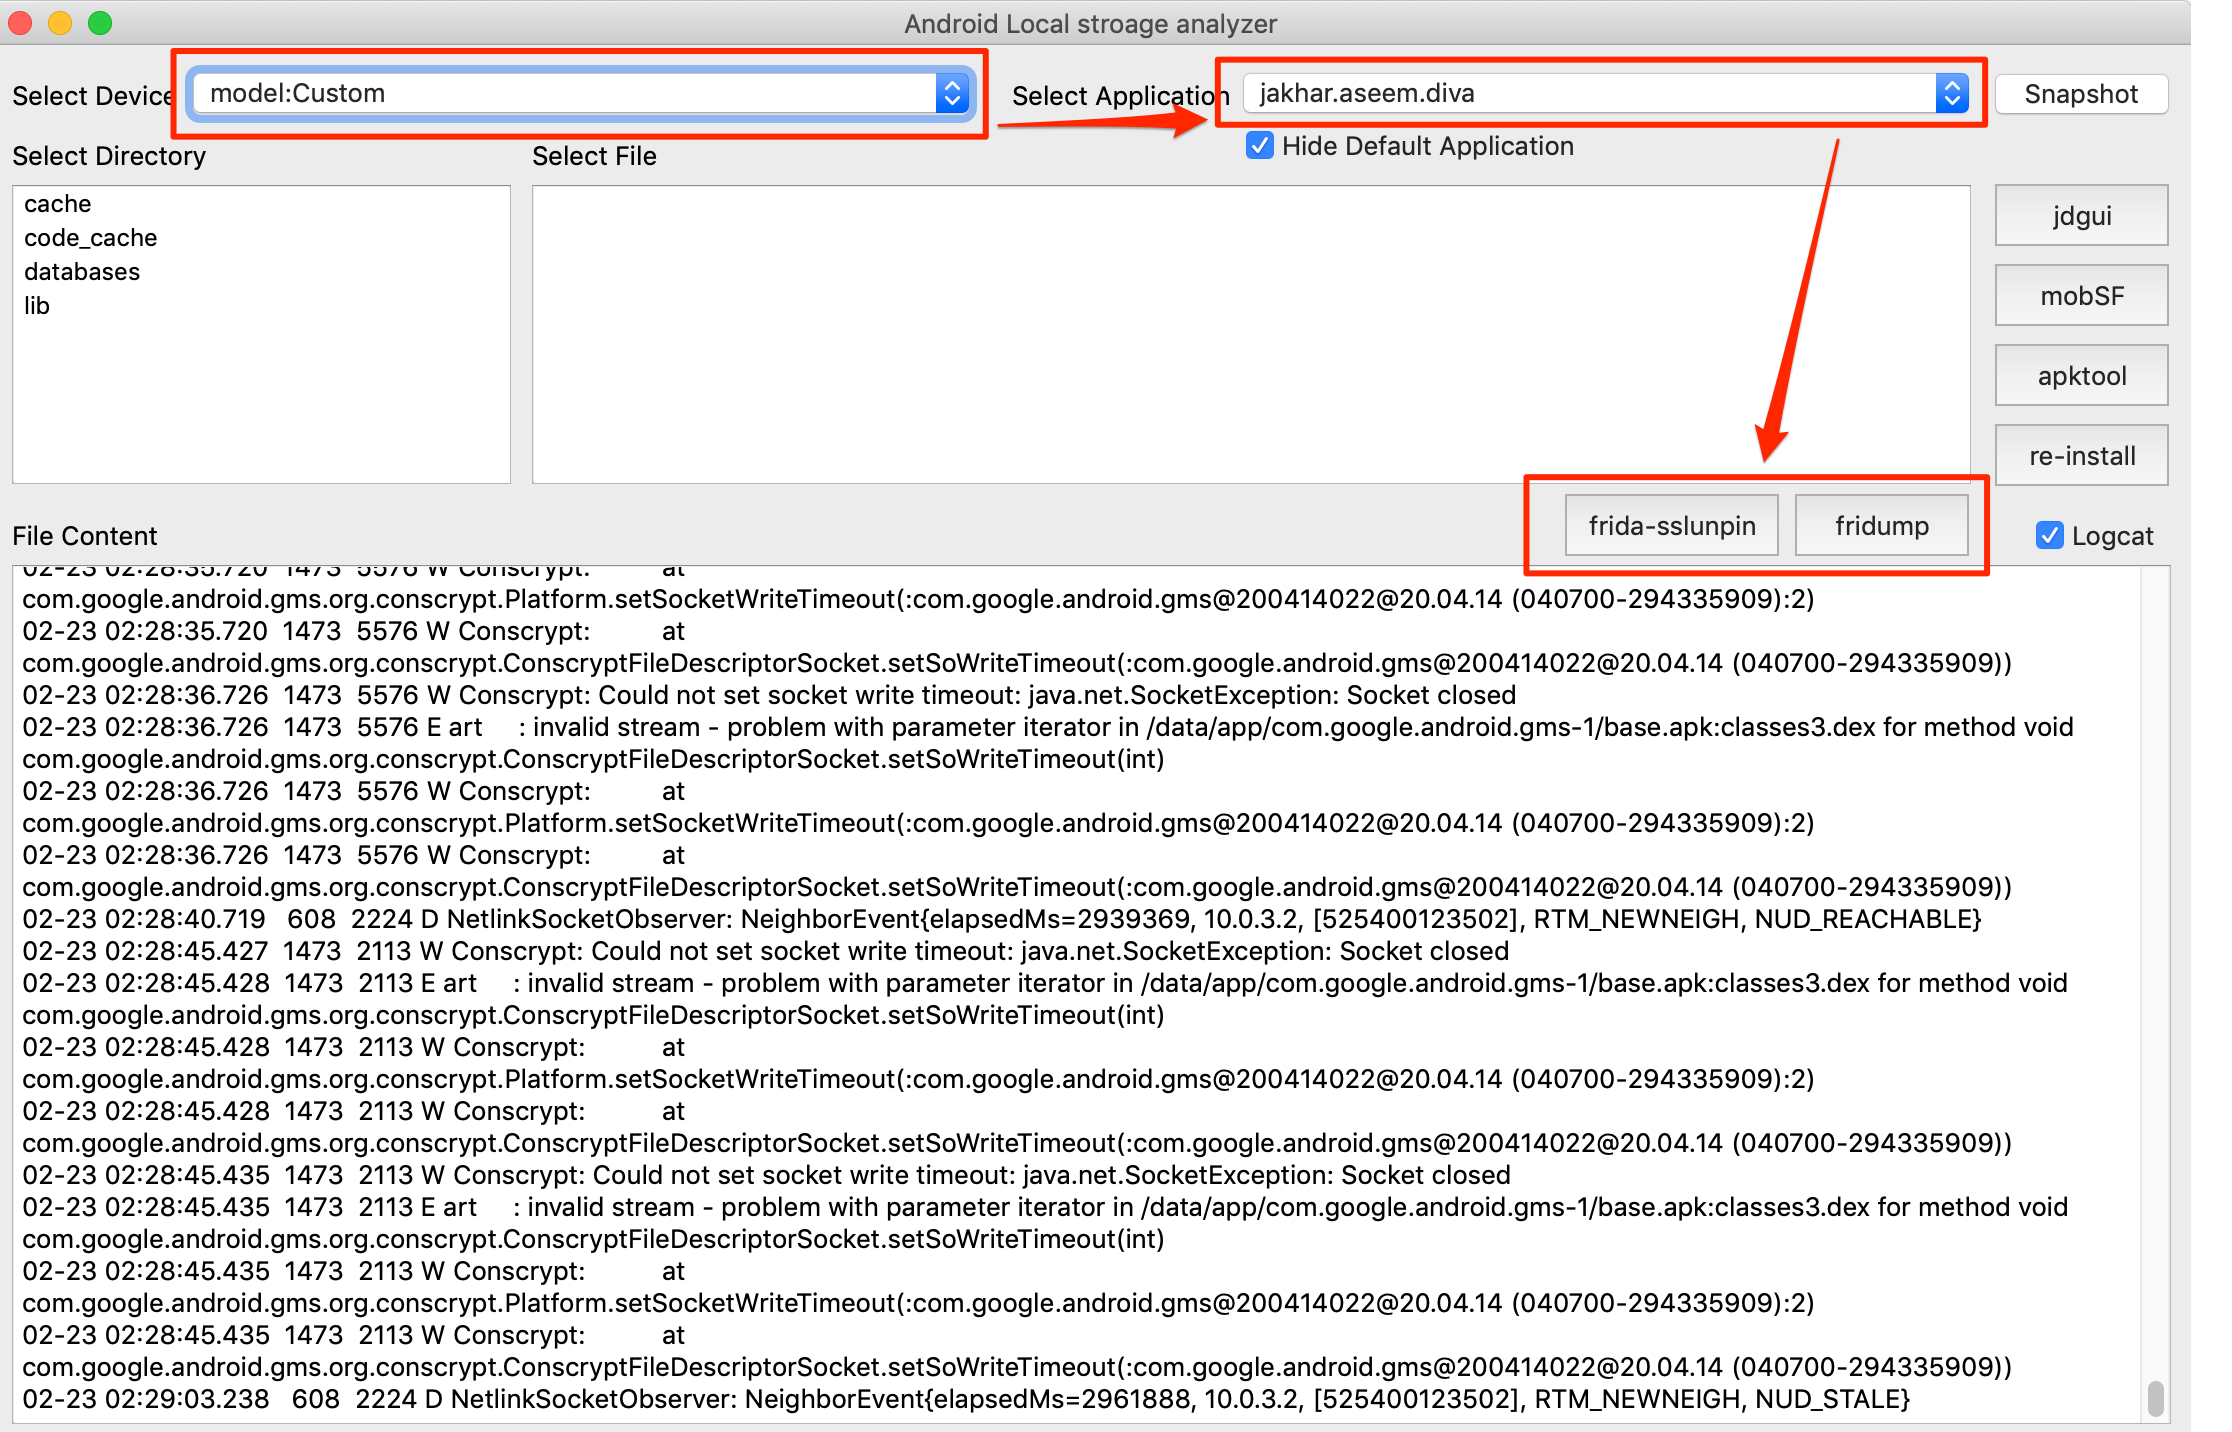 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
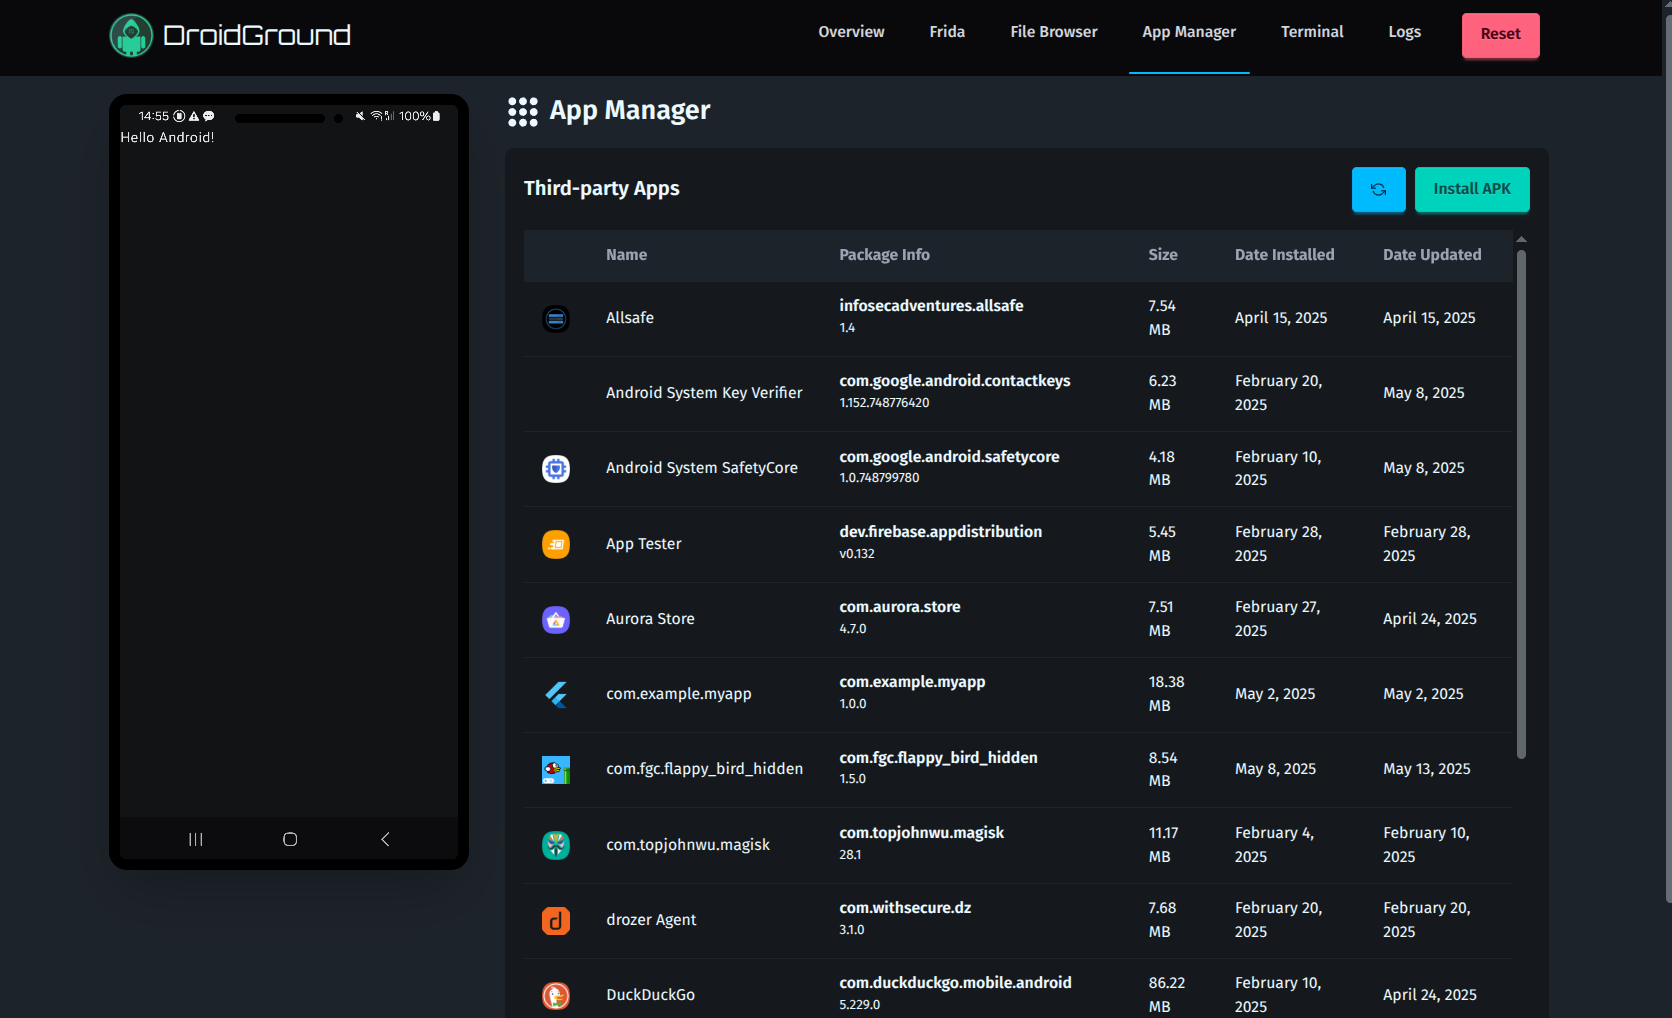 secforce/droidground
A flexible playground for Android CTF challenges.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
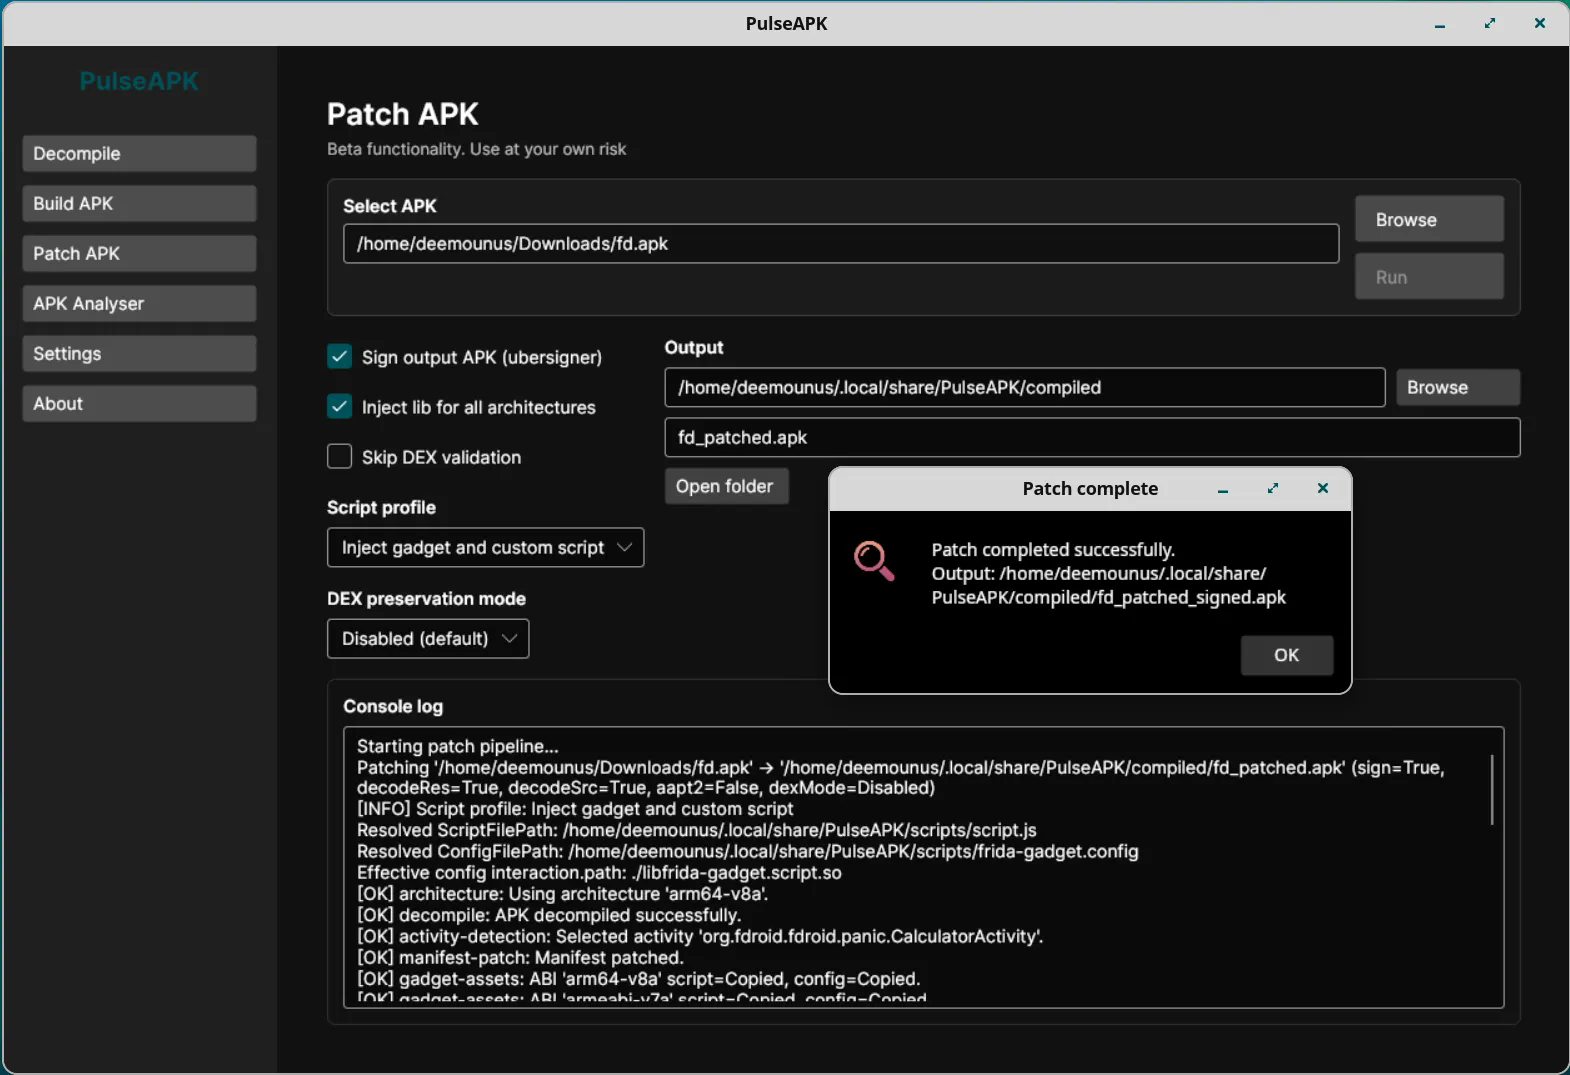 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building