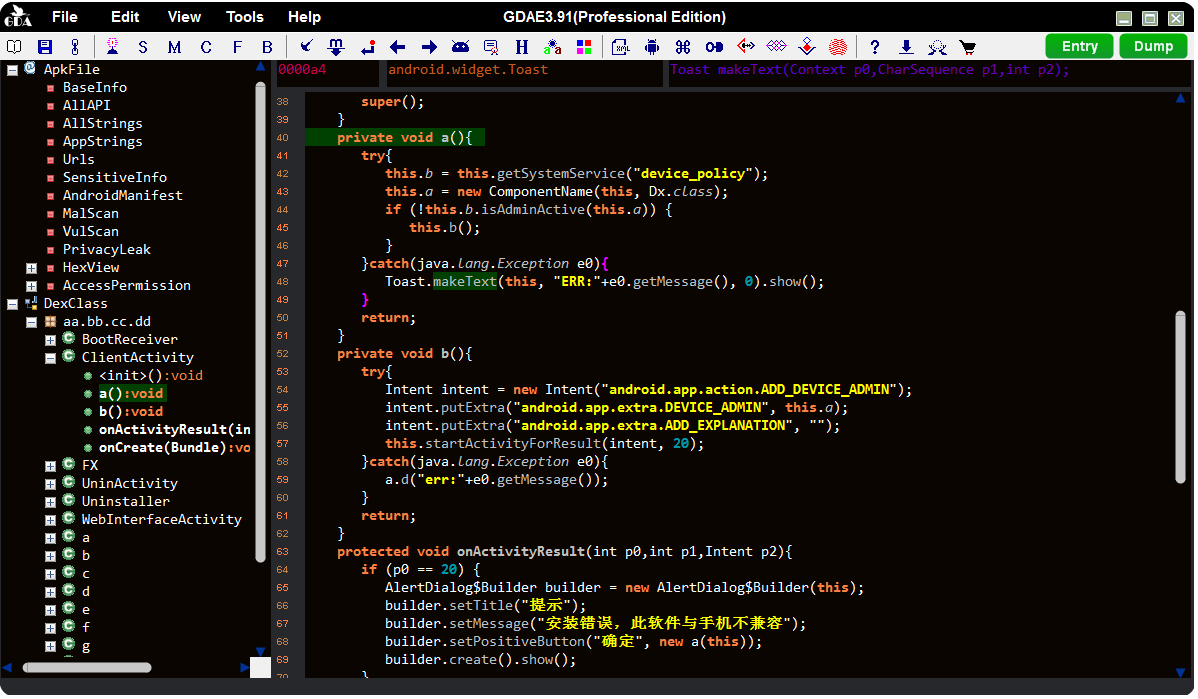
GDA-android-reversing-Tool

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

Walk through CVE-2023-41898: exploit an unvalidated deep link in Home Assistant Android to load arbitrary URLs in a privileged WebView and leak a…

Utility to decrypt App Store apps on jailbroken iOS 11.x

Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…

Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…

Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…

GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes

Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…

Intentionally vulnerable Android banking app for practicing mobile security testing, featuring root detection, anti-debugging, SSL pinning, and…

PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…

Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…

Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…

One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…

Proof-of-concept for CVE-2026-22010 Android intent redirection: demonstrates an exported activity forwarding intents to attacker-controlled internal…