GDA-android-reversing-Tool

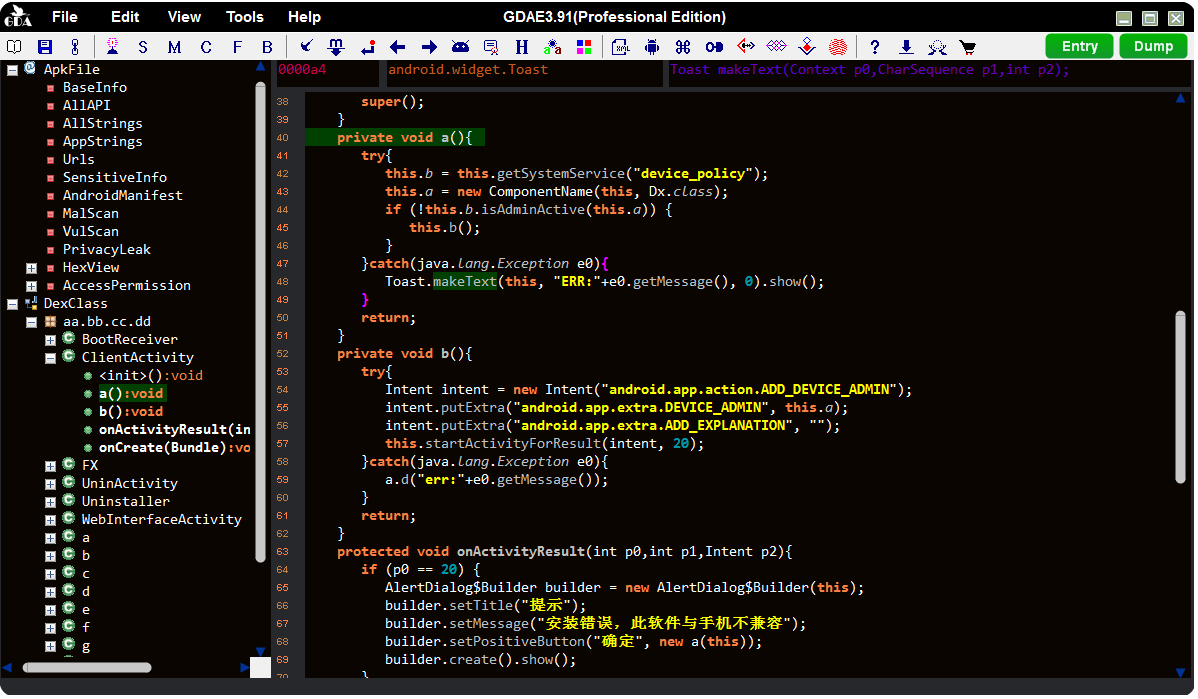
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.

Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…

🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection

Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)

Radare2 and Frida better together.

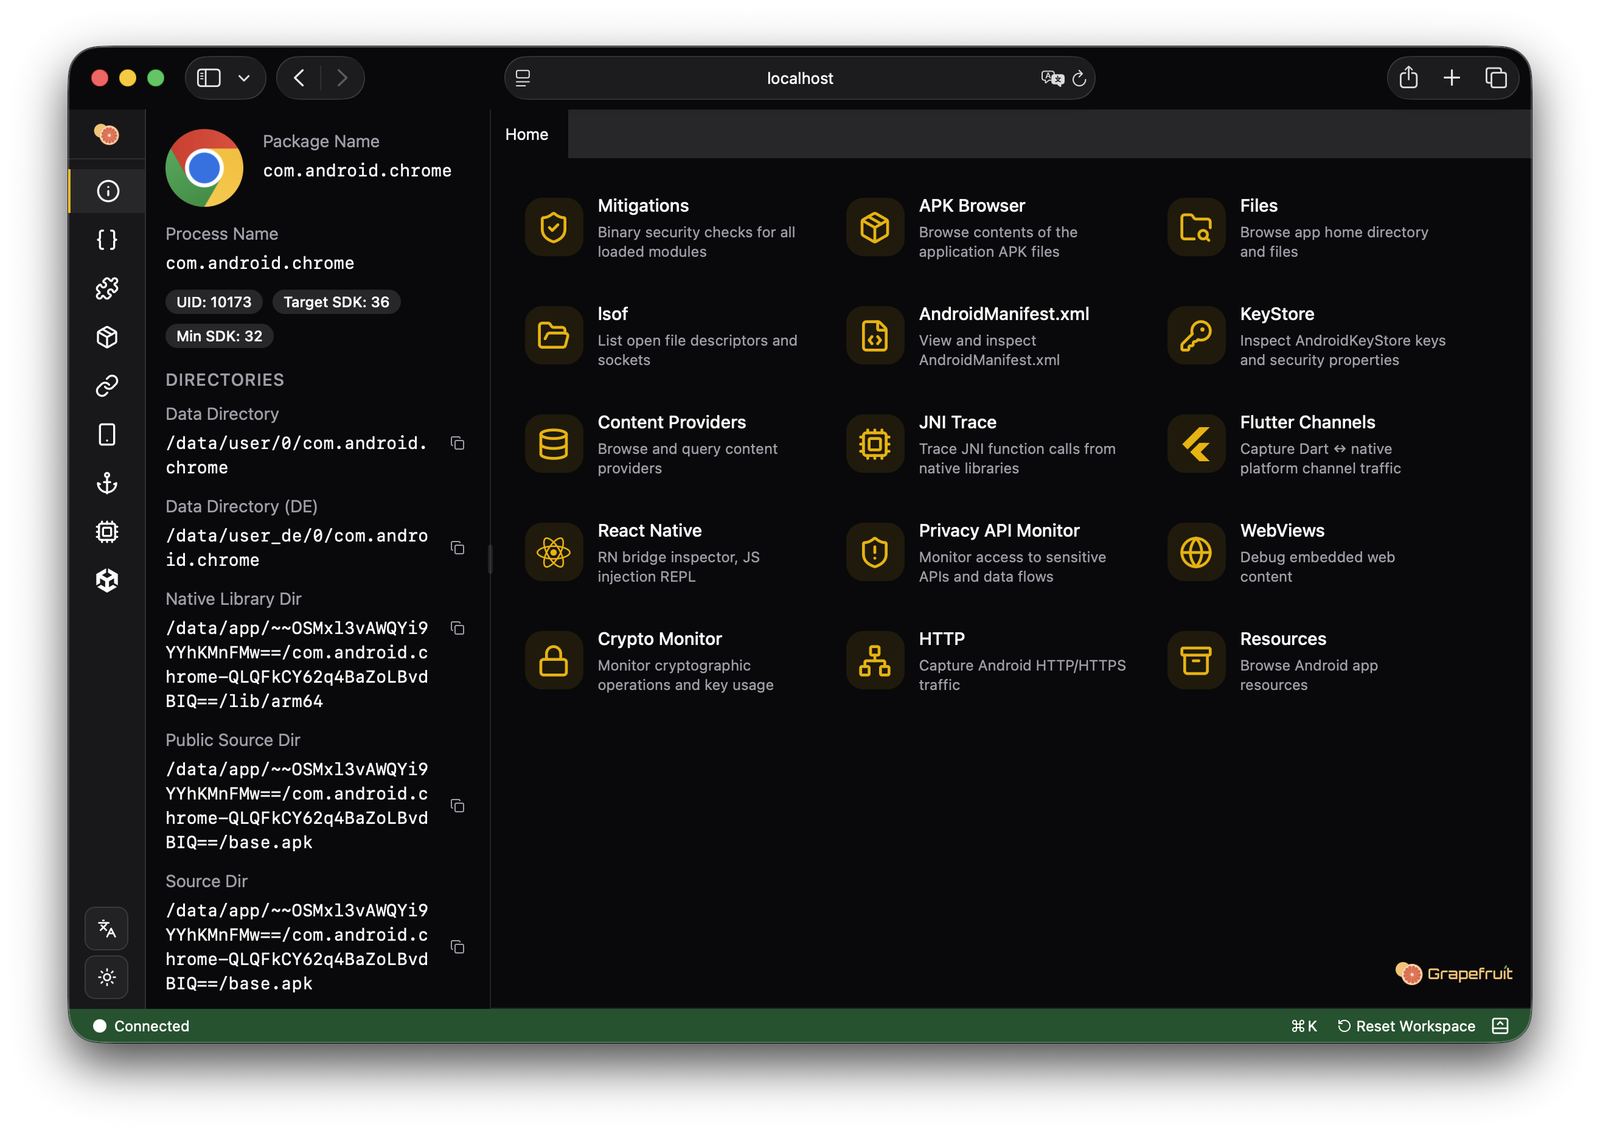
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

The repo contains a series of challenges for learning Frida for Android Exploitation.

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…

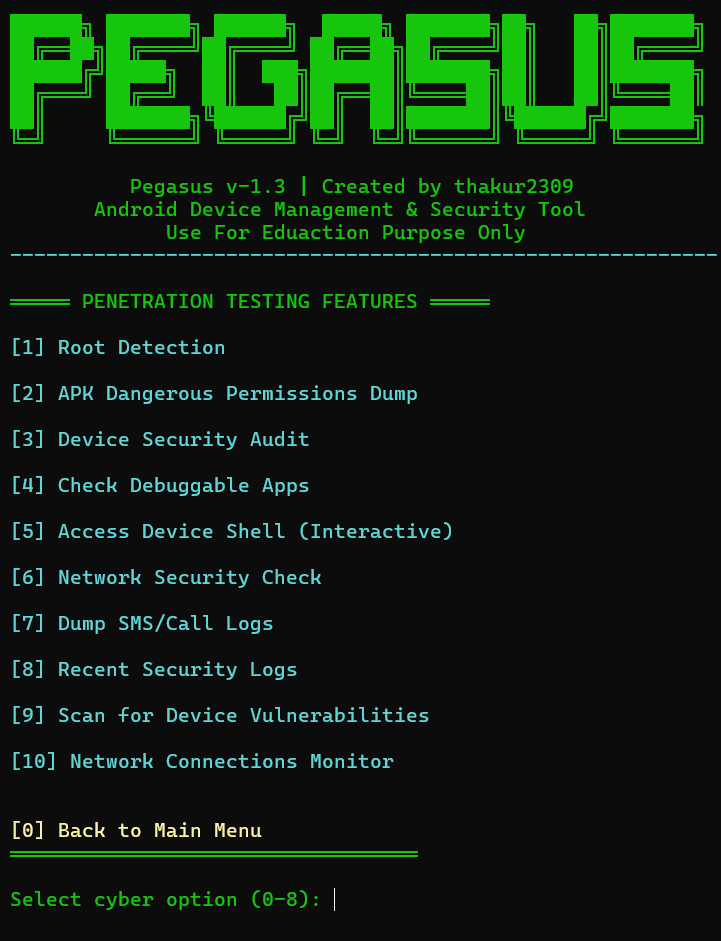
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

dex-vm used to protect the android classes.dex file

Python script to inject existing Android applications with a Meterpreter payload.