
binder-trace
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
android-securitybinary-analysisdynamic-analysis-sandboxing+3
770
foundryzero/binder-traceBinder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 mpast/mobileaudit
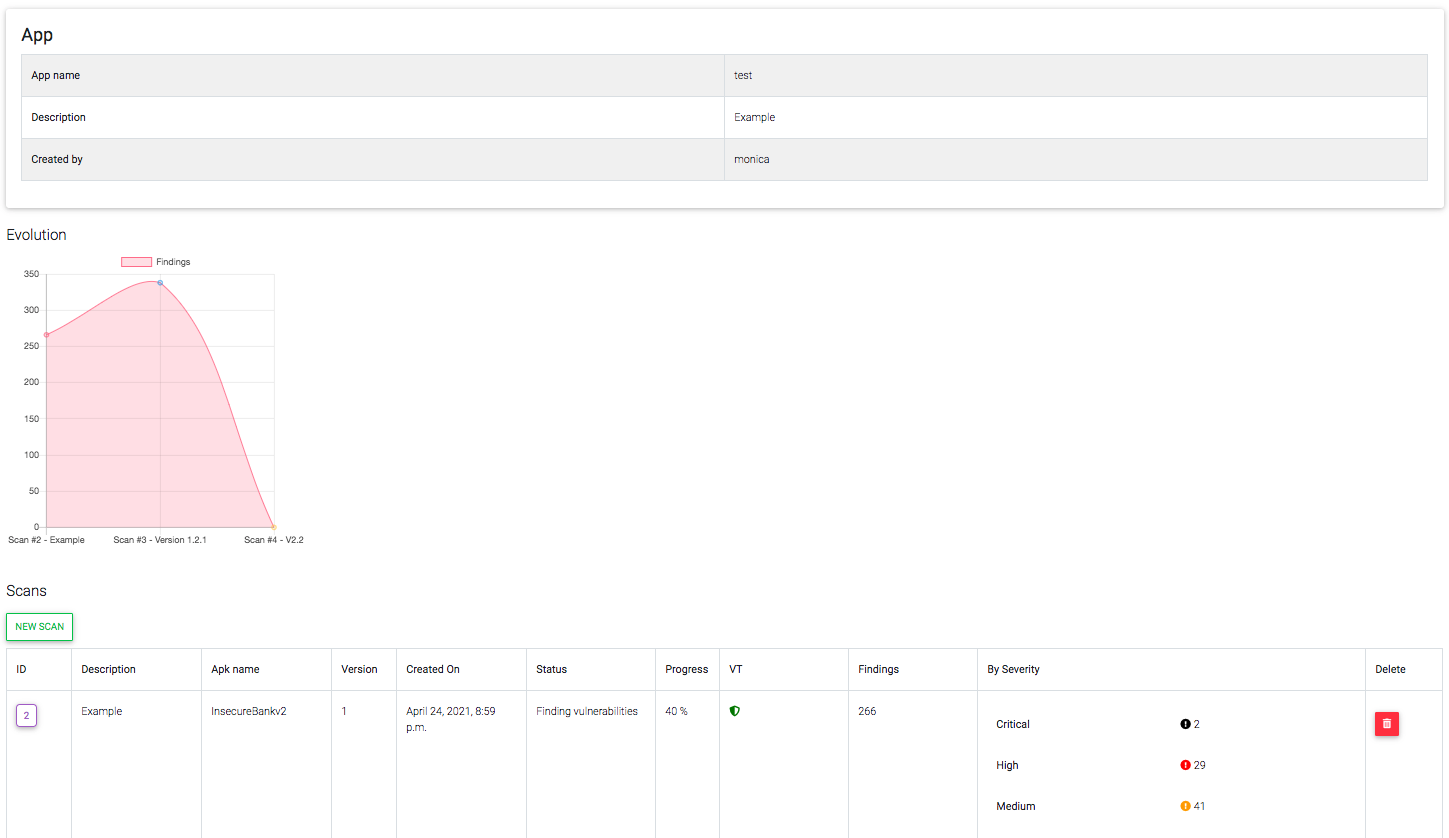
Django application that performs SAST and Malware Analysis for Android APKs
 flankerhqd/jebmcp
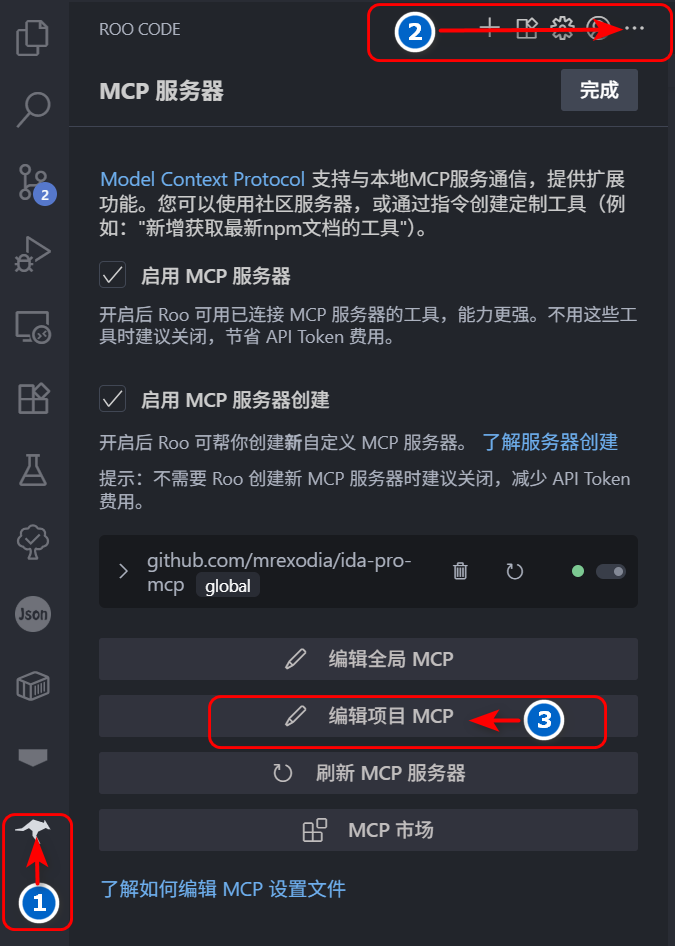
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 logicalhacking/dvhma
Intentionally vulnerable hybrid Android app for security professionals to test tools and techniques, and for developers to learn common hybrid mobile…
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 secforce/droidground
A flexible playground for Android CTF challenges.
 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…
 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
 nccgroup/assethook
LD_PRELOAD magic for Android's AssetManager
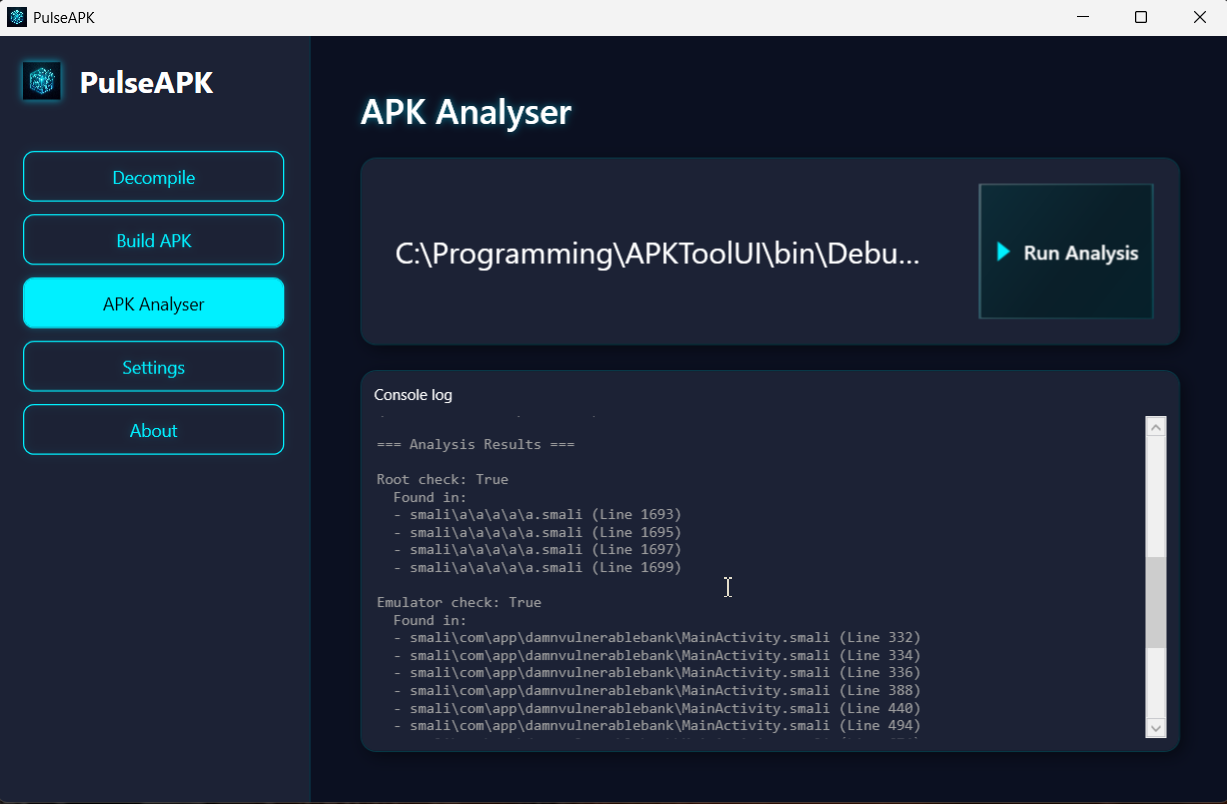 deemoun/pulseapk
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…
 canyie/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…