GDA-android-reversing-Tool

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…

Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.

MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.

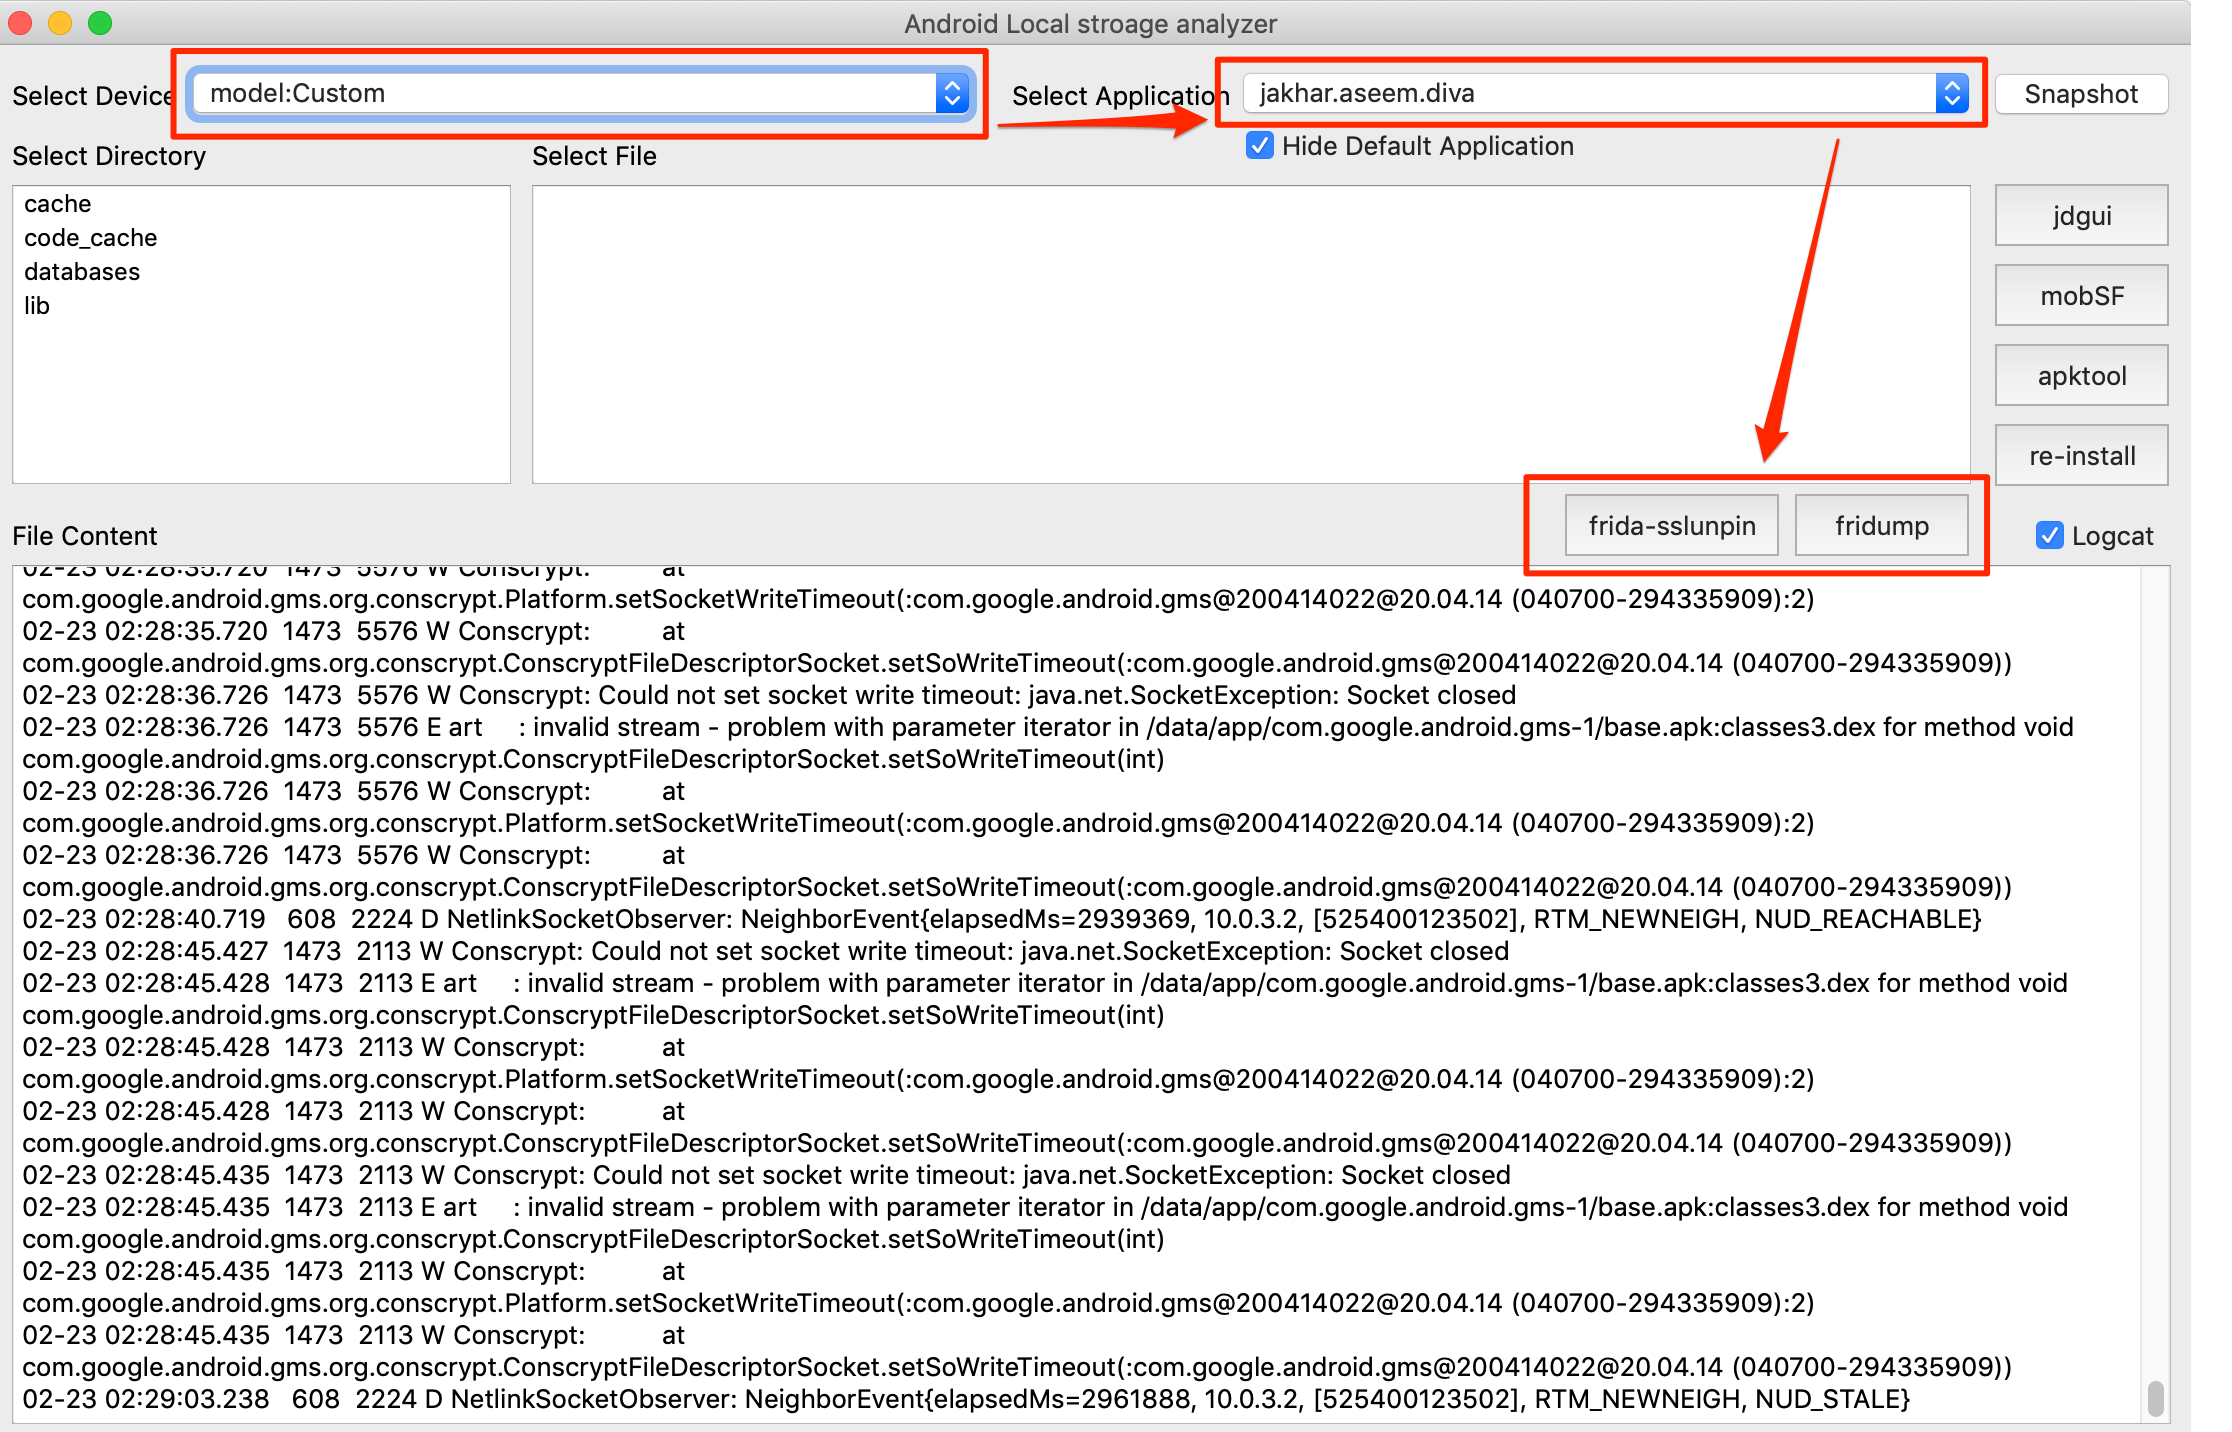
The tool is used to analyze the content of the android application in local storage.

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

Static analysis of APKs with regular expressions

An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs

Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…