
grapefruit
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k
chichou/grapefruitOpen-source mobile security testing suite for iOS and Android. Previously Passionfruit
 chichou/vscode-frida
Unofficial frida extension for VSCode
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
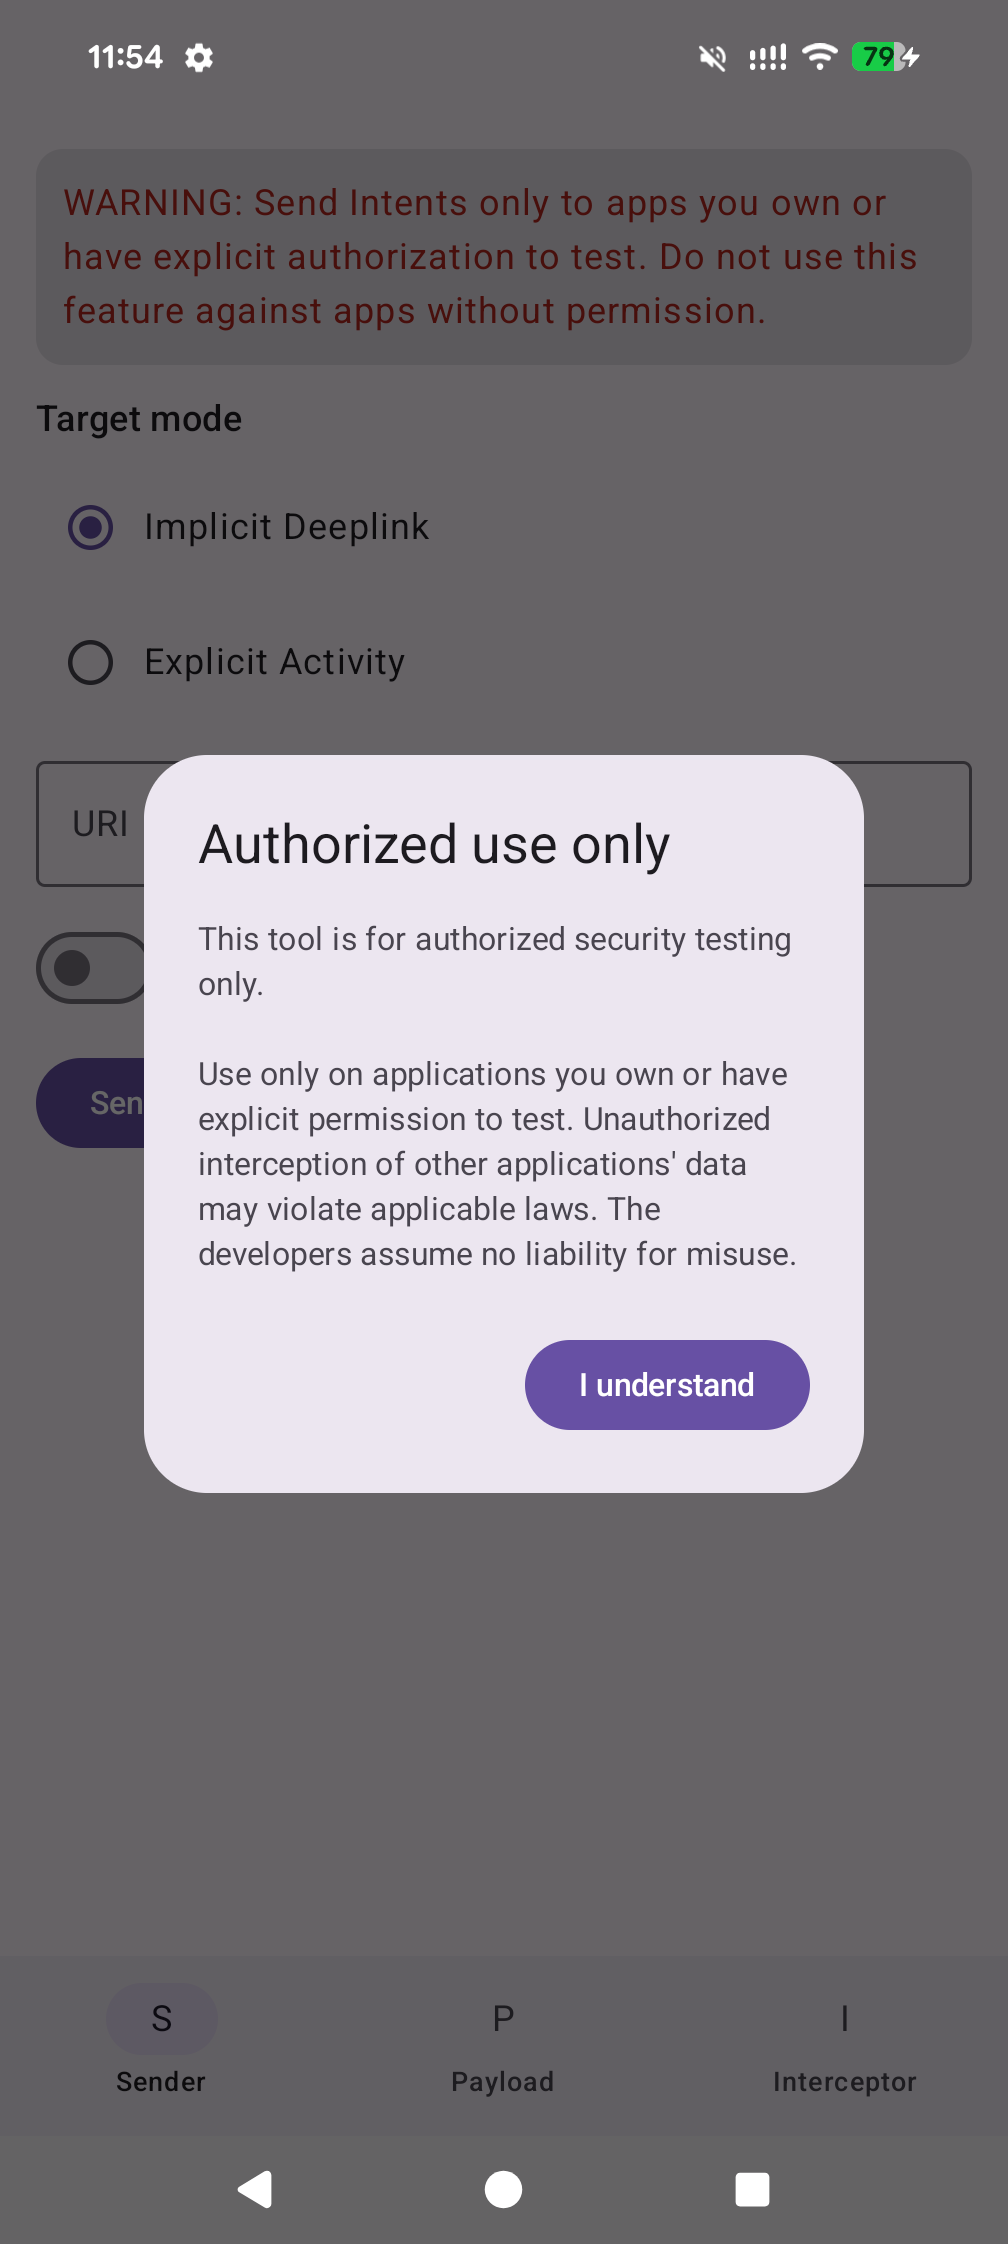 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 nyamisty/ssl-kill-switch3
Next Generation SSLKillSwitch with much more support!
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
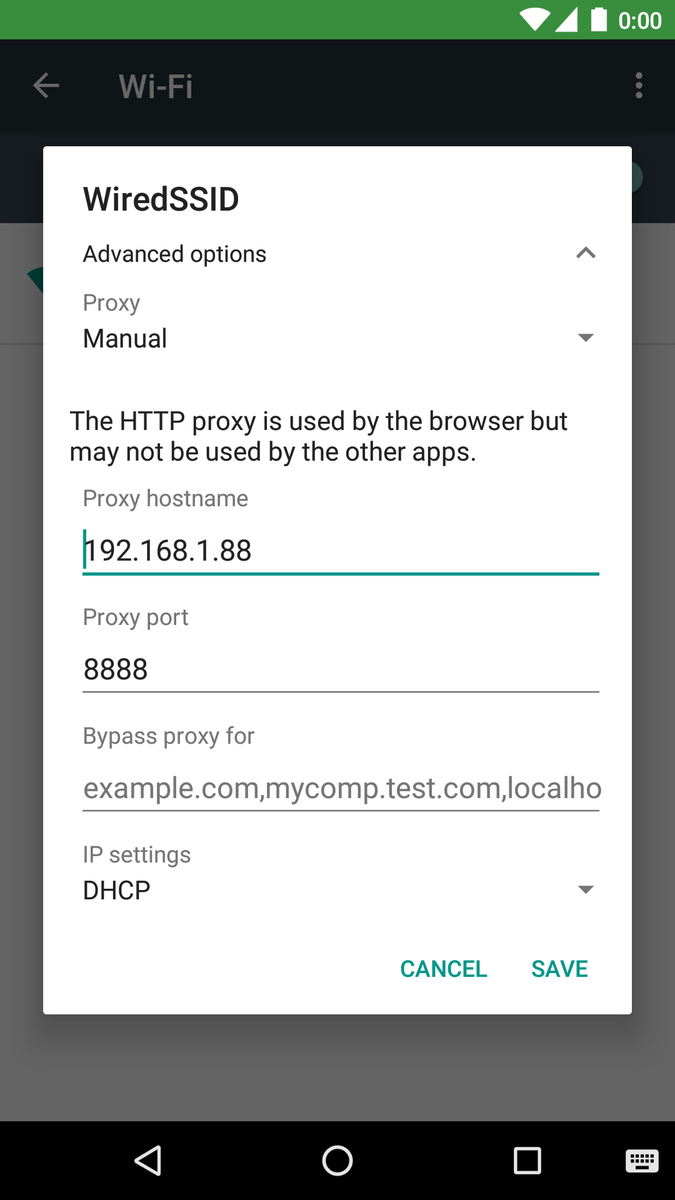 thyrlian/charles-proxy-mobile-guide
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
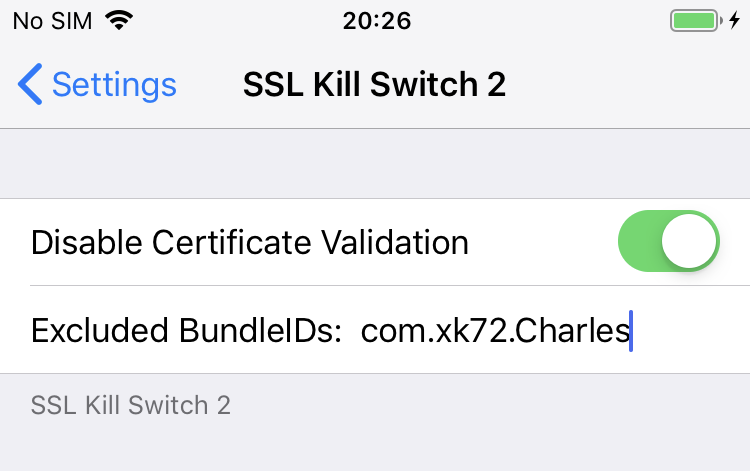 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust