
ZygoteExploitDemo
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
android-securitybinary-exploitationeducation+7
2
gitamans/zygoteexploitdemoEducational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
 michaelsplayground/cve-2019-9465
Demo Android application demonstrating CVE-2019-9465 for security testing and vulnerability analysis on mobile platforms.
 markblah/smsofdeath
Android PoC app that sends a malformed 8-byte WAP Push PDU over SMS to crash com.android.phone remotely, silently dropping calls on the target…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 androbugs/androbugs_framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…
 anasfik/flutterguard
Offline security audits for Flutter APKs on Android. Inspect permissions, SDKs, endpoints and potential secrets. No root, account, ads or analytics.
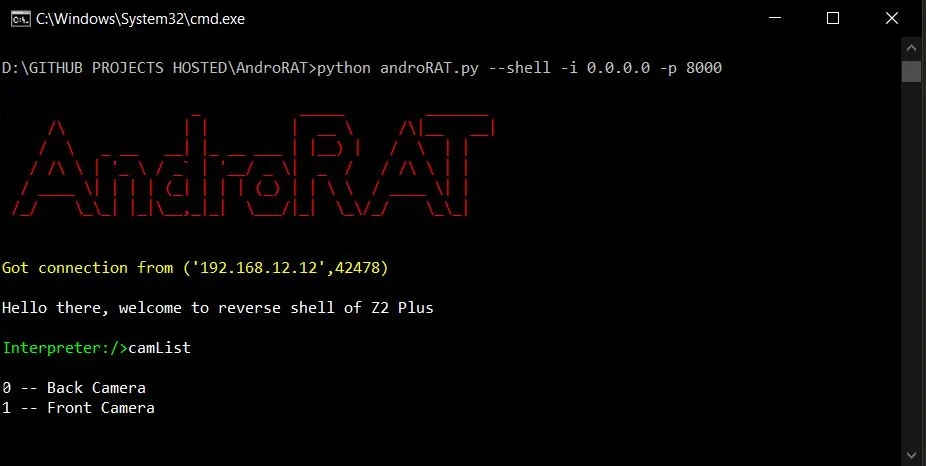 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
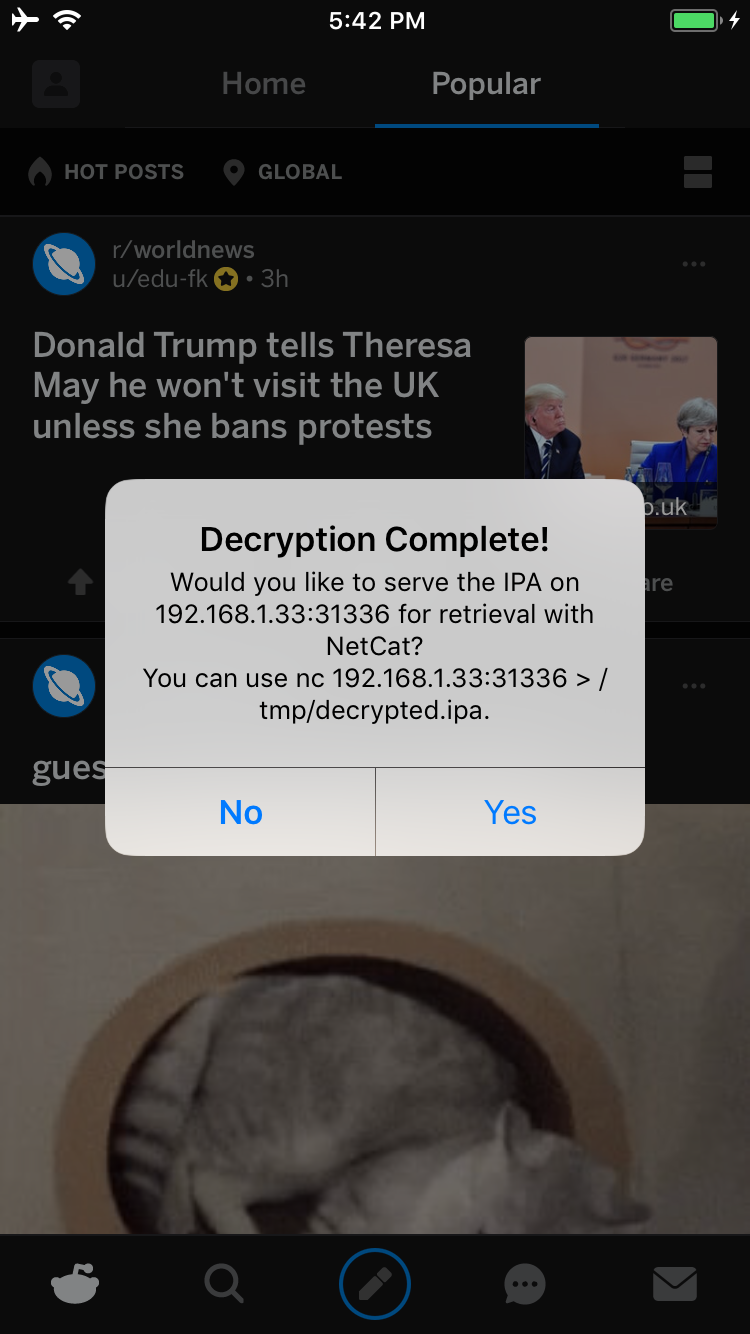 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 chichou/vscode-frida
Unofficial frida extension for VSCode
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
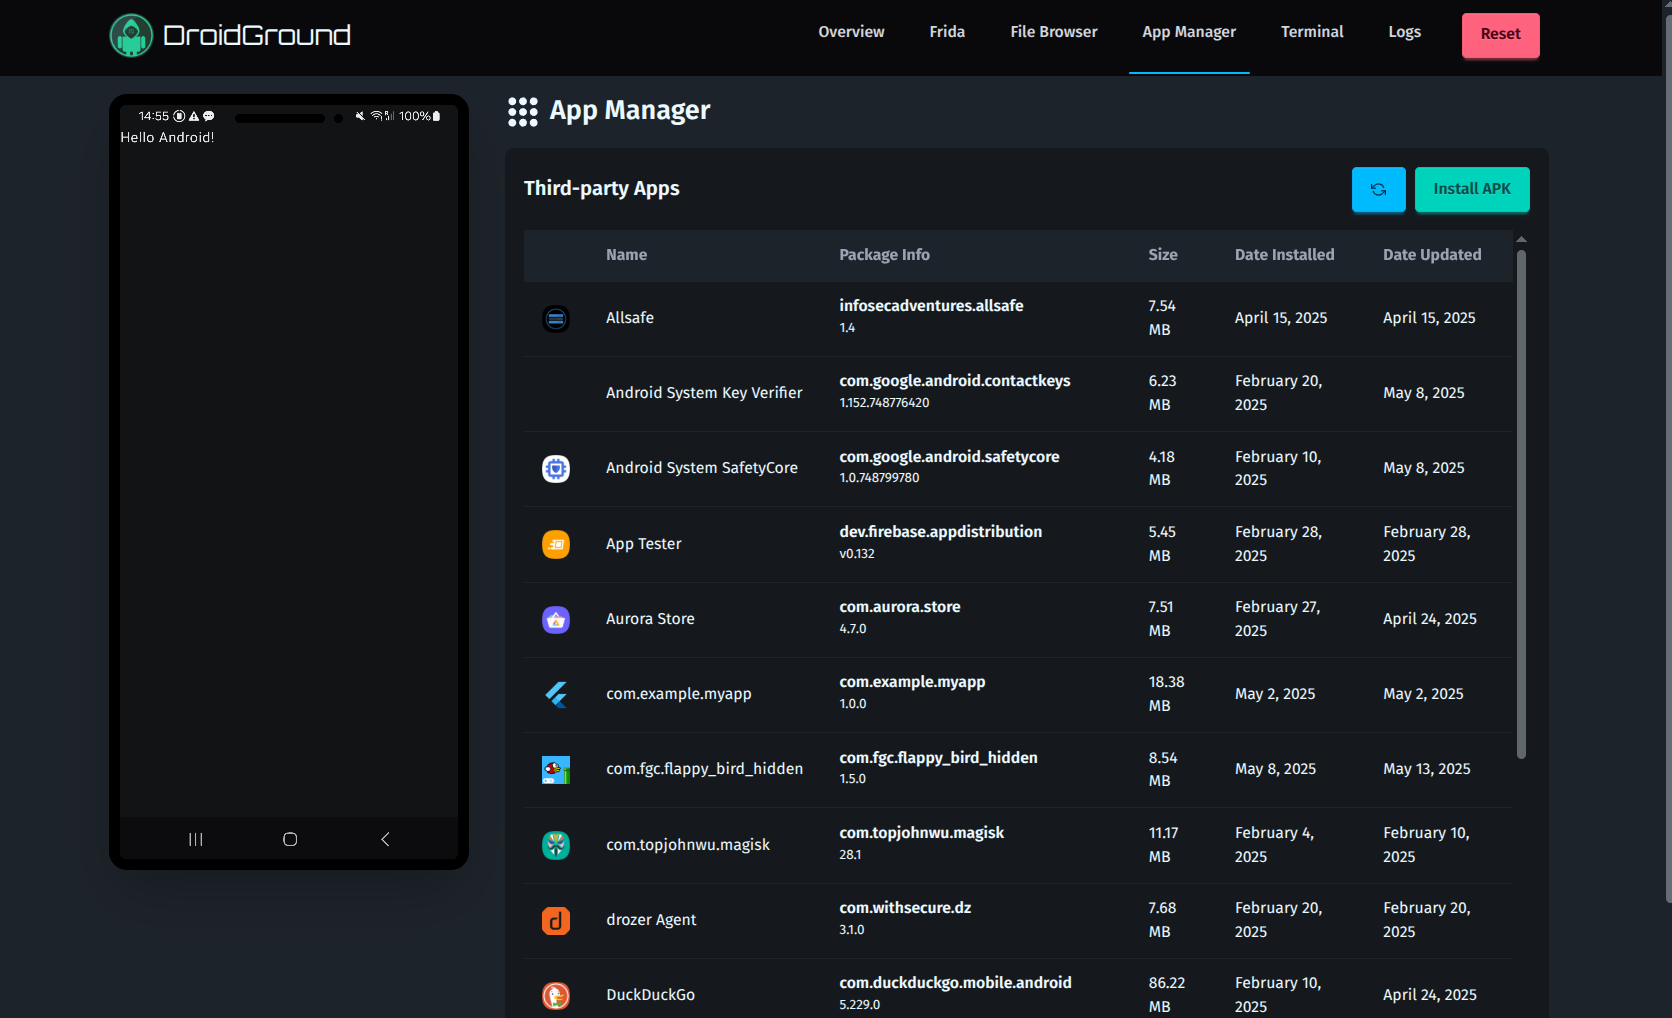 secforce/droidground
A flexible playground for Android CTF challenges.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.