

LIEF
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k
lief-project/liefCross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
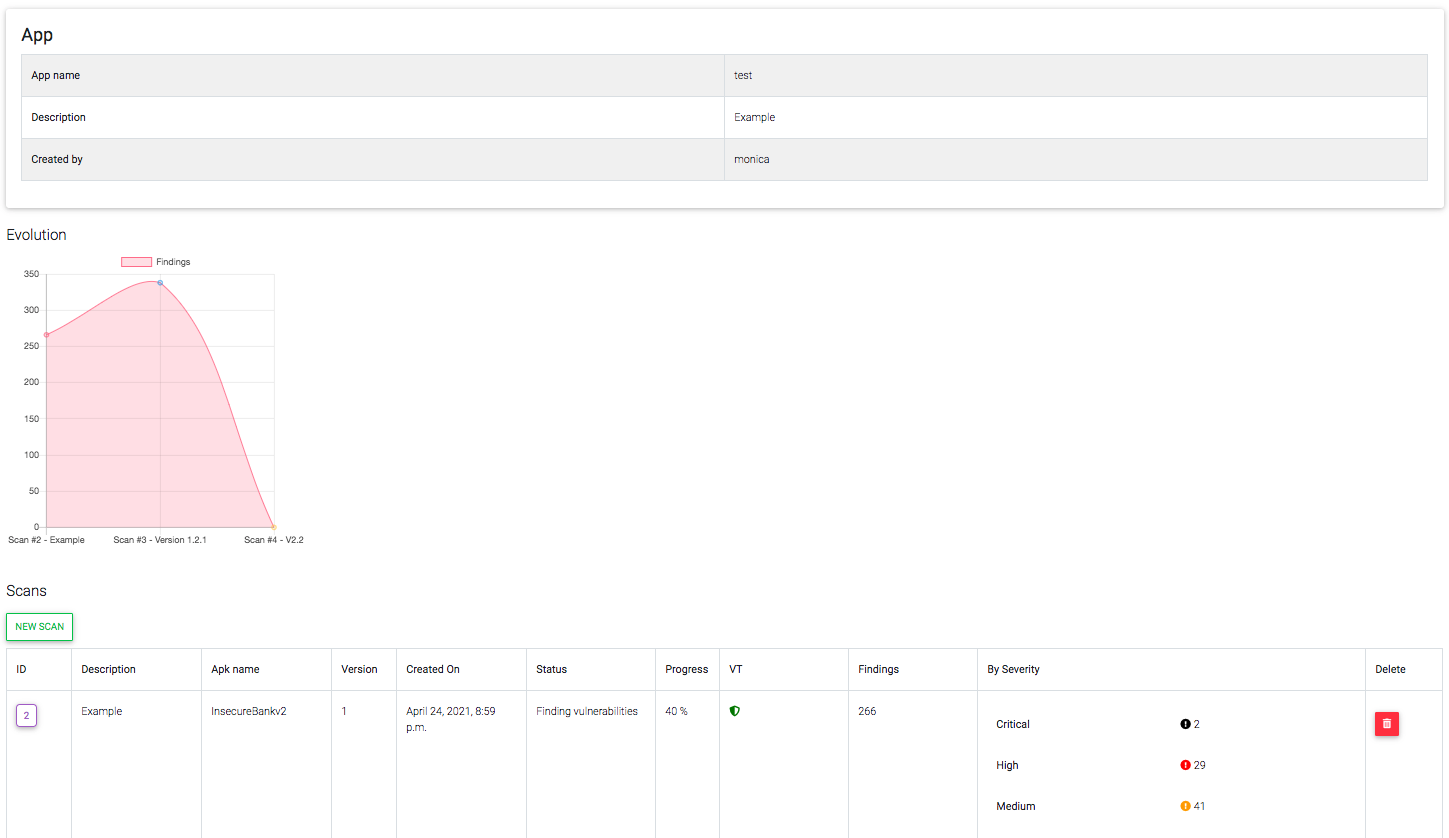 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 nowsecure/r2frida
Radare2 and Frida better together.
 deancyl/s9180-rootmygalaxy
RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 frida/frida
Main repo for hosting release binaries
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust