Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Main repo for hosting release binaries

Reverse engineering and pentesting for Android applications

UNIX-like reverse engineering framework and command-line toolset

PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…

A tool for reverse engineering Android apk files

GhostLock (CVE-2026-43499) app for the Galaxy S26 series

Ghidra is a software reverse engineering (SRE) framework

RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox

Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…

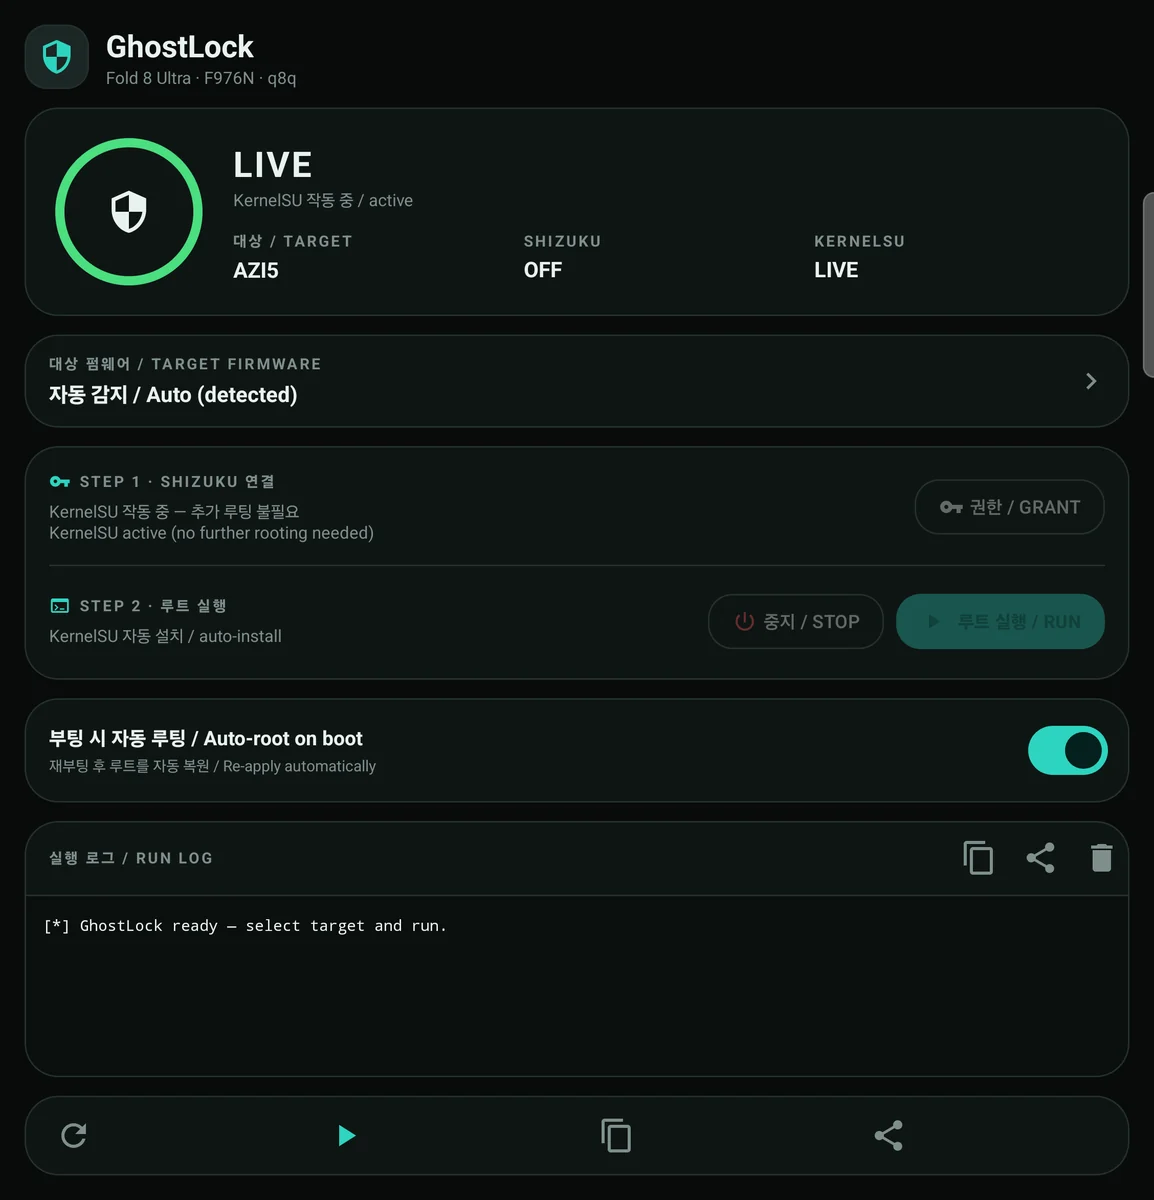
One-tap KernelSU installer for the Galaxy Z Fold 8 Ultra (SM-F976N / q8q) using the CVE-2026-43499 late-load exploit via Shizuku. Supports…

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…

Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…

Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0