

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
45.2k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 frida/frida
Main repo for hosting release binaries
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
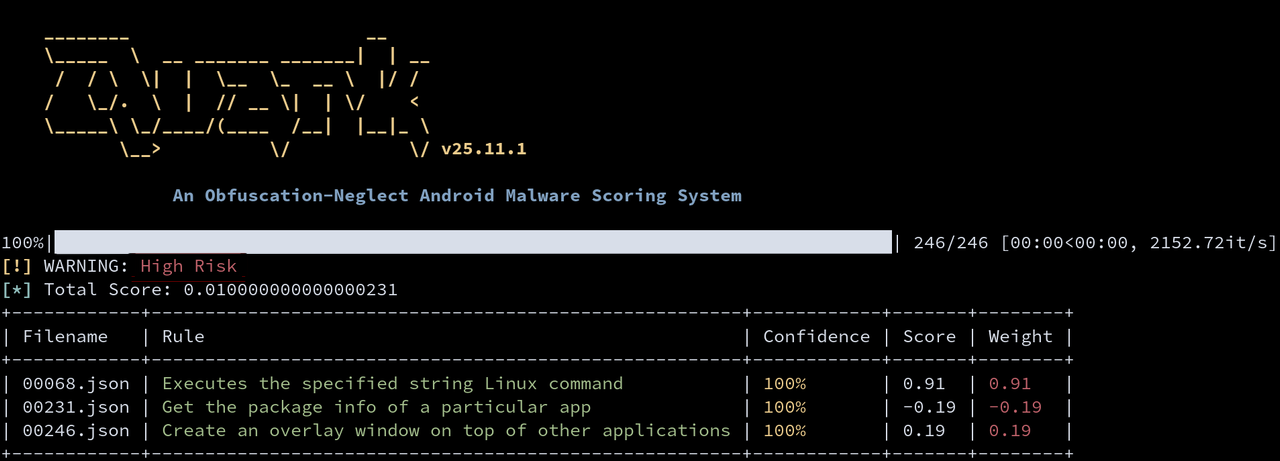 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 deancyl/s9180-rootmygalaxy
RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox