

rdx
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
android-securitybinary-analysiscode-analysis+6
ch0pin/rdxA native APK and DEX decompiler written in Rust
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 chichou/vscode-frida
Unofficial frida extension for VSCode
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
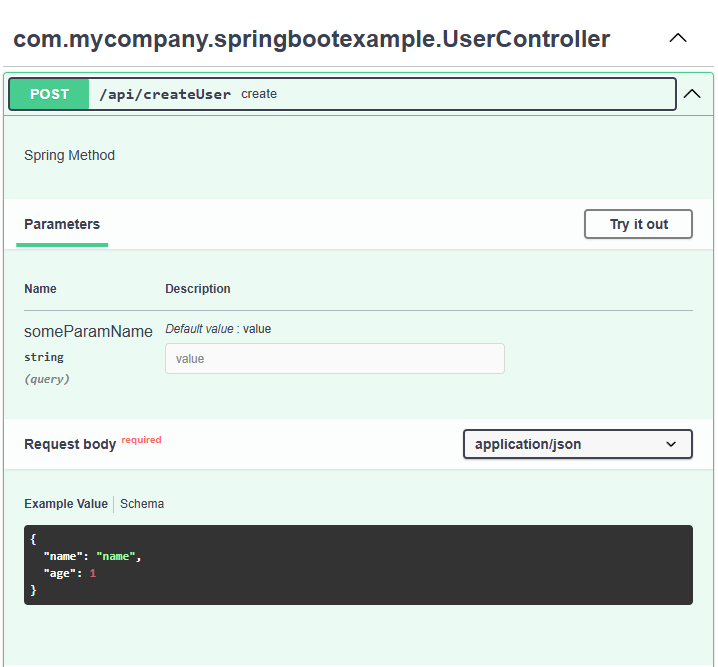 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
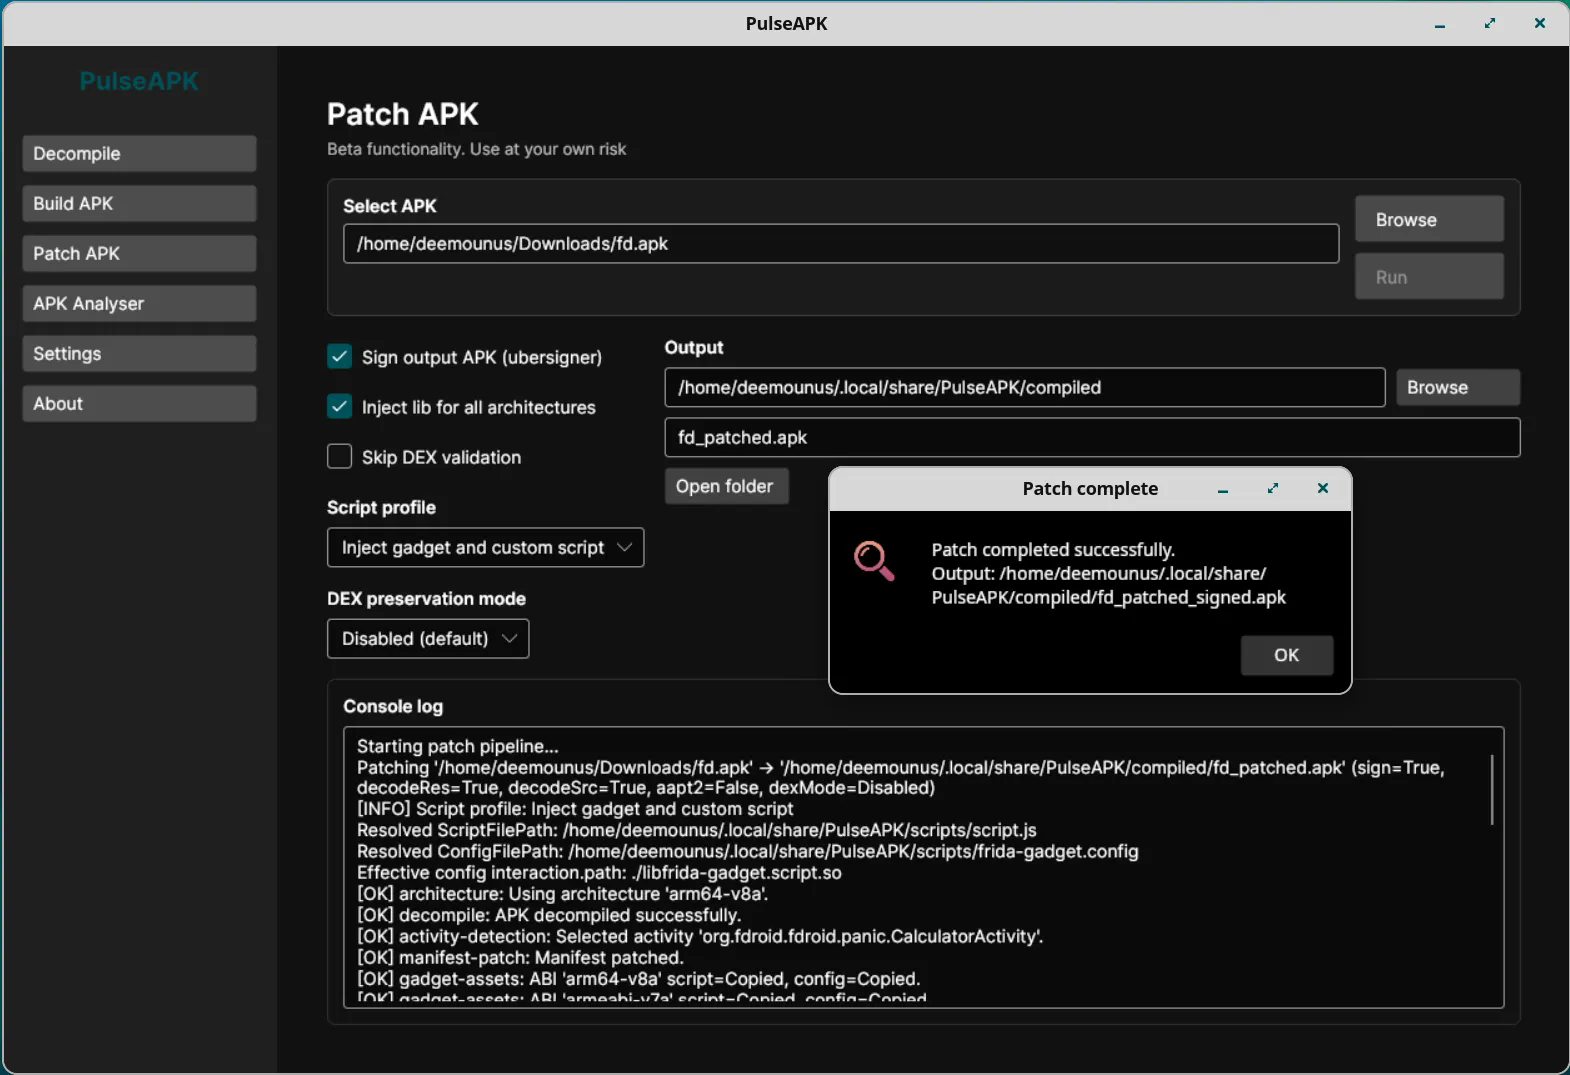 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.