
harlogger
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
information-gatheringios-securitymobile-app-pentesting+5
doronz88/harloggerSimple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
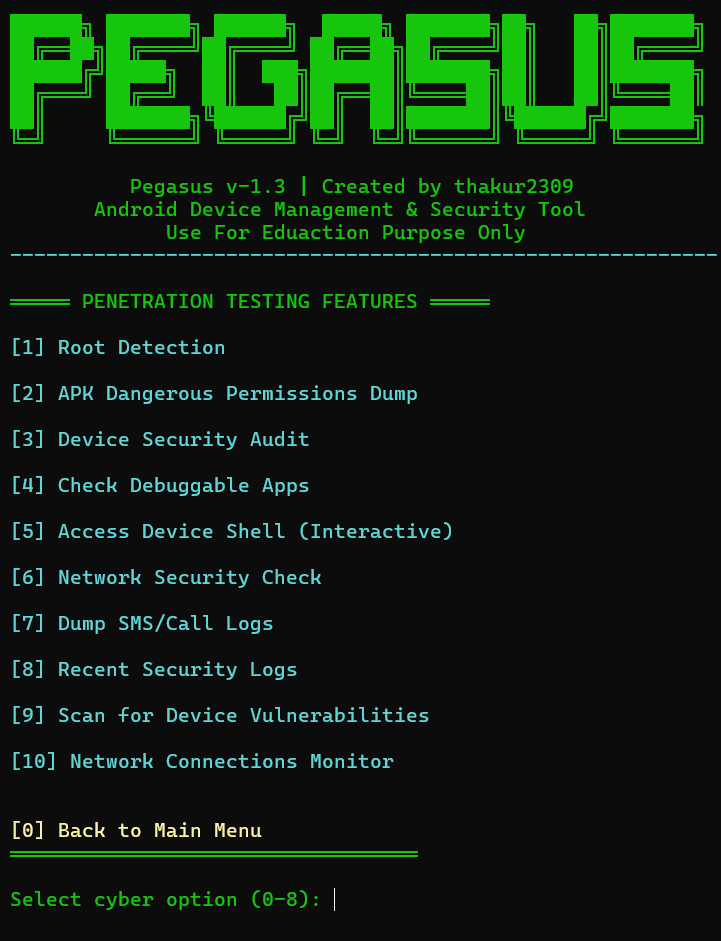 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 bronils/aotopsy
Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
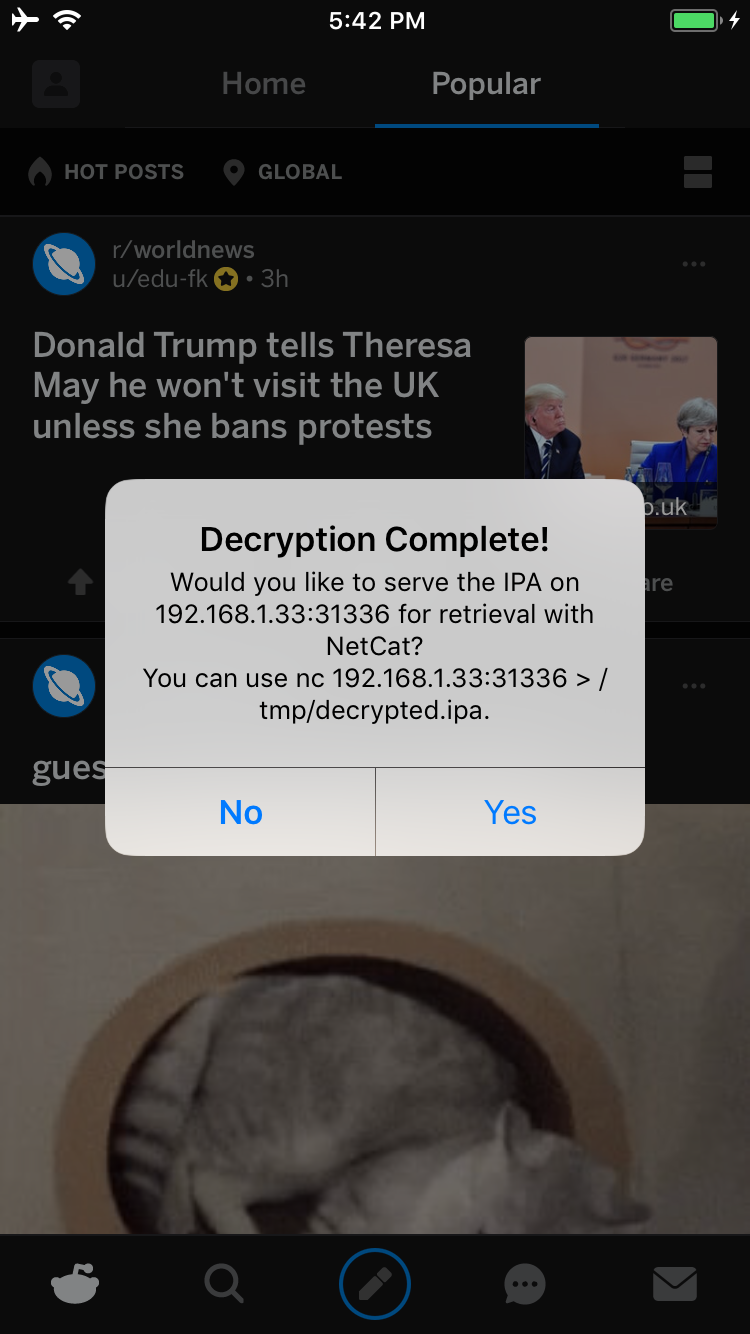 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 illusionofchaos/ios-nehelper-enum-apps-0day
iOS 15 0-day exploit (still works in 15.0.2)
 ustayready/mavd
Mobile Application Vulnerability Detection
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.
 ginsudev/wdbfontoverwrite
Proof-of-concept app to overwrite fonts on iOS using CVE-2022-46689.
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.
 a0zhar/quarkpoc
iOS Application w/Implementation of CVE-2024-27804